0xMarcio/cve: A Curated Feed of Exploit PoCs, Not a Vulnerability Database
Latest CVEs with their Proof of Concept exploits. The vulnerability allows an attacker to upload a malicious serialized payload to the server, leading to arbitrary code execution via deserialization when specific conditions are met.
At a glance
- What is it?
- 0xMarcio/cve is a Python-based index that tracks recently published proof-of-concept exploits for CVEs. It is a discovery tool for security researchers, not a replacement for a vulnerability scanner or a CVE database.
- Who is it for?
- Adopt 0xMarcio/cve if you are a security researcher, red teamer, or incident responder who needs a fast, human-curated list of recently published exploit PoCs. Do not use it as your primary vulnerability database, as it only covers CVEs with public PoCs and is not a scanner.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
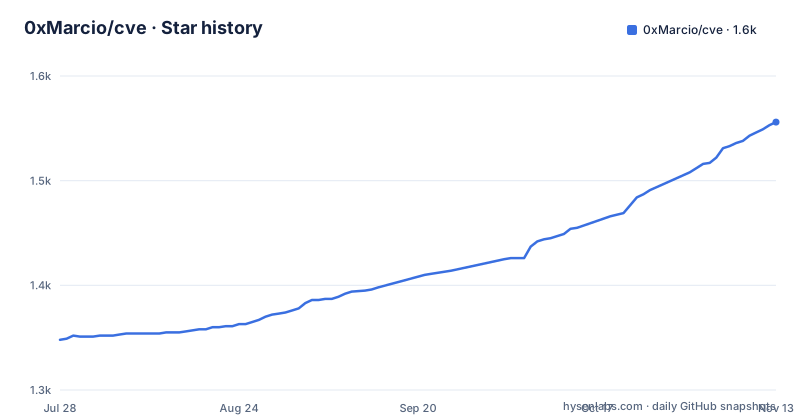
- 0xMarcio/cve1,556 ★ · +208
| Repository | 2026-07-28 | 2026-11-13 |
|---|---|---|
| 0xMarcio/cve | 1.3k | 1.6k |
208 Stars in the last 108 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What This Project Actually Tracks
0xMarcio/cve is a GitHub repository that maintains a list of recent CVEs, each paired with a link to a proof-of-concept exploit repository. The README shows tables organized by year, with the most recent entries at the top. For example, the 2026 section lists 20 repositories, and the 2025 section lists another 20, with the total counts stated as 498 and 581 respectively. The project does not host exploit code itself. It is a directory of links, with each row showing a star count, an update timestamp, a repository name, and a short description. This makes it a discovery feed rather than a tool you run against your own systems.
Who Benefits From a PoC Index
The intended audience is clear from the content: security researchers who want to see what exploits are circulating, red teams looking for a starting point for a specific CVE, and defenders who need to know what public exploits exist for a vulnerability they are tracking. The descriptions in the README cover a wide range of targets: Linux kernel local privilege escalation, cPanel authentication bypass, Netlogon stack buffer overflow, n8n arbitrary file read to RCE, Next.js RCE, and Kubernetes container escape. If you are patching a system and want to know if a public exploit exists, this list gives you an answer quickly. It is less useful for developers who need to scan their own codebase, because the project does not compare your software against these CVEs.
How the Data Is Organized and Maintained
The repository structure is simple: a README with markdown tables. Each table is split by year, and each year has a 'Latest 20 of N Repositories' header, implying the list is larger than what is displayed. The update timestamps in the README are recent, with some entries marked '28 minutes ago' or '1 hour ago', which suggests the maintainer updates the file frequently. The project is written in Python, but the README does not describe any scripts or automation. It is possible that Python is used to generate the tables from GitHub API data. What is visible is a manually or semi-automatically maintained markdown file. The lack of a formal release process, as indicated by 'Recent releases: (none retrieved)', means you should treat the README as the canonical output.
Getting Started: What You Actually Do
There are no installation steps in the README, because there is nothing to install. You do not clone the repository to run a tool. You visit the homepage at https://cve.codepwn.win/ or open the README on GitHub. The workflow is to scan the tables for a CVE of interest, note the linked repository, and then go to that repository to read the exploit code. For example, if you see 'CVE-2026-31431' with a link to 'theori-io/copy-fail-CVE-2026-31431', you click through to examine the exploit. The only command you might run is 'git clone' on a specific PoC repository, but that is outside this project. The Python tag is likely for the generator script, but the README does not document how to run it. So the practical usage is purely as a web reference.
What the List Does Not Tell You
The project has clear limits. It only includes CVEs with public PoCs, so it is not a complete CVE list. The star counts in the table are a popularity signal, but they do not indicate exploit reliability or safety. Some descriptions are vague, like 'CVE-2026-41651' with an empty description, or 'CVE-2026-31431-Advanced-Exploit' with a Chinese phrase that translates to 'pure file exploitation', which is unclear. The README does not provide any metadata about the CVEs themselves, such as CVSS scores, affected versions, or patch status. You have to go to each linked repository to get those details. Also, the list mixes verified exploits with unverified PoCs and analysis repos, so you cannot assume every link contains a working exploit. The 'Poc-Analysis' entries for Xiaomi devices are explicitly for educational purposes, but others may not be.
A Real Alternative: The NVD and Vendor Advisories
The most direct alternative is the National Vulnerability Database (NVD) at nvd.nist.gov. The NVD provides structured data for every CVE, including descriptions, CVSS scores, and references. It does not curate PoC links, but it does include references to exploit databases and vendor advisories. The difference in approach is that NVD is comprehensive and authoritative, while 0xMarcio/cve is selective and community-driven. If you need to know whether a specific CVE has a public exploit, this project is faster. If you need to track all vulnerabilities in your software stack, NVD or a commercial scanner is the right choice. Another alternative is the Exploit Database at exploit-db.com, which hosts actual exploit code and is searchable, but it is not as timely for brand-new CVEs. This project's advantage is that it surfaces PoCs within hours or days of publication, as seen in the timestamps.
Maintenance, Licensing, and Trust Considerations
The project is licensed under MIT, so you can reuse the README content or the generator script without restriction, as long as you include the license notice. The repository is not archived, and the last push was on 2026-08-29, which is recent relative to the material's timeframe. However, there are no releases, which means there is no versioned artifact. The maintenance cost is low for a consumer: you just revisit the page. For a maintainer, the cost is high because keeping the list current requires constant updates, and the README shows that. A key trust issue is that the project aggregates links from third parties. Some of those repositories may contain malicious code disguised as PoCs, a known risk in the exploit ecosystem. The README does not include any warnings about this, so you must exercise caution when cloning and running any linked code. The project also does not verify that a PoC works, so a 'POC' label is not a guarantee of functionality.
Editorial conclusion
Adopt 0xMarcio/cve if you are a security researcher, red teamer, or incident responder who needs a fast, human-curated list of recently published exploit PoCs. Do not use it as your primary vulnerability database, as it only covers CVEs with public PoCs and is not a scanner. Before relying on any PoC, verify the linked repository's code, check the CVE ID against the NVD or vendor advisory, and test only in isolated environments. The project's value is its timeliness and curation, not its completeness.
Frequently asked questions
What is the 0xMarcio/cve repository for?
It is a link directory for third-party proof-of-concept repositories, split into a Just landed table and Trending tables for 2026 and 2025, where star count and last update are the only ranking signals.
Does 0xMarcio/cve host the exploit code itself?
Every row links out to a separate repository owned by someone else, and the README carries no exploit code, so the payloads live in those third-party projects rather than in this one.
How does 0xMarcio/cve decide what to list?
The tables separate newly pushed entries from the higher-starred entries of each year, and within a table the order follows how recently the linked repository was updated, with stars acting as the secondary signal.
Can one CVE show up more than once in 0xMarcio/cve?
Yes. Two WinRAR path traversal proof-of-concept repositories sit in the Just landed table, and one publisher holds both Citrix NetScaler rows, so a row counts a repository rather than a vulnerability.
Which products do the visible 0xMarcio/cve entries cover?
WordPress core and its plugins, Citrix NetScaler, WinRAR, Microsoft Defender, GitLab, Keycloak, CrushFTP, Craft CMS, CUPS, sudo, GNU inetutils-telnetd, a TYPO3 extension and several Android handset kernels.
How current is the 0xMarcio/cve listing?
The last push on record is 25 September 2026 and the repository publishes no releases. Inside the tables the freshest row is marked 22h ago and the oldest visible one 46d ago.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/0xmarcio-cve)Star history chart for your README
[](https://hysenlabs.com/projects/0xmarcio-cve)Was this useful?