Androguard 5: a Python toolkit for Android APK and DEX analysis
Reverse engineering and pentesting for Android applications
At a glance
- What is it?
- Androguard exposes APK archives, DEX structure and Dalvik bytecode to Python scripts, with an optional decompiler and disassembler. It is a library first and a CLI second, and version 5 is a rewrite that is not the package on PyPI.
- Who is it for?
- Adopt Androguard if you need to script Android analysis: enumerate classes and methods, pull strings out of a DEX, decompile a specific method, or feed APK structure into a larger Python pipeline. Do not adopt it if you want a GUI, or if you expect `pip install androguard` to give you version 5, because that command currently fetches 4.1.4 and uninstalls 5.0.0.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 28 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
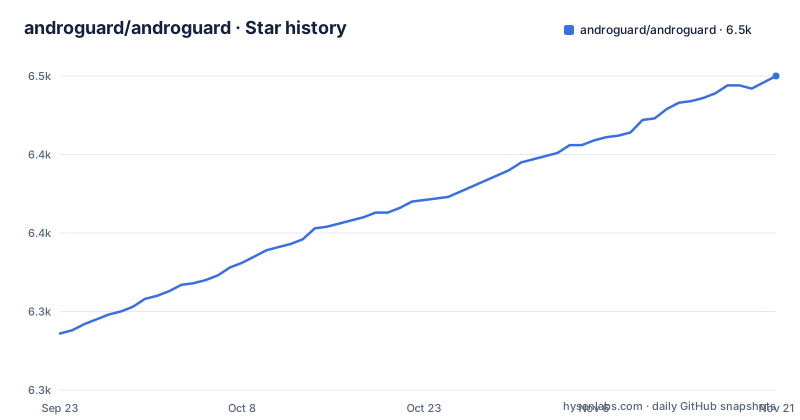
- androguard/androguard6,450 ★ · +164
| Repository | 2026-09-23 | 2026-11-21 |
|---|---|---|
| androguard/androguard | 6.3k | 6.5k |
164 Stars in the last 59 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What Androguard is for, and who actually needs it
Androguard parses Android application files and hands the result to Python. The README describes it as a tool for reverse engineering and pentesting. The audience is narrow and specific: security engineers triaging an APK, analysts who want to answer questions about a large set of apps programmatically, and tool authors who need a DEX parser they can import rather than a binary they have to shell out to.
The distinction that matters is library versus application. The CLI exists and the README documents it, but the primary surface is the Python API. The CLI summary reports the package, main activity, dex count, classes and methods. That shape tells you what the project is optimised for: extracting structured facts from an APK, not producing a readable reconstruction of an app for a human to browse. If you want to open an APK and read it like source, this is the wrong entry point.
How Androguard 5 splits the work across parsers
Version 5 is assembled from separate libraries rather than one monolith. The README gives a table: `apk-parser` (package `apkparser-ag`) handles the ZIP structure, signatures and manifest hooks; `dex-parser` (package `dexparser-ag`) provides the Rust core with Python bindings for classes, methods, fields and bytecode; `axml` and `axml-parser` decode `AndroidManifest.xml` and `resources.arsc`. Everything above that is optional and installed through extras: `androguard[disasm]` for Dalvik disassembly and control-flow graphs, `androguard[decompile]` for DEX to Java, `androguard[arm]` for native ARM64 code, and `androguard[patch]` for in-memory decode and build.
The data flow is layered and you can enter at any level. At the top sits the high-level `Application` API; below it are the APK, DEX and binary XML libraries listed in the table.
One consequence is worth stating plainly. Because the DEX layer is a Rust core behind Python bindings, the optional extras require a Rust toolchain to build from a checkout. The README says so directly in a comment above the install commands.
Installing Androguard 5 from a checkout
The README is unusually explicit about a trap: Androguard 5 is this repository, and it is not the package currently published on PyPI, which is `androguard` 4.1.4. A bare `pip install androguard` downloads 4.1.4 and uninstalls 5.0.0. Install from a checkout instead. The README notes that a Rust toolchain is required for the optional extras, and that Python 3.14 needs a forward-compatibility flag because the bindings use PyO3 0.23, which supports up to 3.13.
export PYO3_USE_ABI3_FORWARD_COMPATIBILITY=1
pip install -e .
pip install -e '.[full]'
After 5.0.0 is published, the README states the same extras install from PyPI with `pip install androguard` and `pip install 'androguard[full]'`. Until then, the editable install is the path. Note the dependency lines in `pyproject.toml`: `apkparser-ag` and `dexparser-ag` are both tracked from git, with comments saying apkparser-ag stays on git until 0.0.3 is on PyPI and that PyPI dexparser-ag 0.0.1 is the old hachoir parser. That means your build reaches out to GitHub during install.
For a first real use, the CLI is the fastest way to confirm the install works. Point it at an APK and ask for a summary.
androguard -i my.apkThe README says this prints the package, main activity, DEX count, classes and methods.
Where Androguard stops being the right tool
The decompiler is optional and it is a separate repository. If you install plain `androguard`, `--decompile` and `--disasm` are not available; you need `androguard[decompile]` or `androguard[disasm]` respectively, and both are git dependencies in `pyproject.toml`. pyproject.toml classifies the project as `Development Status :: 4 - Beta`.
The harder limitation is historical. The README warns that versions from 4.0.0 onward differ substantially from 3.3.5, the previous stable release from 2019, and that certain functionalities have been removed. Anyone migrating a script written against the 3.x API should expect breakage, and the README's suggested remedy is to open an issue.
There is also a versioning hazard that is easy to miss. The latest published release is v4.1.4 from 2026-06-05, while the repository declares `version = "5.0.0"`. The README states that a bare `pip install androguard` will uninstall 5.0.0. If your team pins versions in a lockfile and someone runs that command, the environment silently moves backwards. That is not a bug in the code; it is a consequence of publishing under the same distribution name, and it deserves a note in your own install instructions.
Androguard compared with jadx
A common alternative is jadx, and the difference is architectural rather than cosmetic. jadx is a decompiler with a user interface: you open an APK, it reconstructs Java source in a browsable tree, and you read it. Androguard is a parsing library with a CLI attached. It gives you package metadata, permissions, classes, methods, strings and cross-references, and it leaves the presentation to you.
That makes jadx the better choice for manual investigation of one app, and Androguard the better choice when the unit of work is a thousand apps or a CI job. Androguard's decompiler extra exists, and the README lists decompiling to Java (requires androguard[decompile]) among the CLI uses, so it can produce Java. But the surrounding design assumes you are consuming structured output in code, not reading it in a window. If your workflow is "open the app, find the login check, read it", Androguard adds a layer of scripting between you and the answer.
Maintenance, licence and upgrade cost
The repository is not archived, and the last push was on 2026-10-25. Releases are sparse rather than continuous: v4.1.4 on 2026-06-05, v4.1.3 on 2025-02-24, v4.1.2 on 2024-05-31. The 5.0.0 version in `pyproject.toml` has not appeared on PyPI as of the README's own statement.
The licence is Apache-2.0, declared both in the classifier list and as `license = { file = "LICENCE" }`. For most users that is permissive enough to embed in internal tooling. The practical licence question is not Androguard itself but its dependency chain: the optional extras pull in `dex-decompiler`, `dex-bytecode-py`, `arm-disassembler` and `arm-decompiler`, each from its own repository. Check those separately if you redistribute a bundled tool.
Upgrade cost is dominated by two things. First, the 3.x to 4.x/5.x break the README describes. Second, the git-tracked dependencies: `pyproject.toml` comments say `apkparser-ag` stays on git until 0.0.3 is on PyPI and that `dexparser-ag` 0.0.1 on PyPI is the old hachoir parser, so both are pinned to git. A build that resolves from git is not reproducible in the way a pinned wheel is, and that will matter to anyone building in an offline or air-gapped environment. Python support is declared as 3.10 through 3.13, with `requires-python = ">=3.10"`.
Agent skills and the examples directory
Two parts of the repository are easy to overlook. The `examples/` directory holds runnable demos that the test suite also executes via `tests/test_examples.py`, so they are kept working rather than left to rot. The README lists `python -m examples.application_summary`, `examples.disassemble`, `examples.decompile`, `examples.arm`, `examples.patch_decode` and `examples.run_all`, each tied to the extra it needs. Running `examples.application_summary` is a reasonable second check after the CLI, because it exercises the Python API rather than the argument parser.
The other is Claude Code support: `CLAUDE.md`, an analyst agent at `.claude/agents/androguard-analyst.md`, skills named `/analyze-apk`, `/decompile-apk`, `/find-refs` and `/scan-vulns`, and a `workspace/` directory for samples, decompiled output and reports. The README shows `claude /analyze-apk path/to/app.apk`. This is a thin orchestration layer over the same library, and it is only useful if you already use that agent tooling. It is not a substitute for understanding the API, and the README does not claim otherwise.
Editorial conclusion
Adopt Androguard if you need to script Android analysis: enumerate classes and methods, pull strings out of a DEX, decompile a specific method, or feed APK structure into a larger Python pipeline. Do not adopt it if you want a GUI, or if you expect `pip install androguard` to give you version 5, because that command currently fetches 4.1.4 and uninstalls 5.0.0. Before committing, verify that your Python version is 3.10 through 3.13, that a Rust toolchain is available for the optional extras, and that the `dexparser-ag` and `apkparser-ag` git dependencies resolve in your environment.
Frequently asked questions
How do I install Androguard?
Version 5 installs from a checkout of the repository, not from PyPI: export PYO3_USE_ABI3_FORWARD_COMPATIBILITY=1, then run pip install -e . and optionally pip install -e '.[full]'. A bare pip install androguard downloads 4.1.4 and uninstalls 5.0.0, according to the README.
How do I use Androguard to analyze an APK?
The CLI takes an APK with -i and prints a summary of package, main activity, DEX count, classes and methods. The README also offers a high-level Application API for use from Python.
What is Androguard?
It is a Python library and command line tool for reverse engineering and pentesting Android applications, covering APK archives, DEX structure, binary XML and optionally Dalvik disassembly, Java decompilation and ARM64 native code.
What does Androguard do?
It parses Android application files and exposes their structure to Python: package metadata, permissions, class and method lists, strings and manifest data. Optional extras add disassembly, control-flow graphs, decompilation to Java, ARM64 support and APK patching.
How does Androguard differ from jadx?
jadx is a decompiler with a user interface for reading reconstructed Java, while Androguard is a parsing library with a CLI, built for scripting and bulk analysis. Androguard does offer a decompiler extra, but its primary output is structured data rather than a browsable source tree.
What can I use instead of Androguard?
jadx is a common alternative, and the difference is approach: jadx centres on reading decompiled source interactively, whereas Androguard centres on importing parsed APK and DEX data into your own Python code. Which one fits depends on whether your unit of work is one app or many.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/androguard-androguard)Star history chart for your README
[](https://hysenlabs.com/projects/androguard-androguard)Was this useful?