Ansible: Agentless Automation That Keeps SSH at the Center
Ansible is a radically simple IT automation platform that makes your applications and systems easier to deploy and maintain. Automate everything from code deployment to network configuration to cloud management, in a language that approaches plain English, using SSH, with no agents to install on remote systems.
At a glance
- What is it?
- Ansible is a Python-based IT automation platform that typically manages POSIX machines over SSH without a persistent agent and also supports Windows transports. This review covers its design, installation, limitations, and who should adopt it.
- Who is it for?
- Adopt Ansible if you want agentless automation across Linux and network devices, value plain-language playbooks, and can tolerate Python-based execution. Windows targets are supported through WinRM, PSRP or supported SSH configurations; assess the setup and modules you need.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 3 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
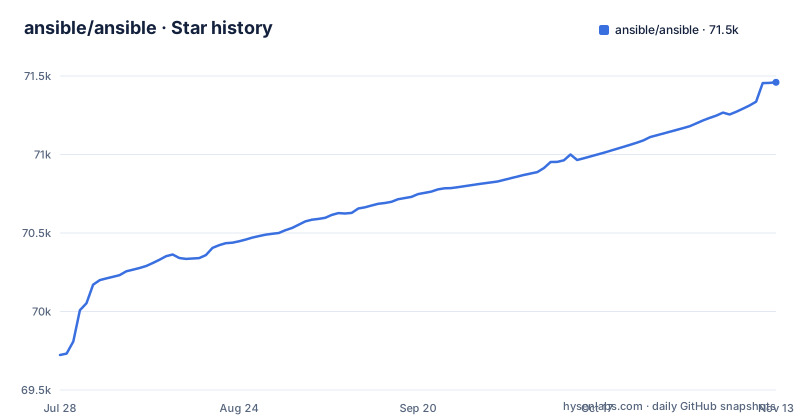
- ansible/ansible71,460 ★ · +1,737
| Repository | 2026-07-28 | 2026-11-13 |
|---|---|---|
| ansible/ansible | 69.7k | 71.5k |
1,737 Stars in the last 108 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What Ansible Actually Solves
Ansible is an IT automation system for configuration management, application deployment, cloud provisioning, ad-hoc task execution, network automation, and multi-node orchestration. It solves the problem of managing many machines without installing dedicated agent software on each one. The README lists design principles: minimal setup, parallel execution, agentless operation via the existing SSH daemon, and a language that is both machine and human friendly. It is aimed at system administrators and DevOps engineers who want to automate repetitive tasks, roll out updates across a fleet, or provision cloud resources, all from a single control node. The claim of being 'radically simple' is a strong one, but the core idea is straightforward: you describe desired state in files, and Ansible makes it happen over SSH.
The Agentless Mechanism: SSH as the Transport
The central mechanism is agentless execution. Ansible connects to remote machines over the existing SSH daemon, so there is no custom agent and no additional open ports. This differs from tools that require a daemon or client installed on each target. The README states that Ansible can manage new remote machines instantly, without bootstrapping any software. That means the control node runs Ansible, and it pushes commands or modules to targets via SSH. Modules can be written in any dynamic language, not just Python, which broadens who can contribute. The flow is: you write a playbook, Ansible connects over SSH, transfers the necessary module code, executes it, and reports results. This pull-free model is simple to understand, but it also means that changes are only applied when you run Ansible, not continuously.
Installation and Getting Started
The README directs you to install a released version with pip or a package manager. The installation guide is linked, but the exact commands are not in the README. The published package is ansible-core, which requires Python 3.13 or newer. The README mentions that power users can run the 'devel' branch directly, which has the latest features and fixes, but warns it is more likely to have breaking changes. For most users, a stable release from pip or a system package is the safer path. The repository shows recent releases v2.22.0, v2.21.6, and v2.20.11, all published on 2026-11-02, indicating a regular release cycle with multiple maintenance branches. The default branch is 'devel', which corresponds to the version under active development. If you want stability, pick a release from a stable branch, not devel.
Playbooks and the Push Model: What It Means in Practice
Ansible's model is push-based: you initiate changes from a control node. This is visible in the design principle of managing machines 'quickly and in parallel'. You write playbooks that describe the desired state, and Ansible pushes them out. This is fine for scheduled maintenance or on-demand changes, but it means there is no continuous enforcement. If someone manually changes a file on a target, Ansible will not fix it until you run it again. The README does not mention a daemon or scheduler, so you must rely on external cron jobs or CI systems to trigger runs. That is a trade-off: simplicity over constant state enforcement. For environments that need immediate, automatic remediation, this push model is a limitation.
Security and Auditability: A Design Choice
The README emphasizes security and easy auditability, review, and rewriting of content. Because playbooks are plain text, they can be version-controlled and reviewed like code. The agentless approach reduces the attack surface on managed nodes: there is no extra service to secure or update. However, this also means that the control node becomes a high-value target. If an attacker gains access to the control node, they have SSH credentials or keys to all managed machines. The README does not discuss control node hardening, but it is an implicit risk. Also, Ansible is usable as non-root, which is a plus for security, but some tasks will require privilege escalation. The security model relies on the existing SSH infrastructure, so your SSH configuration and key management directly affect Ansible's security.
Limitations and Failure Modes
One genuine limitation is the lack of a continuous agent. A standard playbook run is initiated by a controller rather than a persistent agent; event-driven automation can be built separately with Ansible Rulebook. Windows targets are supported using WinRM, PSRP or supported SSH configurations, each with setup and version requirements. The README also states that the 'devel' branch is 'reasonably stable' but has a higher chance of breaking changes, so using it in production is risky. A failure mode is that if SSH is misconfigured or a target is unreachable, the entire run fails or skips, and you need to handle error handling in playbooks. The README does not provide details on error handling, but it is a known operational challenge with any SSH-based tool.
Alternatives: Puppet or SaltStack
A real alternative is Puppet, which uses a client-server model with an agent installed on each node. Puppet continuously enforces desired state, pulling configuration from a master server. This is the opposite of Ansible's push model. With Puppet, changes are applied automatically on a schedule, which is better for drift correction but requires agent installation and more infrastructure. SaltStack is another alternative, which can operate in both agent and agentless modes, but it often uses a master-minion setup. The key difference is that Ansible typically uses SSH for POSIX targets and WinRM, PSRP or supported SSH configurations for Windows, while Puppet and SaltStack typically require agents and a central server. If you need continuous enforcement or have Windows-heavy environments, Puppet might be a better fit. If you value simplicity and minimal footprint, Ansible's approach is simpler to start with.
Maintenance, Licensing, and Community
Ansible is licensed under GPL-3.0 or later, which has implications if you modify and distribute the code, but the README does not provide legal advice. The project is sponsored by Red Hat, which suggests long-term support. The repository shows multiple stable branches (stable-2.X) and a regular release cadence: v2.22.0, v2.21.6, and v2.20.11 on 2026-11-02. This indicates active maintenance and a clear upgrade path. The README points to a release and maintenance page for details on active branches. The community is a major part of the project, with a forum and a newsletter called the Bullhorn. The README credits contributions from over 5000 users. For maintenance cost, you need to track new releases and update playbooks for breaking changes, especially when moving between major versions. The README advises talking to the community before making larger changes, which is a sign that the codebase is complex and contributions need coordination.
Editorial conclusion
Adopt Ansible if you want agentless automation across Linux and network devices, value plain-language playbooks, and can tolerate Python-based execution. Windows targets are supported through WinRM, PSRP or supported SSH configurations; assess the setup and modules you need. Standard playbook runs are initiated by a controller, while event-driven integrations are available separately. Before adopting, verify the appropriate SSH, WinRM or PSRP transport for your targets and that your use case fits Ansible's push-on-command model. Check the installation guide for your platform and review the release and maintenance page to understand which version branch you should run.
Frequently asked questions
What is Ansible and why is IT used?
Ansible is an IT automation system covering configuration management, application deployment, cloud provisioning, ad-hoc task execution, network automation and multi-node orchestration. It runs over the existing SSH daemon with no agent installed on the remote machine, and describes infrastructure in a language meant to be both machine and human friendly.
Is Ansible still relevant in 2026?
The last push to the repository was on 2026-11-02, and three releases were published that day: v2.22.0, v2.21.6 and v2.20.11. The package is marked Development Status :: 5 - Production/Stable in its classifiers.
Which is better, Ansible or terraform?
The repository makes no comparison with Terraform. Its own stated scope is configuration management, application deployment, cloud provisioning, ad-hoc task execution, network automation and multi-node orchestration, driven over an existing SSH daemon with no custom agents and no additional open ports.
Is Ansible difficult to learn?
The design principles put an extremely simple setup process and a minimal learning curve first, and ask for a description language that is both machine and human friendly, with security and easy auditability as the focus. The file offers no measurement of how long that takes, so treat the claim as a design target rather than a figure.
How do I install Ansible?
Install a released version with pip or a package manager, following the linked installation guide; the README gives no command of its own. The published package is ansible-core, which requires Python 3.13 or newer and whose classifiers name POSIX as the operating system.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/ansible-ansible)Star history chart for your README
[](https://hysenlabs.com/projects/ansible-ansible)Was this useful?