Archestra: one Docker image for the LLM proxy, the MCP registry and the agent runtime
Enterprise AI Platform with guardrails, MCP registry, gateway & orchestrator
At a glance
- What is it?
- Archestra bundles an LLM gateway, an MCP gateway, a private tool registry, a Kubernetes orchestrator and an agent runtime into a single container image. It suits platform teams who already run agents in production and need one control plane in front of them, and it costs you a large TypeScript surface to keep.
- Who is it for?
- Adopt Archestra if you already run coding agents across Claude Code, Codex or Cursor and need one auditable gateway with per-team cost limits and an MCP registry. Do not adopt it for a single-team proof of concept: the Kubernetes dependency and the platform surface both assume an enterprise operator.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
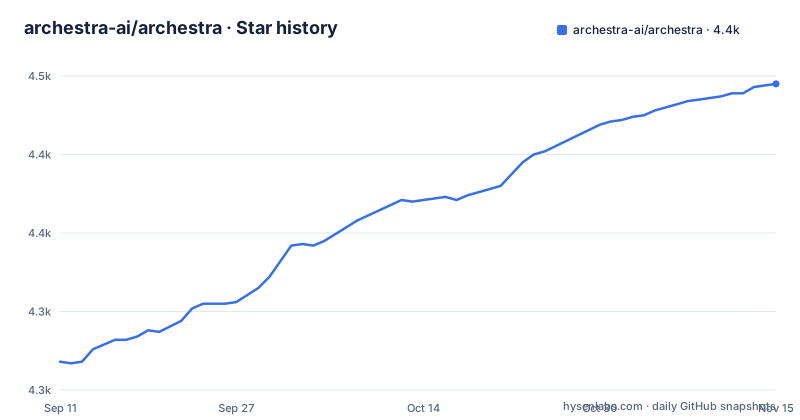
- archestra-ai/archestra4,445 ★ · +177
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| archestra-ai/archestra | 4.3k | 4.4k |
177 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The gateway sits between your agents and every provider
Pointing Claude Code, Codex or Cursor at one URL is the whole premise, and the replacement for a pile of per-provider API keys. That single endpoint fronts Anthropic, OpenAI, Azure, Bedrock and DeepSeek, and it carries three controls that would otherwise live in each client's config file: virtual API keys, cost limits, and dynamic model routing.
The design bet is that the agent is untrusted. Every call a tool-using agent makes passes through the same proxy, so per-team cost tracking and egress policy have somewhere to attach. Environments come with their own egress policies and their own cost limits, which is the feature that matters when more than one team shares a deployment.
Identity is treated as part of the data path rather than a wrapper. SSO covers OIDC, SAML, Okta and Entra. The MCP gateway adds OAuth plus On-Behalf-Of flow, so a tool call executes as the calling user instead of as one shared service account holding every permission. For an agent platform that difference decides whether an audit log means anything.
Dual-LLM and Lethal Trifecta guardrails check calls before the tool runs
Guardrails here are deterministic rules on tool calls, and the README makes a pointed claim that they are part of the foundation rather than bolted on. Two named pieces do the work: tool call guardrails and Lethal Trifecta protections aimed at the combination of private data access, untrusted content and outbound communication.
Sandboxed code execution sits beside the guardrails rather than inside them, and agents get a Kubernetes-native filesystem. So the containment boundary is the pod, and the policy boundary is the gateway. Neither replaces the other.
One docker run starts the UI, the proxy and Postgres, and mounts the Docker socket
The quickstart is a single image with two published ports already bound to loopback, one environment variable, and three volumes:
docker pull archestra/platform:latest

docker run \
  -p 127.0.0.1:9000:9000 -p 127.0.0.1:3000:3000 \
  -e ARCHESTRA_QUICKSTART=true \
  -v /var/run/docker.sock:/var/run/docker.sock \
  -v archestra-postgres-data:/var/lib/postgresql/data \
  -v archestra-app-data:/app/data \
  archestra/platform:latest
Open http://localhost:3000 afterwards and you land in the UI. The command also publishes port 9000.
Two details in that command deserve a second look. Both port bindings are pinned to 127.0.0.1, so nothing is reachable from another machine until you change them yourself. And the command mounts /var/run/docker.sock, which grants the container control over the Docker daemon on the host. That is a large privilege for a quickstart, and it is there so the platform can manage the workloads it orchestrates. Anyone evaluating this should decide early whether they accept that mount on a shared host.
Why the quickstart container is not the container you ship
The Docker tag archestra/platform:latest points at the newest build, and the newest build is usually a preview rather than the patched line. That means the quickstart command above hands you preview code on your first run, and the quickstart is what most people copy.
Here is the catch a skim misses. Work lands on main first and only fixes are carried back to the supported branch, so a feature you see in one build can wait a long time for the line you actually pinned. Choosing which line to sit on is the first operational decision this project forces on you.
Docker is the demo path. The README points at Helm and Kubernetes for anything else, and names the Helm chart as the recommended production route.
The orchestrator promotes MCP servers between environments without an operator
The MCP registry is where teams publish their own tools, and the orchestrator is a Kubernetes operator that acts on them. Self-serve promotion is the mechanism worth understanding: a published tool moves between environments, each with its own egress policy and cost limits.
That is the right shape for an internal platform team shipping tools to hundreds of users.
A2A triggers and webhook triggers extend the same idea to agents talking to agents, and there is a migration kit in the repository aimed at teams already running single-tenant agents such as Claude Cowork, OpenClaw or Hermes.
What sits in the repository root, and what an upgrade drags along
The last push to main landed on 2026-11-02, so the tree is moving rather than sitting still.
The repository root tells you what an upgrade actually touches. platform/ holds the server itself. ai-labs/ and docs/ sit beside it, mcp-catalog/ sits beside them, and migration-kit/ exists for moving single-tenant agents onto the platform. AGENTS.md and the .claude/ and .codex/ directories point at agent-assisted development, which fits a project that markets itself to agent builders. LICENSE.md, LICENSE_AGPL and LICENSE_ENTERPRISE sit at the root as separate documents, so read the three side by side rather than assuming one applies to the whole tree.
Cost follows headcount rather than feature access. Teams under 30 users sit in the free Open Core tier, and enterprise licensing applies above that, so count every colleague who touches the UI, not just the platform engineers.
What Archestra asks for, and what a plain proxy does not
The honest alternative is a thin LLM proxy in front of your providers. Tools such as a reverse proxy or a cost-tracking wrapper give you key abstraction and spend reporting. The difference in approach is scope: Archestra treats the agent runtime, the tool registry and the identity layer as one product, so a tool call is observable and attributable end to end, at the cost of adopting a platform rather than a library.
That trade only pays off if the pieces are actually connected in your case. If your team wants a spend dashboard and already has a registry and an identity provider wired up, Archestra duplicates work you have done. The parts a plain proxy does not obviously serve are the deterministic tool call guardrails and the self-serve environment promotion; those are where the platform earns its weight.
The cost of saying no is real too. Once agents run unattended against production data, the absence of one audit trail across providers, tools and users tends to get noticed later, at higher price.
Editorial conclusion
Adopt Archestra if you already run coding agents across Claude Code, Codex or Cursor and need one auditable gateway with per-team cost limits and an MCP registry. Do not adopt it for a single-team proof of concept: the Kubernetes dependency and the platform surface both assume an enterprise operator. Verify first what the archestra/platform:latest tag currently resolves to on your machine, since the quickstart defaults to the newest build rather than the patched one, then check whether the Docker socket mount survives your security review before anything else.
Frequently asked questions
What is archestra AI?
Archestra is an open source enterprise AI platform that bundles an LLM gateway, an MCP gateway, a private MCP registry, an orchestrator and an agent runtime into one image. It runs under a TypeScript codebase with a platform/ directory and ships as archestra/platform.
what is archestra ai
It is a platform for running AI agents with guardrails and observability built in, rather than added later. That includes SSO and RBAC, sandboxed code execution, Lethal-Trifecta guardrails, OpenTelemetry traces and Prometheus metrics.
what is archestra software
On the software side the project runs as a Docker image with the UI on port 3000 and port 9000 also published, with a Postgres data volume. Production deployments are directed to the Helm chart and Kubernetes instructions.
Official sources
Where developers are discussing it
Posts on Hacker News, dev.to and Lobsters that link to this repository, found by our scan of those communities. 1 in the last 30 days; newest first.
- Archestra 1.4: OpenAPPA and Self Hosted Runtime for Claude Code and CodexHacker News · Oct 21, 2026 · 8 points · 0 comments
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/archestra-ai-archestra)Star history chart for your README
[](https://hysenlabs.com/projects/archestra-ai-archestra)Was this useful?