Hx0 HawkEye: A Browser-Sidebar Packet Capture and AI Security Audit Extension
A lightweight browser extension for traffic capture and security analysis, enabling capture, interception, modification, replay, rule-based detection, and AI-assisted analysis, all from the browser sidebar.
At a glance
- What is it?
- Hx0 HawkEye is a Chrome and Firefox extension that moves HTTP and WebSocket capture, interception, replay, fuzzing, and AI-assisted analysis into a sidebar, avoiding system proxy configuration. The v1.0.6 release adds a browser automation MCP and a browser-level agent for pro users.
- Who is it for?
- Adopt Hx0 HawkEye if you are a developer or security tester doing authorized API audit, debugging, or initial screening inside a real browser session and you want to avoid system proxy and certificate setup. Do not adopt it if you need full proxy-level transparency, deep TLS inspection, or team-scale collaboration, because it only sees page-context traffic.
- Can I use it commercially?
- Not without permission. GitHub finds no licence file in the repository, and without a licence all rights are reserved by default: you may read the code but not reuse it. Check the README, or ask the authors, before using it.
- Is it still maintained?
- Yes. The repository last received commits 11 days ago.
- What is it written in?
- GitHub does not report a main language for this repository.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
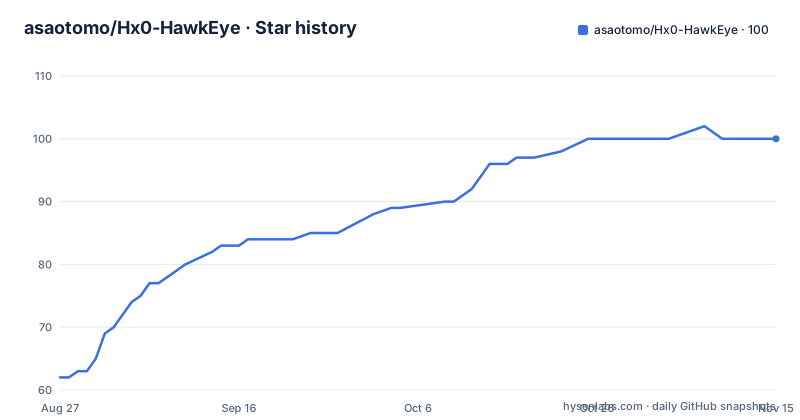
- asaotomo/Hx0-HawkEye100 ★ · +38
| Repository | 2026-08-27 | 2026-11-15 |
|---|---|---|
| asaotomo/Hx0-HawkEye | 62 | 100 |
38 Stars in the last 80 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What It Solves: The Session Consistency Problem
Traditional proxy tools like Burp Suite require changing the system proxy, trusting a root certificate, and often lose the cookie and login state that the browser tab holds. Hx0 HawkEye is a native browser extension that intercepts fetch and XHR traffic directly in the page's main world, so requests and responses carry the same origin and login session as the current tab. The README states this eliminates the common 'proxy drops cookie' and 'frequent login loss' pain points. The tool is aimed at engineers who switch between a real browser session and packet inspection during daily development, API troubleshooting, and authorized security screening. It does not replace a full proxy for deep TLS interception, but it removes the setup overhead for page-level traffic.
How It Works: Page-World Injection and IndexedDB History
The extension hijacks fetch and XHR in the page's main world to record requests and responses, including bodies, with capacity protection. WebSocket handshakes (such as GET 101) and data frames (OUT and IN) are recorded when enabled. History is persisted in IndexedDB, with filters for type, host, method, status code, sensitive hits, and search. The interceptor queues HTTP requests and, when rules match, WebSocket outbound and inbound frames, allowing edit, forward, or drop from the sidebar. Replay works by editing the raw request and sending it again; for WebSocket, the replay uses an already OPEN connection in the page to send outbound frames, not a new handshake. This design keeps everything inside the browser context, which is both the strength and the boundary.
Getting It Running: Install, Configure, and First Use
The README does not provide explicit installation commands, but as a browser extension, you load it from the Chrome Web Store or Firefox Add-ons, or load an unpacked build from the repository for development. The default branch is main, and releases are tagged v1.0.4 through v1.0.6. After installation, you enable capture in the sidebar, optionally select WebSocket, and set target domain or IP filters. For AI features, you must configure a model endpoint: the README lists support for OpenAI, DeepSeek, local LM Studio, and custom Base URL, all using an OpenAI-compatible style. Data is sent only to the endpoint you configure (BYOK). The community edition covers basic capture, history, detail view, ordinary replay, WebSocket frame replay, and basic encoding. Pro features like page replay, fuzzing, AI analysis, and the agent require a license or a 30-minute trial.
The v1.0.6 Pro Additions: MCP and Browser-Level Agent
The latest release adds two pro-only capabilities. The first is a browser automation MCP server, described as a security-focused Playwright MCP. It exposes browser navigation and HawkEye tools (capture, replay, mutation, encoding, and evidence) to agent hosts like Codex, Cursor, and LM Studio, over stdio, Streamable HTTP, or legacy SSE. The second is a browser-level agent that plans and executes multi-step tasks in the user's real tab and login state, interacting with complex controls and iframes, performing capture analysis, replay verification, web research, and native downloads. The README explicitly states the agent mode only works under a valid trial or pro license. This is a significant expansion from a simple packet viewer to an automation platform, but it also means the pro tier is where the interesting new value sits.
Genuine Limitations and Wrong-Tool Cases
The most obvious limitation is that the extension only sees page-context traffic. It cannot capture traffic from other processes, non-browser applications, or requests that bypass the page's fetch and XHR. The README mentions a 'smart proxy diverter' in community edition that forwards matched requests to Burp or Yakit, but that is a forwarding feature, not a full replacement. WebSocket replay depends on an existing OPEN connection in the page; if the connection is closed, replay fails. The AI features are pro-only and require a configured endpoint, so without a license or API key, you lose fuzzing, AI analysis, and the agent. Also, the README notes differences between Chrome and Firefox in sidebar hosting and HTTPS helper options, which means behavior is not identical across browsers. For a team needing centralized logging or multi-user collaboration, this extension is not the right tool.
Alternative: Burp Suite and the Proxy Approach
The direct alternative is a traditional intercepting proxy like Burp Suite. Burp operates at the network level, requiring system proxy and certificate trust, but it sees all traffic from the browser and other clients, supports complex matching and replacement rules, and has a mature ecosystem for extensions and automation. The core difference is the interception point: Burp sits between the browser and the server, while HawkEye hooks inside the page. This means Burp can handle non-browser traffic and TLS inspection, but it struggles with session consistency, as the README points out. HawkEye sacrifices breadth for convenience and session fidelity. If you need to test a mobile app or a desktop client, HawkEye is useless; Burp is the proven choice. If you are debugging a SPA's XHR calls, HawkEye's page-context capture is faster to set up.
Maintenance, Licensing, and Upgrade Cost
The repository does not declare a license, which is a red flag for adoption. You should check the repository files for a LICENSE before using it in a commercial context. The project is actively maintained, with releases in June and August 2026. The community edition is free, but pro features require a license or a 30-minute trial that automatically reverts to community. Upgrade cost is not monetary for the community tier, but there is a functional cost: as of v1.0.6, the smart proxy diverter and full deep search are open to community, yet AI, fuzzing, and the agent are locked. The README also mentions performance refactors in v1.0.6 for Firefox and Chrome, including single-pass DOM snapshotting and dynamic webRequest listener registration, which suggests ongoing maintenance effort. Before adopting, verify the license and whether the pro tier's recurring cost fits your budget.
Editorial conclusion
Adopt Hx0 HawkEye if you are a developer or security tester doing authorized API audit, debugging, or initial screening inside a real browser session and you want to avoid system proxy and certificate setup. Do not adopt it if you need full proxy-level transparency, deep TLS inspection, or team-scale collaboration, because it only sees page-context traffic. Verify first whether the 30-minute pro trial covers your workflow, whether your AI endpoint is compatible with the OpenAI-style API, and whether the Firefox-specific proxy modes match your environment. The project's value is real but bounded by the browser extension model.
Frequently asked questions
What is Hx0 HawkEye?
It is a lightweight security workbench extension for Chrome, Firefox and mainstream Chromium browsers. It works inside your real tab and login state and unifies capture and interception with modification including WebSocket, traffic replay, micro fuzzing, sensitive information and hidden link detection, AI security audit, MCP and a browser level agent.
Does Hx0 HawkEye need Burp or a system proxy for basic capture?
No. Basic capture works without opening Burp, without changing the system proxy and without configuring Java. Optional MCP access is the part that needs Node.js installed separately.
What can the community edition of Hx0 HawkEye do?
It covers the everyday chain: capture with basic WebSocket observation, detail view, ordinary replay including WebSocket frame replay, and basic codec work, plus intercept and modify for HTTP and for WebSocket frames that match a rule. PRO adds in-page replay and fuzz, micro fuzzing, userscripts, AI, the AI task desk, Skills, hidden links and the batch workbenches.
How do I install Hx0 HawkEye?
The repository root carries the official Chrome and Firefox 1.0.6 release ZIP files alongside the Chinese and English READMEs. Upgrading means replacing the extension and the MJS file and restarting the MCP Host. The product page is at hx0.store/products/hawkeye.
How does Hx0 HawkEye connect an AI agent host?
Through its PRO MCP: once a host such as Codex, Cursor or LM Studio connects hx0-hawkeye, the model can call browser and HawkEye tools to control real tabs, over stdio, Streamable HTTP or legacy SSE. The local MCP server is at 1.0.13, and the standalone hawkeye-mcp-server.mjs stays directly runnable for troubleshooting while the extension scripts inside the ZIP are obfuscated.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/asaotomo-hx0-hawkeye)Star history chart for your README
[](https://hysenlabs.com/projects/asaotomo-hx0-hawkeye)Was this useful?