Authelia: a Go single sign-on and multi-factor portal, read through its Dockerfile, go.mod and release history
The Single Sign-On Multi-Factor portal for web apps, now OpenID Certified™
At a glance
- What is it?
- Authelia is an Apache-2.0 licensed login portal for web apps that adds single sign-on and multi-factor authentication, and it is OpenID Certified. Its repository shows a container that defaults to root identifiers, a source build pinned to Go 1.27, and a master branch that has moved on since the last tagged release.
- Who is it for?
- Authelia suits self-hosters who want an Apache-2.0, OpenID Certified login portal with multi-factor options in front of their web apps, deployed from the authelia/authelia Docker image, the AUR package or the bundled systemd units. It is a poor fit if you cannot run a container with explicit PUID and PGID overrides, or if you need fixes that have landed on master but not in a tag.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
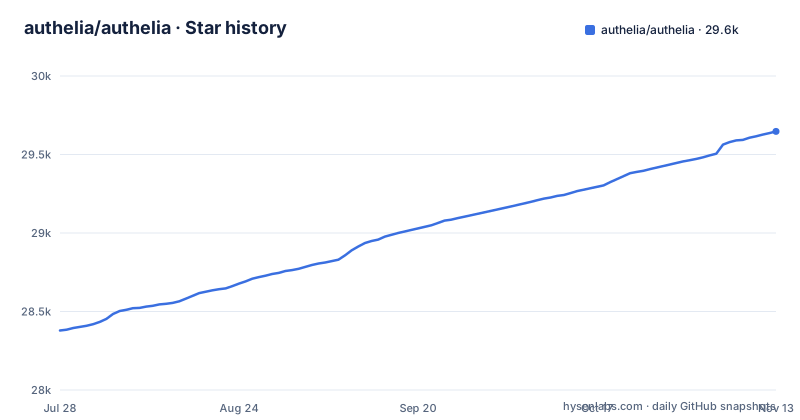
- authelia/authelia29,647 ★ · +1,268
| Repository | 2026-07-28 | 2026-11-13 |
|---|---|---|
| authelia/authelia | 28.4k | 29.6k |
1,268 Stars in the last 108 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
An OpenID Certified login portal that sits in front of web apps
Authelia describes itself as the single sign-on multi-factor portal for web apps, and it carries OpenID certification. In practice that means it is a separate service your applications defer to for login: users authenticate once at the Authelia portal, prove a second factor, and are then let through to the apps behind it. The codebase is Go, published as the module github.com/authelia/authelia/v4, which matches the v4.39.x release line. The repository also holds a web/ directory for the portal front end, an api/ directory, and a crowdin.yml file, so the login screens are translated through Crowdin rather than shipped in English only. The license is Apache-2.0, and the project takes sponsorship through Open Collective.
go.mod shows which identity and storage backends are compiled in
The dependency list is the most honest map of what the single binary carries. For user directories, go.mod pulls in github.com/go-ldap/ldap/v3. For second factors it includes github.com/authelia/otp for one time passwords, github.com/go-webauthn/webauthn v0.18.2 for WebAuthn security keys and passkeys, and github.com/duosecurity/duo_api_golang for Duo push. For persistence it links three SQL drivers: github.com/jackc/pgx/v5 for PostgreSQL, github.com/go-sql-driver/mysql, and github.com/mattn/go-sqlite3. The OpenID side runs on authelia.com/provider/oauth2 v0.3.3 and github.com/golang-jwt/jwt/v5. Password strength checks use github.com/trustelem/zxcvbn, the HTTP layer is github.com/valyala/fasthttp with fasthttp/session, and metrics go out through github.com/prometheus/client_golang, which pairs with the examples/grafana-dashboards/ folder.
The container reads /config/configuration.yml and listens on 9091
The official Dockerfile is short and sets the contract for every container deployment. It sets X_AUTHELIA_CONFIG to /config/configuration.yml, so the process looks for its configuration in a /config directory you must mount. It exposes port 9091, which is the port your reverse proxy or browser has to reach. The entrypoint is /app/entrypoint.sh, and a HEALTHCHECK runs /app/healthcheck.sh every 30 seconds with a 3 second timeout and a one minute start period. Configuration is parsed through koanf, with YAML, TOML and JSON parsers plus environment and command line flag providers listed in go.mod. The full set of keys starts from config.template.yml at the repository root, and a working stack layout is in examples/compose/.
PUID and PGID default to 0 in the official image
The same Dockerfile sets PUID=0 and PGID=0 as environment defaults. Unless you override them, the image's user and group identifiers point at root. For a service whose job is guarding logins to everything else on your network, that default deserves attention on day one rather than after an audit.
The consequence for readers is a deployment task, not a theoretical risk: set PUID and PGID to an unprivileged account in your compose file or orchestrator, and make sure that account can read the mounted /config directory and write wherever your SQLite file or logs live. If you skip this, the container still starts and passes its health check, so nothing in the default setup will warn you that the portal is running with root identifiers.
Packaging spans Docker Hub, AUR, systemd and rc.d
Authelia is self-hosted, and the repository ships several deployment paths side by side. The container image is published on Docker Hub as authelia/authelia. Arch Linux users have an AUR package named authelia. For bare metal installs, the root of the repository contains authelia.service and a templated [email protected] for systemd, along with authelia.sysusers.conf and authelia.tmpfiles.conf for creating the service user and its directories, plus an rc.d script named authelia-fb-rc.d. Release binaries are built with GoReleaser, configured in .goreleaser.yml, and attached to GitHub releases.
There is no single copy and paste install command at the top of the repository. Pick the path that matches your host, then start from config.template.yml and the docs at authelia.com.
Building from source requires the Go 1.27 toolchain
go.mod declares go 1.27.0 and pins toolchain go1.27.3. Anyone compiling Authelia from a clone, or packaging it for a distribution, needs that toolchain or newer. Older Go releases shipped by long term support distributions will refuse to build the module, and with toolchain switching disabled the build stops rather than fetching a newer compiler.
This matters most for people who avoid containers and prefer building on the host. The practical alternatives are the prebuilt release binaries, the AUR package, or the container image. The repository also contains Dockerfile.dev and Dockerfile.coverage for development and coverage builds, and a bootstrap.sh script, but those are contributor tooling rather than a supported route around the Go version floor.
Master has moved on since v4.39.28
The last three tags arrived close together: v4.39.26 on 2026-09-12, v4.39.27 on 2026-09-15 and v4.39.28 on 2026-09-17. Commits kept landing afterwards, with the latest push to master on 2026-11-02. The project is plainly active, but there is a gap of roughly seven weeks between the newest tag and the newest commit.
For operators this has a concrete effect. A fix or dependency bump that is on master is not in the image or binary you pull by version tag until a new release is cut. If you are tracking a specific issue, check whether its fix is inside a tagged release before assuming an upgrade to v4.39.28 resolves it. Running master builds to get it earlier means running code that has not gone through a release.
Supply chain checks are wired into the repository itself
For a security component, the project advertises a set of external checks: an OpenSSF Best Practices gold badge, an OpenSSF Scorecard, SLSA level 3, Codecov coverage and Buildkite CI. The tree backs those badges with files: .grype.yaml for container vulnerability scanning, osv-scanner.toml for dependency advisories, a .trufflehog configuration for secret scanning, .golangci.yml for linting, REUSE.toml and a LICENSES/ folder for license compliance, and a SECURITY.md for reporting vulnerabilities. The official image is built FROM authelia/base pinned by both tag and sha256 digest.
None of that replaces your own review of how you configure it. These signals say the build process is controlled; they do not say a given configuration is safe, and a root default or a weak policy in configuration.yml stays your responsibility.
Editorial conclusion
Authelia suits self-hosters who want an Apache-2.0, OpenID Certified login portal with multi-factor options in front of their web apps, deployed from the authelia/authelia Docker image, the AUR package or the bundled systemd units. It is a poor fit if you cannot run a container with explicit PUID and PGID overrides, or if you need fixes that have landed on master but not in a tag. Before deploying, read config.template.yml end to end, set PUID and PGID, mount /config, and confirm which v4.39.x release you are pulling.
Frequently asked questions
What is Authelia used for?
Authelia is a single sign-on and multi-factor authentication portal for web apps. Users log in once at the portal and pass a second factor before reaching the applications behind it, and the project is OpenID Certified.
Is Authelia free and open source?
Yes. Authelia is released under the Apache-2.0 license with its source on GitHub, and the project accepts financial support through Open Collective.
Can Authelia be self-hosted?
Yes. It is distributed as the authelia/authelia Docker image, an AUR package, GoReleaser built binaries, and systemd unit files in the repository root.
How do I install Authelia with Docker?
Pull the authelia/authelia image from Docker Hub, mount a /config directory containing configuration.yml, and expose port 9091. The examples/compose/ folder in the repository holds compose layouts, and you should set PUID and PGID because both default to 0.
Is Authelia secure?
Authelia holds an OpenSSF Best Practices gold badge, SLSA level 3 and OpenID certification, and it publishes a SECURITY.md for vulnerability reports. Your deployment still depends on your configuration, including overriding the root PUID and PGID defaults in the container.
Official sources
Where this project is recommended
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/authelia-authelia)Star history chart for your README
[](https://hysenlabs.com/projects/authelia-authelia)Was this useful?