Automic Vault: a macOS secrets manager that gates what credentials do
The missing secrets manager for developers
At a glance
- What is it?
- Automic Vault moves developer-tool credentials into the macOS Data Protection Keychain and puts an authorization gate in front of each use. It is macOS-only, and the README is explicit that a clean scan is not a security certification.
- Who is it for?
- Adopt Automic Vault if your team works on macOS and you want per-operation approval over what agents and terminals can do with credentials, rather than a store that only hands secrets out. Do not adopt it if you need Linux or Windows coverage, or if you want a policy file that travels with the repository; the README states that repositories need no policy file, which means the policy lives on each Mac.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 3 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
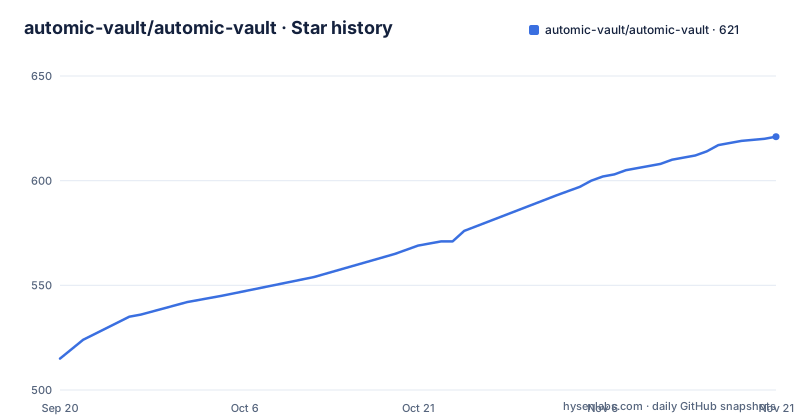
- automic-vault/automic-vault621 ★ · +106
| Repository | 2026-09-20 | 2026-11-21 |
|---|---|---|
| automic-vault/automic-vault | 515 | 621 |
106 Stars in the last 62 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The problem Automic Vault takes on: secrets managers that stop at delivery
Most secrets managers answer one question: is the secret stored safely, and can it reach its destination. The README states the position plainly: "Is the destination safe? That's your problem." Automic Vault is built on the claim that a secrets manager should know what a secret does, not just where it lives.
The target user is a developer on macOS who runs terminals, IDEs, coding agents, and project tooling that all reach for the same credentials. The README names agents specifically: they need no Automic Vault plugin, and repositories need no policy file. That design choice matters. If you have ever tried to get an autonomous agent to respect a credential policy, you know the failure mode is that the agent simply does not load your policy layer. Automic Vault instead intercepts the operation at the point where the credential would be released.
The scope is narrow on purpose. This is a macOS product, built around the Data Protection Keychain and macOS biometrics. Nothing in the README suggests a Linux or Windows path.
Detectors, Hardeners, and Authorization Gates: how the pieces fit
Three mechanisms carry the product.
Detectors check over 100 developer-tool configurations for what the README calls Exposures and Hazards: plaintext credentials, permissive Keychain items, and ambient credential helpers. Each Finding comes with a mitigation. Detectors inspect without changing your environment or requesting Secrets, which is why a scan is safe to run repeatedly. The README is careful about what a clean result means: it cannot certify that your machine is holistically secure.
Hardeners do the migration. They move supported credentials into Secret Custody in the macOS Data Protection Keychain and configure the tool's Authorization Gate. Depending on the tool, that is a credential helper, a wrapper, or an Isotope, which the README defines as an Automic Vault-compatible build of the tool. The README makes an argument for why hardening is possible at all: credentials could not be migrated if they were not already stored in an exposed state.
Authorization Gates are the interesting part. Before allowing an operation, Automic Vault checks the Verified Launcher, the tool, the target, the command, the arguments, the working directory, the Secret Names, and the selected value sources, on the Mac where the operation will run. The README gives a concrete example under Read Only access, where one GitHub token produces three different decisions: gh issue list is automatically authorized, gh issue create requires approval, and gh auth token is treated as Secret Disclosure and requires approval. Unknown operations require approval at every access level. The README also states the boundary: Automic Vault controls the handoff, and the target controls the secret after receiving it.
Installing Automic Vault and hardening your first tool
The README offers two install paths: download the latest release, or use Homebrew with the project's cask. The cask command is:
brew install --cask automic-vault/isotopes/automic-vault
open /Applications/Automic\ Vault.app
The first line fetches the cask from the automic-vault/isotopes tap. The second opens the app, which is where you complete any setup the app requires.
With the CLI available, the README's quickstart is three commands: scan for exposed credentials, harden a supported tool, then verify the result.
av scan
av harden gh
av doctor gh
av scan looks for Exposures and Hazards across supported tool configurations and reports Findings with mitigations. It does not change your environment. av harden gh moves GitHub's credentials into Secret Custody and configures the Authorization Gate for that tool. av doctor gh verifies the protection that was installed. Run doctor after hardening rather than assuming the migration took; that is the command whose output tells you whether the gate is actually in place.
The README notes that hardeners are not the only mechanism. Blessed Scripts, Launcher Bundles, the Secret Proxy, and Direct Secret Access exist for situations a Hardener does not cover, and the project points to docs/choosing-a-mechanism.md for picking between them. If av harden does not list your tool, that document is the next place to look rather than a workaround.
Where the model strains: local policy, local history, and a narrow platform
The most consequential limitation is the one the README treats as a feature. Repositories need no policy file. That means the authorization policy lives on each Mac, not in the repository. For a solo developer this is fine. For a team, it means there is nothing to review in a pull request and nothing to diff when someone changes an access level. Onboarding a new machine means reproducing the policy by hand.
Authorization History has hard ceilings that matter for audit work. It is stored locally as encrypted rows in one SQLite file with its key in the Data Protection Keychain. It is available for up to 30 days or 25 MiB of encrypted record payloads, whichever comes first. Replies over 1 MiB fail without truncation, so a broad query is not just slow, it fails, and the README's answer is to use a narrower window. If your retention requirement is a year, this is not the system that satisfies it.
Reading history is itself gated. Each read requires approval unless you grant that exact Verified Launcher Authorization History Access in Settings, and that is a separate setting from av list's Secret Name Access. An unverifiable launcher cannot use the grant and needs approval. The read also appears in the returned history, which is a reasonable design but means you cannot quietly inspect what an agent did.
Two more constraints. Recording failure denies release: if Automic Vault cannot persist and verify the record of an allowed secret use, the secret is not released. That is the right default for security and the wrong default for availability, and you should know which one you are choosing. And iPhone Approval changes the Mac's own controls: enabling it removes pointer- and keyboard-driven allow actions from that Mac. The README also warns that iPhone Mirroring and Show on Mac can put approval controls back onto a Mac when phone biometrics are off, so the security property depends on how those features are configured.
Automic Vault compared with HashiCorp Vault
HashiCorp Vault is the obvious comparison, and the two solve different halves of the problem. HashiCorp Vault is a server: it centralizes secret storage and issues credentials to clients that authenticate to it. Its unit of control is the secret and the identity requesting it. Automic Vault is a local macOS agent whose unit of control is the operation, evaluated against the launcher, tool, target, command, arguments, working directory, and secret names on the machine where it runs.
That difference shows up in what each can do. A central Vault can rotate a database credential for a fleet and give you one audit log across every host. Automic Vault cannot do either; its history is local, encrypted in a single SQLite file, and capped at 30 days or 25 MiB. Conversely, a central Vault has no opinion about whether gh issue create should be allowed while gh issue list is automatic, and no mechanism to require Touch ID for one specific release of one credential. Automic Vault does.
If you already run HashiCorp Vault, Automic Vault is not a replacement. It is closer to a local enforcement layer that sits between your shell or agent and the credentials already on your laptop. The README's own advice supports that reading: run supply-chain-sensitive operations like npm i in a separate terminal with no Automic Authorizations and no macOS TCC permissions. That is a containment strategy, not a centralization strategy.
Temporary grants and approvals: the part aimed at agent workflows
The feature that most clearly targets agents is Temporary Access Grants. An eligible Codex task or Claude Code session can request Allow Write Access for 10 Minutes. The grant is in-memory and covers one Verified Launcher, one tool-specific gate, and one agent task. A visible strip lets you add ten minutes, suspend access and its countdown, or end the grant outright.
The README is honest about the trust model here: the task identifier is a forgeable narrowing label, and the Verified Launcher remains the identity boundary. In other words, do not treat the task label as a security control. The grant also excludes direct secret access, secret mutations, elevated credential use, disclosure, and unknown operations, so a write grant is not a master key.
Approval has two biometric paths. Touch ID requires an active Mac session and awake displays, uses a fresh biometric result for that exact request, and has no password, Apple Watch, or pointer-driven fallback. It can coexist with iPhone Approval. iPhone Approval works across enrolled Macs from eligible iPhones on the same iCloud Keychain account, with each Mac keeping its secrets, policy, enforcement, and history local; the iPhone never receives secret values. The README's recommended starting posture is approval-required gates by default, read-only for agents, and write for your terminal, with the suggestion that a read-only terminal plus Blessed Scripts reduces approval fatigue.
Editorial conclusion
Adopt Automic Vault if your team works on macOS and you want per-operation approval over what agents and terminals can do with credentials, rather than a store that only hands secrets out. Do not adopt it if you need Linux or Windows coverage, or if you want a policy file that travels with the repository; the README states that repositories need no policy file, which means the policy lives on each Mac. Before rolling it out, verify two things on one machine: run av scan to see which of your tools it actually detects, and run av harden gh followed by av doctor gh to confirm the protection it installs survives your normal workflow. Then check the 30-day and 25 MiB history limits against how long your audit retention needs to reach.
Frequently asked questions
What is Automic Vault used for?
It is a macOS secrets manager for developer tools and agents. It scans supported tool configurations for exposed credentials, moves supported credentials into the macOS Data Protection Keychain, and checks the complete operation before applying a credential.
How do I install Automic Vault on macOS?
The README gives two paths: download the latest release, or install the Homebrew cask with brew install --cask automic-vault/isotopes/automic-vault and then open the app. After that, the quickstart is av scan, av harden gh, and av doctor gh.
Is Automic Vault safe to use?
The README states that a clean scan means no supported Detector found an issue and that it cannot certify your machine is holistically secure. It also states that recording failure denies release, so an allowed secret use is not released if its record cannot be persisted and verified.
Does Automic Vault work on Linux or Windows?
The README describes Automic Vault as a macOS secrets manager and builds its mechanisms on the macOS Data Protection Keychain and macOS biometrics. Nothing in the README describes a Linux or Windows path.
How long does Automic Vault keep authorization history?
History is stored locally as encrypted rows in one SQLite file with its key in the Data Protection Keychain, and is available for up to 30 days or 25 MiB of encrypted record payloads, whichever comes first. Replies over 1 MiB fail without truncation.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/automic-vault-automic-vault)Star history chart for your README
[](https://hysenlabs.com/projects/automic-vault-automic-vault)Was this useful?