Agentic Bug Hunter: an AI recon and reporting toolkit for HackerOne and Bugcrowd
AI-powered bug bounty hunting toolkit that works with or without subscription.
At a glance
- What is it?
- Agentic Bug Hunter is an MIT-licensed Python toolkit that runs reconnaissance, vulnerability testing and report writing from the terminal, with a standalone mode that needs no subscription. The interesting part is the validation gate.
- Who is it for?
- Adopt it if you already run a bug bounty workflow on HackerOne or Bugcrowd and want recon, validation and report drafting in one terminal tool under a permissive licence. The README says a fully offline setup is possible with Ollama as a local provider.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 3 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
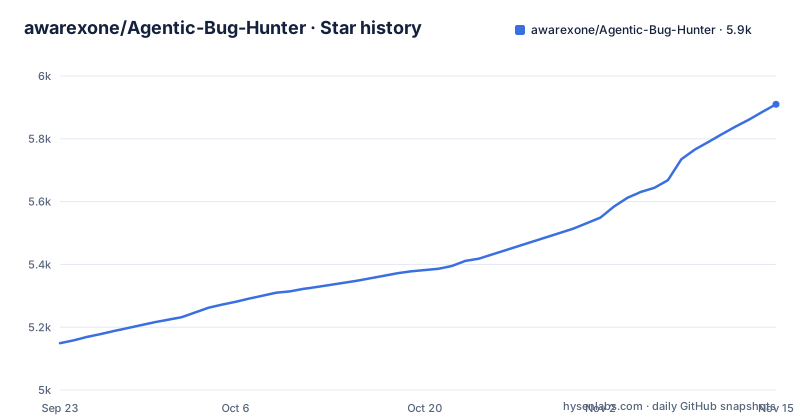
- awarexone/Agentic-Bug-Hunter5,910 ★ · +761
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| awarexone/Agentic-Bug-Hunter | 5.1k | 5.9k |
761 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What Agentic Bug Hunter is for, and who it is not for
The README frames the project around one claim: it finds "real, reportable bugs, not theoretical ones." That is a positioning statement aimed at a specific frustration. Recon tools produce long lists of hosts, endpoints and parameter names. Turning that list into a submission that a triage team accepts is separate work, and it is the work most tools skip. Agentic Bug Hunter tries to cover the whole path: point it at a target, and per the README it runs recon, tests for vulnerabilities, validates findings against a gate, and writes a report for HackerOne, Bugcrowd, Intigriti or Immunefi.
The intended user is a working bug bounty hunter or a small security team that already participates on those platforms. The repository layout supports that reading: there are directories for rules, skills, commands and hooks, plus a web3 directory and a netflix-privacy-analysis directory. The presence of platform names in the README suggests the author targets people who file reports, not people who want a general-purpose scanner.
It is a weaker fit for teams that need a CI-friendly static analysis tool or an authenticated application scanner with a stable rule engine. It is also a poor fit for anyone who wants a tool with no external dependencies at all: the requirements file lists requests, pytest and mcp, so the core install pulls in a Model Context Protocol library.
How the pipeline works: recon, validation gate, report
The mechanism the README describes is a four-stage chain. Recon collects the attack surface. Testing probes for vulnerabilities. A validation step then filters candidates against what the README calls "a strict gate." Only what survives that gate becomes a report draft for one of the four platforms.
The gate is the part worth attention. Version 5.0.0 is titled "False Positive Reduction + Repository Polish," which tells you the author treats noise as the main failure mode of AI-assisted hunting. That is the right instinct. A model that reports every reflected parameter as a finding produces a submission queue nobody wants to read, and repeated low-quality submissions get a hunter's reputation downgraded on the platforms. A validation stage that discards weak candidates is the difference between a useful tool and a report generator.
The repository layout hints at how the pieces connect. The bughunter/ package sits at the top level, with commands/, skills/, rules/ and hooks/ alongside it. The mcp dependency in requirements.txt indicates the project speaks the Model Context Protocol; the README says it works as a Claude Code plugin, and the repository carries a .claude-plugin/ directory. The README also claims it "remembers everything: patterns found on one target inform the next," and says output lands in ~/.bughunter/.
Version 6.0.0 is titled "Provider Freedom," and the description says the toolkit works "with or without subscription." That is the release that matters most for cost planning. The standalone mode is linked from the top navigation as "Free Setup," and the README says it needs no paid subscription: `bughunter setup` connects a free AI provider, with Ollama listed as free and running locally.
Installing Agentic Bug Hunter and running a first target
The README's quick start installs the CLI with `uv tool install agentic-bug-hunter` (or `pipx install agentic-bug-hunter`) and then runs `bughunter setup`; the standalone route is `./install.sh --agent standalone` from a clone. pyproject.toml sets requires-python to >=3.10. The dependency list in requirements.txt is short enough to read before you commit. It contains three entries: requests, pytest and mcp. mcp is constrained only by a minimum version (mcp>=2.2.0), so a fresh environment can resolve to a newer release than the author tested against. If you want the environment reproducible, pin it yourself in a local constraints file rather than editing requirements.txt.
The repository also ships install_tools.sh and uninstall_tools.sh, which suggests external recon binaries are fetched separately from the Python package. The README says full recon also uses subfinder, httpx, nuclei, katana, ffuf and nmap, installed with install_tools.sh.
The repository ships config.example.json, and the README says `bughunter setup` saves provider configuration in ~/.bughunter/config.json, which the installer preserves on reruns. On the same pass, read TERMS.md. A tool that sends traffic at third-party targets has usage conditions attached, and they are in the repository rather than the README.
For a first run, the README's own framing is the guide: point it at a target you are authorised to test, and expect recon output before anything else. Use a program you have already joined on HackerOne or Bugcrowd, because the report stage writes for those platforms. Before you trust a draft, open the target's scope page and check that the host you tested is in scope.
The validation gate is the selling point, and the least documented part
Everything in the README rests on the claim that the gate works. If it does, the tool saves the hours between "I think this endpoint is interesting" and "here is a submission." If it does not, you have a scanner that generates plausible-looking findings, which is worse than no scanner because it costs reviewer time and your reputation on the platform.
The evidence for the gate is a release title, a README sentence and the `bughunter validate` command, which the README labels a "7-Question Gate". There is a tests directory, a pytest.ini and a GitHub Actions workflow referenced by the tests badge, so there is some automated checking in the repository. What those tests cover is not described. Whether the gate is a set of deterministic rules under rules/, a model-based judge, or a combination is not stated. That matters because a deterministic gate is auditable and a model-based gate inherits the model's opinions.
The memory feature raises a related question the README does not answer. If patterns from one target inform the next, the tool accumulates state across programs. Bug bounty platforms generally expect findings to be reported to the program that owns the asset, and a memory store that mixes targets is a data handling question, not just a technical one. Check how retention and per-program isolation are handled before you point the tool at a second program.
Agentic Bug Hunter versus a scripted recon pipeline
The obvious alternative is the traditional approach: chain subdomain enumeration, HTTP probing, content discovery and a scanner, then triage by hand. Tools in that space are mature, deterministic and cheap to run repeatedly. Their output is a list of candidates, and the hunter decides what is real.
The difference in approach is where judgement sits. A scripted pipeline puts judgement entirely with the human and optimises for coverage. Agentic Bug Hunter puts a validation stage between discovery and reporting, optimising for precision at the cost of transparency. You get fewer candidates, but you also get less visibility into why a candidate was dropped.
That trade is defensible for solo hunters whose bottleneck is writing reports, not finding hosts. It is a worse trade for teams that need to explain a finding to a client or reproduce a result months later, because a gate you cannot inspect is hard to defend in a post-mortem. It is also a worse trade for anyone whose recon needs are unusual, since a fixed pipeline is harder to reorder than a shell script.
The project's own history points at the same tension. Version 4.0.0 added a Meme Coin Security Module, which is a narrow addition aimed at web3 targets. That suggests the author is willing to add domain-specific paths rather than keep the pipeline generic. Whether that breadth helps or dilutes the core gate is a judgement the README does not make for you.
Licence, maintenance and upgrade cost
The project is MIT-licensed, and the LICENSE file is at the top level. MIT is permissive: you can use it commercially, modify it and redistribute it, provided the copyright notice and permission notice travel with the code. That is the whole obligation, and it is why the licence is unlikely to block adoption inside a company.
The licence does not cover what you do with the output. Reports you generate go to a platform under that platform's terms, and the target's scope rules apply to your traffic. The repository carries a separate TERMS.md, which the README does not summarise. Read it before running the tool against anything you do not own.
Maintenance is the weaker signal. The last push was on 2026-10-28, so the repository is not dormant. Three major releases landed between April and August 2026: v4.0.0 on 2026-04-13, v5.0.0 on 2026-06-09 and v6.0.0 on 2026-08-21. A major version every two months is fast, and fast major releases mean upgrade work. The v6.0.0 title, "Provider Freedom," implies configuration changes around model providers, which is exactly the kind of change that breaks a working setup.
For upgrades, the README says to rerun the same install command after pulling updates; the installer refreshes the bughunter command while preserving your saved provider configuration in ~/.bughunter/config.json. The go.mod file adds a separate wrinkle: it notes that tags v1 through v6 were published under the old github.com/shuvonsec/claude-bug-bounty path and recorded as incompatible, and that new consumers should depend on github.com/awarexone/Agentic-Bug-Hunter. If you have tooling pinned to the old module path, that is the rename to plan for.
Editorial conclusion
Adopt it if you already run a bug bounty workflow on HackerOne or Bugcrowd and want recon, validation and report drafting in one terminal tool under a permissive licence. The README says a fully offline setup is possible with Ollama as a local provider. Before installing, read config.example.json and TERMS.md, then run `./install.sh --agent standalone` or `uv tool install agentic-bug-hunter` and confirm the Python 3.10+ requirement against your interpreter.
Frequently asked questions
Does Agentic Bug Hunter require a paid subscription?
The repository description says the toolkit works with or without subscription, and version 6.0.0 is titled Provider Freedom. The README says standalone mode needs no paid AI subscription: `bughunter setup` connects a free provider, and Ollama runs locally for free.
Which bug bounty platforms can Agentic Bug Hunter write reports for?
The README names HackerOne, Bugcrowd, Intigriti and Immunefi as report targets.
What Python version does Agentic Bug Hunter need?
pyproject.toml sets requires-python to >=3.10. The requirements file lists requests, pytest and mcp.
How do I install Agentic Bug Hunter?
The README's quick start is `uv tool install agentic-bug-hunter` (or `pipx install agentic-bug-hunter`) followed by `bughunter setup`; from a clone, `./install.sh --agent standalone` installs the standalone command. install_tools.sh installs the external recon tools subfinder, httpx, nuclei, katana, ffuf and nmap.
Is Agentic Bug Hunter the same as claude-bug-bounty on GitHub?
The go.mod file states that release tags v1 through v6 were published under the pre-rename path github.com/shuvonsec/claude-bug-bounty and recorded by the Go module proxy as incompatible. New consumers are directed to github.com/awarexone/Agentic-Bug-Hunter.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/awarexone-agentic-bug-hunter)Star history chart for your README
[](https://hysenlabs.com/projects/awarexone-agentic-bug-hunter)Was this useful?