Betterleaks: A Secrets Scanner That Filters by Context, Not Just Regex
Scan the world (for secrets). | New Sources | Support for sources like GitHub, GitLab, Hugging Face, S3, and more.
At a glance
- What is it?
- Betterleaks is a Go-based secrets scanner from the Gitleaks team that adds Expr-based filtering, async validation, and token-efficiency checks to cut false positives. It scans git repos, filesystems, and cloud sources like GitHub, GitLab, Hugging Face, and S3.
- Who is it for?
- Adopt Betterleaks if you need a secrets scanner that goes beyond regex matching, especially if you manage many repositories and want to filter false positives with contextual logic. Do not adopt it if you prefer a simple, out-of-the-box tool with minimal configuration, because Betterleaks expects you to write Expr filters and maintain your own config.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
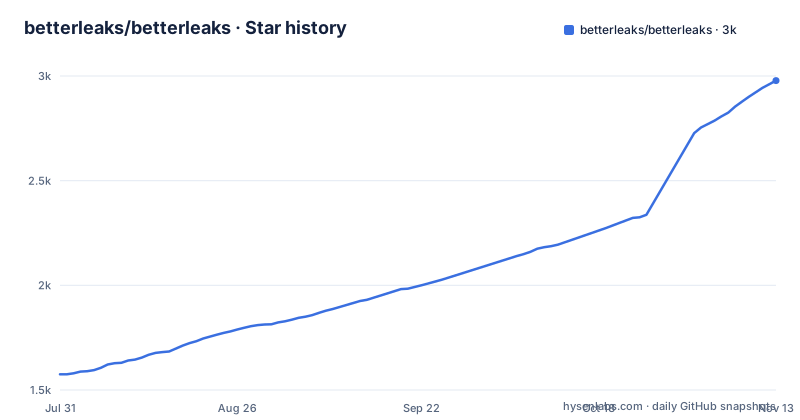
- betterleaks/betterleaks2,978 ★ · +1,403
| Repository | 2026-07-31 | 2026-11-13 |
|---|---|---|
| betterleaks/betterleaks | 1.6k | 3k |
1,403 Stars in the last 105 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What Betterleaks Solves and Who It Is For
The project is written in Go and distributed as a small binary. The README claims portability across modern OS and architecture. The core value is not just finding secrets but filtering out the non-secrets, which the blog post titles hint at: 'Regex is all you need' and 'Rare Not Random'. That framing tells you the project is opinionated about detection methodology, not just a wrapper around existing tools.
The Detection Engine: Prefilters, Filters, and Expr
The filtering logic is written in Expr, a language that the README says is more expressive than the old CEL-based system. CEL configs are still accepted for compatibility, but new configs should use Expr. This is a deliberate trade-off: you get more power but you have to learn a new syntax. The README also describes multipart rules, where a primary rule declares component rules and reads their secrets through expressions like components['rule-id']?.secret. This allows detecting secrets that are split across multiple fields or files. The detection engine is the core of the project, and the blog posts linked in the README go deeper into how it works, but the README itself gives enough to understand the data flow: attributes in, prefilter, regex, filter, validation.
Scanning Sources: Git, Files, GitHub, GitLab, S3, and More
The source list is a differentiator. Most secrets scanners focus on git history or filesystem. Betterleaks extends to cloud and platform sources, which matters if you want to scan for leaked secrets across an entire org or a Hugging Face model repository. The README says it is easy to add new sources, but does not detail the interface. That is a gap you would need to check in the docs or source code.
Installation and Getting Started
A basic scan is one command: 'betterleaks git /path/to/repo -v --source-workers=16'. The -v flag is verbose, and --source-workers controls parallelism. The README mentions sane default parallelization, so you can adjust workers for large scans. For a filesystem scan, 'betterleaks dir /path/to/file/or/dir -v'. The config file is betterleaks.toml, and the README recommends maintaining your own config in production rather than extending the default upstream config. That is a maintenance point: you want stable rules across upgrades, and you want to review new upstream rules before adopting them. The README also points to a web playground at betterleaks.com/playground for testing rules.
Validation and Token Efficiency: Two Unusual Filters
Second, token efficiency filtering: the scanner uses BPE tokenization to measure how 'rare' or non-human a string is. The idea is that natural language text is common and thus has low token efficiency, while a real secret like a long random string is rare. This is a heuristic, and the README does not explain the threshold or how to tune it. It is a clever approach, but it could also filter out legitimate secrets that happen to look like prose, or keep false positives that are random-looking but not secrets. The blog post 'Rare Not Random' likely explains the math, but the README does not.
Limitations and When It Is the Wrong Tool
It is the wrong tool if you need a zero-config scanner that just reports matches. Betterleaks expects you to invest in config. It is also not ideal if you want to scan a single file quickly without setting up a config, though the dir command works for that. The README does not mention any built-in reporting or dashboard, so you would need to integrate with other tools for that.
Alternatives: Gitleaks and TruffleHog
Another alternative is TruffleHog, which also scans for secrets across git history and has its own verification mechanisms. TruffleHog uses a different approach: it looks for high-entropy strings and then verifies them against known APIs. Betterleaks relies on regex plus contextual filtering and validation. The difference is that TruffleHog is more automated with built-in verifiers, while Betterleaks gives you more control through Expr. The choice depends on whether you want to write custom logic (Betterleaks) or rely on pre-built verifiers (TruffleHog).
Maintenance, Upgrades, and License
Upgrade cost is moderate. Since the config format changed from CEL to Expr, you may need to migrate existing configs. The README says CEL is accepted for compatibility, but that is a temporary bridge. You should plan to rewrite rules in Expr eventually. The binary is small and portable, so deployment is easy, but the config is where the real work lies. The playground is a useful tool for testing rules before deploying them.
Editorial conclusion
Adopt Betterleaks if you need a secrets scanner that goes beyond regex matching, especially if you manage many repositories and want to filter false positives with contextual logic. Do not adopt it if you prefer a simple, out-of-the-box tool with minimal configuration, because Betterleaks expects you to write Expr filters and maintain your own config. Before adopting, verify that your team can handle Expr syntax, that your existing Gitleaks configs migrate cleanly (CEL is accepted but deprecated), and that the sources you need (like S3 or Hugging Face) are covered. Also, check the default config to see which rules are active and whether you need to adjust parallelization settings for your scan environment.
Frequently asked questions
Does Betterleaks contact credential providers during a scan?
Not by default. The README states that scans detect secrets without credential provider requests by default, and that -v or --validate checks credentials while -a or --analyze also resolves identity and permissions, with analysis implying validation. The environment variables BETTERLEAKS_VALIDATE and BETTERLEAKS_ANALYZE do the same thing, and explicit flags win.
How do I install Betterleaks v2?
Until the first stable v2 release, package managers and the Docker latest tag may still provide v1. The README points at the tap cask, brew install --cask betterleaks/tap/betterleaks, the Docker v2 tag, go install of the /v2 module path, or a clone with make build, and a v2 migration guide covers the CLI, config, report and SDK changes.
Will a Betterleaks scan revoke a credential I found?
No. Rules may define an optional revoke expression, and revocation is executed with betterleaks revoke --rule <id> after checking support with betterleaks config show ids --revocation. The README states plainly that scans never run revocation.
What is the difference between a prefilter and a filter in Betterleaks?
A prefilter runs before any regex matching and can see only the attributes map describing the resource, so it is for bailing out cheaply. A filter runs after a match and can also read candidate data such as finding["secret"] and finding["match"]. Both are written in Expr.
Can I use Betterleaks as a Go library?
Yes, with the v2 module path. The SDK examples cover custom configuration, analysis, both regex engines and concurrent scanning, and the README notes that scanners and analyzers are silent by default and safe to reuse across scans.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/betterleaks-betterleaks)Star history chart for your README
[](https://hysenlabs.com/projects/betterleaks-betterleaks)Was this useful?