Certbot: What the EFF ACME Client Actually Automates, and Where It Stops
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any other CA that uses the ACME protocol.
At a glance
- What is it?
- Certbot fetches Let's Encrypt certificates from the command line and can rewrite your Apache or nginx configuration to serve HTTPS. The parts it automates are narrow, and the plugin you pick decides how much of your server it touches.
- Who is it for?
- Adopt Certbot if you run your own Apache or nginx server with root access and want certificate issuance plus optional http to https redirect handled by a command you can put in cron or a systemd timer. Do not adopt it if you are on shared hosting without shell access to the web server, since the README states Certbot is meant to be run directly on the server and points you back to your hosting provider for certificate upload instead.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
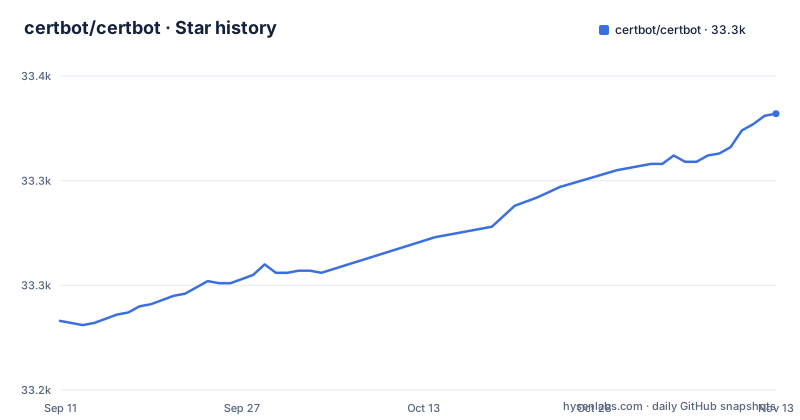
- certbot/certbot33,332 ★ · +99
| Repository | 2026-09-11 | 2026-11-13 |
|---|---|---|
| certbot/certbot | 33.2k | 33.3k |
99 Stars in the last 63 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The Problem Certbot Solves Is Certificate Plumbing, Not HTTPS Configuration
A web server needs a certificate from a certificate authority before browsers will treat its HTTPS responses as trustworthy, and the README frames the whole project around that one chore: getting and maintaining a certificate. Certbot is the client that talks to Let's Encrypt, the open CA the EFF launched with Mozilla and others, and pulls a domain-validated certificate down to the machine. The audience is narrow and specific. You run your own web server, you have root or administrator access to it, and you are willing to work on the command line. The README says this outright, and it also says the opposite case plainly: if you are on a hosted service without direct server access, Certbot may not be usable and you should ask your provider how to upload certificates or use Let's Encrypt-issued ones. That sentence is the most useful line in the README, because it pre-empts the most common support question. Certbot is not a certificate dashboard and not a hosted service. It is a program you install next to the thing it is securing.
Domain Validation Happens Through a Plugin, and the Plugin Decides the Blast Radius
To issue a certificate, the CA has to confirm you control the domain. Certbot supports several ways to prove that, and the choice is not cosmetic. The Apache and nginx plugins are the ones that can both obtain and install: they are listed as supporting Apache and nginx, and the feature list says configuration changes are logged and can be reverted. The webroot plugin takes a different route. It adds files to directories your web server already serves, so the CA can fetch them over HTTP. That means Certbot never touches your vhost configuration, which is the point: it works with server software that has no first-party plugin, and it works when you would rather edit config yourself. The standalone plugin goes further in the other direction. It runs its own simple web server to answer the challenge, which is why it needs the port free. On a machine already serving traffic on port 80, standalone will conflict with whatever is listening there. The README also notes that other server software is supported through third-party plugins, so the plugin list is extensible rather than closed. One detail worth flagging: the private key is generated locally on your system, which means the key material does not travel to the CA. Certbot can also revoke certificates.
Getting It Running: The Guide, the Flags, and the Root Requirement
Install steps depend on your operating system and web server, so follow the project's installation guide for your setup. You run Certbot on the server, you need root or administrator access in most cases, and you select a plugin. The plugin selection is expressed as flags in Certbot's documentation: --apache, --nginx, --webroot, and --standalone are the four first-party options named in the feature list, with -i or --installer used when you want to separate the installer from the authenticator. The feature list states that Certbot can optionally install an http to https redirect so the site effectively runs https only, and that it is fully automated. That combination is the reason people use the Apache and nginx plugins at all: with webroot you get a certificate file and nothing else, and with the server plugins you get the certificate plus the configuration edit plus the redirect, all in one command. Use the project's installation guide to get the exact package name for your distribution.
The Limits Are Structural: Hosted Hosting, Port Conflicts, and DV-Only Certificates
Certbot issues domain-validated certificates. If you need organization validation or extended validation, this is the wrong tool, and no plugin choice changes that. The standalone plugin needs to bind a port to answer the challenge, so it is a poor fit for a machine that is already serving HTTP on that port, which is most production web servers. The webroot plugin avoids the port problem but requires you to know which directory your server exposes and to point Certbot at it, and it will not install anything for you. The biggest limit is environmental. The README's own framing is that Certbot runs on your web server, not on your laptop, and that hosted customers without direct server access may not be able to use it. There is also a dependency on the ACME protocol itself. Certbot can talk to Let's Encrypt or to other ACME-compliant services. That is a real interoperability property, but it also means the tool's behaviour is bounded by what the CA's ACME endpoint allows, including rate limits and challenge types. Check your CA's own limits before assuming automation will cover a large batch of names.
Compared With a Configuration-Management or Proxy Approach
The realistic alternative for many teams is not another ACME client but a different layer entirely: terminating TLS at a reverse proxy or load balancer that handles certificate issuance and renewal itself, so individual web servers never hold a certificate. The difference in approach is where the certificate lives. Certbot installs a certificate onto the server it runs on, and its Apache and nginx plugins edit that server's configuration. A proxy-based setup centralizes the certificate on the proxy and leaves backend servers speaking plain HTTP behind it. If you have one server and no proxy, Certbot's model is simpler because there is no extra component. If you have many servers behind a proxy, running Certbot on each one duplicates work and spreads private keys across machines. That trade-off is the decision most teams actually face.
Maintenance, Releases, and What the Licence Field Does Not Tell You
The repository shows a steady release cadence: v5.7.0 in July 2026, v5.8.0 in September 2026 and v5.9.0 on 2026-10-29, with the last push to main later that same day. That rhythm matters for an ACME client because the protocol and the CA's policies move, and a client that stops tracking them eventually fails at issuance. The repository has a CHANGELOG.md for the detail, which is where you should look before upgrading a production server, since the Apache and nginx plugins modify configuration files and a behaviour change there is the kind of thing you want to read about first. On licensing, the repository metadata reports NOASSERTION, which means the automated classifier could not map the licence file to a known identifier. Do not treat that as permission or as a restriction. Read the actual licence file in the repository before you redistribute Certbot or bundle it into a product, and if you need a definitive answer, ask someone qualified rather than inferring from a metadata field. The repository also has a CODE_OF_CONDUCT.md, which concerns contribution, not use.
Editorial conclusion
Adopt Certbot if you run your own Apache or nginx server with root access and want certificate issuance plus optional http to https redirect handled by a command you can put in cron or a systemd timer. Do not adopt it if you are on shared hosting without shell access to the web server, since the README states Certbot is meant to be run directly on the server and points you back to your hosting provider for certificate upload instead. Before rolling it out, verify the exact plugin name for your server and confirm whether you want --installer or -i at all, because that flag is what separates obtaining a certificate from letting Certbot edit your vhost files.
Frequently asked questions
What is certbot used for?
It is the EFF's client for obtaining certificates from Let's Encrypt and optionally enabling HTTPS automatically, and it also works as a client for any other authority that speaks the ACME protocol. The README describes it as an easy-to-use client that fetches a certificate and deploys it to a web server, and says using it with Let's Encrypt is free.
how to install certbot
Installation steps depend on your operating system and web server, so follow the project's installation guide. In most cases you need root or administrator access to the web server to run Certbot at all. There is also documentation for users, a main website, and a changelog in the repository.
how to use certbot with nginx
Certbot ships an nginx plugin (the certbot-nginx directory in the repository), and the README points to the user documentation for the details. The feature list also notes that it can optionally install a redirect from HTTP to HTTPS so the site runs HTTPS only, and that configuration changes are logged and can be reverted.
how to use certbot with cloudflare
Cloudflare is one of thirteen DNS plugin directories in the repository, each packaged separately from Certbot itself. Those plugins solve the case where you cannot run a challenge on the web server itself; the two web server plugins for Apache and nginx are the ones Certbot's own feature list documents.
Is certbot safe to use?
The README states that the private key is generated locally on your system, that Certbot is meant to be run on the web server with root or administrator access, and that configuration changes are logged and can be reverted. It also notes that a hosted user without direct server access might not be able to use it and should ask their provider about uploading certificates instead.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/certbot-certbot)Star history chart for your README
[](https://hysenlabs.com/projects/certbot-certbot)Was this useful?