Cloudflare's MCP Server: 2,500 API Endpoints Behind Three Tools
MCP server for the Cloudflare API
At a glance
- What is it?
- Cloudflare's MCP server puts its entire API behind a search-and-execute pair of tools instead of one tool per endpoint. The README's own token table explains why, and the same table explains when you should turn that design off.
- Who is it for?
- Adopt this server if your agent needs broad Cloudflare coverage and your context budget is tight, because the README's own table puts code mode at roughly 1,100 tokens against 244,047 for minimal native schemas. Do not adopt it if your client has no JavaScript execution path for tool payloads, or if you need a token with Client IP Address Filtering, which the README states is not supported.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
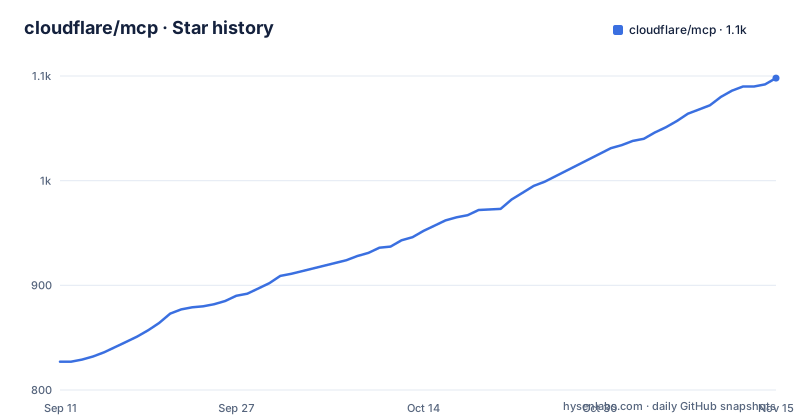
- cloudflare/mcp1,098 ★ · +271
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| cloudflare/mcp | 827 | 1.1k |
271 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The context bill that Cloudflare's API spec runs up
The Cloudflare OpenAPI spec is the problem this project was built around. The README states it is 2 million tokens, and that exposing the API as native MCP tools with full schemas costs 1,170,523 tokens across 2,594 tools. Trimming schemas to required parameters only still lands at 244,047 tokens, which the README's own table scores at 122 percent of a 200K context window. That is the failure mode: the server does not run out of endpoints, the agent runs out of room for the user's actual request. This server targets engineers wiring Cloudflare into an agent that also has to hold a conversation, a codebase, or a runbook. If your only goal is one scripted API call, an MCP server is the wrong layer entirely and curl against the REST API is shorter.
Three tools, a spec on the server, and a JavaScript sandbox in between
The README describes three tools. `docs` searches Cloudflare developer documentation. `search` runs JavaScript against `spec.paths` to find endpoints. `execute` runs JavaScript that calls `cloudflare.request()` with the endpoints that search turned up. The data flow is the point: the spec stays on the server, the agent writes code that queries it, and only the execution result crosses back. The README's diagram shows exactly two round trips, search then execute. The security properties of this design rest entirely on the sandbox that runs that code, so check which JavaScript runtime executes it, how long it may run, and what it can reach beyond `spec.paths` and `cloudflare.request()`. That is a gap worth naming rather than guessing at, because the security properties of this design rest entirely on a sandbox the README does not document. The GraphQL Analytics API is handled through the same `execute` tool, with the README showing a POST to `/client/v4/graphql` carrying a `query` and a `variables` object.
Getting it connected: OAuth, bearer tokens, and the codemode flag
The MCP URL is `https://mcp.cloudflare.com/mcp`. OAuth is the recommended path: connect to that URL and you are redirected to Cloudflare to authorize and pick permissions. The README's JSON block uses `"type": "http"` and the `url` key under `mcpServers`. The token path is for CI/CD and automation. Create a Cloudflare API token with the permissions you need; both user tokens and account tokens work. For account tokens, add Account Resources : Read so the server can auto-detect your account ID, which removes the need to pass `account_id` on every `execute` call. Two constraints are stated plainly. API tokens with Client IP Address Filtering enabled are not currently supported. And if you want the per-endpoint tool layout instead of code mode, append `?codemode=false` to the URL, which registers tools like `get_workers_scripts` and `post_d1_database` with schemas derived from path parameters, query parameters and request body. The README warns that this raises cost to roughly 244k tokens and says to disable code mode only when composing with another code mode system.
The codemode=false path is a different product, not a setting
The two modes do not share a cost profile, and the README is direct about it. Code mode is about 1,100 tokens. The full per-endpoint layout is roughly 244,047. That is a difference of two orders of magnitude from one query parameter. The per-endpoint path also changes what the agent does: tools make direct API calls with no code execution involved, and path parameters like `account_id` are auto-resolved when there is a single account. So the fallback is not merely more expensive, it is a different interaction model in which the agent picks a tool by name rather than writing a query. If your client cannot execute JavaScript that the server hands back, or if it already runs its own code mode and would nest two of them, the fallback is the correct choice despite the token hit. The `docs` tool remains available in both modes, per the README.
Where the token table stops being an argument
The README's comparison table is the strongest evidence in the repository, and it is also the least independently checkable part of it. No methodology, no tokenizer, no measurement date accompanies the figures. Treat 1,100 tokens as a claim from the project, not a benchmark. The more useful limitation is structural: code mode trades a fixed context cost for variable output cost. A `search` call that returns a wide slice of `spec.paths`, or an `execute` call that returns a large API response, spends tokens in the result rather than in the schema. The README's example search loops over every path and method and pushes a summary for each match, which is exactly the shape that can return more than expected. The fixed-schema approach has the opposite profile: expensive up front, predictable per call. Which one is cheaper depends on how many endpoints you touch per session, and the README does not model that.
What to compare against: the official Cloudflare MCP servers
Cloudflare publishes separate, product-scoped MCP servers, and the README's own Supported Products list (Workers, KV, R2, D1, Pages, DNS, Firewall, Load Balancers, Stream, Images, AI Gateway, Vectorize, Access, Gateway) describes what this single server covers. The difference in approach is scope versus precision. A product-scoped server exposes a handful of tools with hand-written schemas for one service, so the agent sees a small, reviewed surface and cannot reach anything outside it. This server exposes the whole REST surface through code, so reach is effectively unbounded but every call is composed at runtime from a spec the agent queried. If your agent only manages R2 buckets, a scoped server gives you a smaller blast radius and schemas somebody wrote deliberately. If your agent has to move between Workers, DNS and D1 in one session, four scoped servers means four connections and four token budgets, and this one server is the better fit.
Licence, maintenance, and what the repository material does not say
The licence is Apache-2.0, which permits commercial use and modification and includes an explicit patent grant. That is a permissive licence, not a legal opinion, and if you fork or redistribute the server you should read the notice and attribution requirements yourself. On maintenance cost, the repository is TypeScript on the `main` branch with no published GitHub releases, so there is no versioned artifact to pin against and no changelog to diff. The practical upgrade cost sits on the server side rather than yours: the spec and the endpoint surface live behind `https://mcp.cloudflare.com/mcp`, so endpoint coverage can change without a change in your config. The `?codemode=false` flag and the Account Resources: Read requirement are the two config details most likely to matter if the server's behaviour shifts, and both are worth re-checking against the README after any change in tool behaviour rather than assumed stable.
Editorial conclusion
Adopt this server if your agent needs broad Cloudflare coverage and your context budget is tight, because the README's own table puts code mode at roughly 1,100 tokens against 244,047 for minimal native schemas. Do not adopt it if your client has no JavaScript execution path for tool payloads, or if you need a token with Client IP Address Filtering, which the README states is not supported. Verify first that your client can handle the search then execute round trip, and that a single account token carries Account Resources : Read so account_id auto-detection works.
Frequently asked questions
What is the Cloudflare MCP server URL?
https://mcp.cloudflare.com/mcp. With the recommended OAuth path you connect that URL and are redirected to Cloudflare to authorize and select permissions. It can also be added as an http type MCP server in a JSON configuration block, pointing the url field at the same address.
How do I use the Cloudflare MCP server in CI?
Use a Cloudflare API token instead of OAuth, created in the dashboard with the permissions you need. Both user tokens and account tokens are supported, and for account tokens you should include the Account Resources read permission so the server can auto-detect your account ID. API tokens with client IP address filtering enabled are not currently supported.
What tools does the Cloudflare MCP server expose in code mode?
Three. The docs tool searches Cloudflare developer documentation, the search tool runs JavaScript against spec.paths to find endpoints, and the execute tool runs JavaScript that calls cloudflare.request() with the endpoints discovered. The spec stays on the server and only the execution result comes back, which is how 2,594 endpoints fit in about 1,100 tokens.
When should I disable code mode on the Cloudflare MCP server?
Only when your MCP client already uses code mode or you are composing this server with another code mode server. Adding ?codemode=false registers about 2,500 individual endpoint tools with schemas derived from path, query and body parameters, makes direct API calls with no code execution, and raises the context cost to roughly 244k tokens. The docs tool stays available in both modes.
What is the result size limit on Cloudflare MCP tool calls?
Each tool result is capped at roughly 6,000 tokens by default, with oversized JSON kept valid, long lists truncated after whole items, long strings clipped, and every cut marked by a --- TRUNCATED --- line. Clients that bound results themselves can add ?truncateToolResult=false, which works with or without code mode, at the risk of a broad query returning megabytes.
Official sources
Where developers are discussing it
Posts on Hacker News, dev.to and Lobsters that link to this repository, found by our scan of those communities. 1 in the last 30 days; newest first.
- MCP Step-Up Authorization vs. OAuth Incremental Authorization: What Actually Changes?dev.to · Oct 22, 2026 · 5 points · 0 comments
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/cloudflare-mcp)Star history chart for your README
[](https://hysenlabs.com/projects/cloudflare-mcp)Was this useful?