Secure OpenClaw: messaging gateway for a personal AI assistant
A personal 24x7 AI assistant like OpenClaw that runs on your messaging platforms. Send a message on WhatsApp, Telegram, Signal, or iMessage and get responses from Claude with full tool access, persistent memory, scheduled reminders, and integrations with 500+ apps.
At a glance
- What is it?
- Secure OpenClaw connects a personal assistant to WhatsApp, Telegram, Signal and iMessage, with persistent memory, reminders and Composio integrations. Its tool access, messaging allowlists and remote deployment require careful configuration.
- Who is it for?
- Secure OpenClaw offers a messaging interface for an assistant with potentially powerful tools and external account integrations. Start in a restricted environment, configure explicit sender allowlists, limit tool and account permissions, protect credentials and memory, and verify approval and pairing behavior in the deployed version.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 120 days ago.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 20, 2026, and from our analysis. They are not legal advice.
Star history
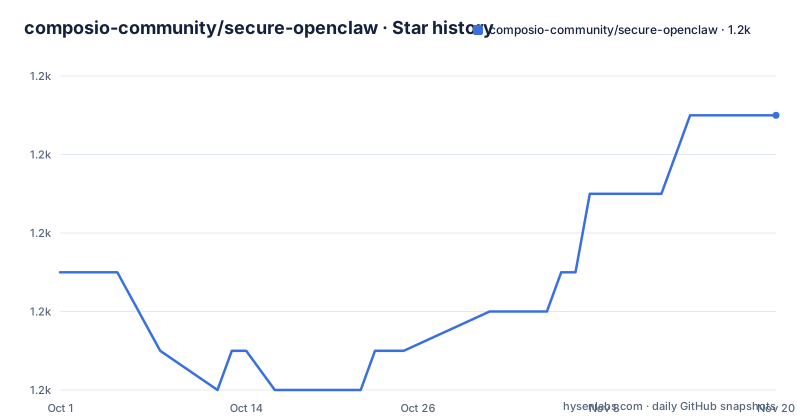
- composio-community/secure-openclaw1,193 ★ · +4
| Repository | 2026-10-01 | 2026-11-20 |
|---|---|---|
| composio-community/secure-openclaw | 1.2k | 1.2k |
4 Stars in the last 50 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Dependencies and reproducible installs
The project's package manifest includes dependencies specified with `latest`. A fresh resolution or dependency update can therefore change versions over time. A committed lockfile helps preserve the resolved tree when used with `npm ci`, but it does not guarantee identical execution across environments or establish what the author tested.
Review the manifest and lockfile, pin or constrain dependencies according to your update policy, and test updates before deployment. The absence of a test script in a manifest does not by itself prove that no tests exist elsewhere.
Project scope and integrations
The repository describes a messaging gateway for an assistant, with integrations supplied through Composio. WhatsApp, Telegram, Signal and iMessage have different setup requirements; iMessage is documented as macOS-only. Availability and permissions of individual integrations depend on the provider and connected accounts.
This is a community repository associated with the integration provider. Review both the gateway and the external service's terms, data handling and permissions before connecting accounts.
Approvals, allowlists and pairing
The README documents allowlists for direct messages and groups. Prefer specific trusted sender IDs to wildcard access, and test the configured restrictions. It also says certain tool requests prompt for approval, with a two-minute timeout; this should not be interpreted as every operation being gated.
The remote instructions expose a WhatsApp QR pairing page. The README does not establish its authentication properties, so inspect the implementation and protect access with an appropriate private network or authenticated gateway before exposing it. A pairing code is sensitive; do not make it publicly accessible while it is active.
Remote hosting and resources
The README includes a small-server Docker example and adds swap because the build needs more than 1 GB. Swap can reduce memory pressure but is not a guarantee that a build or workload will succeed. Size and monitor the host for the actual workload.
Use a supported, updated host, restrict administrative access and the gateway's network exposure, and protect volumes containing credentials, WhatsApp authentication and memory. Verify your provider's current plan, pricing and recovery options independently.
Getting the source and setting up
The README's clone commands contain placeholders. Use the canonical repository URL or the URL of your own fork, inspect the source and dependency lockfile, and follow the current setup instructions. The documented interactive entry point is `node cli.js`, with commands for terminal chat and starting the gateway.
The project lists Node.js 18 or later, provider credentials and platform-specific prerequisites. Verify those prerequisites for your selected adapter; avoid copying a private access token into a URL that can be retained in shell history or logs.
Providers and credentials
The README lists an Anthropic API key and a Composio API key among requirements and describes Claude Agent SDK and OpenCode provider options. Authentication and model availability depend on the selected provider and configuration; consult its current documentation rather than assuming a remote deployment cannot use interactive authentication.
Treat model credentials, messaging tokens and connected app authorizations as separate secrets. Limit their scope, keep them out of logs and source control, and rotate them if exposed.
Troubleshooting and operational checks
The README documents troubleshooting for a killed build, an inaccessible QR page, a gateway still starting, provider authentication and private repository access. Exit code 137 can indicate termination by SIGKILL, including an out-of-memory event, but it is not conclusive on its own; check container and system logs.
Avoid printing environment variables containing API keys when diagnosing configuration. Check whether required variables are present without revealing values, and use least-privilege credentials. Test messaging allowlists, approvals, persistence and recovery in a controlled environment before relying on the service.
Editorial conclusion
Secure OpenClaw offers a messaging interface for an assistant with potentially powerful tools and external account integrations. Start in a restricted environment, configure explicit sender allowlists, limit tool and account permissions, protect credentials and memory, and verify approval and pairing behavior in the deployed version. Review dependencies and test the exact deployment before exposing any service to the internet.
Frequently asked questions
What does secure-openclaw do?
It runs a coding agent behind four messaging platforms, so you can send a message from WhatsApp, Telegram, Signal or iMessage and get a reply with tool access, persistent memory, scheduled reminders, and integrations with several hundred applications through a hosted tool router service.
Why are some of the secure-openclaw dependencies versioned as latest?
Some dependency entries use `latest`, which can resolve to a newer package when the dependency tree is freshly resolved or updated. A committed lockfile and `npm ci` can help reproduce a locked dependency tree, but they do not guarantee identical execution or protect an intentional lockfile update. Review the manifest, lockfile and package provenance before deployment.
How does secure-openclaw authenticate its model provider?
The README lists an Anthropic API key and Composio API key among requirements, with provider-specific setup for Claude and OpenCode. Authentication details depend on the chosen provider and deployment; follow current provider documentation and store secrets securely.
What security controls does secure-openclaw actually have?
The README documents sender allowlists and approval prompts for certain tools, with a two-minute approval timeout. These are not proof that every action requires approval or that the pairing endpoint is authenticated; inspect and test the deployed version and restrict access to it.
What hardware does the remote deployment need?
The README's remote example uses a small server and adds swap because its build needs more than 1 GB. Actual memory needs depend on versions and workload; monitor the build and runtime on the target host.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/composio-community-secure-openclaw)Star history chart for your README
[](https://hysenlabs.com/projects/composio-community-secure-openclaw)Was this useful?