CreditTone/hooker: A Frida Reverse Engineering Workbench for Rooted Android Devices
🔥🔥 hooker is a Frida-based reverse engineering toolkit for Android. It offers a user-friendly CLI, universal scripts, auto hook generation, memory roaming to detect activities/services, one-click SOCKS5 proxy setup, Frida JustTrustMe, and BoringSSL unpinning for all apps.
At a glance
- What is it?
- hooker wraps Frida, a bundled Frida server, a set of universal hook scripts and a SOCKS5 proxy helper behind a Python CLI. It is built for rooted physical devices, and the README says x86 emulators are not compatible.
- Who is it for?
- Adopt hooker if you already work on a rooted ARM Android device over USB and want a single CLI that starts Frida, lists debuggable apps and runs packaged scripts such as just_trust_me.js and dump_dex.js. Do not adopt it for x86 emulators, for iOS work, or if you need a clearly stated licence before shipping it inside a commercial pipeline, because the repository does not declare one.
- Can I use it commercially?
- Not without permission. GitHub finds no licence file in the repository, and without a licence all rights are reserved by default: you may read the code but not reuse it. Check the README, or ask the authors, before using it.
- Is it still maintained?
- Yes. The repository last received commits 66 days ago.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
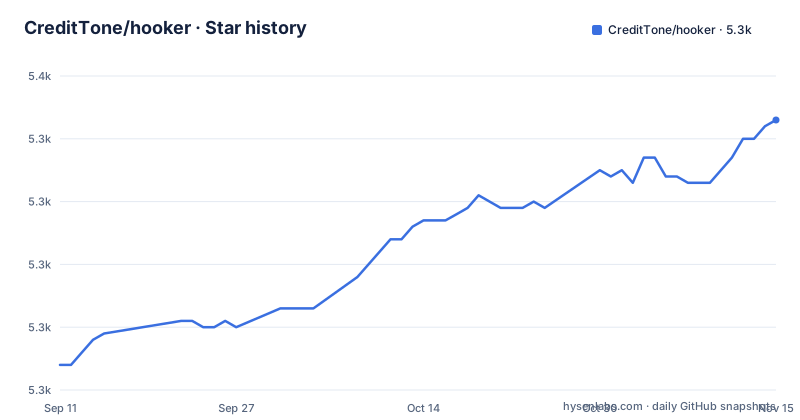
Star history
- CreditTone/hooker5,343 ★ · +39
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| CreditTone/hooker | 5.3k | 5.3k |
39 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What hooker actually packages, and who it is written for
hooker is a Python command line program that sits on top of Frida. The README describes it as a reverse engineering toolkit whose goal is to give Android reverse engineers a comfortable CLI plus a set of universal scripts, automatic hook generation, memory roaming to detect activities and services, a Frida port of JustTrustMe, and BoringSSL unpinning. The audience is narrow and specific: someone with a rooted physical Android phone plugged into a Mac, Linux or WSL host, who already understands what Frida does and wants the repetitive parts handled. The README states that the phone only needs root and that hooker starts frida-server itself, so no manual frida-server launch is required. The same line states x86 emulators are incompatible, which rules out the most common cheap test environment. The disclaimer is explicit that the project is for study and technical exchange, and that it does not include cracking operations against specific apps. That framing matters when you decide whether the tool fits your context.
The startup flow: device enumeration before any hooking
Running python3 hooker.py from inside the cloned directory prints a table of every debuggable app on the device. The README documents four columns. PID is the app's main process id, or 0 when the app is not running. APP is the display name. IDENTIFIER is the package name. EXIST_REVERSE_DIRECTORY is a check mark if the app has been debugged before and a cross if it has not. That last column is the interesting one: hooker keeps a per-app working directory, and its presence is what tells the tool whether it has prior state for that package. The README warns not to invoke the script by absolute path and to cd into the hooker directory first, which suggests the tool resolves its own resources relative to the current working directory. After you type a package name hooker creates the app working directory, and you can call up help at any time to list the available operations. The README's table of contents enumerates them: embedded webserver, automatic Frida script generation, listing the app directory's Frida scripts, attach execution, spawn execution, SOCKS5 proxy setup, JustTrustMe, proxy teardown, app restart, uid and pid lookup, file pull, r0capture, and self-upgrade.
The bundled script catalogue is the real product
The README lists roughly two dozen scripts that ship in the per-app working directory, and that list is where the tool's value concentrates. Some are traffic and crypto oriented: url.js, ssl_log.js, just_trust_me.js, find_boringssl_custom_verify_func.js, hook_encryption_algo.js and hook_encryption_algo2.js. Some are UI and instrumentation oriented: activity_events.js, click.js, android_ui.js, edit_text.js, text_view.js, webview_enable_debug.js. Some target the runtime itself: hook_register_natives.js, jni_method_trace.js, hook_artmethod_register.js, trace_init_proc.js, dump_dex.js, keystore_dump.js, replace_dlsym_get_pthread_create.js. A third group is counter-detection: find_anit_frida_so.js, bypass_frida_svc_detect.js, bypass_root_detect.js, bypass_vpn_detect.js, apk_shell_scanner.js. There is even just_trust_me_for_ios.js, which sits oddly in an Android toolkit. Note the file name find_anit_frida_so.js, which appears to contain a typo for anti. If you script against that path, use the spelling the README gives.
Getting it running: commands, dependencies and the WSL path
The setup sequence in the README is four steps. Clone the repository, install Python dependencies with pip3 install -r requirements.txt, confirm the device with adb devices, then run python3 hooker.py from inside the hooker directory. requirements.txt pins frida==16.7.19 and the WSL steps install Python 3.8, so those are the versions the author was working against. Windows users are told to install WSL first, specifically Ubuntu 24.04, then configure a proxy inside WSL, then install Python 3.8 and Frida there. The README also documents a custom frida-server option. There is an upgrade command listed as hooker automatic upgrade, so the tool can pull its own updates.
The embedded webserver is the most under-documented feature
The README's own pitch list puts the embedded webserver second, describing it as a way to expose an app's internal capabilities as HTTP interfaces for automation. That is a meaningfully different use case from interactive hooking: it turns a session into something a test harness or CI job could call. The README also has a section titled developing phone API interfaces and another listing hooker's native operation API, so the design intent is clearly that users write their own scripts against a stable set of primitives. The README documents it in its own section: it starts an HTTP service inside the target app process on port 8080 by default, and mounts built-in endpoints for UI automation, window hierarchy dumps, screenshots, app info, shared_prefs and databases, and invoking class methods.
Where hooker breaks down, and what to use instead
Three concrete limits stand out. The README states x86 emulators are incompatible, so the fast iteration loop of an emulator snapshot is closed off and you need real hardware. The device must be rooted, which on modern Android means an unlocked bootloader and the attendant trade-offs. And the counter-detection scripts exist precisely because apps detect Frida, root and VPN; their presence in the catalogue is an admission that detection is an ongoing arms race rather than a solved problem. For a different approach, consider objection, which is also Frida-based but drives instrumentation over a REPL and a JavaScript API rather than a menu of pre-written scripts, and which targets both Android and iOS from one interface. The practical difference: hooker hands you a fixed set of scripts plus a Python CLI and a per-app working directory, so you trade flexibility for speed on common tasks. objection gives you a live console and expects you to write the hooks. If your work is one-off and exploratory, objection's model fits better. If you repeatedly run the same unpinning and dump routines across many apps, hooker's catalogue is the point.
Maintenance cost and the missing licence
The repository has no releases. Pin a reviewed Git commit for a reproducible source snapshot and inspect changes before updating; the README's upgrade command tracks the master branch. That is a real cost: a change to a bundled script or to the CLI's output format lands on you the next time you upgrade. The pinned Frida version is the other moving part. Frida's own releases change the internal APIs that scripts like hook_register_natives.js and hook_artmethod_register.js depend on, so a Frida bump on the device side can break scripts that worked the week before. On licensing, the repository does not declare a licence, and the README carries only a disclaimer limiting use to study and technical exchange. Without a licence file, the default is that all rights are reserved, which means you have no granted right to redistribute or embed the code. That is a factual observation about the repository state, not legal advice; if you intend to use hooker inside a commercial product or an internal pipeline that ships to customers, get your own counsel to look at it before you do.
Editorial conclusion
Adopt hooker if you already work on a rooted ARM Android device over USB and want a single CLI that starts Frida, lists debuggable apps and runs packaged scripts such as just_trust_me.js and dump_dex.js. Do not adopt it for x86 emulators, for iOS work, or if you need a clearly stated licence before shipping it inside a commercial pipeline, because the repository does not declare one. Verify three things before relying on it: the Frida version pinned in requirements.txt against your host, whether your target app is listed as debuggable, and whether the app's own anti-Frida checks defeat the bundled bypass scripts. Then read the script you intend to run.
Frequently asked questions
What is hooker and what does it do?
It is a Frida based reverse engineering toolkit for Android, aimed at people doing Android reverse engineering. It offers a command line interface, universal scripts, automatic generation of hook scripts, memory roaming to detect activities and services, one click SOCKS5 proxy setup, a Frida version of JustTrustMe, and BoringSSL certificate unpinning across applications.
What does hooker need before it will run?
A rooted phone. The page states that no manual startup of frida-server or any other configuration is needed, and that hooker handles it all. Emulators on the x86 architecture are not compatible. Windows users go through a WSL install path first.
Does hooker expose the app under test over HTTP?
Yes. It injects a lightweight webserver into the target app process on port 8080 by default, which can expose custom controllers and mounts built in interfaces for UI automation, window hierarchy dumps, screenshots, app info, shared preferences and database reading, with a stop path to shut it down.
Which Python packages does hooker depend on?
Seven of them: frida==16.7.19, frida-tools==13.7.1, adbutils==1.2.11, androguard==3.3.5, jsbeautifier==1.15.4, plus gitpython and loguru, which are listed without a version.
What licence does hooker come under?
The repository contains no licence file in its tree and its licence metadata is recorded as unknown, so there is nothing on the repository to point at. The project also carries no GitHub releases and no test directory.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/credittone-hooker)Star history chart for your README
[](https://hysenlabs.com/projects/credittone-hooker)Was this useful?