CRI-O: The OCI runtime bridge for Kubernetes clusters that want to skip the Docker layer
Open Container Initiative-based implementation of Kubernetes Container Runtime Interface.
At a glance
- What is it?
- CRI-O is a Kubernetes CRI implementation that talks directly to OCI runtimes like runc, skipping the Docker daemon. This review covers its scope, architecture, configuration, and the maintenance constraints that come with following Kubernetes release cycles.
- Who is it for?
- Adopt CRI-O if you run Kubernetes and want a minimal CRI implementation that talks directly to OCI runtimes, especially on OpenShift or in environments where you already use container-libs tools. Do not adopt it if you need a CLI for day-to-day container management, because the project explicitly does not guarantee backward compatibility for its test-only CLIs.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
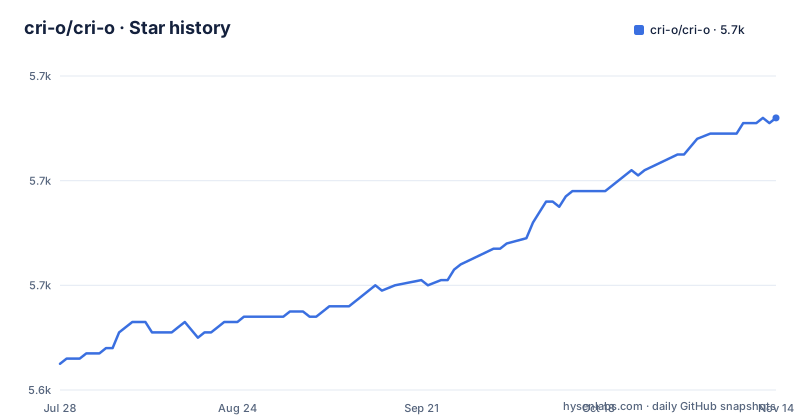
Star history
- cri-o/cri-o5,692 ★ · +47
| Repository | 2026-07-28 | 2026-11-14 |
|---|---|---|
| cri-o/cri-o | 5.6k | 5.7k |
47 Stars in the last 109 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What CRI-O actually replaces
Kubernetes does not launch containers directly. It talks to a container runtime through the Container Runtime Interface, a gRPC API that the kubelet calls. CRI-O is one implementation of that interface. The README states that CRI-O provides an integration path between OCI conformant runtimes and the kubelet. In practice, that means CRI-O replaces the Docker daemon or containerd as the thing that pulls images, manages storage, and starts processes. The target user is a Kubernetes cluster operator who wants a runtime that is narrowly scoped to the CRI and nothing else. The project explicitly excludes building, signing, and pushing images, and it excludes providing a stable CLI. That is a sharper boundary than most runtimes draw.
How CRI-O is built: OCI runtimes and container-libs
The architecture is visible in the README's list of components. CRI-O uses runc, or any OCI runtime-spec implementation, to execute containers. It uses container-libs/image for image management and container-libs/storage for image layers and overlay filesystems. Networking goes through CNI. The data flow is straightforward: the kubelet sends a CRI request, CRI-O translates it into OCI runtime calls, and the runtime starts the container. The storage and image libraries come from the containers project, which is the same ecosystem that powers tools like Podman. That means CRI-O is not a from-scratch runtime. It is a thin CRI layer on top of shared container libraries. The README also mentions support for OCI hooks, which lets you run custom actions at container lifecycle events. The integration with the kubelet is the core, and everything else is delegated.
Getting it running: install and configuration
The README points to a packaging repository for installation, but the configuration section is the part that matters. The README has a Configuration section, and the Makefile's configuration directory is /etc/crio. For a basic setup, you install the package, point the kubelet at the CRI-O socket, and start the service. The README has a section on running Kubernetes with CRI-O. What is clear is that CRI-O exposes an HTTP status API, metrics endpoints, and tracing support. These are the operational surfaces you need to monitor a runtime.
The maintenance model: manual backports and version skew
The README is explicit about how releases work. CRI-O follows Kubernetes minor versions, so v1.36 corresponds to Kubernetes 1.36. Patch releases are not synchronized with Kubernetes patch releases. Kubernetes patches ship monthly, while CRI-O patches ship only when necessary. The README states that maintenance on release-1.x branches is manual and only bugfixes are backported. That is a real operational cost. If you run a Kubernetes cluster that is not on the latest minor version, you depend on manual backports of bugfixes, and any feature backport is a case-by-case community decision. The README says CRI-O follows the Kubernetes n-2 version skew policy for feature graduation, deprecation and removal. You have to track the release notes, which are hand-crafted and published on the GitHub Pages site.
What CRI-O does not do: the CLI and image building gap
The README is refreshingly honest about what is out of scope. CRI-O does not build, sign, or push images. That is not a gap; it is a design choice. But the CLI part is a limitation. Any CLI built as part of CRI-O is only for testing, and there is no backward compatibility guarantee. That means you cannot rely on a CRI-O command as part of your operational tooling. If you need to inspect containers, pull images, or debug runtime state, you have to use cri-tools (crictl) or Kubernetes itself. The project also does not provide a user-facing interface for interacting with CRI-O. This is the wrong tool if you want a runtime that doubles as a developer tool. The scope is strictly the CRI, and anything beyond that is left to other projects.
The alternative: containerd and the difference in approach
The main alternative to CRI-O is containerd, which is also a CRI implementation but takes a different architectural path. containerd is a full container runtime that includes its own image management, snapshotters, and its own CLI (ctr). It originated from the Docker ecosystem and is now a CNCF project. CRI-O, by contrast, delegates image and storage handling to container-libs, which are shared with Podman and other tools. The practical difference is that containerd is a standalone runtime that you can use outside Kubernetes, while CRI-O is tightly coupled to the CRI and the kubelet. If you need a runtime that works for both Kubernetes and standalone container workflows, containerd is the more flexible choice. If you want a minimal CRI implementation that does not carry the Docker lineage, CRI-O is the cleaner fit. The scope statements make the difference clear.
Licence and operational considerations
CRI-O is licensed under Apache-2.0, which is permissive and compatible with most enterprise use. The README references a license scan and a FOSSA badge, indicating the project tracks dependency licenses. That matters if you are deploying in an environment that requires license compliance. The project is part of the Kubernetes community, with governance and a weekly meeting, so it is not a solo effort. The CI setup is split between GitHub Actions and OpenShift's Prow, which is a sign of the project's ties to OpenShift. If you are on vanilla Kubernetes, you have to weigh the manual backport model against the convenience of a runtime that is updated in lockstep with Kubernetes.
Editorial conclusion
Adopt CRI-O if you run Kubernetes and want a minimal CRI implementation that talks directly to OCI runtimes, especially on OpenShift or in environments where you already use container-libs tools. Do not adopt it if you need a CLI for day-to-day container management, because the project explicitly does not guarantee backward compatibility for its test-only CLIs. Before adopting, verify that your Kubernetes version matches a supported CRI-O minor release, check the compatibility matrix, and confirm that your OCI runtime (like runc) meets the runtime-spec requirements. Also verify which patch releases are available for your chosen branch, since maintenance is manual and bugfixes are not backported automatically.
Frequently asked questions
What does cri o stand for?
The repository title gives it as the OCI-based implementation of the Kubernetes Container Runtime Interface. Its own description says the same thing: an implementation of that interface using Open Container Initiative conformant runtimes, which lets Kubernetes launch and manage OCI containers directly.
What is the container runtime Interface (CRI) in Kubernetes?
It is the interface between the kubelet and a container runtime, and the page says CRI-O exists to provide an integration path between OCI-conformant runtimes and the kubelet by implementing that interface. It also says the scope of the project is tied to the scope of the interface itself.
What is CRI-O responsible for?
Six things, listed in the readme: support for several image formats including the one Docker used, several ways of downloading an image including trust and verification, image management including layers and overlay filesystems, container process lifecycle management, the monitoring and logging the interface requires, and the resource isolation the interface requires.
Does CRI-O ship a supported command line tool?
No. The readme puts a command line utility for interacting with CRI-O out of scope, and says that any such tools built as part of the project are meant only for testing it and carry no backward-compatibility guarantees.
How often does CRI-O get released, and what builds it?
The three most recent releases, one from each maintained line, were published within about a minute of each other, and the release notes are hand-crafted rather than generated. The build stands on other projects for every part: a low-level runtime or any implementation of the runtime specification, an image library, a storage library, and the networking plugin interface. Its own build tags come from seven scripts that probe the host for optional features.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/cri-o-cri-o)Star history chart for your README
[](https://hysenlabs.com/projects/cri-o-cri-o)Was this useful?