SecLists: A Wordlist Warehouse, Not a Tool
GitHub describes it as SecLists is the security tester's companion. It's a collection of multiple types of lists used during security assessments, collected in one place. List types include usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells, and many more.. The repository metadata lists PHP as its primary language. The metadata lists the MIT license. This article stays within the project description and details documented in the GitHub repository README.
At a glance
- What is it?
- SecLists bundles many types of lists for security assessments into one repository. It is a data collection with a simple install path, but its value depends on your ability to pick the right list and handle its maintenance quirks.
- Who is it for?
- Adopt SecLists if you are a penetration tester or bug bounty hunter who needs a broad, ready-made set of wordlists for content discovery, password cracking, or fuzzing, and you can tolerate a repository that grows by accretion. Do not adopt it if you need curated, deduplicated, or frequently updated lists, or if you plan to store the data on a production server, since the README warns about local file include risks.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly PHP, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
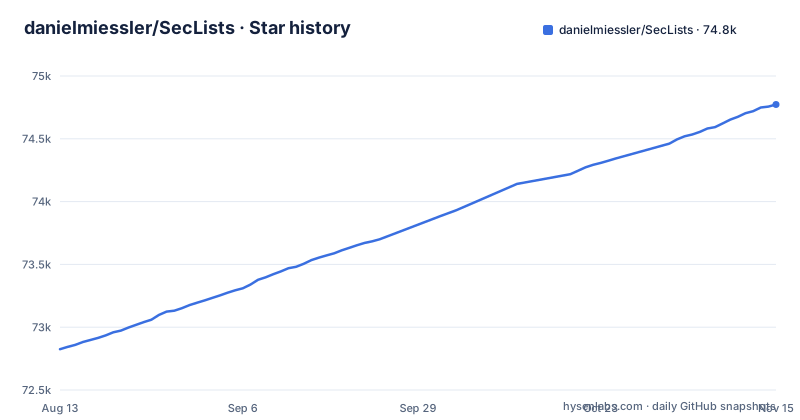
Star history
- danielmiessler/SecLists74,773 ★ · +1,948
| Repository | 2026-08-13 | 2026-11-15 |
|---|---|---|
| danielmiessler/SecLists | 72.8k | 74.8k |
1,948 Stars in the last 94 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What SecLists Actually Provides
SecLists is not a tool that scans or cracks anything. It is a collection of text files: usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells, and more. The README says the goal is to let a security tester pull the repository onto a new testing box and have access to every type of list that may be needed. That is the core promise. The audience is anyone doing security assessments: penetration testers, bug bounty hunters, CTF players, and researchers who need input data for other tools. The project is maintained by Daniel Miessler, Jason Haddix, Ignacio Portal, and g0tmi1k, and it has a release cadence: 2026.2 came out on 2026-10-27, following 2026.1 on 2026-03-23 and 2025.3. The primary language listed is PHP, but that is incidental; the repository is mostly plain text data, not code.
How the Repository Is Organized
The README does not give a full directory tree, but it names list types: usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells. From the repository layout, you can infer that these map to top-level directories like `Usernames`, `Passwords`, `Discovery`, and `Payloads`. The `.bin` directory holds wordlist generators and mutators, which are scripts, not just static files. That is a notable design choice: SecLists is both a data dump and a small collection of tooling. The data flow is simple: you download the repository, then point your own tools, such as ffuf or hydra, at the files. There is no API, no database, no service. The value is in the aggregation and organization. You get a lot of lists, but you have to know which one fits your use case. The README does not offer a metadata index or tags, so finding the right list often means browsing.
Installation: Four Paths, Each With a Catch
The README lists five install methods. The zip download is a one-liner: `wget -c https://github.com/danielmiessler/SecLists/archive/master.zip -O SecList.zip && unzip SecList.zip && rm -f SecList.zip`. That gets you the current master as a snapshot. The git clone with `--depth 1` is faster because it skips commit history, which is useful since the repository is large. A full clone is also possible. For Linux users, package managers exist: on Kali, `apt -y install seclists`; on BlackArch, `sudo pacman -S seclists`. The package routes are convenient but they may lag behind the GitHub releases, so you might not get the latest 2026.2 content. The zip method is the most direct for a fresh box, but it does not give you an easy update path. With git, you can pull updates, but you carry the repository size. The README also warns that downloading SecLists triggers false positives from antivirus software; you need to whitelist the filepath. That is a practical constraint for corporate environments.
The Maintenance and Upgrade Reality
SecLists is actively maintained, with its latest release, 2026.2, on 2026-10-27 and a sponsor page for the maintainers. However, the README does not describe a formal contribution process beyond a link to CONTRIBUTING.md. The repository is a collection of lists from many sources, and the README does not describe what changed between releases such as 2026.1 and 2026.2. That is a limitation. Upgrade cost is low if you use git: a `git pull` gets new lists. But the cost is in curation. There is no deduplication or quality control visible in the README. Some lists may be outdated, especially in the password and username categories, where attack patterns change. The README points to similar projects like Assetnote Wordlists, which are updated monthly, implying that SecLists does not have that cadence. For a security tester, using a stale wordlist can mean missing a vulnerability or wasting time on dead ends. You have to check the file dates and content yourself.
Limitations and Failure Modes
The biggest failure mode is false confidence. A large list does not guarantee coverage. The README explicitly warns about storing SecLists on a server due to local file include attacks. That is a security risk: if an attacker can trick an application into reading a file from SecLists, they might find a payload that works. The README says the files themselves are harmless, but the risk is real. Another limitation is size. The full clone is heavy, and the `--depth 1` option is there for a reason. On a low-bandwidth testing box, downloading the whole repo can take time. Also, the repository is not a tool, so you need other software to use the lists. SecLists does not run scans or generate requests. It is passive data. For someone expecting an all-in-one solution, that is a mismatch. Finally, the content is not always accurate or current. The README does not claim freshness, so you cannot assume the lists match the latest attack techniques.
Alternatives: Where SecLists Falls Short
The README lists several similar projects, and each takes a different approach. Assetnote Wordlists are high quality and auto-updated monthly, focused on content and subdomain discovery. That is a direct competitor for the `Discovery` part of SecLists. If you need fresh, curated lists for web fuzzing, Assetnote is a better bet. FuzzDB is a dictionary of attack patterns and primitives for fault injection, which is more structured than SecLists' raw files. PayloadsAllTheThings is a collection of payloads and bypasses for web security and CTF, that the README describes as a list of useful payloads and bypasses. The key difference is that SecLists is a broad, uncurated dump, while these alternatives are narrower and more focused on quality or context. For password cracking, SecLists has a `Passwords` directory, but tools like CeWL generate custom wordlists from a target site, which is a different approach. The README also mentions SamLists, which is data-driven with HTTP parameter names, a more specific use case.
Licensing and Practical Use
SecLists is MIT-licensed, which is permissive. You can use the lists in commercial tools or redistribute them, though you should keep the license notice. The README does not specify attribution requirements beyond a CONTRIBUTORS.md file. The practical implication is low friction for adoption. However, the repository contains data from many sources, and the MIT license may not cover all individual lists. That is a legal gray area, but I am not giving legal advice. For a security tester, the license is not a barrier. The bigger issue is the `.bin` directory, which contains generators and mutators. These are scripts, and they may have their own dependencies. The README does not document them, so you have to read the source to use them. That is a maintenance cost. Overall, SecLists is a convenient starting point, but you must treat it as a raw material, not a finished product.
Editorial conclusion
Adopt SecLists if you are a penetration tester or bug bounty hunter who needs a broad, ready-made set of wordlists for content discovery, password cracking, or fuzzing, and you can tolerate a repository that grows by accretion. Do not adopt it if you need curated, deduplicated, or frequently updated lists, or if you plan to store the data on a production server, since the README warns about local file include risks. Before relying on it, verify which lists are current for your target: check the dates in the `Discovery` directory and test a few samples against your own corpus. The project is maintained, with a 2026.2 release on 2026-10-27, but the content quality varies by directory, so treat each list as a starting point, not a final answer.
Frequently asked questions
What are SecLists?
It is a collection of multiple types of lists used during security assessments, gathered in one place. The stated goal is that a tester can pull the repository onto a new testing machine and have access to every list type that might be needed, with list types including usernames, passwords, URLs, sensitive data patterns, fuzzing payloads and web shells. It is maintained by Daniel Miessler, Jason Haddix, Ignacio Portal and g0tmi1k, and is MIT licensed.
how to install seclists
There are five routes. A zip download, a shallow git clone with --depth 1 for speed, a complete git clone, or the distribution packages, where Kali Linux uses apt -y install seclists and BlackArch uses sudo pacman -S seclists. Every git and zip route resolves to the master branch rather than to a release, so the version you get is whatever master held when you ran the command.
how to install seclists in kali linux
Kali packages the collection, so the install is a single command: apt -y install seclists. Kali has its own tool page for it. Because it is a distribution package, its version is fixed by Kali's schedule rather than by the repository, so it will not track the master branch commit for commit and may be a release behind it.
how to use seclists
You point a testing tool at a file inside one of the nine top-level list directories, and the path you pass is the whole interface. The repository also has a .bin directory holding wordlist generators and mutators, which the README recommends you look at when you need to permute or combine lists rather than write a script yourself. The README does not document which tool expects which list, so the mapping is something you establish yourself.
What is a seclist file?
A list of terms, one per line, in a directory named for the list type. The repository groups them into Ai, Discovery, Fuzzing, Miscellaneous, Passwords, Pattern-Matching, Payloads, Usernames and Web-Shells. It does not document a line format, a schema, or per-list metadata, so the README does not tell you the encoding, the sort order, or when an individual list was last regenerated.
What is the difference between SecLists and other lists?
SecLists is broad, covering passwords, usernames, discovery, fuzzing and payloads in one repository, and it releases a few times a year. The alternatives it names each bet more narrowly: Assetnote Wordlists focuses on content and subdomain discovery and is updated every month, fuzz.txt on potentially dangerous files, FuzzDB on black-box fault injection patterns, and SamLists on HTTP parameter names, directory names and filenames. For enumeration work, that update frequency is the difference worth checking.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/danielmiessler-seclists)Star history chart for your README
[](https://hysenlabs.com/projects/danielmiessler-seclists)Was this useful?