RustNet: per-process network monitoring in the terminal
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
At a glance
- What is it?
- RustNet shows live TCP, UDP and QUIC connections with process attribution when available, adds deep packet inspection, and uses platform sandboxing where supported. It sits between netstat and Wireshark.
- Who is it for?
- Adopt RustNet if you need to answer which process opened a connection on a machine you already have shell access to, and you want the answer without X11 forwarding or a root tcpdump pipe. Skip it if you need full packet payloads or a guaranteed lossless capture, which the README does not promise.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 16, 2026, and from our analysis. They are not legal advice.
Star history
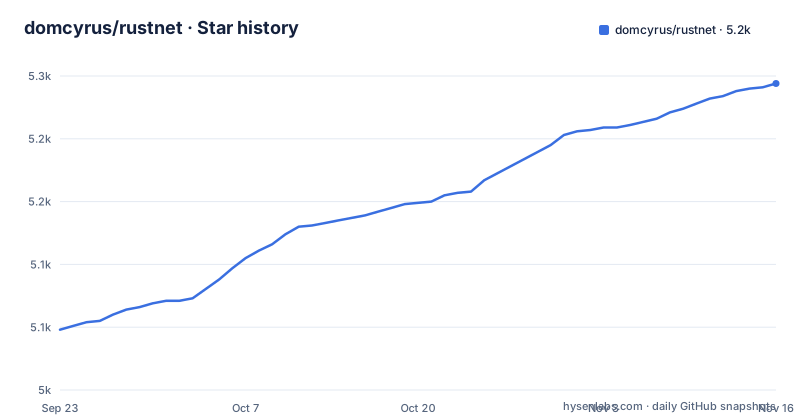
- domcyrus/rustnet5,244 ★ · +196
| Repository | 2026-09-23 | 2026-11-16 |
|---|---|---|
| domcyrus/rustnet | 5k | 5.2k |
196 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The gap RustNet targets between netstat and Wireshark
Tools such as `ss` and `netstat` show socket state and can also display owning process information with the appropriate option and permissions. Packet analyzers focus on captured traffic. RustNet combines a live terminal view of connections and packet-derived protocol information with process attribution when available.
The tool is aimed at engineers who are already on the box. The README calls out SSH-friendliness as a design goal: the TUI runs over an SSH session, so you can look at a remote server without forwarding X11 or piping a capture back to your laptop. That is the audience. Not a network operations centre running continuous capture, but someone debugging why a host is talking to an address they do not recognise, or which of twelve services on a machine is holding a connection open.
Attribution is per platform: the Linux build enables eBPF by default, while on macOS PKTAP requires sudo and, with only BPF access, RustNet uses lsof for process detection. The README says process attribution is shown when available, so it is not guaranteed for every connection.
How capture, parsing and connection state fit together
The README leaves platform backends and performance to ARCHITECTURE.md and does not describe the capture pipeline, queue sizes or idle handling.
The workspace splits the code into four library crates plus the binary: rustnet-core, rustnet-capture, rustnet-host and rustnet-sandbox, all at version 0.6.0, while the binary tracks the 1.x user-facing line at 1.7.0. rustnet-host holds the eBPF programs and bundled vmlinux headers compiled by its own build.rs, and rustnet-core carries the baked-in oui.gz and services assets.
Installing RustNet and reading your first connection list
The repository ships a Dockerfile, and the README sends Docker users to the installation guide. The Dockerfile is multi-stage: a rust:1.98-slim builder pinned by digest installs libpcap-dev, libelf-dev, zlib1g-dev, clang, llvm, make and pkg-config, then builds in release mode, and the runtime stage is debian:trixie-slim, also pinned by digest. On Linux, eBPF is enabled by default in that build. The Kubernetes feature is additive and off unless you pass it through the build argument the Dockerfile defines:
ARG CARGO_FEATURES=""
RUN if [ -n "$CARGO_FEATURES" ]; then \
        cargo build --release --features "$CARGO_FEATURES"; \
    else \
        cargo build --release; \
    fi
The Dockerfile comment states that the CI Kubernetes image variant passes CARGO_FEATURES=kubernetes, while the default image leaves it empty. The README points at INSTALL.md for platform packages, and the debian/ and rpm/ directories exist at the top level, so distribution packaging is part of the repository rather than an afterthought. The crate is published as rustnet-monitor on crates.io. Once installed, the first thing to check is which build you actually have, because the README warns that main documents unreleased features:
rustnet --version
rustnet --help
The README states that for the installed release you should use the v1.7.0 documentation, and check rustnet --version and rustnet --help, because the guides linked from main may describe unreleased changes.
For a first real use, start the TUI: press / to filter connections, Enter to inspect one, and q to quit. Captures can be exported as PCAP or PCAPNG with best-effort annotations for analysis in Wireshark; the usage guide covers the options.
Sandboxing, and what a failed privilege drop actually does
RustNet reduces privileges after startup and uses platform sandboxing where supported. The README leaves sandboxing and privilege management to SECURITY.md, which is the file to read before you put it in a pipeline. Since v1.7.0, RustNet also requires trusted directories for Unix output files and creates diagnostic logs exclusively.
Where RustNet is the wrong tool
RustNet is a terminal monitor of connections, and the README makes no claim of lossless capture. If your job is to produce a forensically complete capture of a busy 10 GbE link, RustNet is not that tool. Use a dedicated capture stack and accept that you will lose process attribution.
Payload inspection is the second boundary. Packet inspection here identifies protocols such as HTTP, TLS/SNI, DNS, SSH, and QUIC. Identifying a protocol is not the same as giving you the bytes. If you need to read a TLS record or reconstruct a stream, the PCAPNG export is the handoff point, not the TUI.
The third boundary is the documentation itself. The README warns that the guides linked from main may describe unreleased changes, so anyone evaluating from the repository front page may read about behaviour a released binary does not have. That is a real cost for an evaluator, and a reason to pin your reading to the v1.7.0 README and to CHANGELOG.md.
How RustNet differs from Sniffnet and Bandwhich
The closest alternatives are Sniffnet and Bandwhich, and the difference is structural rather than cosmetic. Sniffnet is a packet-level traffic monitor: it presents captured traffic and its statistics. RustNet starts from the socket side and attaches process ownership to each connection, which is the inverse starting point. A Sniffnet user looking for per-process attribution has to correlate separately; RustNet's README frames that correlation as the product.
Bandwhich also does per-process bandwidth attribution, and the comparison is closer. The distinction is depth of protocol work: RustNet adds packet inspection for protocols such as HTTP, TLS/SNI, DNS, SSH and QUIC, passive DNS analytics, connection health, and PCAP or PCAPNG export with best-effort annotations. Whether that extra depth is worth it depends on whether you need protocol identification or only a ranked list of talkers. For a quick answer to which process is saturating a link, the lighter tool is sufficient and RustNet is more machinery than the question requires.
On the netstat side, RustNet's difference is a live view rather than a snapshot. That is the honest summary of the alternative: if a snapshot is enough, you already have the tool installed.
Maintenance, licence and the cost of upgrading
The repository is not archived, and the last push was on 2026-11-02. Releases have come at a steady cadence through 2026: v1.5.0 on 2026-07-21, v1.6.0 on 2026-08-20, and v1.7.0 on 2026-10-06. The binary version is decoupled from the library crates, which sit at 0.6.0, and Cargo.toml notes that the binary keeps its own version because it tracks the 1.x release line independently. That means a workspace version bump is a one-line edit in the shared metadata section, but it also means you cannot infer the binary version from the crate versions.
The rust-version is 1.88.0, with a comment that let-chains require it. Edition is 2024. If you build from source rather than installing a package, that is your toolchain floor, and the Dockerfile pins rust:1.98-slim as the builder, so container builds are well above it.
Licence is Apache-2.0 across the workspace, declared once in the shared package metadata. Apache-2.0 is permissive and includes an explicit patent grant, which matters for a tool that links against kernel interfaces. It also means there is no copyleft obligation on your own code. This is a description of the licence text, not legal advice; if you are redistributing a modified binary, read LICENSE and the NOTICE situation for the bundled assets, since rustnet-core bakes in an OUI database and a services file.
The upgrade cost is documentation drift. Because main describes unreleased behaviour, an upgrade from v1.7.0 to the next release is where the changes listed as unreleased actually land. Read CHANGELOG.md rather than the README diff when you move, and re-check rustnet --help, because the README states that --help is the authority on which options your installed build supports.
Editorial conclusion
Adopt RustNet if you need to answer which process opened a connection on a machine you already have shell access to, and you want the answer without X11 forwarding or a root tcpdump pipe. Skip it if you need full packet payloads or a guaranteed lossless capture, which the README does not promise. Before rolling it out, check rustnet --version against the v1.7.0 documentation, since the guides linked from main may describe unreleased changes, and read SECURITY.md for how sandboxing applies on your platform.
Frequently asked questions
How is Rust used in networking?
RustNet is one example: it is written in Rust and uses the language for a capture pipeline where packet parsing runs in parallel while connection updates keep capture order. The workspace uses Rust 2024 edition and requires rust-version 1.88.0, noted in Cargo.toml as needed for let-chains.
How do I install RustNet on Linux?
The README points to INSTALL.md and the repository carries debian/ and rpm/ directories for distribution packaging, plus a Dockerfile; the README also gives commands for the Ubuntu PPA, Fedora COPR, Arch, Alpine, Nix, Homebrew and Cargo. The crate is published on crates.io as rustnet-monitor.
Does RustNet work on Windows and macOS?
Yes. The README lists Linux, macOS, Windows and FreeBSD as supported, with Windows also requiring Npcap, and on macOS PKTAP requiring sudo (with BPF access it can run without it but uses lsof for process detection). It uses platform sandboxing where supported, described in SECURITY.md.
Which documentation matches an installed RustNet release?
The README says the guides linked from main may describe unreleased changes, listed in CHANGELOG.md, and points installed users to the v1.7.0 documentation plus rustnet --version and rustnet --help. It also notes v1.6.0 assets lack the v1.7.0 ARM DEB fixes.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/domcyrus-rustnet)Star history chart for your README
[](https://hysenlabs.com/projects/domcyrus-rustnet)Was this useful?