YubiKey-Guide: A Hardened, Offline Path to GnuPG and SSH Keys
Community guide to using YubiKey for GnuPG and SSH - protect secrets with hardware crypto.
At a glance
- What is it?
- drduh's YubiKey-Guide is a community-built manual for storing GnuPG and SSH private keys on a YubiKey, with an emphasis on offline key generation and defense against physical compromise. It is a thorough, security-first resource that demands patience and a willingness to follow strict procedures.
- Who is it for?
- Adopt this guide if you are a security-conscious individual or system administrator who wants hardware-backed private keys for GnuPG and SSH, and you are willing to dedicate a few hours to a careful, offline setup. Do not use it if you need a quick, GUI-driven solution or if your YubiKey lacks the OpenPGP application (e.g., Security Key or Bio models).
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 12 days ago.
- What is it written in?
- Mainly HTML, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
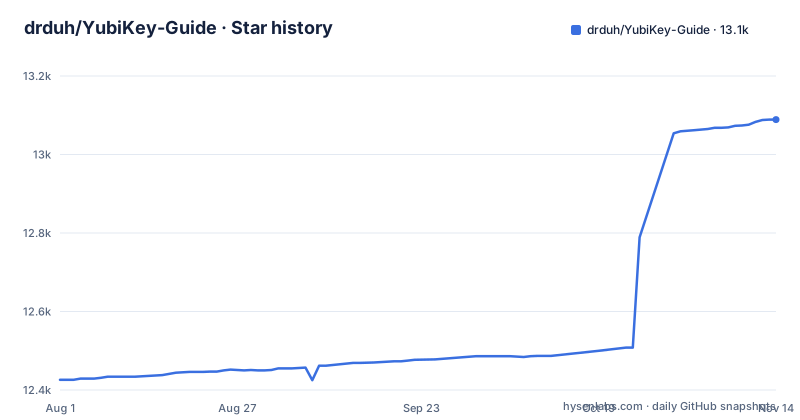
- drduh/YubiKey-Guide13,089 ★ · +663
| Repository | 2026-08-01 | 2026-11-14 |
|---|---|---|
| drduh/YubiKey-Guide | 12.4k | 13.1k |
663 Stars in the last 105 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What Problem This Guide Actually Solves
The YubiKey-Guide addresses a specific failure mode: private keys stored on a computer can be copied, stolen, or extracted by malware. By moving the private key material into a hardware token that refuses to export it, the guide makes key compromise significantly harder. The intended audience is not the average user. It is for engineers, security researchers, and administrators who manage long-lived GnuPG keys for signing, encryption, and SSH authentication, and who are willing to accept a more complex setup in exchange for a stronger boundary. The guide's opening statement is blunt: private keys cannot be copied back out of the device. That is the entire point. A separate offline 'Certify' key is retained, but only to replace or renew the subkeys, never for daily use. This separation is the core design that the rest of the document builds on.
The Offline Key Generation Mechanism
The guide's architecture is built around a hierarchy of keys. You create a Certify key on an air-gapped or ephemeral system, then derive three subkeys: Signature, Encryption, and Authentication. Only the subkeys are transferred to the YubiKey. The Certify key stays offline, usually on encrypted media in a safe place. This is a deliberate trade-off. If the YubiKey is lost or compromised, you can revoke the subkeys and issue new ones from the Certify key. If the Certify key were also on the YubiKey, you would lose the ability to rotate subkeys after a hardware failure. The guide stresses that the environment used for key generation must be dedicated and hardened. It ranks environments from least to most secure, starting with a shared computer and ending with an air-gapped ARM device. For most people, it recommends booting Debian Live from USB, which gives a clean, isolated operating system without touching the host's storage. The key generation itself happens entirely offline, with network access disabled, so no private key material ever touches a connected system.
Step-by-Step Setup: From Debian Live to YubiKey
The guide walks through every command, but the critical path is long. You start by downloading and verifying a Debian Live image. The README gives exact curl commands to fetch the SHA512SUMS file and its signature, then verifies both with gpg. The Debian signing key fingerprint is provided, and there is a fallback keyserver if the primary one is unreachable. After creating a bootable USB drive with dd, you boot into the live environment. Then you install GnuPG and related software, configure gpg with a specific algorithm and expiration policy, and create the Certify key. The YubiKey configuration steps are equally explicit: change the PIN, set attributes, and then transfer each subkey one by one. The guide includes commands for verifying that the transfer succeeded, such as checking that the private key is stored on the card and not in the local keyring. This is not a one-command setup. It is a sequence of deliberate actions, each with a verification step, which is exactly what a security-critical process should look like.
Using the Keys: SSH, GitHub, and Email Integration
Once the YubiKey is configured, the guide covers practical usage. For SSH, it explains how to replace the standard ssh-agent with gpg-agent, which can expose the authentication subkey through the OpenPGP card. The README includes commands to copy the public key to a remote server and to configure agent forwarding, both via ssh-agent and via the S.gpg-agent.ssh socket. There is a section on chained forwarding, which matters if you need to hop through multiple hosts. For GitHub, the guide shows how to add the SSH public key to your account. Email is handled through Thunderbird, Mailvelope, and Mutt, each with its own section. The common thread is that the private key never leaves the YubiKey. Every signature or decryption operation triggers the card, and the guide even explains how to require a physical touch for each operation, which is a useful defense against remote use if the key is plugged into a compromised machine. This section is practical, but it assumes you already know the basics of SSH and GnuPG. Beginners will need to look up terms like 'agent forwarding' and 'subkey' elsewhere.
Genuine Limitations and Failure Modes
The guide is not a silver bullet. The most obvious limitation is that it only works with YubiKey models that include the OpenPGP application. The Security Key and Bio models do not support OpenPGP, so they are explicitly excluded. That is a hard filter. Another limitation is the setup itself. The guide requires a dedicated, offline environment, which is a significant barrier for most users. The README acknowledges this by ranking environments, but it does not sugarcoat the fact that the recommended baseline is booting a live operating system. If you are not comfortable with dd, gpg, and the command line, this guide will be painful. There is also a failure mode that the guide does not fully address: the YubiKey itself can be lost or damaged. The guide covers resetting the YubiKey and rotating subkeys, but if you lose both the key and the offline backup, your data is gone. The guide tells you to store encrypted backups on multiple USB drives, but it does not automate or enforce that. Finally, the guide's security model depends on the host being reasonably clean. If you use the YubiKey on a compromised computer, an attacker can still read your signed or decrypted data in memory. The hardware token only protects the private key, not the data flow around it.
Maintenance and Upgrade Costs
The guide includes a section on updating keys. It covers renewing subkeys before they expire and rotating them when necessary. This is a real maintenance burden. You need to keep the offline Certify key accessible, which means maintaining a secure backup that does not degrade over time. The guide also discusses resetting the YubiKey, which is a full wipe and reconfiguration. That is a destructive operation, and the guide warns about it. The license is MIT, so there are no licensing restrictions on using or modifying the guide. However, the guide is a living document. It is updated as GnuPG, YubiKey firmware, and SSH evolve. That means you should occasionally revisit the repository to see if any commands or recommendations have changed. The README notes that the guide is community-maintained, so there is no formal support. If you hit a problem, the guide has a Troubleshooting section. The cost is not in money, but in time and attention. This is not a set-and-forget tool.
Alternatives: Different Approaches to Hardware Keys
The most direct alternative is Yubico's own personalization tools and documentation, which provide a more GUI-driven path to enable the OpenPGP applet and load keys. The difference is that Yubico's official material does not push the offline generation process as hard. You can generate keys on your daily machine and transfer them, which is faster but less secure. Another alternative is using a different hardware token, such as a Nitrokey or a Trezor. For SSH specifically, you could use a YubiKey's FIDO2 or PIV interfaces instead of OpenPGP, which are supported by ssh-agent in newer OpenSSH versions. That approach is simpler for SSH-only use, but it does not integrate with GnuPG for email signing and encryption. The guide's choice of OpenPGP is deliberate because it covers all three use cases with one key hierarchy. If you only need SSH, a FIDO2-based security key might be a lower-friction choice, but you lose the ability to sign or encrypt email with the same hardware. The guide lists alternative solutions in its own section.
Editorial conclusion
Adopt this guide if you are a security-conscious individual or system administrator who wants hardware-backed private keys for GnuPG and SSH, and you are willing to dedicate a few hours to a careful, offline setup. Do not use it if you need a quick, GUI-driven solution or if your YubiKey lacks the OpenPGP application (e.g., Security Key or Bio models). Before starting, verify your YubiKey model supports OpenPGP, prepare at least two USB drives for encrypted backups, and confirm you can boot a Debian Live or Tails environment. The guide's value lies in its uncompromising offline procedure; skip that and you lose the core benefit.
Frequently asked questions
How do I use a YubiKey as a beginner?
The first step is the model, since YubiKey Security Key and YubiKey Bio have no OpenPGP support and cannot be used with the guide. Then verify the key at yubico.com/genuine by selecting Verify Device and touching it when prompted, prepare a hardened environment with Debian Live on USB as the practical baseline, and hold at least two USB drives or microSD cards in different physical locations for encrypted offline backups.
Can I leave my YubiKey plugged in all the time?
The guide does not give one blanket rule, but it gives you the controls. The Certify key stays offline, only the signature, encryption and authentication subkeys move onto the device, and separate chapters cover Configure touch, Change PIN and Set attributes. What decides how often the device must be touched is in those chapters, not in a single line near the top.
What are the best practices for using a YubiKey?
Keep an offline Certify key, since private keys cannot be copied back out of the device and that key is what lets you replace or renew the others. Keep at least two encrypted offline backups in different physical locations, generate keys in a dedicated hardened environment rather than on a shared or daily-use machine, and check the device path yourself before running the guide's dd command, since its /dev/sdc is only an example.
Is YubiKey still relevant?
The guide is MIT licensed, published as HTML at drduh.github.io/YubiKey-Guide, and its last push was on 2026-11-02. Its chapters still run the full lifecycle, from key generation and subkey transfer through SSH and GnuPG agent forwarding, email clients, renewal, rotation, reset and optional hardening. It has no tagged release, so what you read is whatever the repository currently holds.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/drduh-yubikey-guide)Star history chart for your README
[](https://hysenlabs.com/projects/drduh-yubikey-guide)Was this useful?