NPS: A Self-Hosted Intranet Penetration Proxy with a Web UI That Does the Heavy Lifting
A lightweight, high-performance, powerful intranet penetration proxy server, supporting TCP, UDP, SOCKS5, HTTP and nearly all forms of traffic forwarding - usable for accessing intranet sites, local payment-interface debugging, SSH access, remote desktop, intranet DNS resolution, intranet SOCKS5 proxying and more, with a powerful web management console.
At a glance
- What is it?
- NPS is a Go-based intranet penetration proxy that exposes internal TCP, UDP, HTTP, and SOCKS5 services to the internet. It pairs a lightweight client and server with a web management interface, but its last release is from 2021, so verify current needs before adopting.
- Who is it for?
- Adopt NPS if you need a self-hosted, multi-protocol intranet penetration tool with a web UI and can live with a project that has not seen a release since April 2021. Avoid it if you require active maintenance, frequent security updates, or a strong community.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Probably not. The repository last received commits 29 months ago, on May 30, 2024.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
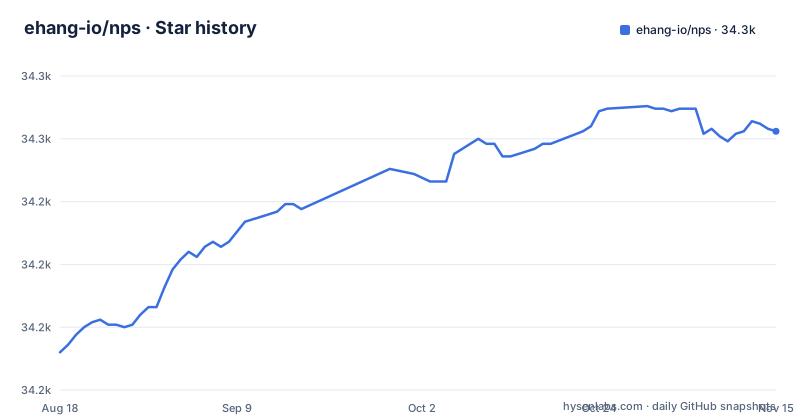
- ehang-io/nps34,253 ★ · +88
| Repository | 2026-08-18 | 2026-11-15 |
|---|---|---|
| ehang-io/nps | 34.2k | 34.3k |
88 Stars in the last 89 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What NPS Solves and Who It Is For
NPS solves the problem of making services on a private network reachable from the internet without opening a public IP or configuring complex router rules. It is aimed at developers and administrators who need to access internal websites, debug local payment interfaces, SSH into home machines, use remote desktop, or run internal DNS and SOCKS5 proxies. The README positions it as a lightweight, high-performance proxy server with a web management terminal. The target user is someone who wants a single tool that covers TCP, UDP, HTTP, HTTPS, SOCKS5, and P2P traffic, and who prefers a graphical interface over editing config files. It is not for someone who wants a cloud-managed service; NPS is self-hosted, meaning you run the server component on a machine with a public IP.
How NPS Works: Server, Client, and the Bridge
NPS uses a client-server architecture. The server, called nps, runs on a machine with a public IP. The client, called npc, runs on the machine inside the private network. The two communicate over a net bridge, which by default listens on port 8024. The server also exposes a web management interface on port 8080, and ports 80 and 443 are used for host mode, which maps domain names to internal services. When a client connects, it registers with the server, and then you configure the actual penetration rules through the web UI. For example, you can create a TCP tunnel that forwards traffic from a specific port on the server to an internal service. The documentation states that the client and server are separate downloads, so you deploy each on the appropriate machine. The README lists extension functions such as cache, compression, encryption, traffic limit, bandwidth limit and port reuse. The web UI is not just for configuration; it also displays traffic, system information, real-time bandwidth, and client versions.
Getting NPS Running: Commands and Default Ports
Installation is straightforward for Linux, macOS, and Windows. For Linux or macOS, you download the server package, unzip it, and run `sudo ./nps install`. For Windows, you run `nps.exe install` from an administrator command prompt. After installation, the configuration file is placed in `/etc/nps` on Linux or macOS, and in `C:\Program Files\nps` on Windows. To start the server, you run `sudo nps start` on Linux or macOS, or `nps.exe start` on Windows. The default configuration uses four ports: 80 and 443 for host mode, 8080 for the web management interface, and 8024 for the net bridge. You access the web UI by navigating to the server IP on port 8080 and log in with the default credentials admin/123, which the README warns must be changed. To connect a client, you create a client in the web UI, copy the startup command, and execute it on the internal machine.
What the Web UI Actually Lets You Control
The web management terminal is the centerpiece of NPS. Instead of editing config files or restarting services, you create clients and configure tunnels through the interface. The README claims that simple configuration on the web UI can complete most requirements. For each client, you can add multiple tunnels, each with a protocol and a mapping. For HTTP and HTTPS, you can set domain names, custom headers, 404 page configurations, host modification, site protection, URL routing, and pan-resolution. For TCP and UDP, you specify a server port and an internal target address. The UI also shows real-time bandwidth, traffic usage, and client versions, which helps you monitor active connections. This is a major advantage over tools that require command-line configuration, especially for users who manage many clients or non-technical colleagues.
Limitations and Failure Modes
The most obvious limitation is that the project has not had a release since v0.26.10 in April 2021. That means no tagged release with fixes since then, although the last push to the repository was on 2024-05-30. Another failure mode is the default credential problem: admin/123 is a well-known default, and if you forget to change it, anyone who can reach the web UI can control your tunnels. The README also notes that if the server does not start, you need to check the log, but it does not describe common errors. The architecture has a single point of failure: all traffic goes through the server, so if the server goes down, every tunnel goes down. This is expected for a proxy, but it means you need a reliable public IP and server uptime. Also, the README claims support for P2P, but the details are in the documentation, which is not part of the README; you should verify that P2P works for your use case before relying on it.
Alternatives: What Else Is Out There
The most common alternative to NPS is frp, another open-source intranet penetration tool written in Go. frp uses a similar client-server model but relies on a configuration file for the client, not a web UI. This is a fundamental difference: frp requires you to edit a configuration file on the client machine, which is more manual but also more explicit and easier to version-control. NPS's web UI is its main differentiator, for anyone who prefers a graphical interface. The README does not mention frp, but the comparison is inevitable for anyone evaluating intranet penetration tools.
Licensing and Maintenance Costs
NPS is licensed under GPL-3.0. This has implications if you modify the code or integrate it into a proprietary product. The GPL requires that derivative works be licensed under GPL-3.0 as well, so if you plan to distribute a modified version, you must make the source available. For internal use, this is rarely a problem, but if you offer NPS as a service or bundle it with commercial software, you need to understand the obligations. The maintenance cost is low in the short term because the installation is simple and the web UI reduces configuration errors. However, the lack of updates since 2021 is a long-term cost: you will have to maintain any patches yourself or risk running an outdated proxy. The documentation is available at ehang.io/nps/documents, but it may also be stale. Before adopting, check the issue tracker for unresolved bugs and see if the community has forked the project. The last push was on 2024-05-30 and the last release was in 2021, so treat it as a largely frozen codebase.
Editorial conclusion
Adopt NPS if you need a self-hosted, multi-protocol intranet penetration tool with a web UI and can live with a project that has not seen a release since April 2021. Avoid it if you require active maintenance, frequent security updates, or a strong community. Before using it in production, verify the GPL-3.0 licensing implications for your distribution, review the default credentials (admin/123) and change them immediately, and check the documentation for any known issues with your platform. You should also test the client-server bridge on your network to ensure ports 80, 443, 8080, and 8024 are free and reachable.
Frequently asked questions
Which ports does the NPS server need?
The default configuration uses four: 80 and 443 for host mode, 8080 for the web management access port, and 8024 as the net bridge port used to communicate between server and client. The bridge port is the one every client machine has to be able to reach.
What are the default NPS login credentials?
The username is admin and the password is 123, and the README says they must be modified when the software is put to official use. You reach the terminal at the server IP and the web service port, which defaults to 8080.
How do I start the NPS client on Windows?
Click the plus sign in front of the client entry in the web management terminal, copy the startup command it produces, replace ./npc with npc.exe, and run it from cmd. Registering it as a system service is documented separately from the quick start.
Where are the NPS configuration and log files?
On linux and darwin the configuration file is at /etc/nps and the log at /var/log/nps.log. On Windows the configuration is at C:\Program Files\nps while the log files are written to the directory you launched the program from.
Which branch should a pull request to NPS target?
The contribution section asks for bugs and code changes to go to the dev branch, and feature feedback through issues. The default branch is master, and the binaries in the quick start come from the releases page rather than from either branch.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/ehang-io-nps)Star history chart for your README
[](https://hysenlabs.com/projects/ehang-io-nps)Was this useful?