Ente: A Monorepo for End-to-End Encrypted Photos, 2FA, and Document Storage
End-to-end encrypted cloud for everything. On top of this platform, we have built three apps so far: Ente Photos (an alternative to Apple and Google Photos), Ente Locker (a safe space for your most important documents and credentials), and Ente Auth (a 2FA alternative to the deprecated Authy).
At a glance
- What is it?
- Ente is an open source platform that builds three end-to-end encrypted apps on a shared server and client codebase. This review covers what it solves, how it works, and where its trade-offs lie for adopters.
- Who is it for?
- Adopt Ente if you need a self-hostable, end-to-end encrypted alternative to Google Photos, Authy, or a document vault, and you are comfortable with the AGPL-3.0 license and a Dart-based codebase. Do not adopt it if you require a permissive license for proprietary integration, or if you want to build and self-host a single app without the rest of a monorepo that bundles three apps and a server.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Dart, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
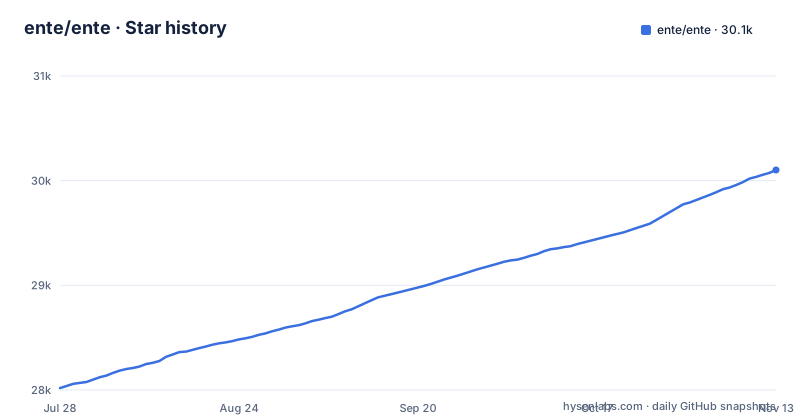
- ente/ente30,102 ★ · +2,084
| Repository | 2026-07-28 | 2026-11-13 |
|---|---|---|
| ente/ente | 28k | 30.1k |
2,084 Stars in the last 108 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The Problem: Trusting Cloud Providers with Your Data
Ente addresses a specific pain point: cloud storage services that can read your data. Google Photos and Apple Photos offer convenience, but they also have access to your original files. Authy, the popular 2FA app, is being deprecated, leaving users to find a replacement. Ente's answer is a platform where encryption happens on your device before anything reaches the server. The README states that you can store data "without needing to trust the service provider." This is for individuals and families who want photo backup, document storage, or 2FA codes without conceding privacy. It is also for developers who want to self-host an encrypted cloud service, since the entire monorepo is open source.
Architecture: A Shared Platform with Three Apps
The repository is a monorepo containing both client apps and the server that powers them. The primary language is Dart, and the client apps cover iOS, Android, F-Droid, Web, Linux, macOS, and Windows. The server is also in the same repository. The core idea is that all three apps, Ente Photos, Ente Auth, and Ente Locker, build on the same end-to-end encryption platform. The README claims that the source code and cryptography have been externally audited by Cure53, Symbolic Software, and Fallible. That is a concrete claim in the README, but it does not tell you which version was audited or the audit scope. The architecture is a trade-off: a unified platform reduces duplication, but it also means anyone building from source works with the whole platform.
Ente Photos: The Flagship with a Free Tier
Ente Photos is the main product. It positions itself as a direct alternative to Apple and Google Photos. The feature list from the README includes 3x data replication, face detection, semantic search, private sharing, collaborative albums, family plans, easy import and export, and background uploads. All of this is end-to-end encrypted. The service is paid, but there is a 10GB free storage tier. For self-hosters, the README says you can clone the repository and self-host. For self-hosting details, check the repository's docs/ and server/ directories. Recent releases, such as photos-v1.3.68, indicate active development.
Ente Auth and Locker: Free Tools with Limits
Ente Auth is a free 2FA authenticator app, built because the team saw no open source end-to-end encrypted alternative to Authy. It is free forever, according to the README. Ente Locker is a newer app for storing documents, credentials, and notes. It is free for up to 100 items, and if you subscribe to Ente Photos, you get 1000 items. Both apps are available on iOS and Android. The limitation here is clear: Locker's free tier is capped at 100 items, which may be too small for a power user. The apps are separate, but they share the same underlying encrypted storage, so you get a consistent security model across them.
Getting It Running: Commands and Config
The README says you can clone this repository and choose to self-host, and the repository carries server/, infra/, docs/ and architecture/ directories alongside the mobile/, web/, desktop/ and cli/ client code. The README links to ente.com for more details; for build and self-hosting steps, consult docs/ and the server/ directory before planning a deployment. This is a real friction point for adopters who expect quick setup.
Limitations and Wrong Use Cases
One genuine limitation is the AGPL-3.0 license. This is a strong copyleft license, which means if you modify the server and offer it as a network service, you must release your modifications under the same license. For a company that wants to build a proprietary product on top of this, that is a deal-breaker. Another limitation is the complexity of the monorepo for anyone building or self-hosting from source; end users can install Ente Auth on its own from the App Store, Play Store or F-Droid. For a small family, the hosted service is fine, but for a large organization, you need to test the server's performance yourself. The Locker app's 100-item free limit is a clear constraint for personal use. Finally, verify data recovery procedures beyond the 3x replication claim before trusting it with irreplaceable photos.
Alternatives and How They Differ
The most direct alternative for photos is Immich, which is also open source and self-hostable. Immich uses a different approach: it is not end-to-end encrypted. Ente's core difference is that encryption is built in from the start, making it a zero-trust design. For 2FA, Aegis is a popular open source authenticator for Android, but it is not end-to-end encrypted with a cloud sync; it stores codes locally. Ente Auth syncs across devices with encryption, which is a different trade-off. For document storage, Bitwarden offers encrypted vaults, but it is focused on passwords, not arbitrary documents. Ente Locker is more general. The key difference across all alternatives is the shared platform and the explicit zero-trust model that Ente promotes.
Maintenance and Upgrade Costs
The project is actively maintained, as shown by recent releases such as photos-v1.3.68 on November 2, 2026 and ente-cli-v0.4.2 on October 27, 2026. The monorepo approach means that a single commit can affect all three apps and the server. For self-hosters, upgrading requires pulling the latest code and rebuilding, which is a standard cost. Check the repository's release notes before upgrading. The license is AGPL-3.0, which has implications if you modify the code. The README mentions external audits, but it does not state whether those audits are updated for each release. That is a maintenance concern: the security guarantee may not cover the latest version. You should verify the audit reports before deploying a new version.
Editorial conclusion
Adopt Ente if you need a self-hostable, end-to-end encrypted alternative to Google Photos, Authy, or a document vault, and you are comfortable with the AGPL-3.0 license and a Dart-based codebase. Do not adopt it if you require a permissive license for proprietary integration, or if you want to build and self-host a single app without the rest of a monorepo that bundles three apps and a server. Before adopting, verify the self-hosting documentation for the server component, check the current state of the Locker app's feature set, and confirm that the Cure53, Symbolic Software, and Fallible audits cover the specific version you plan to deploy. The project is actively maintained with frequent releases, but you must evaluate the operational overhead of running your own server or trust the hosted service.
Frequently asked questions
Is Ente trustworthy?
The README states that the source code and cryptography were externally audited by Cure53, Symbolic Software and Fallible, and the whole platform is AGPL-3.0, so the code is available to inspect and fork. The README sentence making that claim does not name a report, a date or a scope, so look up the audit reports before relying on it.
What does Ente Photos cost?
Ente Photos is a paid service that includes 10GB of free storage. The free tier is one option rather than the only one, because the README also says you can clone the repository and self-host, which moves the cost to the server you run.
Can I self-host Ente?
The monorepo contains the client apps and the server, and the README says you can clone it and self-host. The repository also carries server/, infra/, a .dockerignore, docs/ and architecture/, which are the places to look for deployment details.
What licence is Ente released under?
AGPL-3.0, covering the Photos, Auth and Locker code and the server in the same repository. That is the network copyleft variant of the GPL, which is the term to read carefully if you plan to modify a self-hosted deployment and serve it to users.
Is Ente Auth really free?
The project states that Ente Auth is free and will remain free forever, and asks that people who like it support Ente Photos or spread the word instead. It is distributed on the App Store, Play Store, F-Droid and through Obtainium for GitHub releases.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/ente-ente)Star history chart for your README
[](https://hysenlabs.com/projects/ente-ente)Was this useful?