Fallow: a Rust static analyzer that treats dead code as a graph problem
Codebase intelligence for TypeScript and JavaScript. Free static analysis of code and styles: unused code, duplication, circular deps, complexity hotspots, architecture boundaries, design-system drift. Optional paid runtime layer (Fallow Runtime): hot-path review and cold-path deletion evidence from real production traffic.
At a glance
- What is it?
- Fallow is a free, deterministic code intelligence tool for TypeScript and JavaScript that reports unused code, duplication, circular deps, complexity, boundary violations, and styling drift from a single binary. The optional paid runtime layer adds production evidence, but the static core stands alone.
- Who is it for?
- Adopt Fallow if you work in a TypeScript or JavaScript monorepo and need a deterministic, fast, no-AI static analysis gate for pull requests, especially if you want to avoid running the TypeScript compiler for analysis. Skip it if you need deep type-aware analysis by default (the --type-aware pass is optional), or if you expect runtime evidence without paying for the Fallow Runtime layer.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
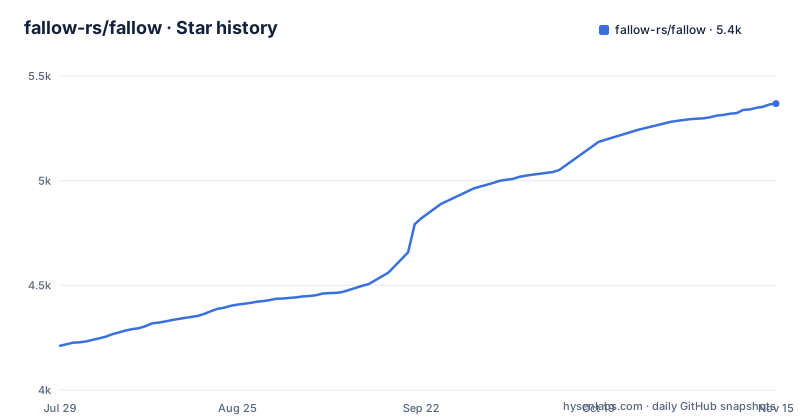
- fallow-rs/fallow5,368 ★ · +1,157
| Repository | 2026-07-29 | 2026-11-15 |
|---|---|---|
| fallow-rs/fallow | 4.2k | 5.4k |
1,157 Stars in the last 109 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What Fallow actually solves
Fallow targets a specific pain: code that nobody deletes because deletion requires proving a negative. Fallow reads the repository as one dependency graph, from import edges to styling tokens, and reports what that graph shows. The tool is for TypeScript and JavaScript projects, including monorepos. It finds unused files, exports, types, enum and class members, and dependencies; circular dependencies; duplication; complexity hotspots; architecture boundary violations; and design-system styling drift. The audience is engineers who want a gate on pull requests, not just a report. The audit command gives a pass, warn, or fail verdict on changed files, which is a concrete workflow fit.
The mechanism: one graph, no compiler, no AI
Fallow's static analysis works by building a single dependency graph from the entire repository. The README stresses two properties: deterministic findings and typed output contracts. No AI is inside the analyzer, and no TypeScript compiler is needed. That is a meaningful architectural choice. Most TS analysis tools either wrap the TypeScript compiler or require a Node environment. Fallow is a Rust binary that parses and analyzes directly. The output is stable: the same input produces the same output with stable fingerprints, so re-running to verify an edit is safe. The graph covers import edges and styling tokens, which is how it can report on CSS and CSS-in-JS drift in the same pass. The optional --type-aware pass adds exact TypeScript symbol identity across aliases, re-exports, and packages, and removes false positives from interfaces and base classes. Without that pass, the analysis is syntactic, which is a trade-off you should know about.
Running it: from zero-install to a configured gate
The quick start is genuinely quick. npx fallow runs the full pipeline with no installation. npx fallow audit gates only what a PR changed. In pull requests it starts with uses: fallow-rs/fallow@v3, in editors with the VS Code extension or fallow-lsp, and for coding agents with npx fallow agent install; all four places read the same config file. The audit gate fails with exit code 1 on findings in changed files, each command has typed JSON output and documented exit codes, and fallow schema prints all commands, flags, output formats, and exit codes as JSON. Over 100 built-in framework plugins find entry points and framework conventions, so the first run needs no config.
The audit gate and inherited findings
The audit command is where Fallow differentiates itself from a plain linter. The README shows illustrative output for a fictional storefront monorepo, auditing 73 changed files against HEAD~15, with 24 circular dependencies, 185 duplicated lines across 6 files, and 28 high complexity functions. The gate fails (exit code 1) on findings in changed files, and findings that existed before the change are excluded. That is a specific mechanism: the audit gate only blocks on findings introduced by the change, not pre-existing ones. This is a sensible default for a PR workflow, but it is also a risk: inherited findings can accumulate silently if nobody addresses them. The README presents this as a feature, and it is, but it means the audit gate alone will not clean up a legacy codebase. You need a separate effort to address inherited debt.
Similar-code and security: opt-in features with real limits
Fallow includes two opt-in features that go beyond the core graph analysis. The first is similar-code discovery, which finds functions that may share intent despite different syntax. The README says this uses a pinned local model that you download once. The second is security candidates, ranked by reachability from entry points, via fallow security. Both features are opt-in, which is the right call for a tool that otherwise promises determinism. But the similar-code model is still a model, so the determinism guarantee does not extend to that feature. If you need reproducible results, the fallow dupes duplication analysis is part of the deterministic core.
Where Fallow is the wrong tool
Fallow has clear limitations. One limitation is the absence of runtime evidence in the static layer. Dead code detection is based on the dependency graph, not on what actually executes in production. That is exactly what the paid Fallow Runtime layer adds: hot-path review and cold-path deletion evidence from real production traffic. If you need to know whether a function is called in production, the free static analysis cannot tell you. The optional --type-aware pass removes false positives from interfaces and base classes, but it is not the default.
Alternatives and the runtime layer
The obvious alternative is the TypeScript compiler itself, or tools built on it like ts-prune or knip. Those tools require a Node environment and often a tsconfig, and they operate on the compiler's type information. Fallow's approach is different: it is a standalone Rust binary that does not need the TypeScript compiler. That makes it faster to install and run, but it means the default analysis is syntactic, not type-aware. For exact symbol usage, you need the optional --type-aware pass. Another alternative is a dedicated duplication tool like jscpd, which handles many languages but does not build a full dependency graph or produce a health score. Fallow's edge is the unified graph: one run gives you dead code, duplication, circular deps, complexity, boundaries, and styling drift in a single typed JSON document. The paid Fallow Runtime layer is not an alternative but an extension: it merges production execution evidence into the same reports. The README frames it as static vs runtime, and the decision to pay depends on whether your deletion risk is driven by production traffic or by static reachability.
Maintenance, licensing, and upgrade cost
Fallow is MIT licensed, which is permissive and low-friction for commercial use. The project is actively maintained, with three releases within a week: v3.38.1 (October 31, 2026) brought audit cache fixes and the VS Code extension back on the marketplaces; v3.38.0 (October 30, 2026) added a file-length limit, Fallow Cloud setup and login, and lean JSON for agents; v3.37.0 (October 27, 2026) added resumable mutation runs, CSS classes from template files, and signed Windows binaries. The release cadence is high, which means you should expect frequent updates. The README publishes an output schema (docs/output-schema.json), and fallow schema prints all commands, flags, output formats, and exit codes as JSON. For upgrade cost, the deterministic output and stable fingerprints help, but you should still test the audit gate after a major version bump, especially if you rely on the JSON output contract.
Editorial conclusion
Adopt Fallow if you work in a TypeScript or JavaScript monorepo and need a deterministic, fast, no-AI static analysis gate for pull requests, especially if you want to avoid running the TypeScript compiler for analysis. Skip it if you need deep type-aware analysis by default (the --type-aware pass is optional), or if you expect runtime evidence without paying for the Fallow Runtime layer. Before adopting, verify how Fallow handles your generated files and framework entry points: run npx fallow, review the findings, and test the audit gate on a small PR to confirm the inherited-findings exclusion matches your workflow.
Frequently asked questions
How do I use fallow on a JavaScript or TypeScript project?
Run `npx fallow` in the root of any JS or TS project. No TypeScript compiler and no configuration are required to start; the terminal, pull request, editor and agent entry points all read the same config file and use the same analysis engine.
Does fallow need a TypeScript compiler or a Node.js runtime?
No TypeScript compiler is needed: the analyzer is one Rust binary. The README runs it with npx fallow. The published Dockerfile still installs Node 26 and corepack in its runtime stage.
What does fallow audit check in a pull request?
`fallow audit` gates changed files on complexity, duplication, unused code and styling drift, with a pass, warn or fail result. It exits 1 on findings a change introduces and excludes findings that already existed before the change.
Which fallow commands are opt-in?
`fallow security` ranks candidates by reachability from entry points, and `fallow similar-code` finds functions with the same intent and different syntax using a pinned local model you download once. Runtime coverage from production is a separate optional add-on merged into health and audit reports.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/fallow-rs-fallow)Star history chart for your README
[](https://hysenlabs.com/projects/fallow-rs-fallow)Was this useful?