mkcert: Local Trust Without the CA Circus
GitHub describes it as A simple zero-config tool to make locally trusted development certificates with any names you'd like.. The repository metadata lists Go as its primary language. The metadata lists the BSD-3-Clause license. This article stays within the project description and details documented in the GitHub repository README.
At a glance
- What is it?
- mkcert creates a local certificate authority, installs it in your system trust store, and issues certificates for any name you need. It is a zero-config tool for developers who are tired of self-signed certificate warnings.
- Who is it for?
- Adopt mkcert if you are a developer who needs locally trusted certificates for localhost, custom domains, or internal services, and you want to avoid the pain of managing your own CA. Do not use it for production, and never share the rootCA-key.pem file.
- Can I use it commercially?
- Yes. BSD-3-Clause is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Probably not. The repository last received commits 27 months ago, on August 13, 2024.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
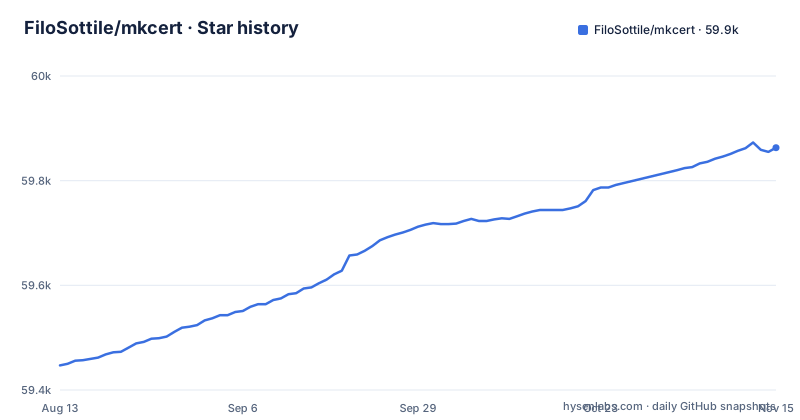
- FiloSottile/mkcert59,863 ★ · +416
| Repository | 2026-08-13 | 2026-11-15 |
|---|---|---|
| FiloSottile/mkcert | 59.4k | 59.9k |
416 Stars in the last 94 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The Problem: Self-Signed Certificates and the Trust Gap
Development servers often run on localhost or on made-up domains like example.test. Real certificate authorities cannot issue certificates for these names, and self-signed certificates trigger trust errors in every browser. The standard workaround is to run your own certificate authority, but that usually means reading man pages for openssl and remembering arcane flags. mkcert removes that friction. It is a single Go binary that creates a local CA, installs it into your system trust store, and then issues certificates for any names you pass on the command line. The intended user is a developer who wants HTTPS on a local machine without spending an afternoon on certificate plumbing. It is not for production, and the README is explicit about that: mkcert is meant for development purposes, not production.
How mkcert Works: A Local CA in Three Steps
The core mechanism is simple. Run mkcert -install and it generates a root CA certificate and a private key. The root CA is then installed into the system trust store, and on Linux and macOS it also installs into Firefox's trust store if certutil is available. After that, running mkcert with a list of names creates a certificate signed by that local CA. The certificate and key are written to files in the current directory, with names derived from the first domain, such as example.com+5.pem and example.com+5-key.pem. The output includes all the names you supplied, including wildcards and IP addresses. The key insight is that the local CA is trusted by the operating system, so any certificate it signs is automatically trusted by browsers and other applications that use the system store. The README shows that the whole flow takes two commands: one to install the CA, one to generate a certificate.
Getting Started: Commands and Configuration
Installation is straightforward on each platform. On macOS, brew install mkcert works, and you add brew install nss if you use Firefox. On Linux, you first install certutil via your package manager, then use Homebrew on Linux or download a pre-built binary. The README gives a curl command that fetches the latest Linux binary from dl.filippo.io. On Windows, Chocolatey or Scoop are the recommended routes. After installation, the two essential commands are mkcert -install and mkcert with your domain names. For example: mkcert example.com "*.example.com" example.test localhost 127.0.0.1 ::1. The tool also supports flags like -cert-file and -key-file to control output paths, -client for client authentication certificates, -ecdsa for ECDSA keys, and -pkcs12 for legacy applications. The -csr flag lets you supply a CSR, but it conflicts with all other flags except -install and -cert-file. The README notes that you must place options before the domain names list, which is a small gotcha.
Where mkcert Falls Short: Trust Store Coverage and Runtime Gaps
The biggest limitation is that mkcert only installs the CA into the stores it knows about. On Linux, the system store support depends on the presence of specific tools: update-ca-trust, update-ca-certificates, or trust. If your distribution uses something else, the CA may not be installed system-wide. Firefox support is only on macOS and Linux, and only if certutil is installed. Windows users have no Firefox integration at all. More importantly, many runtimes do not use the system trust store. Node.js is the prime example: the README explicitly says Node does not use the system root store, so you must set NODE_EXTRA_CA_CERTS to point at rootCA.pem. Java behaves differently, but mkcert does install into Java's trust store when JAVA_HOME is set. If you are writing a custom application that uses its own trust store, you will have to manually add the CA. Another limitation is that mkcert does not configure your server to use the certificates; you still have to point your web server or reverse proxy at the generated files.
Security Boundaries: The Root Key Is the Whole Game
The README carries a warning that rootCA-key.pem gives complete power to intercept secure requests from your machine. That is not hyperbole. Anyone who obtains that file can mint certificates for any domain, and because the CA is in your system trust store, those certificates will be accepted as valid. The tool makes this easy to forget because the CA files live in a folder printed by mkcert -CAROOT, and you rarely look at them. The README is clear: do not share the key. For mobile devices, you only need to install rootCA.pem, not the key, and the README explains that you can copy the certificate to another machine and run mkcert -install with CAROOT set to that directory. That is a safe way to trust the CA on a second machine, but it also means the CA key remains on the original machine, which is the correct boundary. If you lose control of the key, you must delete the CA from all trust stores and start over.
Alternatives: openssl and Full-Featured CA Tools
The obvious alternative is using openssl directly to create a self-signed certificate or a CA. The difference is that openssl gives you full control but requires you to generate a CA, sign certificates, and install the CA into the trust store yourself. That is exactly the arcane process mkcert automates. Another alternative is a tool like step-ca from Smallstep, which is a proper certificate authority with an API, ACME support, and more granular controls. step-ca is overkill for a single developer who just wants a localhost certificate, but it is the right choice if you need to manage certificates for a team or integrate with other systems. There is also certbot for Let's Encrypt, but that only works for public domains, not for localhost or example.test. Each alternative trades simplicity for flexibility. mkcert sits at the simple end of that spectrum, and it is hard to beat for a one-off certificate.
Maintenance and Upgrade Cost
mkcert is a small Go program with a single binary. The last release, v1.4.4, came out in April 2022, and the repository has been stable since then. That is not a sign of abandonment; the tool is feature-complete for its narrow purpose. The upgrade path is trivial: download a new binary and replace the old one. The license is BSD-3-Clause, which means you can use, modify, and distribute it freely, including in commercial products, as long as you retain the copyright notice. The main maintenance cost is not the tool itself but the trust store. Also, if you move to a new machine, you must either copy the CA files or generate a new CA and reinstall it. The README does not mention any automated migration path, so plan for that.
Editorial conclusion
Adopt mkcert if you are a developer who needs locally trusted certificates for localhost, custom domains, or internal services, and you want to avoid the pain of managing your own CA. Do not use it for production, and never share the rootCA-key.pem file. Before adopting, verify that your platform's trust store is supported (macOS, Windows, or Linux with update-ca-trust, update-ca-certificates, or trust), and check whether your browser or runtime uses a custom trust store like Node.js, which requires NODE_EXTRA_CA_CERTS. If you need certificates that are trusted by external parties, use a real CA or a tool like Let's Encrypt instead.
Frequently asked questions
What is mkcert used for?
mkcert is a zero-config tool for making locally-trusted development certificates with any names you want. It automatically creates and installs a local CA in the system root store and generates locally-trusted certificates, so hosts like localhost, 127.0.0.1, and example.test stop throwing trust errors.
Is MKCERT trustworthy?
The project warns that the automatically generated rootCA-key.pem gives complete power to intercept secure requests from your machine and must not be shared, and that mkcert is meant for development rather than production, so it should not be used on end users' machines. The shareable file is rootCA.pem, not the key.
Where does MKCERT put the certificate?
The CA certificate and its key are stored in an application data folder inside the user home, and the location is printed by mkcert -CAROOT. You can set the $CAROOT environment variable to manage separate CAs. Certificates you request are written as .pem files in the working directory, with the key in a matching -key.pem file.
how to install mkcert on ubuntu
On Linux you first install certutil, which on Ubuntu and Debian is the libnss3-tools package. After that you can install mkcert through Homebrew on Linux, build it from source with Go, or download a pre-built binary. Arch users can install it from the official Arch repository with sudo pacman -Syu mkcert.
how to use mkcert
Run mkcert -install once to create and install the local CA into the system and Firefox trust stores, then run mkcert followed by the names you want a certificate for. Flags such as -cert-file, -key-file, -ecdsa, and -pkcs12 must be placed before the domain names list.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/filosottile-mkcert)Star history chart for your README
[](https://hysenlabs.com/projects/filosottile-mkcert)Was this useful?