Firecracker: A Minimalist VMM for Serverless-Scale MicroVMs
Secure and fast microVMs for serverless computing.
At a glance
- What is it?
- Firecracker is a Rust-based virtual machine monitor that uses KVM to run lightweight microVMs. This review covers its architecture, startup flow, configuration API, and the trade-offs you accept when you choose it over a general-purpose VMM.
- Who is it for?
- Adopt Firecracker if you run container or function workloads that need stronger isolation than containers alone, and if you can accept a Linux-only, KVM-only environment with a deliberately narrow device model. Skip it if you need a general-purpose VM with broad device emulation, or if your team lacks the well-configured Linux host that the README says safe multi-tenant use depends on.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
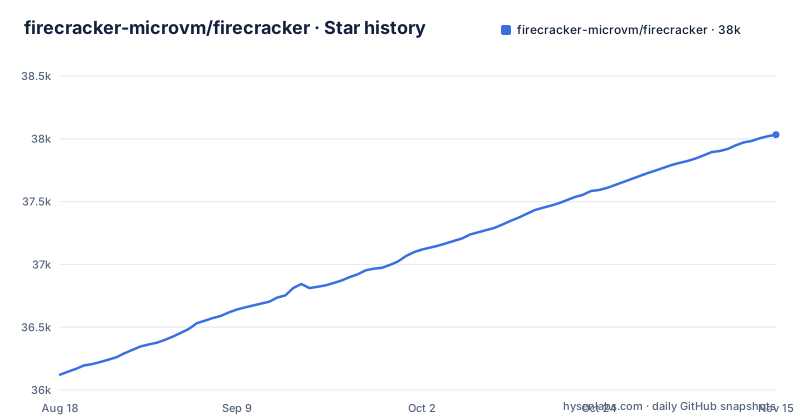
- firecracker-microvm/firecracker38,033 ★ · +1,911
| Repository | 2026-08-18 | 2026-11-15 |
|---|---|---|
| firecracker-microvm/firecracker | 36.1k | 38k |
1,911 Stars in the last 89 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The Problem Firecracker Solves
Firecracker targets a specific gap: running container and function workloads with the isolation of hardware virtualization but without the overhead of a full-featured VMM. The README describes its mission as enabling secure, multi-tenant, minimal-overhead execution of container and function workloads. It was built at AWS to accelerate Lambda and Fargate. For teams running serverless-style services on their own infrastructure, Firecracker offers a way to get VM-level security boundaries without paying for a heavy device emulation stack. The intended user is an infrastructure engineer who wants to run untrusted or multi-tenant workloads and is willing to trade device flexibility for a smaller attack surface and faster startup.
How Firecracker Works: A Single Process with a Narrow Device Model
Firecracker is a single VMM process that uses KVM to create and run microVMs. The design is minimalist: it excludes unnecessary devices and guest-facing functionality. The README lists the devices it does support: virtio network, file-backed block devices, vsock, entropy, and pmem. The guest sees a minimal hardware profile, which reduces the memory footprint and the attack surface. The VMM exposes an API endpoint to the host once started, and that API is specified in OpenAPI format. You configure the microVM through this API: set vCPUs, memory, CPU templates, add network interfaces, disks, rate limiters, and then start the microVM with a kernel image, root filesystem, and boot arguments. The API is the control plane; the process is the data plane. Demand fault paging and CPU oversubscription are enabled by default, which means you can overcommit memory and vCPUs..
Getting It Running: Build, Jailer, and the API Flow
The README gives a build path using a development container. You clone the repository, run `tools/devtool build`, and the binary lands at `build/cargo_target/${toolchain}/debug/firecracker`, where `toolchain` is set to `$(uname -m)-unknown-linux-musl`. For production, the README points to the Jailer process, which applies a cgroup and namespace isolation barrier and then drops privileges. The API is how you drive the VMM: you start the process, it exposes an API endpoint, and you send requests to set the vCPU count, memory size, and boot configuration. The README does not include a full quickstart example beyond the build steps, so you would need to consult `docs/getting-started.md` for the exact API calls. What is clear is that Firecracker is not a turnkey hypervisor; you must script the API interactions yourself or use an integration layer like Kata Containers or Flintlock, both mentioned in the README.
The Security Story: Seccomp, Jailer, and a Host Dependency
Firecracker's security model rests on three pillars: advanced thread-specific seccomp filters, the Jailer, and a well-configured host. The README states that the overall security of microVMs depends on a well-configured Linux host, and it points to a production host setup document. This is a candid admission: Firecracker does not isolate you from a misconfigured host. The Jailer applies cgroup and namespace isolation, then drops privileges, which is a standard defense-in-depth pattern. The seccomp filters are thread-specific, meaning each VMM thread gets its own filter, which narrows the syscall surface. But the README also lists tested platforms, and they are all specific metal instances with specific kernels: m5n.metal, m6i.metal, m7i, m8i, m6a, m7a, m6g, m7g, with host OSes like al2 and al2023. If you are not on one of those combinations, you are on your own. The security bar is high, but it is conditional on the host.
Limitations and Wrong-Tool Cases
Firecracker is the wrong tool if you need a VM that behaves like a physical machine with a variety of devices. The minimalist design means no legacy device emulation, and no hotplugging of arbitrary PCI devices (hotplug of virtio devices is only a Developer Preview, and stopping the microVM is x86_64 only). The README lists memory hotplugging as a feature, but device hotplug is marked as Developer Preview, so you should not rely on it in production. Another limitation is the Linux-only, KVM-only dependency. Firecracker cannot run on Windows or macOS hosts. Finally, the tested platform matrix is narrow: if you run on a different CPU generation or kernel, you are outside the tested set, and the README does not promise anything.
Alternatives and How They Differ
The obvious alternative is QEMU, which is a general-purpose VMM that also uses KVM. QEMU offers a much wider device model, including VGA, USB, and various network adapters, and it supports live migration and snapshots. The trade-off is that QEMU's larger codebase and device emulation increase the attack surface and memory footprint. Firecracker's README explicitly says it excludes unnecessary devices to reduce attack surface and startup time. Another alternative is Kata Containers, which is mentioned in the README as an integration. Kata wraps a VMM (it can use Firecracker or QEMU) behind a container runtime interface, so you get the container workflow with VM isolation. The difference in approach: Firecracker gives you a raw VMM and an API, while Kata gives you a container runtime that happens to use a VMM. If you want to run containers without rewriting your orchestration, Kata is the higher-level choice; if you want to build a custom serverless platform, Firecracker's API gives you finer control.
Maintenance, Upgrades, and License
Firecracker is released every two or three months, according to the README, with a release policy documented in `docs/RELEASE_POLICY.md`. The recent releases (v1.17.0, v1.16.2, v1.16.1) show a steady cadence. The project is under active development, with the last push on 2 November 2026, and it is not archived. The license is Apache-2.0, which is permissive for commercial use, but you should read the license text for your own legal review. The maintenance cost is not zero: because the security guarantees depend on the host, you must track kernel updates and re-evaluate your host configuration as Firecracker releases change. The changelog (CHANGELOG.md) and the release policy are the places to look for breaking changes, so test upgrades against your API scripts.
Editorial conclusion
Adopt Firecracker if you run container or function workloads that need stronger isolation than containers alone, and if you can accept a Linux-only, KVM-only environment with a deliberately narrow device model. Skip it if you need a general-purpose VM with broad device emulation, or if your team lacks the well-configured Linux host that the README says safe multi-tenant use depends on. Before deploying, verify that your host kernel and CPU are among the tested combinations listed in the README, and read the production host setup document to see the host configuration the project believes meets its security bar. Firecracker is not a hypervisor you install and forget; it is a component you integrate, and its security guarantees depend on the host you place it on.
Frequently asked questions
How do I install Firecracker?
Two routes are documented: download the latest release binaries from the GitHub releases page, or build from source on any Unix/Linux system that has Docker running and bash installed. The source build is git clone, tools/devtool build, then setting the toolchain variable from uname -m, and the binary lands under build/cargo_target in a debug directory.
How do I set up Firecracker for real workloads?
Building the VMM is only half of it. The project states that the security of microVMs depends on a well configured Linux host and points to its production host setup document for a configuration it believes meets the bar, then sends you to the quickstart guide for the boot sequence.
How do I use the Firecracker VM once it is built?
Firecracker runs as a single virtual machine monitor process that exposes an API endpoint to the host, specified in OpenAPI format. You set the vCPU count (default 1) and memory size (default 128 MiB), attach disks and network interfaces, then start the microVM with a kernel image, root file system and boot arguments. Stopping the microVM is marked x86_64 only.
What is Firecracker?
An open source virtualization technology written at Amazon Web Services to run container and function workloads in microVMs, with a minimalist design that excludes unnecessary devices and guest-facing functionality. It was built to accelerate services like AWS Lambda and AWS Fargate and is released under the Apache version 2.0 licence.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/firecracker-microvm-firecracker)Star history chart for your README
[](https://hysenlabs.com/projects/firecracker-microvm-firecracker)Was this useful?