Flox: Nix Reproducibility Behind a Manifest and a Lockfile
The Deterministic Foundation for your SDLC
At a glance
- What is it?
- Flox wraps Nix in a declarative manifest and a lockfile so a team can share one environment definition from laptop to CI. It is a strong fit for platform and AppSec groups standardizing toolchains, and a poor fit for anyone who wants a package manager without the Nix store underneath.
- Who is it for?
- Adopt Flox if your problem is toolchain drift across many machines and you are willing to run the Nix store underneath: the README's target users are platform and DevX teams, security and AppSec teams, and AI coding agents that need the same environment on every run. Do not adopt it if you need a single-machine package manager, or if GPL-2.0 obligations are a blocker for how you redistribute the CLI.
- Can I use it commercially?
- Yes, with conditions. GPL-2.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
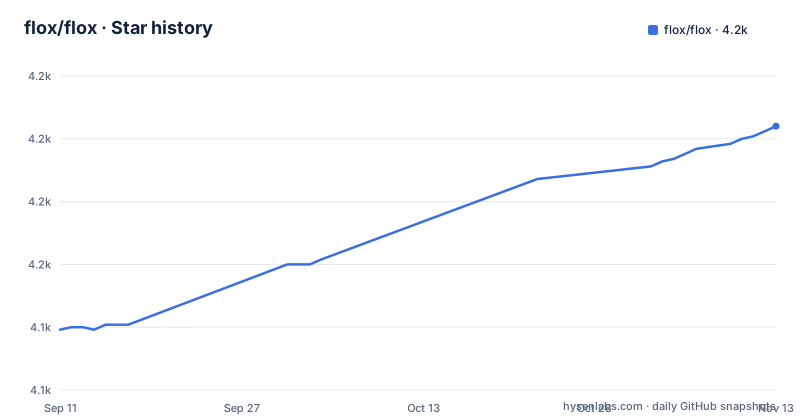
- flox/flox4,205 ★ · +81
| Repository | 2026-09-11 | 2026-11-13 |
|---|---|---|
| flox/flox | 4.1k | 4.2k |
81 Stars in the last 63 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The drift problem Flox is aimed at, and who feels it
The README frames the problem as environment drift: the state where a developer's laptop, a CI runner, and production have quietly diverged in tool versions. Flox's answer is to make the environment a checked-in artifact rather than a sequence of setup steps. The README describes environments as "cryptographically pinned" and "locked to cryptographically pinned, content-hashed inputs," with the claim that "the same lockfile resolves to the same packages on every supported system." That is the whole pitch in one sentence, and it is a narrower claim than "reproducible builds" in the general sense. Flox is not promising bit-identical compiled output; it is promising that the same lockfile selects the same package set. The distinction matters when you evaluate it.
The README names four audiences. Platform and DevX teams standardizing toolchains and shortening onboarding; security and AppSec teams that need SBOMs, CVE remediation, and dependency provenance; individual developers who want a per-project environment on macOS, Linux, or Windows under WSL2; and AI coding agents that need a deterministic environment to run generated code. The fourth one is unusual to see in a package manager README and reflects the linked flox-skills repository. If you are not in one of those four groups, the value proposition is weaker. The README does also list individual developers who want one reproducible, per-project environment for any stack.
Manifest, lockfile, and the Nix store underneath
The mechanism is a two-file split. One manifest describes "every tool, environment variable, and service your project needs," per the README's declarative bullet. A lockfile pins the resolved inputs. Environments are described as composable, meaning you can layer a project environment on top of a team environment on top of a pipeline environment. That layering is the part that distinguishes Flox from a per-project dotfile.
Underneath, this is Nix. The README says Flox is "Built on Nix, with Nix knowledge optional" and pulls from Nixpkgs, which it describes as having 120,000+ packages. So the data flow is: you write a manifest, Flox resolves it against Nixpkgs, produces a lockfile, and materializes the environment from the Nix store. The README also states that Flox can build custom software from source into reproducible packages and publish them for a team alongside Nixpkgs content. That means the store is not just a cache of upstream packages; it is also where your own builds land.
The README compares the runtime model to a virtual environment rather than a container or VM, "with nothing to spin up before you code." That is a meaningful design choice. It means Flox environments share the host kernel and filesystem rather than isolating them, so a Flox environment is a toolchain boundary, not a security sandbox. If you were hoping for container-grade isolation between two environments on the same machine, the README does not claim that.
Installing the CLI: what the README actually gives you
The install section is short and platform-specific. On macOS, the README lists `brew install flox` or a `.pkg` installer. On Linux, it lists `.deb` packages for Debian and Ubuntu and `.rpm` packages for Fedora and RHEL. On Windows, it says to use WSL2 and the Linux packages. The README points to a separate installation guide for the details rather than reproducing them.
The README's Quick Start shows the basic workflow: flox init creates an environment in your project, flox install python3 nodejs adds packages, flox activate enters the environment, and exit leaves it. The environment creation and CI tutorials are linked out to flox.dev rather than shown inline. That is a documentation-distribution choice, not a defect, but it means the README functions as a landing page. If you are evaluating Flox, the README is not sufficient; you need the linked tutorials before you can judge whether the manifest format fits your stack.
The one thing the README does commit to is the supported platform matrix: macOS, Linux, and Windows via WSL2. That is a concrete constraint you can plan against.
Where Flox is the wrong tool
The most obvious limitation follows from the Nix foundation. Flox hides Nix's interface, but it does not remove Nix from the machine. The README says Nix knowledge is optional, which is a statement about the user-facing surface, not about the dependency graph. When a package is missing from Nixpkgs, or when a package's build fails inside the Nix sandbox, the failure surfaces in Nix terms. For a tool that is not in Nixpkgs, the README points to building custom software from source into reproducible packages and publishing them for your team.
Second, the README's reproducibility claim is scoped to package resolution, not to arbitrary build output. If your team's actual pain is non-deterministic compilers, timestamps embedded in artifacts, or network access during builds, Flox addresses the input side of that problem and not the output side. Reading "reproducible" as a guarantee about your binaries would be a misreading of the README.
Third, the README positions Flox as organizational infrastructure, not a personal tool. It says Flox "manages the lifecycle of packages and environments across your entire organization" where traditional package managers work on a single machine. That framing implies a shared manifest, review process, and probably a publishing step for internal packages. A single developer who just wants `ripgrep` and `node` on one laptop is paying the coordination cost of a system designed for many machines, although the README also lists individual developers who want a per-project environment.
Nix, devenv, and what Flox changes
The honest comparison is with Nix itself, and with the tools built on it. Plain Nix gives you the same store, the same pinning, and the same Nixpkgs package set. Flox's difference is the interface: a manifest instead of the Nix expression language, and a lockfile instead of a `flake.lock` you manage by hand. The README's own framing is "All the power of Nix, none of the learning curve," which is a claim about the authoring layer, not the resolution layer. If you already have engineers fluent in Nix flakes, Flox adds an abstraction over something they can already write directly, and you should ask what the abstraction buys you beyond a friendlier diff in code review.
Against container-based approaches, the difference is sharper. A container image pins the whole userland and gives you isolation; a Flox environment pins the toolchain and shares the host. The README explicitly places Flox closer to a virtual environment than to a container or VM. That means faster activation and no image build step, but also no isolation boundary. Teams that adopted containers partly for security separation will not get that property here, even though the README lists security and AppSec teams as a target audience. The security value Flox claims is supply chain provenance (SBOMs, provenance, CVE remediation), which is a different thing from runtime isolation. Do not conflate them.
Nix without Flox remains a legitimate choice for teams that want the store and are comfortable with the expression language. The trade is authoring ergonomics against one more layer to debug.
Release cadence, licensing, and what maintenance looks like
The release history shows a steady cadence: v1.19.3 on 2026-10-28, v1.19.2 on 2026-10-27 and v1.19.1 on 2026-10-22, with frequent patch releases. That rhythm tells you the CLI is under active development, and it also tells you that pinning a CLI version for a large team is worth doing, because a manifest that resolves cleanly under one release may behave differently under the next. Whether the manifest format stays compatible across minor versions is something to establish for yourself rather than assume.
Licensing is GPL-2.0, per the repository metadata and the license badge in the README. GPL-2.0 is a copyleft license. For most teams using the CLI internally to build and run environments, that is unremarkable. It becomes a question when you redistribute the binary, bundle it into a product, or modify it, because copyleft obligations attach to distribution. This is not legal advice and the specifics depend on what you ship. If your organization has a policy against GPL-2.0 tooling in distributed artifacts, that policy applies here and you should route it through whoever owns it before standardizing on Flox. Note also that the license covers the Flox CLI; the packages Flox pulls from Nixpkgs carry their own licenses.
The maintenance cost that the README does not quantify is the lockfile update loop. Pinned inputs are the point, and pinned inputs go stale. Someone has to bump them, and the README's security framing ("fast CVE remediation") implies that this is a routine activity rather than an occasional one. Budget for it as recurring work.
Who should adopt Flox, and what to check first
Flox fits organizations where the same toolchain has to exist on many machines and the current answer is a wiki page of install instructions. The README's platform and DevX framing is the strongest signal: standardizing toolchains, cutting onboarding time, and letting teams extend a base environment without each person learning Nix. The AppSec angle is real but narrower than it sounds, since the supply chain benefits (SBOMs, provenance, CVE patching) come from reproducibility rather than from anything Flox adds on top of it.
Flox does not fit a solo developer on one machine, a team that needs runtime isolation between environments, or anyone whose stack depends on software that is not in Nixpkgs and not buildable from source with the build-and-publish feature the README describes. It also does not fit an organization that has ruled out GPL-2.0 dependencies in distributed artifacts, unless the CLI is used strictly internally and that has been confirmed.
Three things to verify before you commit. First, whether your actual dependency list is covered by Nixpkgs, since that determines how often you fall through to the Nix layer. Second, whether the lockfile resolves identically across every OS in your matrix, which for most teams means macOS plus Linux plus WSL2. Third, what a manifest change looks like in a pull request, because that diff becomes part of your build definition and your review process has to absorb it. The README links to a CI/CD tutorial and a five-minute getting-started guide; read both before deciding, since neither is reproduced in the repository itself.
Editorial conclusion
Adopt Flox if your problem is toolchain drift across many machines and you are willing to run the Nix store underneath: the README's target users are platform and DevX teams, security and AppSec teams, and AI coding agents that need the same environment on every run. Do not adopt it if you need a single-machine package manager, or if GPL-2.0 obligations are a blocker for how you redistribute the CLI. Before committing, verify three things yourself: that the packages your stack actually needs are present in the Nixpkgs set Flox resolves against, that the lockfile resolves identically on every OS you support (the README names macOS, Linux, and Windows via WSL2), and how your team will review manifest and lockfile changes in pull requests, since that diff is now part of your build definition.
Frequently asked questions
What is Flox?
A software environment platform for engineering teams, built on Nix, that delivers cryptographically pinned reproducible environments identical from a developer's laptop through CI to production. One declarative manifest describes every tool, environment variable and service a project needs.
How do I install Flox?
The CLI installs natively on macOS, Linux and Windows via WSL2. On macOS use brew install flox or the .pkg installer, on Linux the .deb package for Debian and Ubuntu or the .rpm for Fedora and RHEL, and on Windows use the Linux packages under WSL2.
Do I need to learn Nix to use Flox?
The readme says Nix knowledge is optional and describes the project as all the power of Nix with none of the learning curve. It also frames the result as more like a virtual environment than a container or VM, with nothing to spin up before you code.
Which packages can Flox install?
120,000 or more packages pulled from Nixpkgs, which it calls the largest open source package repository and which is updated continuously. You can also build your own software from source into reproducible packages and publish them for the team alongside everything from Nixpkgs.
What does Flox give security and AppSec teams?
SBOMs, fast CVE remediation, dependency provenance and reproducible builds, with software composition analysis and clean auditable builds described as falling out of reproducibility. The same environment definition is used on a laptop, in an AI agent's sandbox, through CI and in production.
How do I create and enter a Flox environment?
Run flox init to create an environment in your project, flox install with the packages you want such as python3 or nodejs, then flox activate to enter it. Leaving with exit returns you to the machine's own tools, since nothing is installed globally.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/flox-flox)Star history chart for your README
[](https://hysenlabs.com/projects/flox-flox)Was this useful?