Bramble: a local-first password manager that syncs over a private P2P mesh
Local-first, encrypted password manager with private P2P mesh. Passkeys. Create and sign in with passkeys, stored as ordinary vault entries so they sync between your devices with everything else.
At a glance
- What is it?
- Bramble stores your vault on your own devices and syncs it directly between them, with no server in the middle. The trade-off is that you are responsible for backups and for keeping at least one device online.
- Who is it for?
- Adopt Bramble if you want a password manager with no account, no cloud vault, and direct device-to-device sync, and you are willing to manage your own backups and keep a device online as a sync hub. Do not adopt it if you expect zero-maintenance sync across devices that are rarely awake at the same time, or if you need a hosted recovery path.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
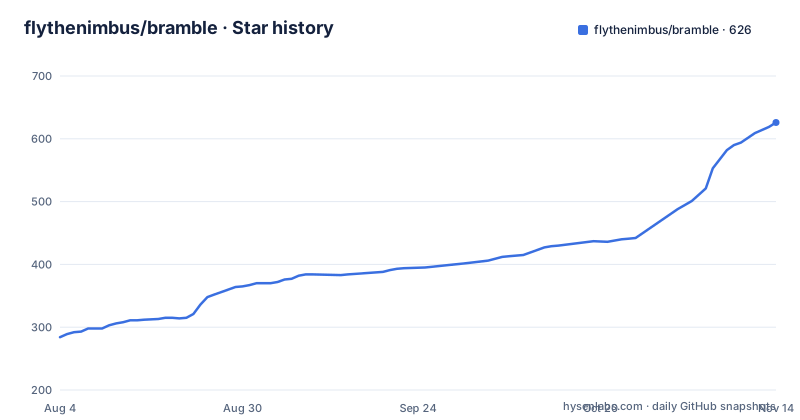
- flythenimbus/bramble626 ★ · +342
| Repository | 2026-08-04 | 2026-11-14 |
|---|---|---|
| flythenimbus/bramble | 284 | 626 |
342 Stars in the last 102 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What Bramble solves and who it is for
Bramble targets people who do not want a password manager that holds their vault on a company server. The README is explicit: no account, no server holding your vault, no company to get breached and leak everything. Instead, the vault lives in browser extension storage, in files on your desktop disk, or in app-private encrypted storage on mobile. The intended user is someone who already trusts their own devices more than a cloud provider, and who is comfortable with the operational burden that comes with that choice. It is for individuals or small groups who can keep at least one device online, because the sync model depends on devices being awake at the same time. It is not for someone who wants a zero-maintenance password manager where a third party handles availability and recovery.
The architecture: one Rust core, four frontends
The cryptographic work happens in a single Rust core. In the browser it is compiled to WebAssembly; on iOS and Android it becomes a native library. Key derivation, encryption, and decryption all run in that core, and derived keys are wiped from memory after use. The desktop app is built with Tauri, so the UI is React but the vault and crypto operations live in a Rust process. The README stresses that the Vault Key never enters the webview at all. That separation is a real design choice: the UI layer cannot directly touch key material, which reduces the attack surface compared to a typical Electron app where the renderer has full access to the main process. The same vault format and crypto core are shared across all four clients, which means a vault created on one platform should be readable on another. The mobile apps are versioned and released independently of the extension, as seen in the recent releases list with separate Android and Chromium versions.
Sync and the always-on hub problem
Peer-to-peer sync is the core feature, but it has a constraint the README acknowledges directly: it wants two devices awake at the same moment, and two phones rarely are. The desktop app is positioned as the always-on sync hub because a computer usually is left in the tray. That means the practical setup is to have a desktop or laptop running Bramble in the background, otherwise your phone might not sync when you open it. The README also describes pairing the desktop app with the browser extension so the panel can fill pages over an encrypted channel that never leaves your machine. Pairing is additive: the extension remains standalone and does not need the app installed. This design is workable, but it shifts a chunk of the reliability burden onto the user. If your desktop is off for a week, your phone's vault is effectively frozen until that machine comes back. That is a genuine limitation, not a hypothetical one.
Getting it running: commands and config keys
There is no single install command because Bramble is distributed through app stores and release pages. The README lists the Chromium extension on the Chrome Web Store, a Firefox add-on, a desktop app for macOS and Linux from bramble.sh, an Android app from the GitHub Releases page, and an iOS app on the App Store. For the browser extension, you install it and you are up and running in a minute, according to the README. The desktop app gives you a global quick-access panel with Cmd+Shift+Space (Ctrl+Shift+Space off macOS). For backups, you configure destinations from Settings. The README names Dropbox (one-click sign-in, extension only for now), any S3-compatible bucket (Backblaze B2, Cloudflare R2, Storj, Wasabi, MinIO), and self-hosted WebDAV (Nextcloud, ownCloud, Fastmail). Each destination gets its own cadence: daily, weekly, or monthly. You can also press Back up now. The backup file format is an encrypted .bramble file. There are no config files or CLI flags mentioned, so configuration is entirely through the GUI.
Backups: the price of local-first
Because nobody else holds a copy of your vault, backup is your job. Bramble gives three layers. Explicit export writes an encrypted .bramble file that you store anywhere; it stays ciphertext and needs your master password to open. Implicit backup comes from sync: every paired device holds a full copy of the vault, so losing one device does not lose the data. Automatic scheduled backups go to Dropbox, S3-compatible storage, or WebDAV, with pruning of old snapshots. The desktop app can run these backups while the vault is locked, because it sits in the tray. The README warns that a stolen backup is useless without the master password, which is a fair claim, but it also means that losing the master password with no recovery code is catastrophic. The README mentions a recovery code as a fallback for biometric unlock, but it does not explain how to recover a vault if you forget both the master password and the recovery code. That is a gap worth verifying before you trust real credentials to it.
Passkeys as ordinary vault entries: a design trade-off
Bramble stores passkeys as ordinary vault entries, which means they sync between devices like any other login. That is convenient, but it also means passkeys are not protected by the platform's dedicated passkey hardware on every device. The README says passkeys are stored as ordinary vault entries so they sync with everything else. On mobile, biometric unlock is gated by the OS keystore, but the passkey itself lives inside the encrypted vault, not in the OS's dedicated passkey storage. That is a meaningful difference from iCloud Keychain or Google Password Manager, where passkeys are tied to the platform's secure enclave. The trade-off is portability and sync simplicity versus platform-level hardware attestation. If you need passkeys that are non-exportable and bound to a specific device's secure element, Bramble is not that. If you want passkeys that work across your own devices without a cloud provider, the vault-entry approach is coherent.
Limitations and when it is the wrong tool
The most obvious limitation is sync availability. If no device is online, there is no sync, period. The README's own framing of the desktop app as an always-on hub admits that. A second limitation is platform coverage: there is no Windows desktop app mentioned, only macOS and Linux. The browser extension is Chromium-only for the latest release (1.22.0-chromium), though a Firefox add-on exists. The mobile apps are versioned independently, which means feature parity is not guaranteed at any given moment. Another limitation is that the README is truncated, so details on the Android and iOS feature sets beyond autofill, biometrics, and passkeys are incomplete. If you need a password manager that works on Windows, or if you cannot keep a desktop machine running, Bramble is the wrong tool. Also, if you are uncomfortable managing your own backups, the explicit export and scheduled cloud backup features are there, but they require you to configure and monitor them yourself.
Alternative: Bitwarden or a self-hosted vaultwarden
The closest alternative in approach is Bitwarden, which offers a hosted cloud vault but also allows self-hosting with the open-source server. The key difference is that Bitwarden's sync is client-server: your devices sync through a central server, whether Bitwarden's or your own. That server can be online 24/7, so your phone can sync even when your desktop is off. Bramble's sync is peer-to-peer, with no server at all, which removes the central point of failure but introduces the online-device requirement. If you run vaultwarden, a community implementation of the Bitwarden server, you get the same self-hosted control but with a persistent sync point. The trade-off is that you have to run and maintain a server, whereas Bramble asks you only to run a client. For someone who already runs a home server, vaultwarden might be more reliable for sync. For someone who wants no server at all, Bramble is the only option in this comparison.
Maintenance, licensing, and upgrade cost
The project is under active development, with recent releases in August 2026 for Chromium, Android, and desktop. The repository is not archived. The license is GPL-3.0, which means if you distribute a modified version, you must release your changes under the same license. That is fine for personal use, but it is a real constraint for a company that wants to embed Bramble's code in a proprietary product. The maintenance cost for a user is mostly operational: you must keep backups, monitor sync, and update clients across four platforms. The desktop app is the one that can run scheduled backups while locked, so you need to keep it installed and running. The README does not mention automatic updates, so you likely need to check for new releases manually or rely on store mechanisms for the extension and mobile apps. There is no migration tool mentioned from other password managers, only import from Settings, so moving from an existing manager may require manual CSV export and import.
Editorial conclusion
Adopt Bramble if you want a password manager with no account, no cloud vault, and direct device-to-device sync, and you are willing to manage your own backups and keep a device online as a sync hub. Do not adopt it if you expect zero-maintenance sync across devices that are rarely awake at the same time, or if you need a hosted recovery path. Before committing, verify that the peer-to-peer sync works reliably on your specific mix of devices, test the export and restore flow on a spare vault, and confirm that the scheduled cloud backup destinations (Dropbox, S3-compatible, WebDAV) meet your storage requirements. The project is GPL-3.0, so check whether that license fits your use case if you plan to modify or embed the code.
Frequently asked questions
How does bramble sync between devices without a server?
Devices sync directly peer to peer, end to end encrypted, with no cloud in between and no relay holding data. Because peer-to-peer needs two devices awake at once, the desktop app has an always-on sync hub in the tray that your other devices can sync with.
How do passkeys work in bramble?
Passkeys are created and signed in with like any other credential, and stored as ordinary vault entries. That is why they sync between your devices along with everything else, with no separate credential store to reconcile.
What backup options does bramble offer?
Three: exporting an encrypted .bramble file by hand, relying on peer-to-peer sync so every paired device holds a live copy, and scheduled automatic backups to Dropbox, any S3-compatible bucket, or your own WebDAV server on daily, weekly or monthly cadences. Only ciphertext is ever uploaded.
Why does an unsigned bramble desktop build misbehave on macOS?
macOS binds a keychain item's access control to the code signature of the binary reading it, so an unsigned build prompts for the login password on every launch and browser pairing looks broken. The signing identity has to be set at build time.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/flythenimbus-bramble)Star history chart for your README
[](https://hysenlabs.com/projects/flythenimbus-bramble)Was this useful?