Dangerzone: Converting Untrusted Documents into Safe PDFs
Take potentially dangerous PDFs, office documents, or images and convert them to safe PDFs
At a glance
- What is it?
- Dangerzone is a desktop application from Freedom of the Press Foundation that converts untrusted PDFs, office documents, and images into safe PDFs inside a sandbox. This article covers how it works, how to install it, and where its limits lie.
- Who is it for?
- Dangerzone is for journalists, researchers, and anyone who regularly receives documents from untrusted sources and wants a sandboxed conversion step before opening them. It is not for people who need to edit documents or preserve exact formatting.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 7 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
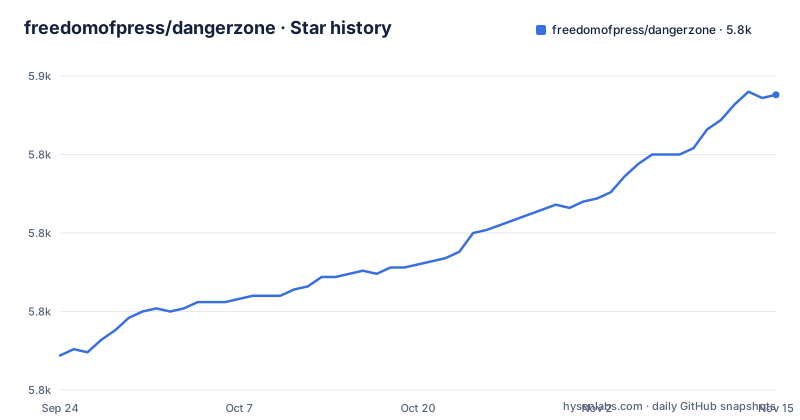
- freedomofpress/dangerzone5,844 ★ · +83
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| freedomofpress/dangerzone | 5.8k | 5.8k |
83 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What Dangerzone Solves and Who It Is For
Dangerzone addresses a specific problem: you receive a document from a source you do not fully trust, and opening it in a normal PDF viewer or office suite means running whatever code or exploit it contains. The README describes the use case directly: you give it a document you do not know if you can trust, such as an email attachment. The project is built for that scenario, not for general document management.
The intended audience is visible in the project's origin. It is maintained by Freedom of the Press Foundation, an organization that supports journalists.
It is not a document editor, a viewer, or a file manager. It takes a file and produces a new PDF. That narrow scope is deliberate.
How the Sandbox Conversion Works
The README describes the mechanism in plain terms. Inside a sandbox, Dangerzone converts the document to a PDF if it is not already one, then converts that PDF into raw pixel data: a huge list of RGB color values for each page. Then, outside the sandbox, Dangerzone takes this pixel data and converts it back into a PDF. The output contains only rendered page images, not the original document structure, scripts, or embedded objects.
setup.py describes the sandbox: Dangerzone uses disposable VMs on Qubes OS, or container technology in other OSes, to convert the documents within a secure sandbox.
Installing Dangerzone and Converting Your First Document
Installation instructions live in the documentation at docs.dangerzone.rocks, which the README links for macOS, Windows, Ubuntu, Debian, Fedora, Qubes OS, and Tails. The README does not reproduce the commands inline.
For development or building from source, the repository uses Poetry. The Makefile defines a poetry-install target that runs:
make poetry-installThat target runs `poetry install`, which installs the dependencies listed in pyproject.toml, including PySide6, PyMuPDF, and click. The project requires Python >=3.10,<3.15 according to pyproject.toml.
The CLI entry point is defined in pyproject.toml as:
dangerzone-cli = "dangerzone.cli:run"So after installation, the `dangerzone-cli` command is available. The README does not give a full CLI usage example, so consult the project documentation for the exact flags. The GUI entry point is:
dangerzone = "dangerzone.gui.run:run"Running `dangerzone` launches the graphical application.
Limitations and Cases Where Dangerzone Is the Wrong Tool
Dangerzone converts documents to images wrapped in a PDF. That means the output is rebuilt from page pixel data rather than from the original text.
The conversion also discards document structure. Forms, links, bookmarks, and embedded files do not survive the pixel-data round trip. If your workflow depends on any of those, Dangerzone produces a less useful file.
Finally, Dangerzone is a desktop application. The README does not describe a server mode or a REST API, though pyproject.toml does define a dangerzone-cli command alongside the GUI.
How Dangerzone Differs from Qubes Trusted PDF
setup.py states that Dangerzone uses disposable VMs on Qubes OS, or container technology in other OSes, to convert the documents within a secure sandbox.
A VM boundary is stronger than a container boundary because it includes a separate kernel.
The trade-off is portability for isolation strength. Dangerzone runs on macOS, Windows, and several Linux distributions without requiring Qubes OS. If your threat model demands VM-level isolation, setup.py says Dangerzone itself uses disposable VMs on Qubes OS. If you need something that works on a standard laptop, Dangerzone is the practical choice.
Maintenance, Updates, and Licence
The repository is not archived, and the last push was on 2026-11-02. The most recent release listed is v0.11.1 from 2026-10-22, following v0.11.0 on 2026-07-02 and v0.10.0 in December 2025. That cadence suggests the project receives periodic releases rather than continuous updates.
Dangerzone is licensed under AGPL-3.0. The copyright lines in the README cover 2022 to 2024 for Freedom of the Press Foundation and contributors, and 2020 to 2021 for First Look Media. AGPL-3.0 is a copyleft licence with a network-use clause. If you modify Dangerzone and offer it as a network service, the licence likely requires you to publish your modifications. That is a summary of the licence text, not legal advice; consult a lawyer for your specific situation.
Editorial conclusion
Dangerzone is for journalists, researchers, and anyone who regularly receives documents from untrusted sources and wants a sandboxed conversion step before opening them. It is not for people who need to edit documents or preserve exact formatting. Before relying on it, verify that your platform is supported in the documentation at docs.dangerzone.rocks, and confirm whether your threat model requires the disposable VMs Dangerzone uses on Qubes OS rather than containers.
Frequently asked questions
How do I install Dangerzone?
The README points to the installation documentation at docs.dangerzone.rocks, which covers macOS, Windows, Ubuntu, Debian, Fedora, Qubes OS, and Tails. Follow the section for your platform.
Can Dangerzone run without an internet connection?
The README does not say; check the documentation at docs.dangerzone.rocks.
Does Dangerzone preserve the text in my documents?
The README says Dangerzone converts each page into raw pixel data and then converts that back into a PDF, so the safe PDF is rebuilt from page images rather than the original text.
Has Dangerzone been security audited?
The README does not mention a security audit; it links to the project's security policy in SECURITY.md.
Can I use a different Podman version with Dangerzone?
The README does not cover this; see the supported platforms page in the documentation at docs.dangerzone.rocks.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/freedomofpress-dangerzone)Star history chart for your README
[](https://hysenlabs.com/projects/freedomofpress-dangerzone)Was this useful?