Awesome Hacking: A Directory of Security Lists, Not a Toolbox
GitHub describes it as A collection of various awesome lists for hackers, pentesters and security researchers. The metadata lists the CC0-1.0 license. This article stays within the project description and details documented in the GitHub repository README.
At a glance
- What is it?
- Awesome Hacking is a meta-list that points to dozens of specialized security resource collections. It is a starting point for researchers, not a tool itself, and its value depends entirely on the health of the lists it links to.
- Who is it for?
- Adopt Awesome Hacking if you are a newcomer to security research or a pentester who needs a broad map of available resource collections. It is not for you if you expect tools, code, or executable content, because it contains only links.
- Can I use it commercially?
- Yes. CC0-1.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 20 days ago.
- What is it written in?
- GitHub does not report a main language for this repository.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
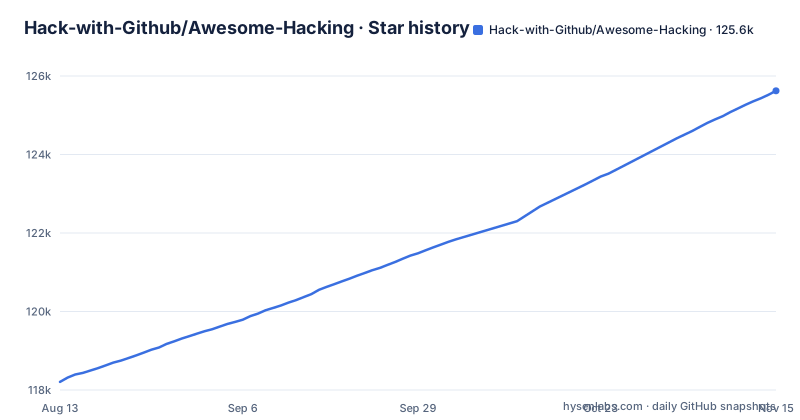
- Hack-with-Github/Awesome-Hacking125,622 ★ · +7,415
| Repository | 2026-08-13 | 2026-11-15 |
|---|---|---|
| Hack-with-Github/Awesome-Hacking | 118.2k | 125.6k |
7,415 Stars in the last 94 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What This Repository Actually Is
Awesome Hacking is a single README file that organizes links to other awesome lists. It does not contain tools, scripts, or original research. The description says it is a collection of awesome lists for hackers, pentesters and security researchers. The README presents a table with two columns: repository name and a one-line description. There are over 40 entries. The scope is broad, from Android Security to YARA, and includes niche areas like Drone Hacking and Mainframe Hacking. If you are looking for a specific tool like Nmap or Burp Suite, this is not the place. It is a directory of directories. The value is in the curation, not the content.
The Mechanism: A Table of Links, Nothing More
The repository has no code, no configuration, and no runtime. The README file is the entire product. Each row in the table points to an external GitHub repository that itself is an awesome list. For example, the Android Security row links to ashishb/android-security-awesome, and the Fuzzing row links to secfigo/Awesome-Fuzzing. The descriptions are one line each. There is no filtering, no ranking, and no quality scoring. The repository owner does not maintain the linked lists. That is a critical design choice. It means Awesome Hacking is only as useful as the sum of its upstream lists. If a linked list goes stale, the index still shows it as current.
How to Use It and How to Contribute
There are no installation steps. You open the README on GitHub. To contribute, the README says your contributions are always welcome and points to a contributing.md file. That file is not shown in the README, but it likely contains guidelines for adding new lists. The repository uses the default branch master. Since there are no releases, you cannot pin a version. You simply use the latest master. The license is CC0-1.0, which means the repository owner has waived all rights to the content. That is unusual for a curated list and it means you can copy the table and reuse it without attribution, though the linked lists themselves have their own licenses. For a security researcher, the practical use is as a bookmark file. You scan the table, pick a domain like OSINT or Malware Analysis, and click through.
Coverage Gaps and Blind Spots
The list is broad, covering many subfields. The descriptions are uneven. Some are specific, like the one for Asset Discovery, which mentions the asset discovery phase of a security assessment. Others are vague, like the one for Security, which says it is a collection of awesome software, libraries, documents, books, resources and cools stuffs about security. That entry is so broad it is almost useless. The list also mixes training resources, such as Cyber Security University, with tool collections, such as SecLists. A beginner might confuse the two. The visible table is a flat alphabetical list, so you may have to scan many rows to find what you need.
Maintenance and the Risk of Stale Links
The repository has no GitHub releases, but the last push was on 2026-10-27. Without a release history, the push date is the main signal of how active the maintenance is. The upstream lists vary in their own maintenance. The repository itself does not check for dead links. If a linked list is deleted or moved, the README will still show it. That is a genuine failure mode. For a researcher, a stale link wastes time. The CC0 license does not help with maintenance. It only affects copyright, not ongoing upkeep. You should check the last commit date of any linked list before relying on it.
Alternatives: Searching GitHub Directly or Using a Specialized Index
The obvious alternative is to search GitHub for awesome security lists yourself. A search for awesome security returns many repositories, but you have to filter through duplicates and low-quality lists. Another alternative is to use a specialized index like SecLists, which is a single repository with actual lists of payloads and wordlists, not a meta-list. SecLists gives you concrete content, not just links. The difference in approach is that Awesome Hacking points you to other lists, while SecLists is the end resource. For a pentester who needs a wordlist right now, SecLists is more direct. For a researcher who wants to survey the field, Awesome Hacking is a map. The choice depends on whether you need a directory or a destination.
Who Should Adopt It, and What to Verify First
Adopt Awesome Hacking if you are new to security and want a broad overview of available resource collections. It is also useful for a pentester who needs to quickly find a list for an unfamiliar domain, like cellular hacking or vehicle security. Do not adopt it if you need tools, code, or executable content. The repository provides none. Before you rely on any linked list, verify three things. First, check the last commit date on the upstream repository. Second, confirm the linked repository still exists. Third, read the description carefully, because some are too vague to be useful. The repository is CC0-1.0, so you can legally reuse its structure, but you should not assume the linked lists share that license. This is a starting point, not a destination. Its value degrades as its links go stale, so treat it as a living document that needs your own verification.
Editorial conclusion
Adopt Awesome Hacking if you are a newcomer to security research or a pentester who needs a broad map of available resource collections. It is not for you if you expect tools, code, or executable content, because it contains only links. Before relying on any linked list, verify its last commit date and whether its entries still point to live tools. The repository itself is CC0-1.0 licensed, so you can reuse its structure freely, but the linked lists carry their own licenses. Check the contributing.md file before adding entries, and recognize that the real maintenance burden sits on the upstream lists, not on this index.
Frequently asked questions
What is the Awesome-Hacking repository used for?
It is a directory of other people's curated security lists, presented as a two-column table of repository names and one-line descriptions, aimed at hackers, pentesters and security researchers. Topics run from CTF and asset discovery to static analysis, reversing, prompt injection and vehicle security.
Does Awesome-Hacking review or verify the tools it links?
The table rows make no such claim. Each row holds a name, a URL and a single description sentence, with no maintainer, update date or status, and the only process document is a contributing file that invites new entries.
Can I reuse the Awesome-Hacking list in my own project?
The LICENSE file at the root is CC0-1.0, a public domain dedication covering the content of this repository, so reuse carries no attribution condition. The linked repositories keep their own separate licenses, which the index does not change.
How many security lists are in the Awesome-Hacking table?
The table carries more than forty rows, from Android Security and AppSec through Web3 Security and YARA, and the document continues past those. Entries include both single-subject lists and meta-lists such as The Art of Hacking Series, described as holding thousands of references.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/hack-with-github-awesome-hacking)Star history chart for your README
[](https://hysenlabs.com/projects/hack-with-github-awesome-hacking)Was this useful?