HaGeZi DNS Blocklists block ads, trackers, and threats network-wide
DNS-Blocklists: For a better internet - keep the internet clean!
At a glance
- What is it?
- HaGeZi DNS Blocklists is a GPL-3.0 set of DNS blocklists that blocks ads, trackers, telemetry, phishing, malware, and scams network-wide, organized into five Multi tiers plus specialized standalone lists.
- Who is it for?
- HaGeZi DNS Blocklists is a GPL-3.0, network-wide blocking project that organizes its coverage into five cumulative Multi tiers, a large Threat Intelligence Feeds add-on, and a wide set of specialized standalone lists for scams, pop-ups, new domains, rebind protection, NSFW content, and more. The repository ships the lists in several format directories, including adblock, dnsmasq, rpz and wildcard, so users pick the format that matches their tool.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Text, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
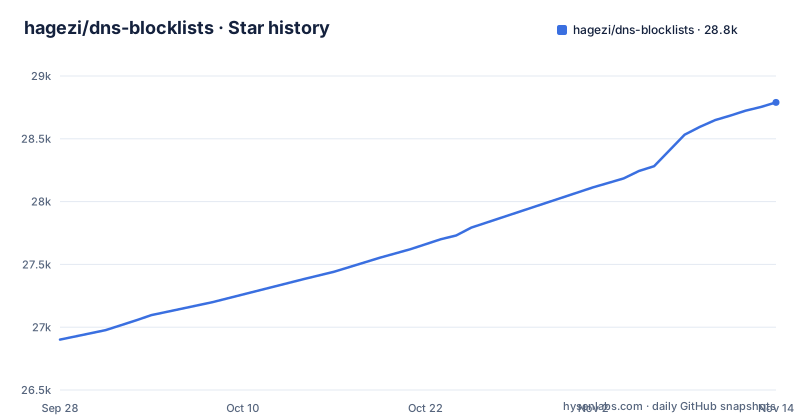
- hagezi/dns-blocklists28,753 ★ · +1,852
| Repository | 2026-09-28 | 2026-11-13 |
|---|---|---|
| hagezi/dns-blocklists | 26.9k | 28.8k |
1,852 Stars in the last 46 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
A network-wide set of DNS blocklists
HaGeZi DNS Blocklists is a set of DNS blocklists that block ads, trackers, telemetry, phishing, malware, scams, and other unwanted domains network-wide. The project is licensed under GPL-3.0 and states that the lists work for any region and with every common DNS server, ad blocker, and content blocker. The README frames the goal as making the internet a cleaner, safer place, and it notes the lists are built from various source blocklists that have been optimized and extended rather than simply concatenated.
The lists are designed to run standalone or alongside each other, and the documentation repeatedly emphasizes that a user should pick the tier and format that match their tool and risk tolerance. New users are pointed at Multi PRO plus the Threat Intelligence Feeds list as a starting combination, with a quick setup guide and a direct link generator offered to remove manual steps.
The five Multi tiers build on each other
The all-in-one Multi list ships in five versions named after cleaning tools: Light is the hand brush for basic protection, Normal is the broom for all-round protection, Pro is the big broom for extended protection and is recommended, Pro++ is the sweeper for advanced and more aggressive protection, and Ultimate is the ultimate sweeper for maximum and most aggressive protection. The documentation explains that the bigger the tool, the more thoroughly it cleans, and the more likely it is to sweep up something the user wanted to keep.
The first five tiers build on each other, so the guidance is to pick exactly one of them. The README's at-a-glance table lists entry counts that grow from Light at 79,665 entries through Normal at 176,107, Pro at 211,778, Pro++ at 257,464, and Ultimate at 283,026, with size-optimized mini versions available for the larger tiers. Each step up also raises the stated risk of breakage, from minimal on Light to high on Ultimate.
Standard formats and how to pick one
The README links a "Which format do I need?" guide from its overview, and the repository ships the lists in separate adblock/, adguard/, dnsmasq/, rpz/ and wildcard/ directories, so the first step is to pick the format that matches your tool.
Threat Intelligence Feeds as an add-on layer
The Threat Intelligence Feeds list, abbreviated TIF, is described as a serious security boost and is marked in the README table as blocking threats only, with low breakage risk. Unlike the five Multi tiers, TIF is meant to run alongside a tier: the README's suggested start is Multi PRO plus TIF.
TIF is the largest list by a wide margin, with 1,879,829 entries in its full form, and Medium and Mini versions exist at 311,171 and 191,527 entries, plus an IPs version.
Specialized standalone lists beyond the Multi tiers
Beyond the Multi tiers and TIF, the project maintains a long catalog of focused standalone lists. These include Fake for scams, traps and fake sites, Pop-Up Ads for annoying and malicious pop-ups, Newly Registered Domains for disposable attacker domains, Dynamic DNS abuse protection, Badware Hoster, Most Abused TLDs, and DNS Rebind Protection.
Further standalone categories cover DoH, VPN, Tor, and Proxy bypass prevention, search engines that skip Safesearch, URL shorteners, anti-piracy, gambling, social networks, NSFW or adult content, and native trackers built into devices, apps, and operating systems. The documentation also offers a Direct Link Generator that builds download links with a few clicks, plus a Blocklist Lookup to check any domain or IP against every list.
Entry counts and the trade-off of aggression
The central trade-off is spelled out in the cleaning-tools note: more aggressive tiers clean more thoroughly but raise the chance of blocking a domain the user wanted to keep, which is why Light carries minimal breakage risk while Ultimate carries high risk.
The project supports this with practical guidance rather than just bigger lists. Pro is marked as recommended, Pro++ as more aggressive, and Ultimate as the most aggressive, and size-optimized Mini versions are listed for Pro, Pro++ and Ultimate.
Editorial conclusion
HaGeZi DNS Blocklists is a GPL-3.0, network-wide blocking project that organizes its coverage into five cumulative Multi tiers, a large Threat Intelligence Feeds add-on, and a wide set of specialized standalone lists for scams, pop-ups, new domains, rebind protection, NSFW content, and more. The repository ships the lists in several format directories, including adblock, dnsmasq, rpz and wildcard, so users pick the format that matches their tool. The documentation is candid that aggression trades breakage risk for thoroughness, pointing new users at Multi PRO plus TIF and providing a direct link generator and lookup tool to simplify setup. It is a maintained, source-transparent option for anyone running DNS or content blocking at the network level.
Frequently asked questions
What are the best DNS blocklists?
The README presents HaGeZi DNS Blocklists as one maintained, GPL-3.0 set that covers ads, trackers, telemetry, phishing, malware, and scams network-wide, with five Multi tiers and a Threat Intelligence Feeds add-on. Which set is best depends on a user’s tool, region, and tolerance for breakage, and the documentation recommends starting with Multi PRO plus the TIF list rather than claiming a single universal winner.
Which DNS blocks 18+ content?
The project includes a dedicated NSFW list whose stated purpose is to block adult content. It is one of the specialized standalone lists in the catalog alongside gambling, social networks, and similar category-based blocklists.
What is a DNS blocklist?
A DNS blocklist is a set of domains that a DNS server or content blocker refuses to resolve, which blocks the associated ads, trackers, telemetry, phishing, malware, scams, and other unwanted traffic network-wide. The README describes HaGeZi as exactly such a set, usable with any common DNS server, ad blocker, or content blocker and for any region.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/hagezi-dns-blocklists)Star history chart for your README
[](https://hysenlabs.com/projects/hagezi-dns-blocklists)Was this useful?