Vault 2.x: Where HashiCorp's Secrets Manager Stands After the Big Version Jump
A tool for secrets management, encryption as a service, and privileged access management
At a glance
- What is it?
- HashiCorp Vault is a secrets management, encryption, and privileged access tool written in Go. This review covers its core mechanisms, the recent 2.x releases, and the operational trade-offs you need to weigh before adopting it.
- Who is it for?
- Adopt Vault if you need centralized secrets storage with strong access control, dynamic credential generation for cloud or database systems, and a detailed audit trail. Do not adopt it if your team lacks the operational capacity to manage a highly available service, because Vault is a stateful system that demands careful backup, unsealing, and upgrade procedures.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
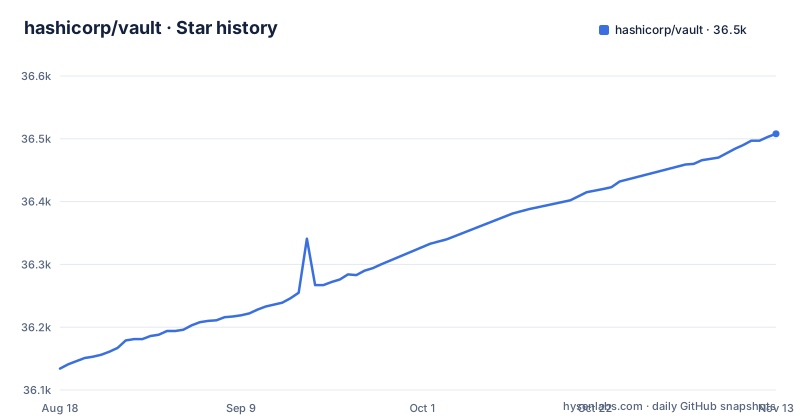
- hashicorp/vault36,508 ★ · +374
| Repository | 2026-08-18 | 2026-11-13 |
|---|---|---|
| hashicorp/vault | 36.1k | 36.5k |
374 Stars in the last 87 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The Problem Vault Solves and Who Needs It
Vault addresses a specific pain: modern systems need many secrets, from database credentials to API keys for external services. Tracking who accesses what is already hard, and adding key rolling, secure storage, and audit logs without a custom solution is nearly impossible. Vault provides a unified interface to any secret, with tight access control and a detailed audit log. The intended users are security teams that define policy and developers who need a consistent way to fetch secrets. It is not a simple key-value store for casual use; it is a control plane for secret lifecycle management.
How Vault Works: Storage, Encryption, and Leases
Vault encrypts data before writing it to persistent storage. That means gaining access to the raw storage is not enough to read the secrets. The README lists several storage backends, including disk and Consul. Each secret gets a lease. At the end of the lease, Vault automatically revokes the secret. Clients can renew leases through built-in renew APIs. This lease model is the core mechanism that makes dynamic secrets safe: credentials exist only for a limited time, and revocation can happen automatically. Vault also supports revoking a tree of secrets, such as everything read by a specific user or all secrets of a particular type. That tree-based revocation is useful for key rolling and for locking down systems after an intrusion.
Dynamic Secrets and Encryption as a Service
The dynamic secrets feature is what separates Vault from a static password manager. For systems like AWS or SQL databases, Vault can generate credentials on demand. An application asks for an S3 bucket credential, and Vault creates an AWS keypair with valid permissions, then revokes it when the lease expires. This removes the need to rotate static keys manually. Separately, Vault can encrypt and decrypt data without storing it. A security team defines encryption parameters, and developers store the encrypted result in their own database. The encryption-as-a-service mode means you do not have to design your own encryption scheme, but you do have to trust Vault's key management and API availability for every encrypt and decrypt call.
Getting Vault Running: Commands from the README
The README focuses on building from source. You need Go installed and a GOPATH configured. Clone the repository outside the GOPATH because Vault uses Go Modules. Run `make bootstrap` to download build tools. Then `make dev` compiles a development binary into `bin/vault`. For the UI, run `make static-dist dev-ui`. Tests require Docker and run via `make test`. You can target a single package with `make test TEST=./vault`. For production server startup, unsealing and configuration, see the official documentation at developer.hashicorp.com/vault/docs. The repository is the product source, not a quick-start guide.
The 2.x Release Line: What Changed and What It Means
The repository shows recent releases v2.2.0-rc1 (2026-10-08), v2.2.0 (2026-10-15) and v2.2.1 (2026-10-22). The jump to 2.0 is a major version change after years of 1.x. Check the release notes and CHANGELOG.md to see what changed in 2.x. Given that it is a major version, you should expect API or configuration incompatibilities. The steady run of 2.2.x releases suggests active maintenance, but the project's license is listed as NOASSERTION, which is unusual for a HashiCorp project. The Dockerfile in the repository carries an SPDX-License-Identifier of BUSL-1.1. You must verify the license in the repository before using it in a commercial product.
Operational Costs and Failure Modes
Vault is not a fire-and-forget tool. The lease model means every client must handle renewal and revocation. If an application caches a secret beyond its lease, it will get authentication failures. The README mentions that Vault can write to disk or Consul. In practice, Vault requires key shares and unsealing procedures, and losing the unseal keys can lock you out of your secrets permanently. The encryption-at-rest model protects against raw storage theft, but it also means you must manage the master keys carefully. The repository layout and the build instructions suggest a system that is designed for operators who understand distributed systems, not for a small team looking for a quick password vault.
Alternatives: How They Differ in Approach
A common alternative is a managed secrets service like AWS Secrets Manager. The difference is fundamental. AWS Secrets Manager stores static secrets and can rotate them for some services, but it does not generate credentials on demand for arbitrary systems. Vault's dynamic secrets engine creates credentials with scoped permissions and automatically revokes them, which is a different security model. Another alternative is an encrypted key-value store like etcd with your own encryption layer. That gives you storage but not the lease, revocation, or audit features. Vault bundles those features into one system. The trade-off is that Vault is a separate service to run and protect, whereas a managed service reduces your operational burden but locks you into a cloud provider and a less flexible secret model.
Maintenance, Upgrades, and Licensing
The repository is actively maintained, with recent releases v2.2.0-rc1, v2.2.0 and v2.2.1 all published in October 2026. That signals a responsive project, but it also means you will need to keep up with upgrades. Major version jumps like 2.0 require careful review of migration paths. The README mentions that the repository publishes two importable libraries: `github.com/hashicorp/vault/api` and `github.com/hashicorp/vault/sdk`. If you write a Go application that integrates with Vault, you depend on those libraries. The license is listed as NOASSERTION in the metadata, which is a red flag for legal review. HashiCorp's business model includes enterprise features, so the open-source core may have functional limits. Before adopting, check the actual license file in the repository and understand what is open source versus enterprise.
Editorial conclusion
Adopt Vault if you need centralized secrets storage with strong access control, dynamic credential generation for cloud or database systems, and a detailed audit trail. Do not adopt it if your team lacks the operational capacity to manage a highly available service, because Vault is a stateful system that demands careful backup, unsealing, and upgrade procedures. Before committing, verify your target platforms are covered by the secrets engines you need, and test the lease and renewal behavior against your application's connection patterns. Vault 2.x is a major version change, so review the upgrade notes for breaking changes before moving from 1.x.
Frequently asked questions
What is vault used for?
Vault is a tool for securely accessing secrets, and the project describes it as covering secrets management, encryption as a service, and privileged access management. It stores arbitrary key/value pairs, generates dynamic credentials for systems such as AWS or SQL databases, encrypts data without storing it, and records a detailed audit log.
how to install vault
The README's developer instructions cover building from source: install Go, set up a GOPATH, point GOBIN at $GOPATH/bin, clone the repository outside the GOPATH because Go Modules are used, then run make bootstrap and make dev, which places the binary in the bin and $GOPATH/bin folders.
how to install vault cli
The `vault` binary produced by make dev is placed in bin/vault; the README points to the Vault documentation site for further documentation.
how to use vault
The repository points to the Getting Started guides on HashiCorp's learning platform, to the documentation at developer.hashicorp.com/vault/docs, to the vault-examples repository for per-language integration samples, and to a sample application called hello-vault-go. The core model is that each secret is leased, renewed through built-in renew APIs, and revoked automatically when the lease ends.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/hashicorp-vault)Star history chart for your README
[](https://hysenlabs.com/projects/hashicorp-vault)Community discussions
Was this useful?