Hexclave: A User Infrastructure Platform Behind One Prompt
The user infrastructure platform. You choose the frontend, backend, and database. Hexclave handles everything else.
At a glance
- What is it?
- Hexclave bundles authentication, teams, RBAC, API keys, payments, email, analytics, webhooks and a secrets vault into one catalog of apps sharing a single user model. The repository describes the product well and the integration mechanics hardly at all, so the adoption decision rests on how much you trust a prompt-driven setup.
- Who is it for?
- Adopt Hexclave if you want auth, teams, RBAC, API keys, payments and email behind one user model and you are willing to let an AI agent drive the initial wiring. Skip it if you need published SDK reference material, a conventional install guide, or a licence the repository metadata identifies.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
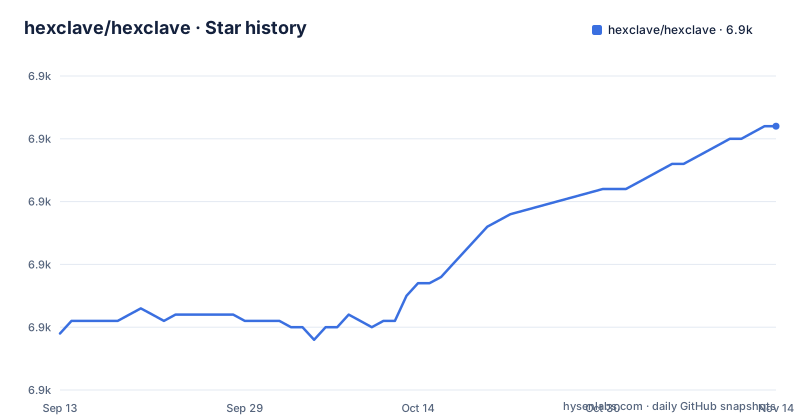
- hexclave/hexclave6,892 ★ · +33
| Repository | 2026-09-13 | 2026-11-14 |
|---|---|---|
| hexclave/hexclave | 6.9k | 6.9k |
33 Stars in the last 62 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The problem Hexclave claims, and the shape of the product
Most products reach the same wall at roughly the same time. You need sign-in, then organisations or workspaces, then roles that gate features, then API keys for programmatic access, then a way to charge for all of it, then transactional email, then some view of what users actually do. Each of those is a separate vendor with a separate data model, and the joins between them are where the bugs live. Hexclave positions itself as the layer that owns all of it under one user model, with each capability shipped as a catalog app you switch on when your product needs it. The README frames the audience as teams that want to choose their own frontend, backend and database while something else handles the user-facing infrastructure. The scope is wide: authentication, teams, RBAC, API keys, payments, emails, analytics, webhooks, a data vault, and a launch checklist. That breadth is the pitch and also the thing to interrogate, because a platform that spans auth through billing has to get the joins right between all of them, and the README does not show those joins.
How the apps share state: one user model, many surfaces
The README's central architectural claim is that every app is built on the same user model. That is what makes the catalog more than a bundle. The README gives a few concrete behaviours that follow from this: the workspace switcher remembers the last selection, an invite to a new address triggers auto sign-up rather than a separate onboarding path, and a permission check runs the same way on server and client. Payments follow the same logic, billing a person or a whole team through one model instead of two code paths. Analytics is described as needing one flag enabled, with active user counts and session replays available without a separate data stack. The design intent is clear: fewer handoffs between systems that each keep their own copy of who a user is. What the README does not expose is the storage schema, the session format, or how a permission check resolves when a user belongs to several workspaces with different roles. Those are the details that determine whether the shared model holds up in a product with non-trivial tenancy.
Setup runs through an AI skill endpoint, not an install guide
The README does not contain a conventional getting-started section. Instead it offers a prompt to paste into a coding agent: read skill.hexclave.com and help me setup hexclave in this project. For agents, it documents a fetch call against the same host with question and context parameters, shown as a curl command with a placeholder question. That is the entire documented setup path in the README. The practical consequence is that your first integration step is a network fetch whose output you have not reviewed, executed by a tool that will then edit your project. That is a real trust decision, and it is worth being explicit about it rather than treating the prompt as a convenience. The upside is that integration instructions can be updated server-side without a new release of the package. The downside is that the instructions you follow are not in the repository, are not versioned alongside the code you install, and cannot be diffed in a pull request. If your team needs a reproducible bootstrap that a human can read and approve, this design works against you, and you will want to capture whatever the skill endpoint returns into your own repository before running it.
Where the documentation thins out
Several claims in the README are stated as outcomes without a mechanism. API keys are said to be auto-revoked when leaked, with the full secret shown only once and plaintext never retained after creation. The one-time display and the no-plaintext rule are ordinary and credible. Auto-revocation on leak implies a detection path, and the README does not say what it is: a scanner over public sources, a pattern match on repository pushes, or something else. Data Vault is described as locked with your secret so the platform never sees plaintext, and as server-only by design, but the encryption scheme is not named. Webhooks are called signed and tamper-proof with retries and backoff handled for you, and verification is said to take five lines, yet no signature header, algorithm or retry schedule appears. Emails claim delivery tracking with opens and clicks. None of this is unusual for a README, and none of it is disproven, but a reader deciding whether to move authentication and billing onto this platform needs those specifics. The honest summary is that the repository describes a product surface, not an integration contract, and the integration contract lives behind the skill endpoint.
Licence: two identifiers on one badge
The repository metadata reports the licence as NOASSERTION, which means GitHub could not map the files it found to a single recognised identifier. The repository does carry a LICENSE file at the top level, and that file, not the metadata, is where the terms have to be read. I am not giving legal advice and cannot confirm which directories fall under which licence. What I can say is that the NOASSERTION metadata is the first thing to resolve before you build on this, and the answer is in the repository's LICENSE file.
Maintenance cost and release cadence
The release list shows dashboard builds moving quickly: versions 1.0.133, 1.0.134 and 1.0.135 between 2026-10-20 and 2026-10-30, with the last push to the dev branch on 2026-11-02. The default branch is dev, not main or master, which suggests development happens on that branch and releases are cut from it. Two things follow. First, a fast-moving dashboard means the surface you configure in the browser can change under you, and any screenshots or written procedures your team keeps will drift. Second, the versioned artifacts in the release list are dashboard builds, not SDK or server packages, so the release list does not tell you how the parts you import into your application are versioned or how breaking changes are communicated. For a platform holding authentication and payment state, the upgrade question is not how often it ships but what guarantees accompany a version bump, and that is not answerable from what is here. Budget for reading release notes rather than assuming semantic versioning discipline.
How it differs from Supabase and Clerk
The examples folder includes supabase and clerk-integration-demo entries, so the comparison is fair game. Supabase gives you a Postgres database first and layers auth, storage and edge functions on top; you own the schema and write the policies, and the platform's value is the database you get. Clerk is narrower and deeper on authentication: prebuilt components, session management and organisation support, with billing and analytics handled elsewhere. Hexclave's stated difference is the opposite of both. It does not give you a database, and it does not stop at authentication. It assumes you already have a frontend, backend and database and offers to own the user-shaped layer across all of them, including payments and email, which Supabase and Clerk largely leave to other vendors. That is a bigger bet on one vendor. The trade is fewer integration seams for more concentration: if the shared user model is right, you avoid stitching four systems together, and if it is wrong for your domain, you have moved billing and identity onto a platform whose internals the README does not describe.
Who should adopt it, and what to check first
The fit is a small team building a multi-tenant product that expects to charge for it, wants passkeys and OAuth without writing the flows, and is comfortable letting a coding agent perform the initial integration. The catalog model suits products that will add teams, roles and metering over time, since those apps are switched on rather than migrated to. The misfit is anyone who needs a published API reference before writing code, a pinned and reviewable install procedure, or a single unambiguous licence. It is also a poor fit if your users are not the unit of tenancy, since the entire design rests on that model. Before adopting, fetch the skill endpoint with your actual stack as context and read what comes back, because that response is the real documentation. Confirm the licence terms from the LICENSE file.
Editorial conclusion
Adopt Hexclave if you want auth, teams, RBAC, API keys, payments and email behind one user model and you are willing to let an AI agent drive the initial wiring. Skip it if you need published SDK reference material, a conventional install guide, or a licence the repository metadata identifies. Before committing, fetch the skill endpoint for your stack and confirm the licence terms in the LICENSE file, since the repository metadata reports NOASSERTION.
Frequently asked questions
How do I start using Hexclave in an existing project?
You paste one prompt into your coding agent: Read skill.hexclave.com and help me setup hexclave in this project. An agent that prefers to fetch directly can curl the same skill documentation with a question and context parameter.
Which package manager does the Hexclave monorepo allow?
pnpm: the repository ships pnpm-lock.yaml and pnpm-workspace.yaml, and both the pre-no-codegen and pre-preinstall scripts first run scripts/check-package-manager.mjs. SDK generation can be skipped with HEXCLAVE_SKIP_TEMPLATE_GENERATION set to true.
Which ports does the local Hexclave CLI use?
HEXCLAVE_API_URL points at http://localhost:8102 and HEXCLAVE_DASHBOARD_URL at http://localhost:8101, both built from NEXT_PUBLIC_HEXCLAVE_PORT_PREFIX, which defaults to 81 so one variable shifts both.
What does the Hexclave API keys app do with a leaked key?
Leaked keys are auto-revoked, keys work for both users and teams, and the full secret is shown only once because the plaintext is never kept after creation.
What happens to secrets I put in the Hexclave Data Vault?
The vault is locked with your own secret so the platform never sees the plaintext, store and retrieve take two lines each, and it is server-only by design. A vault keyed by your own secret has no documented recovery path.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/hexclave-hexclave)Star history chart for your README
[](https://hysenlabs.com/projects/hexclave-hexclave)Was this useful?