Harden-Windows-Security: a Microsoft-only hardening toolkit for Windows 11
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build of Windows | Provides tools and Guides for Personal, Enterprise, Government and Military security levels | SLSA Level 3 Compliant for Secure Development and Build Process | Apps Available on MS Store✨
At a glance
- What is it?
- HotCakeX's repository ships two Windows apps and a PowerShell script that apply Microsoft's own security features without third-party components. It is a good fit for admins who want documented changes, and a poor fit for anyone expecting unattended fleet automation.
- Who is it for?
- Adopt it if you administer a small number of Windows 11 machines and want hardening applied through Microsoft's own documented mechanisms, with AppControl Manager handling application control policy. Do not adopt it if you need a fleet-wide deployment path that does not go through the apps: the README points to Microsoft Store apps and a PowerShell script, with enterprise Intune policies applied using the Harden System Security app.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly C#, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
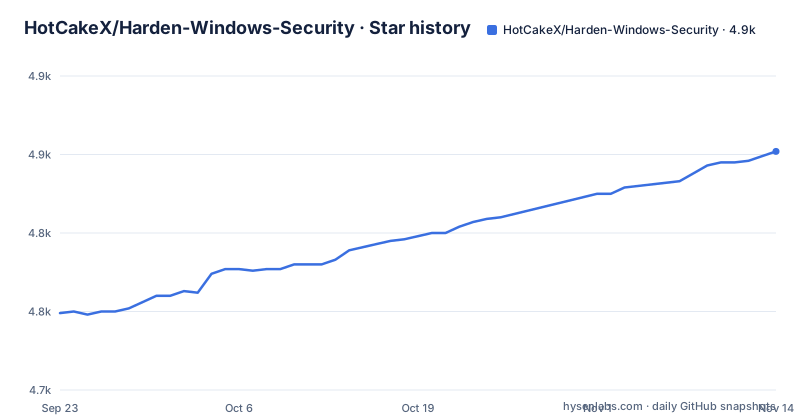
- HotCakeX/Harden-Windows-Security4,852 ★ · +103
| Repository | 2026-09-23 | 2026-11-14 |
|---|---|---|
| HotCakeX/Harden-Windows-Security | 4.7k | 4.9k |
103 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What Harden-Windows-Security actually changes on a Windows 11 machine
The repository is not a single program. It is a collection of tools that configure features Microsoft already shipped in Windows, such as application control. The README states the project "only uses the features that have already been implemented by Microsoft in Windows OS" and avoids third-party components or dependencies. That constraint is the whole design premise.
The audience follows from that premise. Personal users get a guided way to turn on protections they would otherwise have to research one by one. Enterprise, government and military readers are named in the repository description as target security levels, which suggests the tooling is meant to reach stricter configurations than a default install. The repository root also contains a PowerShell script, Harden-Windows-Security.ps1.
What it is not: a monitoring product or an endpoint detection agent. For enterprises, the README says the Harden System Security app can apply the provided Intune security policies to workstations and then verify their compliance against those policies and give a security score.
Two apps and a script: how the pieces fit together
The repository layout shows a top-level folder for each application plus the root PowerShell script. "Harden System Security" is the app that applies the hardening categories, and its documentation lives in the wiki under Harden-System-Security. "AppControl Manager" is a separate app for building and managing application control policies, documented under AppControl-Manager in the wiki. The README links a third resource set, Application Control for Business Resources, which is documentation rather than code.
The split matters because the two apps answer different questions. Harden System Security is about the state of the operating system. AppControl Manager is about what is allowed to execute, which on Windows means App Control (WDAC) policy. The release history reflects the separation: AppControlManager-v2.0.741.0 and HardenSystemSecurity-v1.0.101.0 are versioned independently, so a fix in one does not imply a change in the other.
The implementation language is C#, and the README badges link to the .NET download page and Visual Studio, so building from source means a .NET toolchain. The repository also carries a CITATION.cff, which is unusual for a hardening toolkit and indicates the author expects the work to be cited.
One supply-chain detail is stated in the repository description: SLSA Level 3 compliance for the development and build process. That is a claim about how artifacts are produced, and it is the kind of claim worth checking against the build provenance rather than taking on faith.
Installing the Harden System Security app and running a first hardening pass
The README's How To Use section gives one install route: the Microsoft Store listing for Harden System Security. The install badge links to apps.microsoft.com/detail/9p7ggfl7dx57. The Store is the path the How To Use section presents.
If you would rather not use the Store, the repository root contains the PowerShell script, Harden-Windows-Security.ps1. Open the script and read its own header before running it rather than guessing flags.
For application control, the second app installs from its own Store listing, linked in the README as apps.microsoft.com/detail/9PNG1JDDTGP8. The wiki page AppControl-Manager is where the policy-building workflow is described. A reasonable first use is to open AppControl Manager, build a policy in audit mode, and read the resulting events before switching anything to enforcement.
Both apps are Windows apps distributed through the Microsoft Store.
Where this toolkit stops being the right answer
The biggest limitation is deployment shape. Everything the README highlights is an app or a script you run yourself; for enterprises it points to provided Intune security policies that you apply to workstations using the Harden System Security app. If your environment manages thousands of endpoints through a device management service, the toolkit's own distribution channel, the Microsoft Store, may not be the channel your fleet uses.
Application control is the second sharp edge. WDAC policies that are too strict will block software people need, and the failure mode is a machine that will not run an application rather than a warning dialog. The repository provides AppControl Manager to build and manage those policies. Anyone enabling enforcement without first collecting audit data is taking a risk the tooling cannot undo for them.
Then there is the question of scope creep. A hardening checklist applied wholesale can break line-of-business software, disable a protocol a printer depends on, or lock out a local recovery path. The project's stated approach of using only Microsoft's supported methods reduces the chance of unsupported registry hacks, but it does not make every setting appropriate for every machine. The tool applies configuration; it does not evaluate whether that configuration fits your workload.
How it compares with Microsoft's own baselines and with CIS-style checklists
The obvious alternative is a Microsoft security baseline, distributed as Group Policy or Intune configuration profiles. The difference in approach is architectural. A baseline is a set of policy definitions you import into a management system and link to a scope of devices; the settings then flow through the same policy engine that already manages the fleet, and you can report on compliance centrally. Harden-Windows-Security is the opposite: it configures the machine through an app or a script, and for enterprises the README points to provided Intune security policies applied with the Harden System Security app.
That makes the two options complementary rather than competing. A baseline scales and audits; this toolkit explains and applies. If your problem is "I have one laptop and I do not know which Windows settings to turn on," the baseline route means standing up policy infrastructure you may not have. If your problem is "I have ten thousand laptops and I need drift reporting," the toolkit route means running an app ten thousand times.
A second alternative is a community checklist such as a CIS benchmark, which is a document rather than an executable. You read it, decide which items apply, and implement them yourself. Harden-Windows-Security encodes similar intent but ships the implementation and, per the README, restricts itself to Microsoft's supported mechanisms. That restriction is a real difference: a checklist may recommend a registry value that Microsoft does not document as a supported configuration point, and this project will not.
Maintenance, licensing and what the release cadence implies
The repository is not archived, and the last push was on 2026-10-30. The release list shows AppControl Manager at v2.0.741.0 on 2026-10-29 and Harden System Security at v1.0.101.0 on 2026-10-29, with an earlier Harden System Security release at v1.0.100.0 on 2026-10-26. That is a fast cadence for both apps, which cuts both ways: fixes arrive quickly, and the version you pinned last month is already behind.
The upgrade cost falls mostly on AppControl Manager users. Application control policies interact with the operating system in ways that hardening toggles do not, so a new build of AppControl Manager is worth reading about before you deploy it across machines you cannot easily reach. Harden System Security versioning in the 1.0.x range suggests smaller, more incremental changes.
The licence is MIT, which permits commercial use, modification and redistribution provided the copyright notice and permission notice are included. That is permissive enough for internal enterprise deployment and for embedding the code in another product. It is not a legal opinion, and if you redistribute the apps or ship a derivative, have your own counsel confirm the notice requirements are met. The Microsoft Store listings carry their own terms, which are separate from the repository licence.
Editorial conclusion
Adopt it if you administer a small number of Windows 11 machines and want hardening applied through Microsoft's own documented mechanisms, with AppControl Manager handling application control policy. Do not adopt it if you need a fleet-wide deployment path that does not go through the apps: the README points to Microsoft Store apps and a PowerShell script, with enterprise Intune policies applied using the Harden System Security app. Before rolling anything out, verify which hardening categories apply to your build and confirm that the AppControl Manager release you download matches the version listed in the repository's recent releases.
Frequently asked questions
How do I install Harden System Security?
The README's How To Use section points to the Microsoft Store listing for the app, linked as apps.microsoft.com/detail/9p7ggfl7dx57.
Can Harden-Windows-Security harden a Windows 11 system?
Yes. The repository description says it works with the latest build of Windows, and the README states that it only uses features Microsoft has already implemented in Windows.
Does Harden-Windows-Security require third-party components?
The README states the repository uses only Microsoft's already-implemented Windows features and relies on no third-party component or dependency. The hardening is applied through official, documented Microsoft methods.
What is AppControl Manager and how does it differ from Harden System Security?
They are two separately versioned apps in the repository. AppControl Manager builds and manages application control policies, while Harden System Security applies the operating system hardening categories; each has its own wiki page.
What licence does Harden-Windows-Security use?
The repository is MIT licensed, which permits commercial use and modification as long as the copyright and permission notices are included. The Microsoft Store listings carry separate terms.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/hotcakex-harden-windows-security)Star history chart for your README
[](https://hysenlabs.com/projects/hotcakex-harden-windows-security)Was this useful?