webcrack: deobfuscating obfuscator.io output and unpacking webpack bundles
Deobfuscate obfuscator.io, unminify and unpack bundled javascript
At a glance
- What is it?
- webcrack is a TypeScript tool that reverses obfuscator.io output, unminifies, transpiles and unpacks webpack or browserify bundles. It installs as a CLI or an API, and its main cost is a Node.js version constraint tied to isolated-vm.
- Who is it for?
- Adopt webcrack when you have a minified or obfuscator.io-processed file and need readable output, and you can run Node.js 22 or 24. Skip it if you are on an odd-numbered Node release, if you need an unpacker for a bundler other than webpack or browserify, or if you expect the tool to recover original identifier names.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
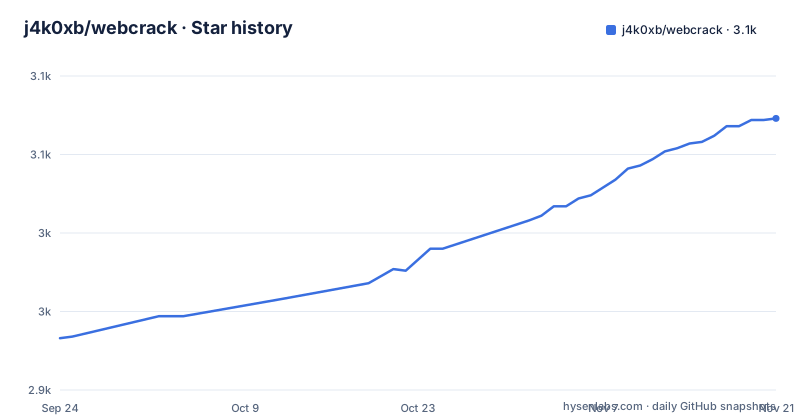
Star history
- j4k0xb/webcrack3,073 ★ · +140
| Repository | 2026-09-24 | 2026-11-21 |
|---|---|---|
| j4k0xb/webcrack | 2.9k | 3.1k |
140 Stars in the last 58 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What webcrack is for
The README states the goal plainly: webcrack is a tool for reverse engineering javascript. It deobfuscates obfuscator.io output, unminifies, transpiles, and unpacks webpack or browserify bundles, aiming to resemble the original source code as much as possible. That last phrase is the honest framing. This is not a decompiler that recovers the file the author wrote. It is a set of transformations applied to a build artifact so a human can read it.
The people who need this are usually looking at code they did not write and cannot read in its shipped form. A security reviewer handed a minified script from a third-party vendor. Someone auditing a browser extension. An engineer trying to understand what a site actually runs before deciding whether to trust it. The README also points at an online playground at webcrack.netlify.app, which matters because you can evaluate the output on a sample before installing anything.
The repository is a pnpm workspace with apps/ and packages/ directories, built with turbo and tested with vitest. The root package.json is private and marks the workspace, while the published artifact is the webcrack package on npm.
How the transformations work
webcrack is AST-based. The topics list includes ast, and the README's feature list makes two claims that only make sense for a scope-aware transform: safety, described as considering variable references and scope, and auto-detection, described as finding code patterns without needing a config.
That combination is the interesting part. A naive deobfuscator substitutes string arrays and wrapper calls textually, which breaks as soon as two scopes reuse the same name. webcrack instead parses the input, identifies obfuscator.io patterns, and rewrites them while tracking which binding each identifier refers to. The same machinery handles the bundler case: webpack and browserify both wrap modules in a runtime with a module map, and unpacking means resolving that map into separate files with their original module paths where the runtime preserves them.
The API example in the README shows the shape of the result. You get result.code, a single transformed string, and result.bundle, a separate structure. Then result.save('output-dir') writes out a directory. That split tells you the two modes are distinct: a single-file deobfuscation produces code, while a bundle produces a tree. The CLI mirrors this with a -o output-dir flag for the bundle case and stdout redirection for the single-file case.
One dependency deserves attention. The README notes webcrack depends on isolated-vm. That library executes code in a separate V8 isolate, which is how a deobfuscator can safely evaluate expressions that obfuscator.io generates at runtime rather than statically. It is also the source of the project's tightest constraint, covered below.
Installing webcrack and running a first deobfuscation
The README gives two install paths. For command-line use, install globally:
npm install -g webcrack@latestAfter that, the binary is on your PATH. The README's first example passes a file and prints the result to stdout:
webcrack input.jsIf you want the output in a file rather than the terminal, the README redirects it:
webcrack input.js > output.jsFor a bundle, the README uses the -o flag to write a directory instead of a stream:
webcrack bundle.js -o output-dirExpect output-dir to contain the unpacked modules rather than one file. If your input is a single obfuscated script and not a bundle, the redirect form is the one to use.
The programmatic path starts with a local install:
npm install webcrack@latestThen the README's API example reads a bundle, runs the default export, and saves the result:
import fs from 'fs';
import { webcrack } from 'webcrack';

const input = fs.readFileSync('bundle.js', 'utf8');

const result = await webcrack(input);
console.log(result.code);
console.log(result.bundle);
await result.save('output-dir');
The function is async, and result.save is awaited too. Note that no configuration object is passed in this example, which is consistent with the auto-detection claim: the default call is meant to work without options. The README does not document the full option set here; it links to an API reference at webcrack.netlify.app/docs/guide/api.html.
The Node.js version constraint is the real adoption cost
The README states the requirement as Node.js 22 or 24, and adds a note that webcrack depends on isolated-vm, which does not recommend using odd-numbered Node.js releases because they frequently break ABI and API compatibility with V8. The README itself carries a TODO comment about adding 26 on release.
Read that as an operational constraint, not a footnote. If your environment pins an odd-numbered Node release, or if you upgrade Node on a schedule that outpaces webcrack's supported list, the isolated-vm dependency is where things break. The failure is at the native module level, which typically means an install or load error rather than a wrong answer. That is a better failure mode than silent corruption, but it still means your Node version is coupled to this tool's release cadence.
The release history supports the same reading. The most recent release listed is v2.16.0 from 2026-04-25, following v2.15.1 from 2025-02-27 and v2.15.0 from 2024-12-05. The last push to the repository was on 2026-07-26. Releases are not frequent, and the gap between v2.15.0 and v2.15.1 is roughly three months while the gap to v2.16.0 is about fourteen months. Plan for a tool you install at a known version and revisit, not one that tracks upstream changes quickly.
Where webcrack stops being the right tool
The README scopes the target precisely: obfuscator.io for obfuscation, webpack or browserify for bundling. Anything outside that is not claimed. If your input was processed by a different obfuscator, auto-detection has no pattern to match, and you are relying on the generic unminify and transpile passes, which will not undo a transformation they were not written for.
The deeper limitation is naming. Nothing in the README claims identifier recovery. Obfuscator.io renames variables to short meaningless strings, and a deobfuscator can restructure control flow and inline the string array, but it cannot know that a variable called _0x4a2b was named userToken in the original. You get readable structure and unreadable names. For auditing logic that is often enough. For reconstructing a maintainable codebase it is not.
There is also a category error worth naming. webcrack is a static transformation tool with a sandboxed evaluator, not a debugger and not a dynamic analysis framework. If the question you are answering is what this code does at runtime under specific inputs, running it in a controlled environment gives you a different and sometimes better answer. webcrack gives you source-shaped text you can read, which is a different deliverable.
Finally, the README's safety claim is about variable references and scope, meaning the tool avoids breaking the program's semantics during rewriting. It is not a claim that running webcrack on hostile input is safe. The isolated-vm dependency exists precisely because evaluating untrusted expressions is part of the job.
Alternatives and how they differ
The related searches surface Restringer and De4js alongside webcrack, and the differences are structural rather than cosmetic.
De4js is a browser-based deobfuscator. You paste code into a page and get transformed output back. That is a lower-friction starting point and requires no Node install, which sidesteps the isolated-vm constraint entirely. The trade-off is that a browser tool is a manual, one-file-at-a-time workflow with no programmatic interface, so it does not fit a pipeline where you process many artifacts or want the result saved to a directory tree.
Restringer takes a different architectural position. Where webcrack's README emphasizes auto-detection without configuration, a configurable deobfuscation framework expects you to select the transforms that apply to your input. That is more work up front and more control when auto-detection guesses wrong, which is exactly the situation you hit with an obfuscator that is not obfuscator.io.
There is also the option of not using a deobfuscator at all. For a webpack bundle, a source map, if the project ships one, gives you the original sources with original names, which no deobfuscator can match. Checking for a map before reaching for webcrack is cheap and occasionally makes the whole exercise unnecessary. The README does not mention source maps, so treat this as an alternative outside the tool rather than a feature it offers.
Licence and upgrade cost
webcrack is MIT licensed, and the LICENSE file sits at the repository root. MIT is permissive: it allows use, modification and redistribution with the licence and copyright notice retained. That is a statement about the licence text, not legal advice, and it covers webcrack itself.
Two things sit outside that grant. The isolated-vm dependency has its own licence, and the README links to that project's security section when explaining the odd-numbered Node release caveat. If your organisation audits transitive dependencies, isolated-vm is a native module and belongs in that review. Separately, the licence on the code you deobfuscate is a different question entirely. webcrack transforms input you supply; it says nothing about whether you are permitted to process that input.
Upgrade cost is dominated by the Node constraint. Because isolated-vm is native and tracks V8, moving webcrack forward may force a Node move with it. The release cadence listed above is slow enough that pinning a known-good combination of webcrack and Node version and upgrading deliberately is more practical than tracking latest. The repository uses pnpm workspaces with turbo, so building from source is a pnpm install at the root followed by the turbo build script, but for normal use the npm package is the path the README describes.
Editorial conclusion
Adopt webcrack when you have a minified or obfuscator.io-processed file and need readable output, and you can run Node.js 22 or 24. Skip it if you are on an odd-numbered Node release, if you need an unpacker for a bundler other than webpack or browserify, or if you expect the tool to recover original identifier names. Before committing, run one real input through `webcrack input.js` and inspect whether the output is readable enough for your purpose, then check the docs page for the CLI reference at webcrack.netlify.app/docs/guide/cli.html, because the README does not document individual flags.
Frequently asked questions
How can I deobfuscate JavaScript code with webcrack?
Install it with npm install -g webcrack@latest and run webcrack input.js, or redirect the result to a file with webcrack input.js > output.js. For a webpack or browserify bundle, use webcrack bundle.js -o output-dir to write the unpacked modules to a directory.
Which Node.js version does webcrack require?
The README states Node.js 22 or 24. It notes that webcrack depends on isolated-vm, which does not recommend odd-numbered Node.js releases because they frequently break ABI and API compatibility with V8.
Can webcrack recover the original variable names?
The README does not claim identifier recovery. It describes deobfuscating obfuscator.io output and unpacking bundles so the result resembles the original source as much as possible, which means readable structure but not the names the author originally used.
Can I try webcrack without installing it?
Yes. The README points to an online playground at webcrack.netlify.app, where you can run it in the browser before installing the CLI or the npm package.
Does webcrack support bundlers other than webpack and browserify?
The README names only webpack and browserify for unpacking. Other bundlers are not mentioned, so unpacking support for them is not documented.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/j4k0xb-webcrack)Star history chart for your README
[](https://hysenlabs.com/projects/j4k0xb-webcrack)Was this useful?