djangorestframework-simplejwt: token auth that plugs into DRF instead of replacing it
A JSON Web Token authentication plugin for the Django REST Framework.
At a glance
- What is it?
- A JazzBand plugin that adds JSON Web Token authentication to the Django REST Framework, with a small dependency surface.
- Who is it for?
- Simple JWT keeps a narrow shape: three runtime dependencies and an optional token_blacklist subpackage. It has 4,337 stars and 708 forks.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 6 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 22, 2026, and from our analysis. They are not legal advice.
Star history
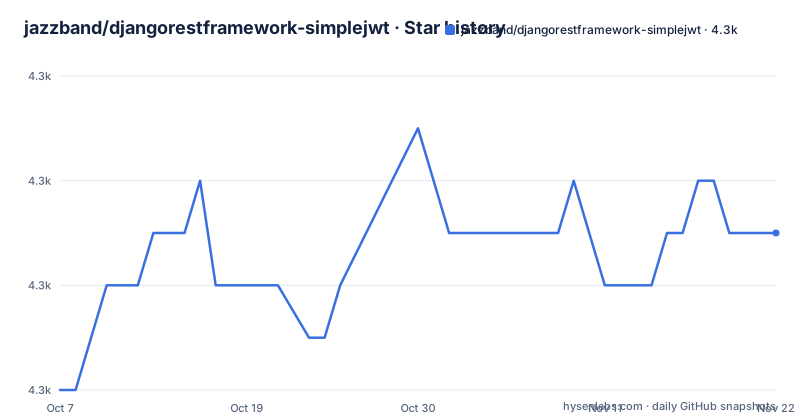
- jazzband/djangorestframework-simplejwt4,337 ★ · +3
| Repository | 2026-10-07 | 2026-11-22 |
|---|---|---|
| jazzband/djangorestframework-simplejwt | 4.3k | 4.3k |
3 Stars in the last 46 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
A deliberately small plugin with a very short README
The repository describes itself in one line: Simple JWT is a JSON Web Token authentication plugin for the Django REST Framework. That is the whole scope. It does not replace DRF, it does not wrap it, and it does not ask you to change your views. It registers authentication classes that DRF already knows how to call.
The README is correspondingly short. It carries the Jazzband badge, CI and codecov badges, PyPI version and supported-Python badges, a Read the Docs badge, then an abstract and a pointer to the documentation site. The only other content is a translations section that invites pull requests and links to inlang as the translation editor.
That last detail is worth noting because it tells you something about the project's maintenance culture. Translations can be contributed either directly with pull requests or through the inlang hosted editor.
The documentation site at django-rest-framework-simplejwt.readthedocs.io is where the full documentation lives. The repository itself is MIT licensed, written in Python, and last pushed on 2026-11-02.
Three runtime dependencies tells you what the design bets on
The dependency list in `setup.py` is short enough to read as a design statement. Django, Django REST Framework, and PyJWT. Nothing else.
    install_requires=[
        "django>=4.2",
        "djangorestframework>=3.14",
        "pyjwt>=1.7.1",
    ],
There is no Redis dependency for a denylist, no cache library, no async HTTP client. The Python floor is 3.10 and Django's floor is 4.2, which puts the project in line with current long-term-support Django releases rather than older ones.
The cryptography story is handled through extras rather than required packages. The `crypto` extra asks for `cryptography>=3.3.1`, and there is a separate `python-jose` extra pinned to `python-jose==3.5.0`. The hard pin on that one is unusual and suggests the version has to be exact rather than merely compatible.
The development extras are far more elaborate than the runtime list, which is normal for a package with this many contributors. The `test` extra pulls in pytest along with pytest-django, pytest-cov, pytest-xdist, freezegun, tox and cryptography. Linting uses ruff, yesqa, pyupgrade and pre-commit. Typing uses mypy with django-stubs, djangorestframework-stubs and types-pytz. Documentation uses Sphinx with the Read the Docs theme. And the `dev` extra is deliberately built by concatenating all of those together with dev-only tools like pytest-watch, wheel, twine and ipython, which is a neat trick for avoiding a duplicated list.
How releases are versioned and published
Versions come from the tag rather than a hardcoded number. `setup.py` uses `setuptools_scm` with a post-release version scheme, so the released number is derived from git history at build time.
The Makefile shows the release path a maintainer actually walks. Linting goes through a tox environment, tests run under pytest, and the documentation target runs `sphinx-apidoc` with an explicit list of paths to exclude from the API docs before building HTML and running doctests.
.PHONY: build-docs
build-docs:
	sphinx-apidoc -o docs/ . \
		setup.py \
		*confest* \
		tests/* \
That exclusion list is interesting on its own. It names `backends.py`, `exceptions.py`, `settings.py` and `state.py`, plus the whole `token_blacklist` subpackage. Those paths are left out of the auto-generated API docs.
Publishing is a two-step local dance. The `dist` target cleans, builds both an sdist and a wheel, and lists the output directory. The `publish` target does the same build and then hands the result to twine.
.PHONY: publish
publish:
	python setup.py sdist bdist_wheel
	twine upload dist/*
Note the ordering implication: `dist` runs `clean` first, `publish` does not. A maintainer who runs `publish` straight after a build is uploading whatever is sitting in `dist/`, which is a small thing to know when reading a project's release habits.
Version 5.5.0 changed refresh behaviour and capped PyJWT
The repository lists three recent releases: v5.4.0 on 2025-01-07, v5.5.0 on 2025-02-26 and v5.5.1 on 2025-07-21. The repository also carries a `CHANGELOG.md`.
The 5.5.1 patch is a story about a migration file
Version 5.5.1 came out on 2025-07-21, five months after 5.5.0.
The repository currently shows 4,337 stars, 708 forks and 158 open issues. That backlog is worth reading before you commit to the package in production. The tree is conventional for a JazzBand package: the `rest_framework_simplejwt/` package with a `token_blacklist` subpackage, `tests/`, `docs/`, `scripts/`, a `licenses/` directory, `inlang.config.js`, `setup.cfg` alongside `setup.py`, `tox.ini`, `pytest.ini`, `codecov.yml` and a `CHANGELOG.md`.
Editorial conclusion
Simple JWT keeps a narrow shape: three runtime dependencies and an optional token_blacklist subpackage. It has 4,337 stars and 708 forks. The trade-off is equally real, since the README is three paragraphs long and everything you actually need lives in the Read the Docs site, so budget an hour reading the settings reference before you commit. If you are upgrading across v5.4.0, v5.5.0 and v5.5.1, read CHANGELOG.md first.
Frequently asked questions
What does djangorestframework-simplejwt do?
It is a JSON Web Token authentication plugin for the Django REST Framework, maintained under Jazzband and MIT licensed. It registers token-based authentication classes with DRF rather than replacing the framework, so your existing views, serializers and routers stay as they are.
What are the runtime dependencies?
`setup.py` lists three: django 4.2 or newer, djangorestframework 3.14 or newer, and pyjwt 1.7.1 or newer. Python 3.10 is the floor. Cryptography support is optional through the `crypto` extra, and there is a separate `python-jose` extra pinned to python-jose 3.5.0.
What changed in version 5.5.0?
The repository lists v5.5.0 as released on 2025-02-26; the repository also carries a CHANGELOG.md.
Why was version 5.5.1 released?
The repository lists v5.5.1 as released on 2025-07-21; the repository also carries a CHANGELOG.md.
Where is the real documentation?
The README is intentionally brief and points to django-rest-framework-simplejwt.readthedocs.io. The Makefile shows that modules such as settings, exceptions, backends and the token_blacklist package are deliberately excluded from generated API docs.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/jazzband-djangorestframework-simplejwt)Star history chart for your README
[](https://hysenlabs.com/projects/jazzband-djangorestframework-simplejwt)Was this useful?