ccglass shows you exactly what your coding agent sends to the model
See what your coding agent (Claude Code, Codex, Kimi) sends to the model — local proxy + web dashboard
At a glance
- What is it?
- A local logging proxy and web dashboard for Claude Code, Codex, Kimi, and a dozen other CLIs, built on base-URL redirection instead of TLS interception.
- Who is it for?
- ccglass is a focused answer to a real gap: agent CLIs that ignore proxy variables and hide their payloads. By intercepting only the loopback hop through base-URL redirection, it avoids CA certificates, TLS pinning, and fragile fetch patching, and the provider table shows the technique covering Claude Code, Codex, Kimi, Ollama, OpenRouter, and beyond.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 40 days ago.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 20, 2026, and from our analysis. They are not legal advice.
Star history
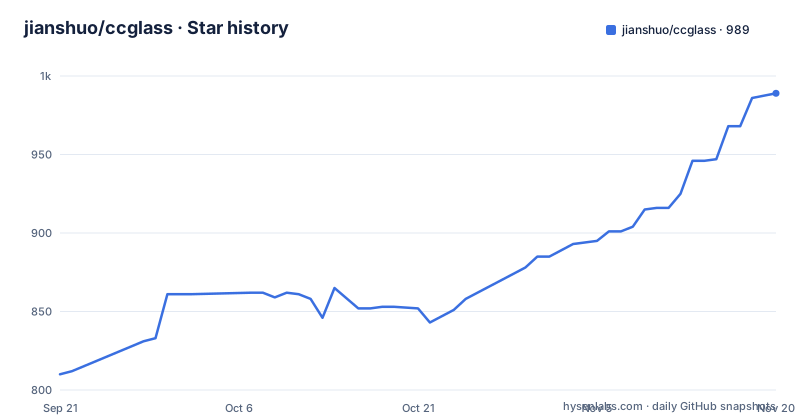
- jianshuo/ccglass989 ★ · +179
| Repository | 2026-09-21 | 2026-11-20 |
|---|---|---|
| jianshuo/ccglass | 810 | 989 |
179 Stars in the last 60 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The visibility problem
Coding agent CLIs hide their traffic. You type a prompt, the agent runs for a minute, tokens burn, and you never see the actual payload: the assembled system prompt, the tool schemas injected behind your back, the message history that grew to forty turns, or which cache hits saved money. When something goes wrong, a tool that misbehaves, a cost spike, a context blowout, you are debugging blind.
ccglass, an MIT-licensed npm package from jianshuo, fixes this with two pieces: a lightweight local logging reverse proxy and a web dashboard. It targets Claude Code, Codex, OpenCode, DeepSeek-TUI, Reasonix, CodeBuddy, Kimi, Ollama, OpenRouter, and more. The dashboard shows every request in real time, including the full system prompt, every tool schema, message history with tool calls, token, cache, and cost numbers, the agent-loop flow view, and a turn-to-turn diff.
Install and first run
Install and launch take two commands:
npm install -g ccglass     # or: brew install jianshuo/tap/ccglass
ccglass
With no arguments, ccglass asks which client to inspect, listing Claude Code, Codex, DeepSeek-TUI, Reasonix, Kimi, OpenCode, and CodeBuddy. Or name it directly: ccglass claude, ccglass codex, ccglass deepseek, ccglass kimi, and so on.
The tool then starts a proxy, points the client at it through the right base-URL environment variable, launches the client for you, and prints the dashboard address:
● ccglass watching Codex (OpenAI) → https://api.openai.com
  dashboard: http://127.0.0.1:57633
From that point, every request the agent makes passes through the local proxy and lands in the dashboard, where you watch it live.
Why base-URL redirection works
The engineering choice that makes ccglass simple is documented under a heading called Why. These agent CLIs are Node or native applications that ignore HTTP_PROXY and HTTPS_PROXY, so classic interception tools like Charles or mitmproxy never see their traffic. Fetch-patching tools that hook the client's internals break across updates.
ccglass sidesteps both problems. The client still does its own HTTPS to the real API endpoint; ccglass only intercepts the plain HTTP hop to localhost, which the client reaches because its base-URL variable was pointed there. No CA certificates to install, no TLS pinning to defeat, no monkey-patching that version drift breaks. The proxy sees the decrypted request body because the client hands it over in the clear on the loopback hop, then forwards it upstream itself. One mechanism, minimal moving parts.
Provider coverage
The provider table is the proof this approach generalizes. Each provider entry maps a command, the wrapped client, the environment variable it sets, the upstream it forwards to, and the wire format it expects. Claude Code goes through ANTHROPIC_BASE_URL to api.anthropic.com in Anthropic Messages format. Codex uses OPENAI_BASE_URL to api.openai.com in OpenAI Responses or Chat format. Kimi routes Claude Code against Moonshot's Anthropic-compatible endpoint, which means setting ANTHROPIC_AUTH_TOKEN to a Moonshot key.
Local runtimes are covered too: Ollama at 127.0.0.1:11434 and LM Studio at 127.0.0.1:1234 need no key at all. OpenRouter, GLM, Bedrock, and Vertex AI entries handle the enterprise and aggregator cases, with Bedrock using its own ANTHROPIC_BEDROCK_BASE_URL variable and Vertex pointed at a regional endpoint. The one structural outlier is CodeBuddy, whose built-in models hardcode their upstream URL, so ccglass falls back to a forward-proxy mode with TLS interception for that single provider.
Quirks worth knowing
The provider notes are refreshingly honest about failure modes. Codex only captures traffic in API-key mode. If Codex authenticates through ChatGPT login, it uses a WebSocket transport to chatgpt.com that bypasses OPENAI_BASE_URL entirely, and the dashboard stays empty. The README tells you to run codex doctor to check: if it reports auth mode chatgpt, switch to API-key mode.
Bedrock has its own documented limit: direct AWS endpoints fail through the proxy because SigV4 signs the Host header, so ccglass works against Bedrock-compatible gateways and prints a warning when it detects a direct endpoint. OpenCode auto-detects its upstream from OPENAI_BASE_URL and accepts a different variable name through --env-var. These notes read like they were written by someone who hit each problem personally, which is exactly what you want in debugging tool documentation.
IDE support and custom providers
IDE extensions that accept a custom API base URL, such as Cursor in BYOK mode, Cline, or Continue.dev, work through the proxy subcommand, which starts the proxy and dashboard without spawning any child process:
ccglass proxy --provider openai   # OpenAI-compatible IDEs (Cursor, Cline, Continue…)
ccglass proxy --provider claude   # Anthropic-compatible IDEs
You point the IDE's API base URL at the printed local address and watch requests appear in the dashboard. The limitation is stated plainly: it only works when the IDE lets you configure the base URL, which rules out locked-down enterprise builds.
Anything else that reads a base-URL variable works through the generic escape hatch:
ccglass run \
  --upstream https://my.custom.api/v1 \
  --env-var MY_CUSTOM_BASE_URL \
  -- my-tool [args...]
A shorthand form reuses an existing provider's format with a different upstream, so an OpenAI-compatible internal gateway inherits all of the OpenAI parsing and cost accounting without new code.
What you actually learn from it
The dashboard's value shows up in specific observations. The turn-to-turn diff reveals how much invisible state accumulates between your prompts: tool results you forgot, file contents re-read, system reminders injected. The token, cache, and cost numbers turn vibes about a model being expensive into a per-request accounting, and the cache-hit view explains why two identical-looking sessions cost different amounts.
The agent-loop flow view matters for debugging agent behavior: which tools the model chose, in what order, with what arguments, and what it saw back. That is the layer where most agent failures live, and it is normally invisible. For teams evaluating agents, comparing providers, or just auditing what a CLI sends to a third-party API, ccglass turns an opaque local process into a readable transcript, with everything staying on 127.0.0.1.
Editorial conclusion
ccglass is a focused answer to a real gap: agent CLIs that ignore proxy variables and hide their payloads. By intercepting only the loopback hop through base-URL redirection, it avoids CA certificates, TLS pinning, and fragile fetch patching, and the provider table shows the technique covering Claude Code, Codex, Kimi, Ollama, OpenRouter, and beyond. The dashboard turns system prompts, tool schemas, token costs, and turn-to-turn diffs into visible facts, which is what agent debugging has been missing. Captures may contain sensitive prompts, code and tool output: protect the log directory even though authorization headers and API keys are masked by default.
Frequently asked questions
Does ccglass need certificates or TLS interception?
Not for most providers. The client does its own HTTPS to the real API while ccglass intercepts only the plain HTTP hop to localhost via base-URL redirection, so no CA certs and no TLS pinning are involved. The single exception is CodeBuddy, whose hardcoded upstream URL forces a forward-proxy mode with TLS MITM.
Why is my ccglass dashboard empty when watching Codex?
Codex only sends traffic through ccglass in API-key mode. With ChatGPT login, Codex uses a WebSocket transport that bypasses OPENAI_BASE_URL entirely. Run codex doctor to check your auth mode, and switch to API-key mode if it reports chatgpt.
Can ccglass inspect tools beyond the built-in providers?
Yes. Any tool that reads a base-URL environment variable works through ccglass run with --upstream, --env-var, and your command, and ccglass proxy supports IDEs like Cursor, Cline, and Continue.dev by giving them a local base URL to point at. Ollama and LM Studio need no API key at all.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/jianshuo-ccglass)Star history chart for your README
[](https://hysenlabs.com/projects/jianshuo-ccglass)Was this useful?