OWASP Juice Shop: A Deliberately Vulnerable Web App for Security Training and Tool Testing
OWASP Juice Shop: Probably the most modern and sophisticated insecure web application.
At a glance
- What is it?
- OWASP Juice Shop is a modern, intentionally insecure web application designed for security training, awareness demos, CTFs, and testing security tools. This review covers its setup, architecture, limitations, and maintenance considerations.
- Who is it for?
- Adopt OWASP Juice Shop if you run security trainings, awareness demos, CTFs, or need a realistic target to test security tools. It is not for production use, as it is intentionally vulnerable.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 3 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
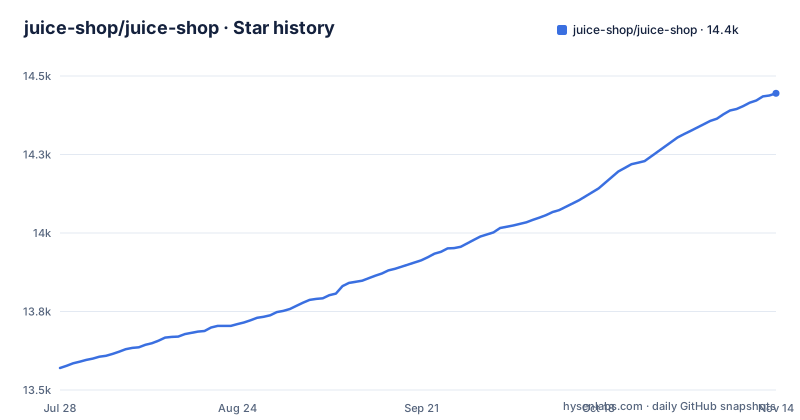
- juice-shop/juice-shop14,445 ★ · +875
| Repository | 2026-07-28 | 2026-11-14 |
|---|---|---|
| juice-shop/juice-shop | 13.6k | 14.4k |
875 Stars in the last 109 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What Problem Juice Shop Solves and Who It Is For
OWASP Juice Shop is a deliberately insecure web application. It exists to give security trainers, penetration testers, and CTF organizers a realistic target that contains vulnerabilities from the OWASP Top Ten and many other real-world flaws. The README describes it as 'probably the most modern and sophisticated insecure web application.' That is not marketing fluff; it is a practical tool. If you are teaching someone how SQL injection works, or you need a safe environment to test a vulnerability scanner, Juice Shop gives you a web shop built to fail in interesting ways. It is not for building a real store. It is for breaking things on purpose, and it is built to make that breaking educational and repeatable.
How Juice Shop Works: Architecture and Vulnerability Coverage
The application is a standard Node.js web app written in TypeScript. The repository layout and README indicate a typical Express-style server with a SQLite database, as hinted by the packaged binaries for sqlite3. The README states it encompasses the entire OWASP Top Ten along with other flaws. That means you get a coherent shopping site where each vulnerability has a place in the user journey. For example, a product search might be injectable, a comment field might store XSS, and the checkout process might have a broken access control. The README positions it as a guinea pig for security tools. The data flow is typical: a browser sends HTTP requests to the server, the server processes them with vulnerable code, and the database stores state.
Getting Juice Shop Running: Commands and Config Options
The README gives several ways to run Juice Shop. The simplest is from sources. You need Node.js installed, then you run `git clone https://github.com/juice-shop/juice-shop.git --depth 1`, `cd juice-shop`, `npm install`, and `npm start`. That starts the app on `http://localhost:3000`. For a quick test, the Docker route is faster: `docker pull bkimminich/juice-shop` and then `docker run --rm -p 127.0.0.1:3000:3000 bkimminich/juice-shop`. There are also packaged distributions for Windows, macOS, and Linux, which include binaries for sqlite3 and libxmljs2 bound to the OS and Node.js version. If you use Vagrant, you can clone the repo and run `cd vagrant && vagrant up` to get an instance at `192.168.56.110`. One important config note: some challenges require an external AI/LLM provider.
Node.js Compatibility and Distribution Constraints
Juice Shop officially supports specific Node.js versions, aligned with the Node.js LTS schedule. The README table shows that Node.js 26.x and 24.x are supported and tested, while 25.x is supported but not tested, and 23.x is not supported at all. This matters if you plan to run from sources or use a packaged distribution. Among the rows shown, packaged distributions are offered for Node.js 24.x, as x64 builds for Windows, MacOS and Linux. Docker images are available for `linux/amd64` and `linux/arm64` from the `master` branch, with a `snapshot` tag for the `develop` branch. If you are on a non-x64 platform, you will have to use Docker or run from source, which may introduce friction. The README warns that the packaged binaries are bound to the OS and Node.js version used during `npm install`, so you cannot swap them across platforms. This is a concrete constraint that can trip up a quick setup.
A Real Limitation: The AI/LLM Dependency for Some Challenges
Not every vulnerability in Juice Shop is self-contained. The README explicitly states that some challenges require an AI/LLM provider to work properly. That is a significant limitation if you are running an offline training environment or a CTF without internet access. You cannot just spin up the Docker container and expect every challenge to be solvable. You have to configure an external dependency, either a local model or a cloud provider, following the companion guide. This adds setup complexity and a potential cost if you use a paid API. For a tool that is supposed to be a low-friction training aid, this is a notable hurdle. It also means that the 'most sophisticated insecure web application' is not fully self-contained. If your goal is to demonstrate classic web vulnerabilities without any external services, you may need to skip those challenges or invest time in setting up a local AI provider.
Alternative Approaches: Other Insecure Web Apps and Their Differences
There are other deliberately vulnerable applications, but they take different approaches. For example, OWASP WebGoat is a Java-based training application that provides a structured set of lessons, each focusing on a specific vulnerability. WebGoat is more like a classroom exercise, with guided hints and a linear progression. Juice Shop, in contrast, is a full application that you have to explore and exploit organically. Another alternative is DVWA (Damn Vulnerable Web Application), which is a PHP/MySQL app with a simpler interface and a security level setting that changes the difficulty of each vulnerability. DVWA is easier to set up for a beginner, but it lacks the realism and breadth of Juice Shop. The key difference is that Juice Shop aims to be a modern web application with current frameworks and patterns, while WebGoat and DVWA feel more like lab exercises. If you want a realistic target that mimics a real e-commerce site, Juice Shop is closer. If you want structured lessons, WebGoat is a better fit.
Maintenance and Upgrade Costs, and License Implications
Juice Shop is actively maintained. The repository shows regular releases, with v20.3.0 released in October 2026, and the project is not archived. That means you can expect updates that add new challenges, fix bugs, and keep up with Node.js LTS versions. However, maintenance is not free. If you run from sources, you have to run `npm install` again when you pull new code, and you may need to upgrade your Node.js version to stay compatible. The README states that Node.js 23.x is not supported, so if you are on that version, you will have to change Node.js versions. Docker images are tagged latest from master and snapshot from develop, for linux/amd64 and linux/arm64. The license is MIT, which is permissive. You can use, modify, and distribute the code freely, even in commercial training. But note that the project is an OWASP flagship, so there is an expectation of responsible use: it is not meant to be deployed as a real application. The license does not restrict that, but the project's purpose does. The README also mentions a demo instance, but it warns that it is not for hacking and has no guaranteed uptime, so you should not rely on it for testing.
Editorial conclusion
Adopt OWASP Juice Shop if you run security trainings, awareness demos, CTFs, or need a realistic target to test security tools. It is not for production use, as it is intentionally vulnerable. Before adopting, verify the Node.js version compatibility, check the AI/LLM provider requirements for certain challenges, and confirm that the packaged distribution or Docker image matches your OS and architecture. Avoid it if you need a stable, secure application for real-world use.
Frequently asked questions
What is a juice shop in cyber security?
OWASP Juice Shop is a deliberately insecure web application written in TypeScript, built to cover vulnerabilities across the OWASP Top Ten plus other flaws found in real applications. The project positions it for security trainings, awareness demos, capture the flag events, and as a target for security tools.
how to install juice shop
There are four documented routes. From sources: clone the repository, run npm install, then npm start. Packaged: download the juice-shop archive for your OS and node version, unpack it, then npm start. Docker: pull bkimminich/juice-shop and run it with port 3000 mapped. Vagrant: clone, cd vagrant, then vagrant up, which gives a machine at 192.168.56.110.
how to install juice shop in docker
Install Docker, then run docker pull bkimminich/juice-shop and docker run --rm -p 127.0.0.1:3000:3000 bkimminich/juice-shop. Browse to localhost:3000. On macOS and Windows, browse to 192.168.99.100:3000 instead when you use docker-machine rather than native Docker.
how to run juice shop
Start from sources it is npm start after npm install, with the app served on port 3000. The Dockerfile form runs /juice-shop/build/app.js instead, and the Vagrant form serves the shop at 192.168.56.110 once vagrant up finishes.
how to access owasp juice shop
Every local route ends on port 3000, so browse to http://localhost:3000 after npm start or after starting the container. The Vagrant machine is at http://192.168.56.110. A public instance exists at http://demo.owasp-juice.shop, but the README calls it a deployment test and sneak-peek instance and states you are not supposed to use it for your own hacking endeavours.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/juice-shop-juice-shop)Star history chart for your README
[](https://hysenlabs.com/projects/juice-shop-juice-shop)Was this useful?