JumpServer: A Browser-Based PAM Platform for Mixed SSH, RDP, and Database Access
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.
At a glance
- What is it?
- JumpServer is an open-source privileged access management platform that centralizes SSH, RDP, Kubernetes, database, and RemoteApp access through a web browser. This review covers its component architecture, quickstart, licensing, and where it fits.
- Who is it for?
- Adopt JumpServer if you need a self-hosted, browser-based PAM for heterogeneous endpoints and prefer an all-in-one deployment over assembling separate tools. Avoid it if you require a permissive license.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
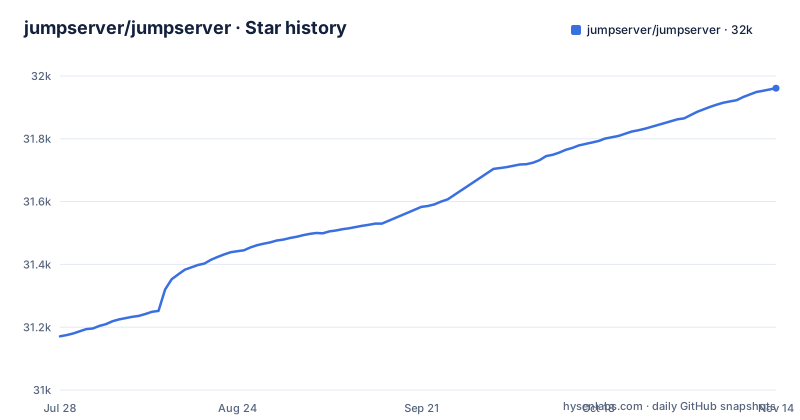
Star history
- jumpserver/jumpserver31,961 ★ · +790
| Repository | 2026-07-28 | 2026-11-14 |
|---|---|---|
| jumpserver/jumpserver | 31.2k | 32k |
790 Stars in the last 109 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What JumpServer Actually Solves
JumpServer addresses the problem of managing privileged access to many different endpoint types without exposing credentials or requiring users to install multiple clients. Instead of handing out SSH keys or RDP passwords, teams can funnel access through a single web interface. The target audience is DevOps and IT teams that need auditability and control over who reaches production servers, databases, or Kubernetes clusters. The README positions it as a PAM platform, which is a broader label than a simple SSH jump host. It covers SSH, RDP, Kubernetes, database, and RemoteApp endpoints. That breadth is the core value proposition: one tool for several protocols. For a team that currently juggles separate bastion hosts for each protocol, JumpServer could consolidate that. The browser-based access is a key differentiator, as it removes the need for a local client on the user's machine.
The Component Architecture: More Than a Single Binary
JumpServer is not a single application. The README lists the components in tables. Lina is the web interface, Luna is the web terminal and native client, KoKo is the general-purpose protocol connector and proxy, Chen is the web database connector, and Kael is the AI component. There are also application connectors for Windows (Tinker, free for Community Edition) and Linux (Panda, Enterprise Edition), plus enterprise-only components like Razor for RDP proxy, Magnus for database proxy, and Nec for VNC proxy. This modular design means that each protocol has its own service,. However, it also means that a deployment is a distributed system. For an operator, this complexity is a real cost. You are not deploying one service; you are deploying several that must be configured to talk to each other. The quickstart script hides this complexity, but for production you will need to understand each component's role. The separation does allow for targeted troubleshooting: if the web terminal fails, you can focus on Luna and KoKo. But it also increases the surface area for configuration errors.
Quickstart: One Command, But With Caveats
The README provides a single command to get started: `curl -sSL https://github.com/jumpserver/jumpserver/releases/latest/download/quick_start.sh | bash`. It requires a clean Linux server with at least 4 cores and 8GB of RAM. After the script runs, you access the platform at `https://<jumpserver-host>/` with username `admin` and password `ChangeMe`. That is a very low barrier to entry for a trial. However, the instructions are minimal. The script pipes a remote script directly into bash, which is a security consideration that a cautious operator will note. You are trusting the JumpServer team's TLS endpoint and the integrity of the script. For a production deployment, you would likely want to inspect the script first. The default credentials are a known risk; verify whether the system forces a password change on first login. The resource requirement of 4c8g is not trivial, especially for a small team that just wants to test. It suggests that the platform is designed for a certain scale, not for a Raspberry Pi.
Protocol Coverage and the Enterprise Split
The README lists support for SSH, RDP, Kubernetes, database, and RemoteApp endpoints. The open-source components cover the core protocols: KoKo as the general-purpose protocol connector and proxy, and Chen for web database access. But some connectors are marked as EE (Enterprise Edition): Razor for RDP proxy, Magnus for database proxy, Nec for VNC proxy, and Panda for the Linux application connector. That means the open-source version may not have full-featured proxy support for RDP and databases. If your environment relies heavily on RDP proxying or database connections through a proxy, you might need the commercial edition. The web database access via Chen is open-source, but the database proxy connector is EE. That distinction is not explained further. For an engineer evaluating the project, this split is a critical factor. You need to map your required protocols to the open-source components and confirm they meet your needs. Consult the official website or documentation for a feature comparison between CE and EE.
Licensing and Maintenance Considerations
JumpServer is licensed under GPL-3.0. That is a strong copyleft license. If you modify the source and distribute it, you must release your modifications under the same license. For internal use, this is usually not a problem, but if you plan to offer JumpServer as a managed service or embed it in a commercial product, the GPL obligations apply. The project is actively maintained, with recent releases including v5.1.1, v4.10.20 (LTS) and v3.10.24 (legacy LTS). The default branch is `dev`, which suggests that the `dev` branch is not for production use. You should use the LTS releases. The release cadence appears to be frequent, with multiple versions in a month. That means you will need to track updates and test upgrades. The component-based architecture means that an upgrade might require updating several services. The README points to SECURITY.md for version maintenance status. The GPL license also means that any third-party components you integrate must be compatible.
Alternatives and the Difference in Approach
A common alternative to JumpServer is Teleport, which also provides privileged access management for SSH, Kubernetes, and databases. Teleport uses a certificate-based approach where users authenticate to a proxy and then receive short-lived certificates for accessing targets. JumpServer, based on the README, appears to use a web-based terminal and proxy connectors. The key difference is that Teleport is designed around identity-aware access and zero trust, with a strong emphasis on machine-to-machine access and audit. JumpServer is more traditional bastion host, focusing on human access through a web UI. Another alternative is Apache Guacamole, which is a clientless remote desktop gateway. Guacamole supports RDP, VNC, and SSH, but it does not have the same PAM features like asset management, approval workflows, or database access. JumpServer has a broader protocol list, including Kubernetes and RemoteApp, which Guacamole does not. If you need a lightweight RDP gateway, Guacamole might be simpler, but it lacks the comprehensive audit and control features that JumpServer claims. The choice depends on whether you need a full PAM platform or just a gateway.
What the Documentation Does Not Tell You
The README is mostly component tables and a quickstart, so for authentication, session recording and upgrade procedures consult the official documentation. The quickstart gives you a way to test, but it does not guarantee that the default configuration is secure or production-ready, and the admin account ships with the documented password ChangeMe.
Editorial conclusion
Adopt JumpServer if you need a self-hosted, browser-based PAM for heterogeneous endpoints and prefer an all-in-one deployment over assembling separate tools. Avoid it if you require a permissive license. Before adopting, verify that the quickstart script's target Linux distribution is supported, confirm that all required components (Lina, Luna, KoKo, Chen) are deployable in your environment, and test the default admin credentials immediately. The project is actively maintained with recent LTS releases, but you must plan for GPL-3.0 compliance and the operational overhead of running multiple interconnected services.
Frequently asked questions
What is JumpServer?
An open-source privileged access management platform, also described as a bastion host. It gives DevOps and IT teams on-demand access to SSH, RDP, Kubernetes, databases, websites, RemoteApp and VirtualApp endpoints through a web browser, built from separate core services and Enterprise components.
How do you install JumpServer?
The documented quickstart asks for a clean 64-bit Linux server with at least 4 CPU cores and 8 GB of RAM, then runs a curl pipeline that fetches quick_start.sh from the latest release and pipes it into bash. Afterwards you open https://<jumpserver-host>/ and sign in as admin with the password ChangeMe.
Is JumpServer free?
The main platform is open source under GPL-3.0, and the Tinker Windows application connector is annotated as free for the Community Edition. The Enterprise components, including the RDP, VNC and database protocol proxies and the recording transcoding worker, are not part of the open build.
Is JumpServer safe?
The README does not make a safety claim. The image does contain specifics worth weighing: host key checking is disabled in the bundled SSH config, UserKnownHostsFile points at /dev/null, and diffie-hellman-group1-sha1 plus ssh-rsa are re-enabled so the platform can reach older managed hosts. The admin account also ships with the documented password ChangeMe.
What is the difference between a VPN and a jump server?
A VPN grants network reach to the target network, while a jump server brokers a single session through one entry point. JumpServer takes the second approach, brokering sessions over its own connectors, KoKo for general protocol connections and Chen for web database access, and the enterprise edition adds Razor for RDP, Magnus for database protocols and Nec for VNC.
How does JumpServer compare with Guacamole?
JumpServer brokers connections through its own components, such as Lina, Luna, KoKo and Chen, and is positioned as a PAM platform rather than only a remote desktop gateway. Guacamole is a separate project that this repository does not cover.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/jumpserver-jumpserver)Star history chart for your README
[](https://hysenlabs.com/projects/jumpserver-jumpserver)Was this useful?