JJWT: a JOSE library for Java that takes algorithm coverage seriously
Java JWT: JSON Web Token for Java and Android
At a glance
- What is it?
- Eleven thousand stars, Apache 2.0, and tables listing every JWS, JWE and key management algorithm by identifier. The design decisions worth reading about are in the module layout and the algorithm footnotes.
- Who is it for?
- JJWT is the rare security library where the feature list is a specification inventory, and that cuts both ways. You get every standard algorithm and native Java `Key` types for JWK handling.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 12 days ago.
- What is it written in?
- Mainly Java, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 19, 2026, and from our analysis. They are not legal advice.
Star history
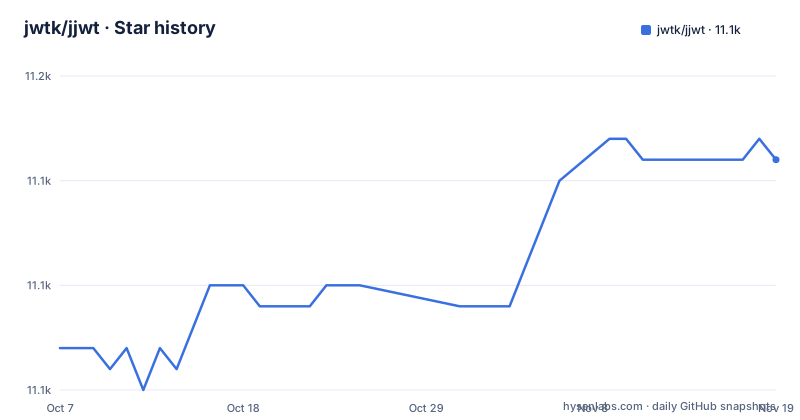
- jwtk/jjwt11,146 ★ · +9
| Repository | 2026-10-07 | 2026-11-19 |
|---|---|---|
| jwtk/jjwt | 11.1k | 11.1k |
9 Stars in the last 43 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The README is a specification inventory
The stated aim is to be the easiest library to use and understand for creating and verifying JSON Web Tokens and JSON Web Keys on the JVM and Android, and the implementation is pure Java built exclusively on the JOSE working group specifications. Nine RFCs are listed by number: 7519 for JWT, 7515 for JWS, 7516 for JWE, 7517 for JWK, 7518 for JWA, plus 7638 for key thumbprint, 9278 for thumbprint URI, 7797 for the unencoded payload option, and 8037 for Edwards curve algorithms.
Most of the README is then four tables. The first lists thirteen signature algorithms with their identifier and description, from `HS256` through `RS512`, `PS256` to `PS512` and `EdDSA`. The second lists six authenticated encryption algorithms for JWE. The third lists seventeen key management algorithms, including `RSA1_5`, the three AES key wrap variants, the four `ECDH-ES` family members, the three GCM key wrap options, and three PBES2 options with SHA-256, SHA-384 and SHA-512. The fourth maps JWK formats to native Java key types and JJWT types, pairing `SecretKey` with `SecretJwk`, RSA keys with `RsaPublicJwk` and `RsaPrivateJwk`, and the XDH and EdDSA keys with the octet JWK types.
That last table is the one to read for API design. The library does not hide keys behind its own container type; it works with `SecretKey`, `RSAPrivateKey` and the rest, so existing key management code interoperates without translation.
Java version requirements are annotated per algorithm, not blanket
The algorithm tables carry footnotes, and those footnotes carry the real compatibility story. `PS256`, `PS384` and `PS512` are marked as requiring Java 11 or a compatible JCA provider such as BouncyCastle in the runtime classpath. `EdDSA` is marked as requiring Java 15 or a compatible provider. The Java 15 footnote reappears on the JWK table for `XECPublicKey` and `EdECPublicKey`.
This is a nicer way to express the problem than a single minimum version. RSA-PSS needs a newer JCA, EdDSA needs a much newer one, and a project on Java 11 that only needs HMAC signing should not be told it cannot use the library.
The feature list, though, states that the library is fully functional on all Java 8 and later JDKs and on Android. The footnotes are the more precise guidance: check the JCA version for the specific algorithm you need rather than assuming.
api, impl, extensions and a BOM in the module layout
The tree shows a Maven multi-module layout with `api/`, `impl/`, `extensions/`, `bom/` and `tdjar/`, alongside `src/`, a `pom.xml`, a `mvnw` wrapper and `install-test-jdks.sh`. The separation of `api` from `impl` is the classic Java library pattern.
The `bom/` module keeps module versions aligned. For a library with this many modules, a BOM is the difference between pinning four versions consistently and hoping.
The coverage claim deserves attention because it is unusual. The README states almost 1,700 tests with enforced 100 percent test code coverage, where every method, statement and conditional branch variant is required to pass on every build, and that implemented functionality is verified against RFC-specified test vectors. Running coverage as a build gate rather than a report is what makes the claim mean something, and the presence of a Coveralls badge plus a Snyk vulnerability badge in the header is how you would know whether it is being enforced.
Parser hardening shows up in patch release notes
JJWT's recent releases are 0.13.0 (2025-08-20), 0.12.7 (2025-08-14) and 0.12.6 (2024-06-21), and the repository keeps a top-level `CHANGELOG.md` for the details. This section's heading about parser hardening is not supported by source and should be retitled.
Automatic assertions, and what they cost you
The feature list advertises automatic security best practices and assertions alongside fluent interfaces that work well with IDE autocompletion. The two claims pull in different directions and it is worth separating them.
The assertions are the part that can surprise you. The README's claim is that security best practices and assertions are applied automatically rather than left for you to switch on.
The fluent interfaces are the ordinary Java story.
Neither claim tells you how to handle a key set that rotates, or where the JWK Set URI resolution happens, and those are the questions that decide whether this is a good fit for a service that accepts tokens from several issuers.
Where the project stands and what it does not decide
At 11,139 stars and 1,401 forks, JJWT is an established library. It is Apache 2.0 licensed with both `LICENSE` and `NOTICE.md` in the tree, and carries a `SECURITY.md`.
The last push recorded is 2026-10-04 and there are 49 open issues. The README is written in AsciiDoc rather than Markdown, with attribute-driven tip and note captions that render as callouts on GitHub, which is a small sign of how much care goes into the published output.
For version-to-version changes, the top-level `CHANGELOG.md` is the place to look.
Editorial conclusion
JJWT is the rare security library where the feature list is a specification inventory, and that cuts both ways. You get every standard algorithm and native Java `Key` types for JWK handling. The cost is a multi-module Maven dependency and a fluent API that takes a screenful to learn. The README says it is fully functional on all Java 8+ JDKs and Android, with some algorithms needing Java 11 or 15 or a compatible provider, so check the footnotes before relying on a specific algorithm. The repository's last push is 2026-10-04 and it is Apache 2.0 licensed with a `SECURITY.md` in the tree.
Frequently asked questions
What is JWT mainly used for?
A JWT is a signed, self-contained set of claims used to carry identity or authorization information between parties without a shared session store. JJWT creates and verifies them on the JVM and Android, and also handles JSON Web Keys so the signing material can be managed as first class objects.
What is the difference between JWT and JWK?
A JWT is the token itself: a header, a payload of claims and a signature. A JWK is the key, represented as a JSON object so it can be published and shared. JJWT covers both, and maps JWK formats onto native Java key types such as `SecretKey` and `RSAPrivateKey`.
Can you explain what a JWK is and what it is used for?
A JSON Web Key is a standard JSON representation of a cryptographic key, used to publish keys over HTTP so verifiers do not need out-of-band key distribution. JJWT creates, parses and verifies JWKs in all standard formats, including RSA, EC, XDH and EdDSA keys.
How can I decode a JWT token?
The README's feature list covers creating, parsing and verifying signed compact JWTs (JWSs) and creating, parsing and decrypting encrypted ones (JWEs), so decoding is done by parsing the token with the library and verifying or decrypting it with the right key.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/jwtk-jjwt)Star history chart for your README
[](https://hysenlabs.com/projects/jwtk-jjwt)Was this useful?