Keycloak: A Full-Featured Identity Server with a Heavy Operational Footprint
Open Source Identity and Access Management For Modern Applications and Services
At a glance
- What is it?
- Keycloak is an open source identity and access management server that handles authentication, user federation, and fine-grained authorization. It is powerful but demands serious operational attention, and this review covers what you need to know before adopting it.
- Who is it for?
- Adopt Keycloak if you need a self-hosted, standards-based IAM server with broad protocol support and a large community, and you have the operational capacity to run and tune a Java service. Do not adopt it if you want a lightweight, low-maintenance solution or have minimal in-house security expertise.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Java, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
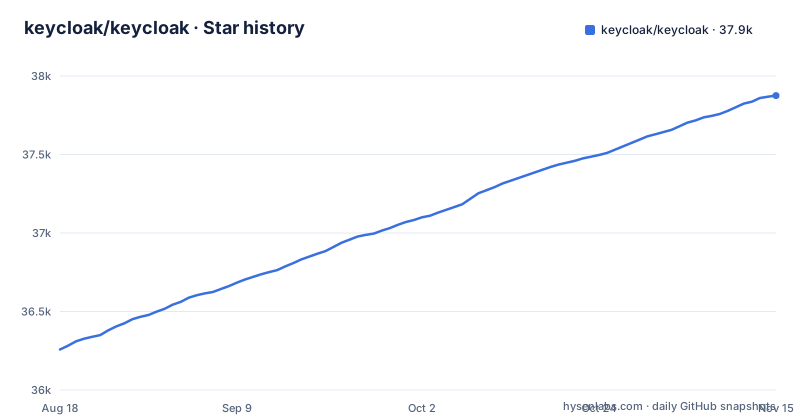
- keycloak/keycloak37,875 ★ · +1,617
| Repository | 2026-08-18 | 2026-11-15 |
|---|---|---|
| keycloak/keycloak | 36.3k | 37.9k |
1,617 Stars in the last 89 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What Keycloak Solves and Who Needs It
Keycloak addresses a common problem: adding authentication to applications without building a user store or login flow from scratch. The README states it adds authentication to applications and secures services with minimum effort, and that you do not need to deal with storing users or authenticating them. That is the core promise. The project targets developers and organizations that need a centralized identity server for multiple applications. It is not a library you embed; it is a standalone server that your apps talk to. The intended users are teams that want user federation and fine-grained authorization without implementing those themselves. If you have one small app and a handful of users, Keycloak is overkill. But if you have several services that need a single sign-on experience, it is a serious candidate.
The Architecture: A Server, Not a Library
The repository is a Java project. The README describes Keycloak as providing user federation, strong authentication, user management, and fine-grained authorization. The actual mechanism is a server that sits between your applications and your user directory. Applications delegate authentication to Keycloak, which then issues tokens or assertions. Keycloak acts as the identity provider. It can federate users from existing directories, which means it does not force you to migrate your user base. It also supports strong authentication, which typically means multi-factor methods. The fine-grained authorization part suggests you can define policies and permissions beyond simple authentication. The server is designed to be a central hub, so you configure clients and users in one place. This is a different model from embedding authentication logic in each app.
Getting Running: Commands and Config
The README gives two ways to start Keycloak. First, download the distribution and run bin/kc.sh start-dev on Unix-like systems or bin/kc.bat start-dev on Windows. Second, use the Docker image with docker run quay.io/keycloak/keycloak start-dev. The start-dev flag indicates a development mode, which is not for production. There is no mention of production configuration in the README, so you must consult the documentation for that. The startup process is a Java server, so it will consume memory and CPU. Do not use start-dev in production. The actual configuration keys for production are not in the README; you would need to read the full documentation.
The Real Limitation: Operational Weight and Complexity
Keycloak is not a lightweight tool. It is a Java server, so you need to plan for infrastructure. You must manage the database schema, backups, and upgrades. The project has a nightly release and recent stable versions like 26.8.1, which shows active development. That also means the upgrade path is not trivial; major versions may change configuration formats. The start-dev mode is easy, but moving to production requires understanding realms, clients, and security settings. If you are a small team without dedicated IAM experience, the learning curve is steep. The README does not offer a managed option, so you are on your own for uptime and patching. This is the wrong tool if you want a zero-maintenance identity solution.
Alternatives: Different Approaches to Identity
A common alternative is a hosted identity service like Auth0 or Okta. The difference is fundamental: those are SaaS offerings, so you do not run a server. You get a management console and SDKs, but you hand over your user data and pay per active user. Keycloak is self-hosted, which gives you full control over data and no per-user fees, but you bear the operational cost. Another alternative is a simple OIDC provider embedded in your app, which is less feature-rich but simpler to run. The trade-off is clear: Keycloak is a heavyweight, all-in-one server, while alternatives trade features for simplicity or external hosting. Your choice depends on whether you value control over convenience.
Maintenance and Licensing: What the Repo Tells You
Keycloak is licensed under Apache-2.0, which is permissive. That means you can use, modify, and distribute it freely, with attribution. For maintenance, the project has a clear contribution process and a code of conduct. There are mailing lists and Slack channels for support, but those are community-driven. The release history shows a nightly build and stable releases, so the project is actively maintained. However, active development means you need to track releases and plan upgrades. The README does not specify a support contract, so you rely on community help. For production, you should budget time for patching and testing. The security vulnerability reporting process is mentioned, which is good, but it implies you must monitor for advisories yourself.
Final Verdict: Who Should and Should Not Adopt It
Keycloak is a strong fit for organizations that need a self-hosted, standards-based IAM solution and have the operations team to run it. It is a poor fit for small projects or teams that want a quick, low-maintenance login. The README's promise of minimum effort is misleading; the effort is shifted to deployment and administration. Before adopting, verify the current stable release and its documentation, because the project moves fast. Test the startup and admin console in your environment to see if the operational cost is acceptable. Also, check whether your user federation needs are covered. If you need SAML and OIDC out of the box, Keycloak is a solid choice. If you prefer a managed service or a lighter library, look elsewhere. The decision hinges on your capacity to run a Java server, not on the feature list.
Editorial conclusion
Adopt Keycloak if you need a self-hosted, standards-based IAM server with broad protocol support and a large community, and you have the operational capacity to run and tune a Java service. Do not adopt it if you want a lightweight, low-maintenance solution or have minimal in-house security expertise. Before committing, verify your required identity protocols (OIDC, SAML, or both), assess your user federation needs, and test the admin console and startup time in your environment. Also, check the current release version and the upgrade path from your chosen starting point, as the project evolves quickly and major version changes can affect configuration.
Frequently asked questions
What is Keycloak used for?
It is open source identity and access management for modern applications and services, covering user federation, strong authentication, user management, and fine-grained authorization, so you do not have to store users or authenticate them yourself.
Is Keycloak an OAuth server?
The README never names OAuth or OIDC anywhere. What the tree shows is saml-core and saml-core-api modules for SAML, and client libraries published separately in keycloak-client, so confirm protocol coverage on the documentation site rather than from this repository.
Is Keycloak an SSO provider?
The README does not use the term single sign-on at all. It does place the Java adapters in this repository, while the Node.js adapter and the client libraries live in separate repositories, so the single sign-on wiring depends on which adapter you choose.
Is Keycloak free?
Yes. The repository is licensed under Apache-2.0 and points to the Apache License, Version 2.0. No paid edition, feature tier, or support subscription is described in the README, so paid support is not something the repository promises.
how to install keycloak
Download the distribution from the website, unzip it, and run bin/kc.[sh|bat] start-dev, or run docker run quay.io/keycloak/keycloak start-dev. Building from source means following the docs/building.md guide, and the README sets no version prerequisite for either path.
Official sources
Where this project is recommended
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/keycloak-keycloak)Star history chart for your README
[](https://hysenlabs.com/projects/keycloak-keycloak)Was this useful?