KingOfBugBountyTips: A Command Collection for Bug Bounty Recon
Our main goal is to share tips from some well-known bughunters. Using recon methodology, we are able to find subdomains, apis, and tokens that are already exploitable, so we can report them. We wish to influence Onelinetips and explain the commands, for the better understanding of new hunters..
At a glance
- What is it?
- KingOfBugBountyTips is a curated set of shell one-liners, YAML templates and helper scripts for reconnaissance and vulnerability discovery. It is a reference you copy commands out of, not a tool you install and run as a program.
- Who is it for?
- KingOfBugBountyTips suits hunters who already know their way around subfinder, httpx, nuclei and the rest of the recon toolchain and want a place to copy working command lines from. It is the wrong choice if you need a single installable program with a version number, a changelog and a supported upgrade path, because the repository ships no releases and no licence file.
- Can I use it commercially?
- Not without permission. GitHub finds no licence file in the repository, and without a licence all rights are reserved by default: you may read the code but not reuse it. Check the README, or ask the authors, before using it.
- Is it still maintained?
- Yes. The repository last received commits 32 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 22, 2026, and from our analysis. They are not legal advice.
Star history
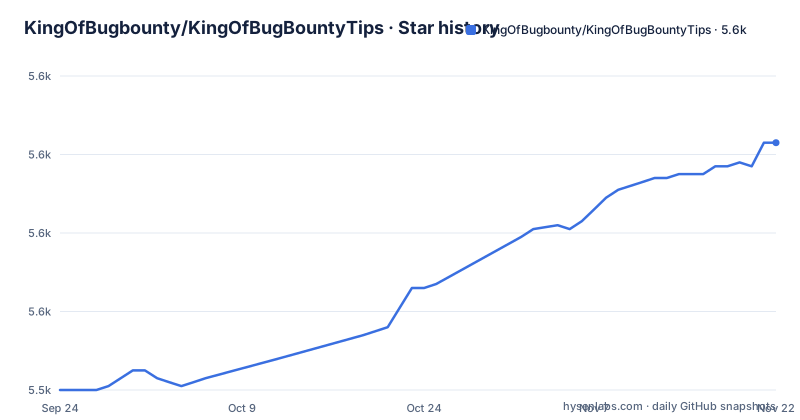
- KingOfBugbounty/KingOfBugBountyTips5,603 ★ · +63
| Repository | 2026-09-24 | 2026-11-22 |
|---|---|---|
| KingOfBugbounty/KingOfBugBountyTips | 5.5k | 5.6k |
63 Stars in the last 59 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What KingOfBugBountyTips Actually Is
The README describes the project as a collection of tips from well-known bug hunters, built around reconnaissance methodology: finding subdomains, APIs and tokens that are already exposed so they can be reported. That description is accurate in the sense that the repository is mostly text. The main artifact is a long README organised as a table of contents with sections for subdomain enumeration, JavaScript recon, XSS detection, SQL injection, SSRF and SSTI, web crawling, parameter discovery, content discovery, Nuclei scanning, API security testing and cloud security. A smaller set of files sits alongside it: YAML templates named OFJAAAH-cpanelXSS.yaml and graphql-OFJAAAH.yaml, a swagger.json and swagger.yaml pair, a Go file called resolvhtml.go, Python scripts named bot.py, bottest.py and DoD crawl.py, plus a DoD Domains.txt scope file and a docker2.yaml. The audience is people who already run command-line recon tools and want a bank of command lines to draw from. The repository does not present itself as a framework, a scanner or a service. If you arrive expecting a binary, you will not find one.
How the One-Liners Fit Together as a Workflow
There is no engine here, so the mechanism is the shell pipeline. Each tip is a command that takes the output of one tool and pipes it into the next, and the README groups those commands by recon stage rather than by tool. Subdomain enumeration feeds a list of hosts into HTTP probing, probing output feeds crawling and parameter discovery, and the resulting URLs feed the scanning sections. The DoD scope block is the clearest example of the pattern: a bbrf command registers wildcard domains so later commands can filter against them.
bbrf inscope add '*.af.mil' '*.army.mil' '*.marines.mil' '*.navy.mil' '*.spaceforce.mil' '*.ussf.mil' '*.pentagon.mil' '*.osd.mil' '*.disa.mil' '*.dtra.mil' '*.dla.mil' '*.dcma.mil' '*.dtic.mil' '*.dau.mil' '*.health.mil' '*.ng.mil' '*.uscg.mil' '*.socom.mil' '*.dds.mil' '*.yellowribbon.mil'The README labels this as BBRF scope for all DoD domains under a heading that says 19 domains, while the command itself lists twenty wildcard entries. Because the commands are independent, you can adopt one section and ignore the rest. That is also the weakness: nothing validates that the tools named in a command are installed, that their flags still exist, or that the pipeline is safe to point at a production host. The repository is a recipe book with no test kitchen.
Getting Started with the Repository and Its YAML Templates
The README points to a Quick Start section, but the repository has no package to install and no setup script. The practical first step is cloning it and reading the table of contents, then picking one section that matches a target you are authorised to test. Cloning is the only command the layout guarantees works.
git clone https://github.com/KingOfBugbounty/KingOfBugBountyTips.git
cd KingOfBugBountyTips
ls
The listing shows the files described above: the README, the two OFJAAAH YAML templates, swagger.json and swagger.yaml, resolvhtml.go, the Python scripts, DoD Domains.txt and docker2.yaml. From there, the most self-contained artifact is the cpanel XSS template, which is a Nuclei template. If you already have nuclei installed, you can point it at an authorised target and let the template do the matching; read the YAML before running it. The Go file resolvhtml.go is a separate build step if you want to compile it, and the Python scripts are invoked directly.
Where the Repository Is Thin: No Licence, No Releases, No Rollback
The most concrete limitation is legal rather than technical. The licence field is unknown, and the README's badge for the licence links to a LICENSE file that the repository listing does not show at the top level. Until you confirm what terms apply, you cannot assume you may redistribute the content, fold it into an internal playbook, or ship the YAML templates inside a commercial product. The Security Notice is explicit that the material is for educational and authorised testing only, and it lists prohibited uses including unauthorized testing, out-of-scope testing and denial-of-service attacks. That is a usage policy, not a licence grant.
The second limitation is maintenance. There are no releases, so there is no version to pin and no changelog to read when a command breaks. The last push was on 2026-10-21, which is recent enough that the collection is being touched, but a push date tells you nothing about whether an individual one-liner was retested against the current version of the tool it calls. Command-line flags in recon tools change, and a copied pipeline that silently stops matching is worse than no pipeline, because you may read an empty result as a clean target. The README does not document rollback, deprecation or a compatibility matrix.
Alternatives That Take a Different Approach
The closest alternative in spirit is a recon framework rather than a tip list. ProjectDiscovery's toolchain, which the README already assumes you have through its Nuclei section, is the opposite design: subfinder, httpx and nuclei are versioned binaries with documented flags and template update mechanisms. The difference is where the maintenance burden sits. With KingOfBugBountyTips you copy a command and own it forever; with a framework you install a binary and inherit its release cycle, its breaking changes and its update path. For a solo hunter who wants to understand each step, copying is instructive. For a team that needs the same scan to produce the same result next quarter, a versioned tool is the safer base.
A second alternative is a general-purpose cheat sheet or methodology document. Those share the copy-and-adapt model but usually carry a licence and a stated scope, which this repository does not. The trade-off runs the other way too: a cheat sheet rarely ships runnable artifacts, whereas this repository includes Nuclei templates, a Go resolver and Python scripts you can execute today. The value and the risk come from the same property, which is that the content is executable and unversioned.
Maintenance Cost and What Adoption Looks Like in Practice
Adopting this repository means adopting an ongoing verification habit. Every command you lift has to be checked against the installed version of the tool it invokes, because the repository will not tell you when a flag was renamed. The scripts under the root carry the same burden: bot.py, bottest.py and DoD crawl.py have no documented dependency list in the README, so you read the imports before the first run. The YAML templates are the easiest to maintain because Nuclei templates are data, not code, and a template that fails to match fails loudly in most cases.
The upgrade story is simply a git pull, and there is no release to compare against, so you cannot tell what changed between two pulls without reading the diff. If you fork the repository to pin a known-good state, you take on the maintenance yourself. On licence, treat the unknown status as a blocker for anything beyond personal, authorised use until you locate terms you can rely on. That is a factual gap in the repository, not a legal opinion.
Editorial conclusion
KingOfBugBountyTips suits hunters who already know their way around subfinder, httpx, nuclei and the rest of the recon toolchain and want a place to copy working command lines from. It is the wrong choice if you need a single installable program with a version number, a changelog and a supported upgrade path, because the repository ships no releases and no licence file. Before you run anything, check the authorization language in the Security Notice, confirm each command against the tool it invokes, and verify whether the individual scripts under the repository root, such as bot.py and DoD crawl.py, carry their own terms.
Frequently asked questions
Is bug bounty legal or illegal?
The repository's Security Notice states that the material is for educational and authorised testing only, and that you should always obtain proper authorization before testing. It lists authorised bug bounty programs, authorised penetration testing with written permission, personal lab environments and the DoD VDP program as permitted use cases, and unauthorized or out-of-scope testing as prohibited.
How hard is it to get into bug bounty with KingOfBugBountyTips?
The repository description says the collection is meant to explain commands for the better understanding of new hunters, and it groups tips by recon stage from subdomain enumeration through to API and cloud testing. The commands assume you already have tools such as Nuclei and bbrf available, so some familiarity with the command line is assumed.
Does KingOfBugBountyTips include a bug bounty recon cheat sheet?
Yes. The README is organised as a table of contents covering subdomain enumeration, JavaScript recon, XSS detection, SQL injection, SSRF and SSTI, web crawling, parameter discovery, content discovery, Nuclei scanning, API security testing and cloud security. It also has sections for new oneliners and earlier oneliners, plus a search engines section for hackers.
What tools do I need installed before using the KingOfBugBountyTips one-liners?
The README has a Required Tools section, and the DoD scope example uses bbrf, so the commands assume a recon toolchain is already present. Check the Required Tools section and confirm each named tool exists on your system before running a pipeline.
Is there an official KingOfBugBountyTips release or version to pin?
The repository has no published GitHub releases, so there is no version number or changelog to pin against. The last push was on 2026-10-21, and the repository has no documented rollback or compatibility matrix, so a git pull is the only upgrade path.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/kingofbugbounty-kingofbugbountytips)Star history chart for your README
[](https://hysenlabs.com/projects/kingofbugbounty-kingofbugbountytips)Was this useful?