KubeKey 4.x: A Task Flow Engine That Happens to Install Kubernetes
Install Kubernetes, and related cloud-native add-ons, it supports all-in-one, multi-node, and HA 🔥 ⎈ 🐳
At a glance
- What is it?
- KubeKey has grown from a Kubernetes installer into a general-purpose task execution tool with playbooks, roles, and multiple connection backends. The 4.x line is the one to evaluate if you need repeatable cluster operations beyond the initial install.
- Who is it for?
- Adopt KubeKey if you manage Kubernetes clusters and want a single binary that handles install, node addition, deletion, certificate renewal, and offline artifacts through a YAML-driven playbook system. Skip it if you need a mature UI (the web interface is not yet open), if you prefer a declarative GitOps model like Cluster API, or if your environment requires a fully supported commercial distribution.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
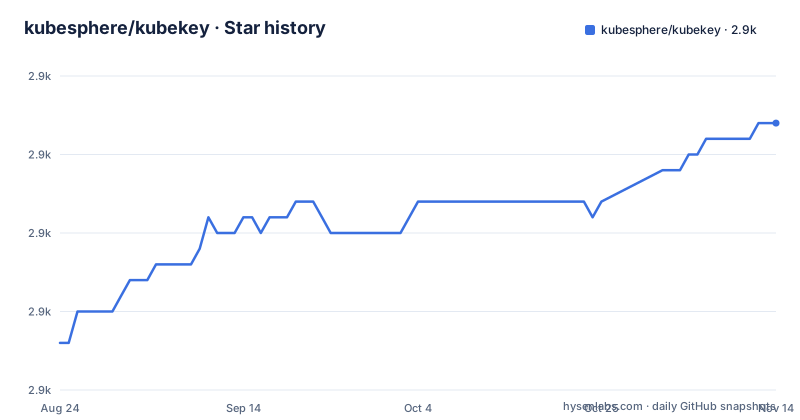
Star history
- kubesphere/kubekey2,872 ★ · +14
| Repository | 2026-08-24 | 2026-11-14 |
|---|---|---|
| kubesphere/kubekey | 2.9k | 2.9k |
14 Stars in the last 82 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
From Installer to Task Engine
KubeKey started as a Kubernetes installation tool, and the README still leads with that. But the 3.x comparison section makes a different claim: the project has expanded from a Kubernetes lifecycle management tool into a task execution tool. The flow design is explicitly inspired by Ansible. That shift matters. If you only need to stand up a cluster, older KubeKey versions or simpler tools like kubeadm will do. KubeKey 4.x is for people who want a repeatable, template-driven way to run a sequence of operations across nodes, whether that sequence is creating a cluster, adding nodes, renewing certificates, or exporting offline artifacts. The target user is an operator who manages multiple clusters and wants the same playbook to work on each one.
How KubeKey Structures Work: Project, Playbook, Role, Task
The framework documentation lists four core concepts: project, playbook, role, and task. A project is the top-level unit, likely a directory or config that holds the playbooks. A playbook defines a sequence of roles, and a role groups related tasks. A task is the smallest execution step. This is a direct parallel to Ansible's inventory, playbook, role, and task hierarchy. The template syntax and variables are documented separately, which means you can parameterize node addresses, credentials, and versions. The README says task templates can be managed via git or local files, so you can version your playbooks like code. The connection methods are local, ssh, kubernetes, and prometheus. That last one is unusual for an installer; it suggests KubeKey can read cluster state from Prometheus, which fits the cloud-native batch management claim. The documentation is thin on how prometheus connection works, so treat that as a feature to verify before relying on it.
Getting It Running: Commands and Modes
The quick start offers two paths. The command line path is one command: ./kk create cluster. That command presumably reads a default config, but the README points to a configuration reference for details. The web UI path requires two flags: ./kk web --schema-path web-installer/schema --ui-path web-installer/dist. This only works after v4.0.0. The release tarball contains more than the kk binary. The web-installer.tgz holds dist resources, task template files (host-check.yaml, kubernetes, kubesphere), schema config files, and a README. There is also package.sh, an offline package build script. So the distribution is designed for both online and offline installs. The script installer is curl -sfL https://get-kk.kubesphere.io | sh -. That is a standard pattern, but you should inspect the script before piping it to a shell, as with any such installer.
Playbooks Cover the Lifecycle, Not Just Install
The documentation lists playbooks for create_cluster, delete_cluster, add_nodes, delete_nodes, certs_renew, artifact_export, precheck, and init_os. That is a practical set. Certificate renewal is a task that often gets ignored until it breaks, and having a dedicated playbook is useful. The artifact_export playbook ties into the offline installation story: you can build an offline package on one machine and deploy it elsewhere. The precheck playbook suggests you can validate a host before committing to a full install, which is a good safety net. The init_os playbook implies you can standardize OS settings as part of the same workflow. The combination of these playbooks means KubeKey is not a one-shot installer; it is a maintenance toolkit. The README also lists an image registry installation doc, which is a common need for air-gapped clusters.
The Web UI Is a Promise, Not a Product
The README says the UI page is not yet open. The command to launch it exists, and the release tarball includes web-installer resources, but the feature is marked as advanced and unavailable. That is a genuine limitation. If you are evaluating KubeKey for a team that prefers a graphical interface, you will be disappointed. The command line is the only reliable path today. The UI also depends on a schema path and a dist path, which means even when it opens, it will be a static front-end served by the kk binary, not a full management plane. For comparison, Rancher provides a complete UI for cluster management, but it is a much heavier system. KubeKey's UI, once available, is likely to be a thin wrapper over the same playbooks, not a separate control plane. That could be an advantage for simplicity, but it is not something you can use now.
Limitations and Wrong Tool Scenarios
The most obvious limitation is the UI unavailability, but there are deeper constraints. The README does not mention support for Windows nodes, and the connection methods are node-oriented, so this is a Linux-focused tool. If your cluster spans Windows or needs fine-grained per-node configuration beyond what playbooks allow, KubeKey will feel rigid. The task flow design borrows from Ansible, but it is not Ansible. You cannot reuse existing Ansible roles, and the module ecosystem is smaller. The README says the flow design refers to Ansible, not that it is compatible. If you already have a large Ansible investment for cluster provisioning, switching to KubeKey means rewriting those playbooks in its own syntax. Another limitation is the alpha status of recent releases. The latest releases include v4.0.7-alpha.1 and v4.0.7-alpha.0, with a stable v4.0.6. Alpha releases signal active development but also instability. Production users should stick to the latest stable tag and verify that their Kubernetes version is listed in the component versions doc.
Alternatives: kubeadm and Cluster API
The most direct alternative is kubeadm, the Kubernetes community's own bootstrap tool. kubeadm handles the initial cluster creation and token management, but it does not provide a playbook system, node addition workflows, or certificate renewal as a high-level task. You would script those yourself with shell or Ansible. KubeKey gives you those as built-in playbooks, which is the main reason to choose it over raw kubeadm. Another alternative is Cluster API, a Kubernetes project that manages cluster lifecycle declaratively through custom resources. Cluster API uses a controller model: you define a cluster spec, and a controller reconciles the actual state. KubeKey is imperative in the sense that you run playbooks on demand. If you want GitOps-style management where cluster changes happen automatically from a desired state, Cluster API is the better fit. If you want a simple CLI that you run when you need to change something, KubeKey is closer to that workflow.
Maintenance and Upgrade Cost
The repository shows active maintenance with regular releases, including multiple alpha releases in a single month. That signals a fast-moving project, which is good for feature development but a cost for adopters. You will need to track version compatibility between kk, Kubernetes, and the add-ons. The README provides a component versions doc, so you can check that, but it is not a guarantee. The offline package script (package.sh) suggests that building your own artifacts is expected, which adds an initial setup cost but reduces runtime dependency on external registries. The license is Apache-2.0, which is permissive for commercial use, but you should read the license text yourself if you plan to redistribute modified binaries. The documentation is organized but not exhaustive; the framework docs cover syntax and variables, but the depth of each page is unknown from the README alone. Plan to spend time reading the docs before your first playbook authoring session.
Editorial conclusion
Adopt KubeKey if you manage Kubernetes clusters and want a single binary that handles install, node addition, deletion, certificate renewal, and offline artifacts through a YAML-driven playbook system. Skip it if you need a mature UI (the web interface is not yet open), if you prefer a declarative GitOps model like Cluster API, or if your environment requires a fully supported commercial distribution. Before adopting, verify that your target OS and Kubernetes version appear in the component compatibility table, and confirm that the connection method you need (local, ssh, kubernetes, or prometheus) matches your cluster topology. The 4.x branch is under active development with alpha releases, so pin a specific version and test the playbooks in a non-production environment first.
Frequently asked questions
How do I install KubeKey?
Either download a binary from the release page, or run curl -sfL https://get-kk.kubesphere.io | sh -, which unpacks a kubekey binary called kk, an interface archive containing interface resources, task templates and schema files, and a script for building an offline package.
Does KubeKey have a web interface?
Yes, from version 4.0.0 onward, started with ./kk web taking a schema path and an interface path. Note that the feature comparison in the README still lists the interface as not yet open, because that section is headed as the changes in 3.x.
How does KubeKey create a cluster from the command line?
With a single command, ./kk create cluster, which the README gives as the whole command-line quick start without further flags.
What is KubeKey's task model?
Four levels, documented as project, playbook, role and task, with separate pages for template syntax and variables. The feature comparison says the flow design refers to Ansible, and the module file includes a Go templating library.
Which operating systems and architectures does KubeKey publish?
The readme's contents table documents one artifact, an archive named for linux-amd64, and does not mention arm64, macOS or Windows. The project itself is built in Go and the readme states it installs Kubernetes and related cloud-native add-ons.
Can KubeKey renew certificates and build an offline install?
Yes. The documentation lists playbooks for renewing certificates and for exporting an offline artifact, alongside separate pages for online and offline installation and for dependency packages.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/kubesphere-kubekey)Star history chart for your README
[](https://hysenlabs.com/projects/kubesphere-kubekey)Was this useful?