lcobucci/jwt: A PHP Library for JWT and JWS That Stays Close to RFC 7519
A simple library to work with JSON Web Token and JSON Web Signature.
At a glance
- What is it?
- lcobucci/jwt is a PHP library for creating and validating JSON Web Tokens and JSON Web Signatures. It targets developers who need RFC 7519 compliance without extra framework baggage, but its documentation is sparse.
- Who is it for?
- Adopt lcobucci/jwt if you need a PHP library that implements JWT and JWS per RFC 7519 with BSD-3-Clause licensing. It suits projects that already use Composer and want a lightweight dependency.
- Can I use it commercially?
- Yes. BSD-3-Clause is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly PHP, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
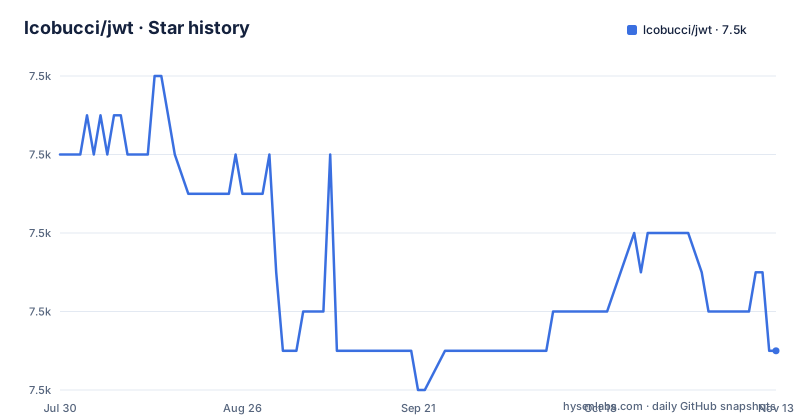
Star history
- lcobucci/jwt7,479 ★ · -5
| Repository | 2026-07-30 | 2026-11-13 |
|---|---|---|
| lcobucci/jwt | 7.5k | 7.5k |
-5 Stars in the last 106 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What lcobucci/jwt Solves for PHP Developers
The project is maintained, with the last push on November 2, 2026, and recent releases including 5.6.1 on October 10, 2026. The default branch is 6.0.x, which suggests active development toward a new major version. The README does not describe the API in detail, so you must consult the external documentation. That is a limitation for quick adoption, but the library's focus on RFC 7519 gives you a clear standard to verify against.
How the Library Works: Token Creation and Validation
The key point is that the library does not reinvent the token format; it implements the spec. That is both a strength and a constraint. It means interoperability with other JWT implementations, but it also means you must follow the RFC's rules, such as base64url encoding and JSON serialization.
Getting Started: Installation and Basic Configuration
Installation is straightforward via Composer. The README gives a single command: 'composer require lcobucci/jwt'. This is the only concrete setup step mentioned. There is no mention of a configuration file or environment variables, which suggests that the library is used directly in code rather than through a service provider. After installation, the README points to the external documentation for usage. The lack of a quick-start example in the README is a notable gap for a library that claims simplicity. However, the installation command is clear, and the package is available on Packagist, so the dependency management is standard. The library has a stable version 5.6.1 and a pre-release 6.0.x branch, which means you should specify a version constraint in your composer.json to avoid unexpected breaking changes. For example, you might use '^5.6' for stability, but the README does not advise on this.
Licence and Maintenance Considerations
The library is licensed under BSD-3-Clause, which is permissive and allows commercial use, modification, and redistribution with attribution. This is a low-license-risk dependency for most projects. The project is actively maintained, with a recent release in October 2026, so you can expect bug fixes and security updates. The default branch is 6.0.x, indicating that a new major version is in the works. Major version changes in a library like this can introduce breaking API changes, especially if the token handling internals are refactored. The maintenance cost is moderate: you need to track releases and test your code against new versions. The documentation is hosted on ReadTheDocs, but the README does not specify the exact documentation version for the stable release. The homepage points to the 'stable' version, while the README links to 'latest', which could be a different version. This discrepancy is a minor issue but something to verify when reading the docs.
Limitations and When This Library Is the Wrong Choice
The most obvious limitation is the lack of detailed documentation in the README. The README is minimal, with only installation instructions and links. If you are a developer who prefers to learn from the README, you will need to visit the external documentation, which may or may not be complete. If you need to support token revocation, you will have to implement it on top of this library, as JWT is stateless by design. The library is also not a good fit for projects that require a full authentication stack, such as login endpoints, user sessions, or role-based access control. For those, you would need a framework like Symfony or Laravel with its security bundle. Finally, the default branch 6.0.x suggests that the 5.x series is legacy, so if you adopt the stable 5.6.1, you may eventually face a migration. If you need cutting-edge features, you might need to use the 6.0.x branch, which is not yet stable and may have unresolved issues.
Alternatives and How They Differ
A common alternative is firebase/php-jwt, which is another PHP library for JWT. Another alternative is the LexikJWTAuthenticationBundle for Symfony, which integrates JWT with Symfony's security system. That bundle provides authentication listeners, user providers, and token storage, which lcobucci/jwt does not. If you are using Symfony, the bundle is a more complete solution. The choice depends on your framework and your need for control.
Editorial conclusion
Adopt lcobucci/jwt if you need a PHP library that implements JWT and JWS per RFC 7519 with BSD-3-Clause licensing. It suits projects that already use Composer and want a lightweight dependency. Skip it if you require extensive documentation in the README, or if your team prefers a framework-integrated solution. Before adopting, verify the exact version you install, since the default branch is 6.0.x but the latest release is 5.6.1, and test token creation and validation against your specific algorithms and claims. Also confirm that the ReadTheDocs documentation at the stable link matches the version you use, as the README points to 'latest' while the homepage points to 'stable'.
Frequently asked questions
What does JWT stand for?
JSON Web Token. This project is a PHP library for working with JSON Web Tokens and JSON Web Signatures, described as based on RFC 7519. It is published on Packagist as lcobucci/jwt and installed with composer require lcobucci/jwt, with BSD-3-Clause licensing.
Which version of lcobucci/jwt will Composer install?
The stable one. The latest listed release is 5.6.1 from 2026-10-10, while the repository's default branch is 6.0.x, and the README carries separate Packagist badges for the latest stable and the unstable version. So the 6.x line is the branch under development rather than what a plain require installs.
Where do I find the lcobucci/jwt documentation?
On readthedocs, at lcobucci-jwt.readthedocs.io. The README links the latest documentation under the /en/latest/ path while the project homepage is the /en/stable/ path, so check which one matches the version you installed. The pages are built from this repository with mkdocs, configured through mkdocs.yml and .readthedocs.yaml.
Will version 6 of lcobucci/jwt break my code?
The repository carries a configuration file for a backward compatibility checker, which is the project's own answer to that question and a better one than a changelog because it describes the public API surface rather than intent. Before moving from 5.x to 6.0.x, read that file.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/lcobucci-jwt)Star history chart for your README
[](https://hysenlabs.com/projects/lcobucci-jwt)Was this useful?