LessPass: A Stateless Password Manager With No Vault to Sync
:key: stateless open source password manager
At a glance
- What is it?
- LessPass generates passwords from a master password and the login you fill in for a site instead of storing an encrypted vault. The design removes the vault and the sync that goes with it.
- Who is it for?
- Adopt LessPass if you want a password generator with no vault to sync and you are comfortable that one master password is the thing you must remember. Do not adopt it for shared team credentials or for accounts whose password rules you cannot encode in the generator options.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 25 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
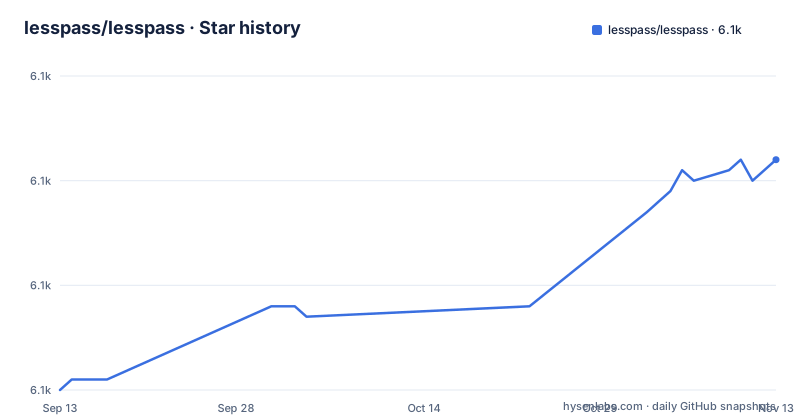
Star history
- lesspass/lesspass6,082 ★ · +22
| Repository | 2026-09-13 | 2026-11-13 |
|---|---|---|
| lesspass/lesspass | 6.1k | 6.1k |
22 Stars in the last 61 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The Vault Is the Thing LessPass Removes
Most password managers store an encrypted blob and synchronize it. LessPass does not store your passwords. The README describes it as a stateless password manager and tells you to stop synchronizing an encrypted vault: remember one master password to access your passwords, anywhere, anytime. The inputs are the master password plus the details of the account you are generating for, which in the README's extension workflow means opening it on the site's password field and filling in the login and master password. Because the output is computed rather than retrieved, there is nothing to sync between devices and no server that has to be reachable when you need a password.
That shifts the threat model. An attacker who compromises a vault server gets ciphertext and has to break the vault password. An attacker who knows your master password and the profile fields can compute the same passwords, because the output is computed from those inputs. The project credits an original idea from masterpassword app. This is the trade you are making, and it is worth stating plainly rather than treating statelessness as a pure upgrade.
Who This Fits, and Who It Quietly Excludes
The natural user is someone with many personal accounts, a few devices, and no appetite for running a sync server. The README points at browser extensions for Chrome and Firefox, a mobile application for iOS, Android and FDroid, a CLI installable with pip, and the generator on the website. The repository is TypeScript, licensed GPL-3.0, and the mobile package is bi-licensed under the Mozilla Public License Version 2 and the GNU GPLv3.
Three groups should look elsewhere. Anyone who needs to share a credential with a colleague cannot, because there is no vault to share and the other person would need the master password. Anyone who must rotate a password on a schedule has a problem, because the generated value only changes when an input changes. Anyone whose sites enforce password rules the generator cannot express will find the output rejected. The README does not document the option set, so check the generator's own controls before assuming a given policy is reachable.
Deterministic Derivation, Not a Database
The mechanism is a pure function. Given the master password and the profile fields, the generator produces the same string every time. The README's extension walkthrough shows the whole data flow: focus the password field on the site, press Ctrl plus Shift plus L (Command plus Shift plus L on a Mac), fill in the login and master password, press Enter, and the password lands in the clipboard. Press esc and paste. Nothing is written to a vault and nothing is fetched, which is why the same inputs on a phone and on a laptop produce the same password without a network round trip.
Getting the CLI Running
The README gives one installation path for the terminal, using pip:
python3 -m pip install --user lesspass lesspass --help
The --user flag installs into your home directory rather than the system Python, which is the right default on distributions that mark the system interpreter as externally managed. The README stops at --help and does not print the option list, so the exact flags for site, login, counter and character set are not verifiable from the README. Run lesspass --help before scripting anything around it, and treat the help output as the source of truth for flag names.
For the browser, the README points at the Chrome and Firefox extension listings rather than a source build, and the mobile apps are on the App Store, Google Play and FDroid. If you want the connected server rather than the plain generator, the README states that LessPass Server is reserved for existing users and that new registrations are no longer possible. New users who want that mode must self-host. The README says a DigitalOcean deployment guide is planned and that the current setup uses App Platform, so the self-hosting path is documented as a todo rather than as finished instructions.
The Counter Problem and Other Failure Modes
The sharpest limitation is that a stateless generator cannot recover from a lost master password. There is no reset email, no recovery phrase, no vault backup. If you forget it, the passwords are gone, and the sites have to be reset one by one through their own recovery flows.
The second failure mode is the one that catches people in practice: a site whose password policy changes after you registered. If it later requires a symbol the generator was not configured to include, or a length outside the range you used, the deterministic output no longer satisfies the form, and you cannot simply regenerate the same password with different options, because different options produce a different string. You are back to a password reset.
Third, the connected mode is not a neutral extra. The README reserves the hosted server for existing users and warns that third-party server implementations are available but that it cannot guarantee they fully support the latest API. If you adopt the server side, you are adopting an implementation whose compatibility is explicitly not assured.
What You Give Up Compared With Vault-Based Managers
KeePassXC is the obvious comparison, and the difference is architectural rather than cosmetic. KeePassXC keeps an encrypted database file that you open with a key file or a master password, and it stores per-entry data: usernames, URLs, notes, TOTP seeds, password history. LessPass computes a password from inputs and stores nothing, so there is no history to consult and no entry to attach a TOTP secret to.
The practical consequence is recovery. A KeePassXC database can be copied, backed up to a USB stick, or synced through any file service, and a corrupted copy can be replaced from a backup. LessPass has no artifact to back up, which is its selling point and also why a forgotten master password is unrecoverable. Conversely, KeePassXC requires you to move that database between devices, which is exactly the chore LessPass exists to remove. If you already have a working sync story for a database file, LessPass is solving a problem you do not have.
Licence, Maintenance and What to Check First
The project is GPL-3.0, which matters if you plan to embed the generator in a product: GPL-3.0 carries copyleft obligations, and the mobile package adds an MPL-2.0 option. This is a description of the licence text, not legal advice; if you are shipping LessPass code inside a commercial application, have a lawyer read the terms rather than a README.
Maintenance cost is mostly in your own habits. There is no vault to migrate and no server to patch if you use the extensions or the CLI, so upgrades are just package updates. If you self-host the server, you inherit the deployment and the API-compatibility risk the README flags for third-party implementations. The README's own todo list still has an unchecked item for a guide to self host a LessPass server on DigitalOcean, so plan on reading the deployment configuration yourself rather than following a finished walkthrough.
Before committing, generate a password for one real account and confirm it is accepted, then do the same for the site with the strictest policy you use.
Editorial conclusion
Adopt LessPass if you want a password generator with no vault to sync and you are comfortable that one master password is the thing you must remember. Do not adopt it for shared team credentials or for accounts whose password rules you cannot encode in the generator options. Before rolling it out, verify the exact profile fields against the password policy of each site you care about, and if you want the connected server, confirm you can self-host it, because the README states new registrations on the hosted service are closed.
Frequently asked questions
How does LessPass avoid synchronizing a password vault?
Nothing is stored. You remember one master password, and the project describes access as working anywhere and anytime with no sync needed, which removes the encrypted vault that other managers spend effort keeping in step across devices.
How do I install the LessPass command line interface?
Through pip, with two documented commands: python3 -m pip install --user lesspass, then lesspass --help. The underlying repository is a TypeScript yarn monorepo, so the CLI reaches users through PyPI.
Do I need a LessPass account to generate passwords?
No for generation. For the connected features, LessPass Server is now reserved for existing users and new registrations are no longer possible, so new users have to self host their own LessPass server.
Can I self host LessPass on DigitalOcean?
That is the intended route for new users, and LessPass itself uses App Platform for automatic server deployment. A guide to self hosting on Digital Ocean is still an open item in the project's todo list, so the steps are not written down yet.
Is it safe to run a third-party LessPass API server?
The project links to third-party implementations in its wiki and asks you to use them with caution, because the author cannot guarantee that they fully support the latest API.
Which license covers LessPass?
The project is licensed under the GNU GPLv3. The LessPass mobile package at packages/lesspass-mobile is bi-licensed under both the Mozilla Public License Version 2 and the GNU GPLv3.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/lesspass-lesspass)Star history chart for your README
[](https://hysenlabs.com/projects/lesspass-lesspass)Was this useful?