Microsoft's Agent Governance Toolkit: Enforcing Agent Actions Outside the Prompt
Project brief: AI Agent Governance Toolkit, Policy enforcement, zero-trust identity, execution sandboxing, and reliability engineering for autonomous AI agents. Covers 10/10 OWASP Agentic Top 10.
At a glance
- What is it?
- A Python library that intercepts tool calls, applies YAML policies, and logs decisions for autonomous AI agents. It targets the OWASP Agentic Top 10, but the public preview status and the ACS migration mean you need to verify the current API before committing.
- Who is it for?
- Adopt this if you operate multi-agent systems where ungoverned tool calls are a real incident risk and you need a deterministic enforcement layer, not a prompt-level reminder. The MIT license and cross-language SDKs remove licensing friction.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
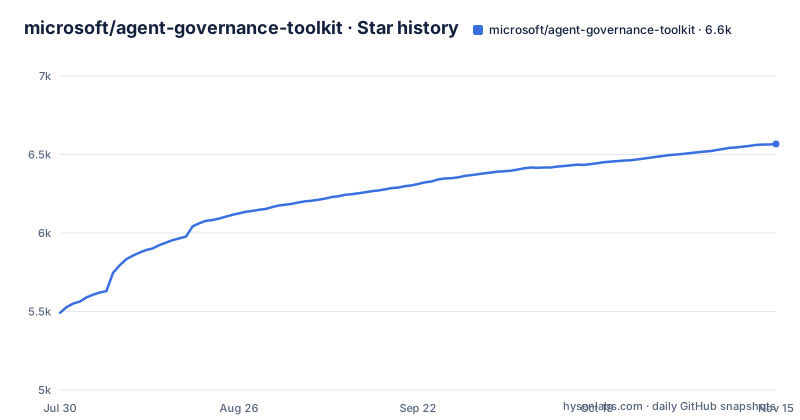
- microsoft/agent-governance-toolkit6,567 ★ · +1,075
| Repository | 2026-07-30 | 2026-11-15 |
|---|---|---|
| microsoft/agent-governance-toolkit | 5.5k | 6.6k |
1,075 Stars in the last 108 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The Problem: OAuth Scopes Do Not Stop a Drop Table
The README frames the core issue clearly: OAuth scopes and IAM roles control which services an agent can reach, not what it does once connected. An agent with `send_email` and `query_database` permissions could still execute `drop_table` if nothing checks the action. Prompt-level instructions are not a control surface, and the README cites OWASP LLM01:2025 to argue that prompt injection has no fool-proof prevention. The toolkit therefore moves enforcement to deterministic application code. Every tool call, message send, and delegation is intercepted before the model's intent reaches the wire. This is a meaningful distinction: the agent cannot perform a denied action, not merely unlikely to. The target audience is anyone running autonomous agents in production, especially multi-agent systems where shared credentials obscure accountability.
Interception, Policy Evaluation, and Audit Trails
The mechanism is a wrapper around any tool function. The `govern` decorator from `agentmesh.governance` takes a callable and a policy file path. On each invocation, it evaluates the YAML policy, logs the decision to an audit trail, and raises `GovernanceDenied` when the rule blocks the action. The policy schema uses `apiVersion: governance.toolkit/v1`, a `default_action` of allow or deny, and a list of rules. Each rule has a `condition` string, an `action` (allow, deny, or require_approval), and an optional `approvers` list. The condition language is expression-based, as in `"action.type in ['drop', 'delete', 'truncate']"`. The README example shows a `require_approval` action that routes to an approver group, though the quick-start example does not show the approval flow. The `AgentControl` API from `agent_control_specification` offers a more programmatic interface, taking a manifest file and an envelope with agent ID and input. The `govern` path writes to an audit trail, which addresses the third question about proving what happened.
Quick Start: Two Lines, But Watch the Distribution
Installation is `pip install "agent-governance-toolkit[full]"`. The README warns that the base wheel installs only the compliance CLI, not the governance modules. The `[full]` extra includes the core distribution, which is where the actual governance code lives. The quick-start import is `from agentmesh.governance import govern`. The older `agent_os` module emits a `DeprecationWarning` because the `agent-os-kernel` distribution is deprecated. There is also a `agent-governance-toolkit-core` distribution as the replacement. The policy engine host code now uses the ACS SDK, and `agt-policies` provides a one-way v4-to-v5 migration command. For Claude Code, you add the repository as a plugin marketplace and install `agt-governance`. The README shows a minimal policy YAML with a `block-destructive` rule and a `require-approval-for-send` rule. The example output shows a `GovernanceDenied` exception with the rule name and description.
Cross-Language SDKs and the Agent Control Specification
The toolkit is not Python-only. The README links to a TypeScript SDK (`@microsoft/agent-governance-sdk`), and a .NET package on NuGet (`Microsoft.AgentGovernance`). The `AgentControl` API in Python reads a manifest file and evaluates an envelope with an `agent_id`. This implies a specification called the Agent Control Specification, or ACS. The README references `agent_control_specification` as an import, and the policy engine host code uses the ACS SDK. This is not a toy: the architecture spans multiple languages and a formal spec. However, the README explicitly says the pre-ACS rule model is gone. If you have existing policies written for the old model, you need the migration command.
OWASP Agentic Top 10 Coverage and the Public Preview Caveat
The description claims coverage of 10/10 OWASP Agentic Top 10. The README links to a compliance document at `docs/compliance/owasp-agentic-top10-architecture.md`. The README also links to the Agentic Trust Framework ecosystem and the AARM builder page. The public preview status is explicit: "production-quality public preview releases. May have breaking changes before GA." This is the single biggest caveat. The v4.1.0 release from June 2026 and the v4.0.0 release from June 1, 2026, both came within days of each other, suggesting active iteration. You should treat the API as moving. The README itself points to `BREAKING_CHANGES.md` for replacements of the old rule model.
Limitations: Approval Flow, Migration, and the Audit Trail
The `require_approval` action names an approver list in the policy YAML; how an approval is requested and granted is not shown in the quick-start example. The README's problem statement calls for tamper-evident records, and the quick start says only that decisions are logged to an audit trail. The migration path is one-way: `agt-policies` provides a v4-to-v5 migration command, but there is no rollback. If the migration produces a policy that behaves differently in production, you cannot easily revert. The base wheel being CLI-only is a footgun: a user who installs the default package without reading the fine print gets a compliance CLI, not the governance engine. The README mitigates this with a warning, but it is an unusual packaging choice that will cause confusion.
Alternatives: Guardrails Libraries and Framework-Level Middleware
The closest alternative is a guardrails library like NeMo Guardrails or Guardrails AI, which also intercept model input and output but often focus on classification and validation rather than tool-level policy. The difference in approach is significant: guardrails libraries typically wrap the model call itself, checking prompts and responses for violations, while AGT wraps the tool call after the model decides. AGT is closer to a service mesh for agents: it sits at the boundary of each external action. Another alternative is framework-level middleware, such as LangChain's callbacks or LlamaIndex's hooks, where you write custom logic to check tool arguments. That gives you full control but requires you to build the policy engine, audit log, and approval flow yourself. AGT provides those as a package. The trade-off is that you inherit the ACS dependency and the public preview API churn. If you need a stable, self-managed solution, framework middleware with a hand-written `if` statement might be simpler for a small number of tools.
Maintenance, License, and Upgrade Costs
The license is MIT, which means you can use, modify, and redistribute without copyleft obligations. That is a low-friction license for commercial adoption. The project is hosted under the `microsoft` GitHub organization, which suggests ongoing corporate backing, but the public preview label means you should expect breaking changes. The release cadence is active: v3.7.0 in May 2026, v4.0.0 and v4.1.0 in June 2026. Each major version may require migration work, as the v4-to-v5 path demonstrates. The README references a CHANGELOG.md, so you can track changes. The packaging split between the base wheel and the `[full]` extra adds upgrade complexity: you need to ensure your dependency pin includes the correct extra. The `DeprecationWarning` on `agent_os` means old code will keep working with warnings, but the eventual removal is a known cost. The ACS SDK dependency is external, so your upgrade risk includes that project's stability as well.
Editorial conclusion
Adopt this if you operate multi-agent systems where ungoverned tool calls are a real incident risk and you need a deterministic enforcement layer, not a prompt-level reminder. The MIT license and cross-language SDKs remove licensing friction. Do not adopt it if you expect a stable API: the public preview allows breaking changes, and the v4-to-v5 migration replaced the rule model. Before deploying, verify which distribution you need (base wheel versus `[full]` extra), confirm the ACS SDK dependency is acceptable in your environment, and test the `govern` wrapper against your actual tool signatures, not just the README examples.
Frequently asked questions
What is the Microsoft Agent Governance Toolkit?
An MIT licensed set of Python and other language packages for policy enforcement, zero-trust identity, sandboxing and reliability work around autonomous agents. Its claim is that tool calls are checked in deterministic application code, so a denied action is structurally impossible rather than merely discouraged by a prompt.
How do I install the Agent Governance Toolkit and actually get the governance modules?
Use Python 3.11 or newer and run pip install "agent-governance-toolkit[full]". The base wheel installs the compliance CLI only; the modules live in agent-governance-toolkit-core, and importing agent_os now emits a DeprecationWarning.
How do I block a destructive tool call with the Agent Governance Toolkit?
Wrap the function with govern(my_tool, policy="policy.yaml") and write a rule whose condition matches the action type, for example action.type in ['drop', 'delete', 'truncate'] with action deny. Calls that fail the policy raise GovernanceDenied, carrying the rule name and description.
Does the Agent Governance Toolkit ship anything for languages other than Python?
Yes. There is an npm package @microsoft/agent-governance-sdk, a NuGet package Microsoft.AgentGovernance, and directories for Go and Rust, plus wrapper directories for Claude Code, Codex CLI, Copilot CLI, OpenCode and the Antigravity CLI.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/microsoft-agent-governance-toolkit)Star history chart for your README
[](https://hysenlabs.com/projects/microsoft-agent-governance-toolkit)Was this useful?