PyRIT: Microsoft's Python Framework for Red-Teaming Generative AI Systems
The Python Risk Identification Tool for generative AI (PyRIT) is an open source framework built to empower security professionals and engineers to proactively identify risks in generative AI systems.
At a glance
- What is it?
- PyRIT is an MIT-licensed Python framework from Microsoft for probing generative AI systems for risk. This article covers what the repository and its documentation actually expose, what the release history suggests about maturity, and where the README hands off to the project website.
- Who is it for?
- PyRIT is worth an evaluation by security engineers and Python developers who already run structured red-team exercises and want a code-level framework rather than a chat UI. It is the wrong starting point for teams without an LLM endpoint to point it at, or for anyone expecting a ready-made test suite, because the README lists no prompt library and no scorer.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
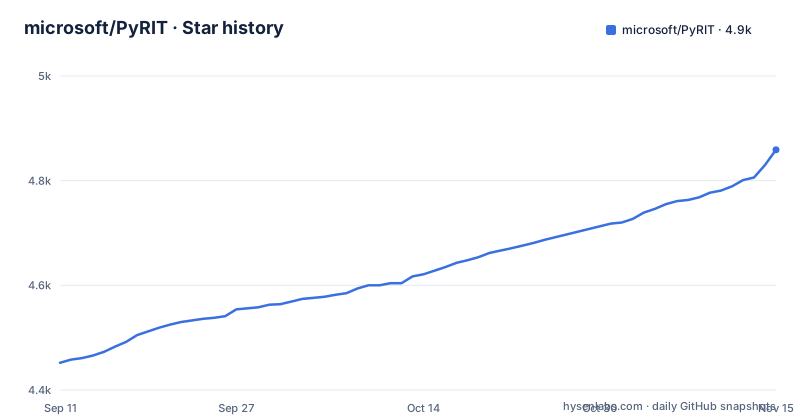
Star history
- microsoft/PyRIT4,859 ★ · +407
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| microsoft/PyRIT | 4.5k | 4.9k |
407 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The Problem PyRIT Names, and Who It Names It For
The repository description gives a one-sentence scope statement: PyRIT is built to let security professionals and engineers proactively identify risks in generative AI systems. That phrasing matters more than it looks. It does not promise automated safety scoring or a compliance report. It names a discipline (red teaming) and a population (people who already do that work, plus engineers who write Python). If you are looking for a library that classifies model outputs as safe or unsafe, the description does not claim to be one. If you are looking for scaffolding to construct adversarial interactions against a model endpoint and record what happens, that is the stated purpose. The distinction is worth holding onto, because it determines whether the rest of the repository will feel like a toolkit or an unfinished product.
What the Repository Actually Exposes
The README is short. It gives the project name, a short description, links to the website, Discord and a whitepaper, three entry points (a command-line Scanner, the CoPyRIT GUI and a Python framework), a list of supported providers and targets, a security policy link, a trademark notice, and a citation instruction pointing at CITATION.cff. It contains no code block, no install command and no configuration example. That is unusual for a tool at version 1.1.0, and it means the README functions as a signpost rather than a manual. Everything operational has been moved to microsoft.github.io/PyRIT. The README does not state how prompts are stored or how results are exported. What can be said is that the project is structured as a Python package with a documentation site, which is the conventional shape for a framework that expects users to read the docs rather than the README.
Release Cadence and What It Suggests
The three most recent releases are v1.0.0 on 24 July 2026, v1.0.1 on 30 July 2026, and v1.1.0 on 4 September 2026. The last push to the default branch is dated 2 November 2026. Two readings are available. The generous one: the project reached a 1.0 milestone and then shipped a minor feature release within six weeks, which indicates active development rather than a frozen artifact. The cautious one: a 1.0 designation usually signals API stability, and a 1.1.0 arriving two months later can carry breaking changes in projects that use minor versions for feature work. Anyone pinning PyRIT in a dependency file should read the v1.1.0 release notes before upgrading, because the version numbering alone does not tell you whether interfaces moved. The repository is not archived.
Getting It Running: What the Material Supports
The README gives no pip command, no conda command, no Docker invocation and no configuration keys. It states that the website at microsoft.github.io/PyRIT contains information about how to use, install, or contribute to PyRIT. That is the only install path traceable to the source. The honest instruction is: start at the website. The same applies to configuration. There are no documented environment variables and no YAML schema in the README. For setup, it points to a provider configuration guide on the documentation site. The one concrete asset the README does hand over is the CITATION.cff file at the repository root, which is the citation path for research use, and the security policy link for private vulnerability reports through the Microsoft Security Response Center.
Where PyRIT Is the Wrong Tool
The first limitation is documentation surface. A framework whose README defers entirely to an external site is harder to evaluate from a repository checkout, and it makes offline or air-gapped assessment awkward. The second is scope. PyRIT is described as a risk identification tool, which places it upstream of mitigation. It does not claim to filter, guardrail or rewrite model responses. Teams that need runtime protection are looking at a different category of software. The third is the absence of any stated evaluation corpus. The README mentions no prompt sets, no scoring rubrics and no benchmark harness. The fourth is the audience gate. The description names security professionals and engineers. The README also lists the CoPyRIT GUI for exploring AI systems interactively and reviewing results in a browser. Finally, the security policy link routes vulnerability reports to Microsoft, which is appropriate for a Microsoft-maintained project but means external contributors cannot triage security issues themselves.
Alternatives and the Difference in Approach
The README does not name any competing project, so a comparison has to stay at the level of category rather than product. The relevant contrast is between a framework and a hosted evaluation service. A hosted service typically presents a web console, ships a fixed set of test categories, and returns a report; the operator configures a target and reads results. PyRIT, as described, is the other shape: a toolkit that brings a command-line scanner, a graphical interface and an extensible Python framework together, with the framework used to compose and extend components into custom red teaming workflows. The trade is control against setup cost. A framework lets you encode a bespoke multi-turn attack that no vendor has thought of, and it keeps the prompts and transcripts inside your own environment. A hosted service gets you to a first result in an afternoon without writing orchestration code. The MIT licence removes the procurement step that a commercial service introduces, and it permits modification and redistribution, which matters if the red-team harness has to be embedded in an internal platform. That is the actual decision: write the orchestration yourself in exchange for full control of the test content.
Licence and Maintenance Cost
PyRIT is released under the MIT licence, which is permissive and short. It allows use, modification, distribution and sublicensing provided the copyright notice and permission notice are retained. It contains no copyleft clause, so embedding PyRIT in a proprietary internal tool does not trigger a source-disclosure obligation. This is a description of the licence text, not legal advice; a legal review is the appropriate step before shipping anything derived from it. The README adds a trademark clause: Microsoft trademarks and logos may only be used under Microsoft's Trademark and Brand Guidelines, and modified versions must not imply Microsoft sponsorship. That clause governs branding, not the code. On maintenance, the costs are twofold. Someone has to track releases, because the version history shows a minor bump within two months of 1.0. Someone has to follow the documentation site, since the README will not tell you when an interface changes. A team that cannot staff those things will find the framework heavier than its one-line description suggests.
Editorial conclusion
PyRIT is worth an evaluation by security engineers and Python developers who already run structured red-team exercises and want a code-level framework rather than a chat UI. It is the wrong starting point for teams without an LLM endpoint to point it at, or for anyone expecting a ready-made test suite, because the README lists no prompt library and no scorer. Verify three things before committing: that the install and usage instructions on microsoft.github.io/PyRIT match your Python version, that the CITATION.cff and security policy URLs resolve, and that the v1.1.0 release notes describe changes you can absorb, since the jump from v1.0.0 to v1.1.0 landed roughly two months after the 1.0 line opened.
Frequently asked questions
how to install pyrit
The repository itself does not give an install command and points to the project website for that. What it does state is the supported range, `requires-python` set to >=3.11, <3.15 with classifiers for 3.11 through 3.14, and its Makefile runs every module through uv with a uv.lock at the top level.
how to use pyrit
PyRIT is a library used to assess the robustness of LLMs, described as an open source framework for security professionals and engineers to identify risks in generative AI systems. The front page directs usage questions to the project website at microsoft.github.io/PyRIT rather than summarising the API in the repository.
how to setup pyrit
Configuration is template driven: the top level holds `.env_example`, `.env_local_example` and `.pyrit_conf_example`, plus a `.devcontainer/` directory, docker/, infra/ and python-dotenv in the dependencies. The repository does not enumerate which values are required.
how to install pyrit in ubuntu
The repository gives no distribution specific instructions and sends install questions to the documentation site. The supported Python range is >=3.11, <3.15, development commands go through uv as the Makefile sets `CMD:=uv run -m`, and documentation builds need jupyter-book, with xelatex and latexmk additionally required for the PDF target.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/microsoft-pyrit)Star history chart for your README
[](https://hysenlabs.com/projects/microsoft-pyrit)Was this useful?