Hacker Scripts: A Terminal Dweller's Legacy of Automation, and What It Teaches About Scripting Culture
GitHub describes it as Based on a true story. The repository metadata lists JavaScript as its primary language. This article stays within the project description and details documented in the GitHub repository README.
At a glance
- What is it?
- NARKOZ/hacker-scripts collects four shell scripts from a true story about a build engineer who automated his life. This review examines what the scripts actually do, how they run, and why they matter as a cultural artifact rather than a production toolkit.
- Who is it for?
- Adopt this repository if you want a quick, amusing look at how a terminal-centric engineer solved mundane problems with shell scripts, or if you need a starting point for similar personal automation. Do not adopt it for production systems: the scripts are tied to a specific anecdote, rely on external services like Twilio and Gmail, and have no documentation beyond the README.
- Can I use it commercially?
- Not without permission. GitHub finds no licence file in the repository, and without a licence all rights are reserved by default: you may read the code but not reuse it. Check the README, or ask the authors, before using it.
- Is it still maintained?
- Probably not. The repository last received commits 37 months ago, on October 23, 2023.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
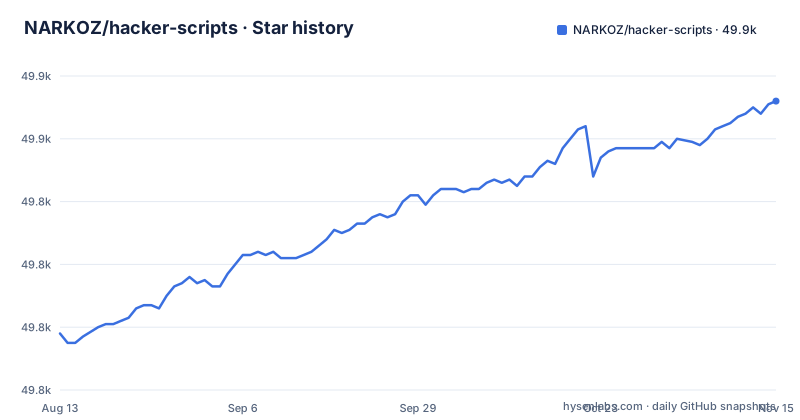
Star history
- NARKOZ/hacker-scripts49,872 ★ · +74
| Repository | 2026-08-13 | 2026-11-15 |
|---|---|---|
| NARKOZ/hacker-scripts | 49.8k | 49.9k |
74 Stars in the last 94 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What This Repository Actually Is
NARKOZ/hacker-scripts is a collection of four shell scripts, plus some Ruby helpers, that were supposedly left behind by a build engineer who automated every task that took more than 90 seconds. The README quotes a story from bash.im, a Russian humor site, where a colleague describes finding these scripts. The scripts are: smack-my-bitch-up.sh, which sends a text message to the engineer's wife when he is working late; kumar-asshole.sh, which scans email for keywords from a problematic DBA and rolls back a staging database; hangover.sh, which sends a fake sick-day email; and fucking-coffee.sh, which triggers a networked coffee machine to brew a latte with precise timing. The repository is a cultural artifact, a joke that became code. It is not a library or a framework. It is a set of personal scripts that happen to be public.
The Mechanism: How Each Script Works
The README tells an anecdote about late-work messages, a database rollback, an absence message and a networked coffee machine. Treat those details as the story's description, not proof that every implementation behaves identically. In the current shell files, hangover.sh checks for an active user session and sends an SMS via Twilio; it does not send email. The coffee and Kumar shell files delegate to external commands named fucking_coffee and kumar_asshole. Inspect the implementation and its dependencies before using any variant. The README provides sample cron schedules and environment variables.
Running the Scripts: Environment and Cron Setup
To run any of these scripts, you need to set environment variables. The README lists TWILIO_ACCOUNT_SID and TWILIO_AUTH_TOKEN for the Twilio-based scripts, and GMAIL_USERNAME and GMAIL_PASSWORD for the kumar script. For the Ruby scripts, you need to install gems: dotenv, twilio-ruby, and gmail. The cron jobs are given as examples. smack-my-bitch-up.sh runs Monday to Friday at 9:20 PM, hangover.sh at 8:45 AM, kumar-asshole.sh every 10 minutes, and fucking-coffee.sh hourly from 9 AM to 6 PM on weekdays. The README shows the exact crontab lines. The examples also depend on external commands and environment-specific endpoints; cloning the repository and setting variables alone does not establish a working setup. Review and adapt each script before scheduling it, especially any action that sends messages or changes a database.
A Genuine Limitation: It Is a Story, Not a Tool
The biggest limitation is that these scripts are anecdotal. They were written for a specific person's environment: a particular server, a particular coffee machine, a particular Gmail account. The scripts assume that the coffee machine is on the network and accepts telnet commands, which is not a common setup. They also assume that the staging database can be rolled back with a single SSH command, which is risky in any real environment. The scripts are not designed for reuse. They are a snapshot of one person's hacky solutions, and they should not be treated as a template for production automation.
The Alternative: Proper Automation Tools
If you want to automate similar tasks, the alternative is to use purpose-built tools. For sending messages, you could use a dedicated messaging API with proper error handling and logging. For checking server sessions, you could use a monitoring tool like Nagios or a simple script with explicit conditions. For database rollbacks, you would use a migration tool or a backup script with validation. The difference is that these alternatives are designed to be robust: they handle failures, log output, and have documentation. Hacker-scripts are the opposite: they are minimal, fragile, and undocumented. The README even says 'Pull requests with other implementations (Python, Perl, Shell, etc) are welcome'.
Maintenance and License Implications
The repository has no releases and its last push was in October 2023, so it is likely unmaintained. The code is released under the WTFPL, which is a permissive license that allows you to do almost anything with the code, including using it in commercial projects, without attribution. However, the license is not a standard one, and some organizations may have policies against using non-standard licenses. The scripts themselves are simple enough that you could rewrite them from scratch, which might be safer than relying on unmaintained code. The maintenance cost is zero if you just read the scripts for amusement, but if you try to use them, you will need to update the API integrations and handle edge cases yourself.
Why This Repository Matters
Despite the lack of production readiness, hacker-scripts is worth looking at because it captures a specific culture of terminal-centric automation. The story is funny, but the scripts reveal a mindset: if a task takes more than 90 seconds, write a script. That is a valuable lesson for engineers, even if the execution is crude. The scripts also show the power of cron and environment variables for personal automation. You do not need a complex framework to automate your life. Sometimes a shell script and a cron job are enough. But the repository also serves as a warning: without documentation, error handling, or a clear purpose, scripts become legacy code that nobody understands. The README is just a quote, a list of environment variables, and example cron lines. There is no explanation of how the scripts work internally, which is fine for a joke, but not for a tool.
Editorial conclusion
Adopt this repository if you want a quick, amusing look at how a terminal-centric engineer solved mundane problems with shell scripts, or if you need a starting point for similar personal automation. Do not adopt it for production systems: the scripts are tied to a specific anecdote, rely on external services like Twilio and Gmail, and have no documentation beyond the README. Before using any script, verify that the environment variables are set correctly, that the cron schedules match your needs, and that the external APIs (Twilio, Gmail) still work as expected. The repository is a snapshot of a particular person's workflow, not a reusable framework.
Frequently asked questions
Who is the No.1 hacker?
The repository does not name one. It is built around a true story about a build engineer who lived inside the terminal, loved Vim, drew diagrams in Dot, and scripted anything that took more than 90 seconds. The humour is about over-automating small daily tasks.
What coding do hackers use?
In this project, the build engineer's tools are Vim, Dot, and Markdown, and the four joke scripts start in shell and Ruby at the top level before being ported into directories for JavaScript, Python, C#, Go, Java, Kotlin, PHP, Perl, Scala, Clojure, Groovy, CoffeeScript, R, and PowerShell.
Do hackers use C++?
Not in this repository, which has no C++ directory. The ported implementations cover shell, Ruby, JavaScript, Python, C#, Go, Java, Kotlin, PHP, Perl, Scala, Clojure, Groovy, CoffeeScript, R, and PowerShell.
Which hacker is illegal?
The repository does not discuss legality. Its four scripts send a text message, send an email, roll back a staging database over SSH, and brew coffee on a networked machine, all framed as jokes from a true story, with the code released under the WTFPL.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/narkoz-hacker-scripts)Star history chart for your README
[](https://hysenlabs.com/projects/narkoz-hacker-scripts)Was this useful?