Ghidra 12.2: NSA's Java-based reverse engineering framework for teams and automation
Ghidra, from the NSA Research Directorate, is a software reverse engineering framework with disassembly, decompilation, graphing, and scripting across many processors.
At a glance
- What is it?
- Ghidra is a full-featured software reverse engineering framework from the NSA Research Directorate. This review covers its install, build, scripting model, and the trade-offs of adopting a government-maintained tool under Apache-2.0.
- Who is it for?
- Adopt Ghidra if you need a free, extensible SRE platform for team-based analysis of compiled code, especially if you value Java/Python scripting and a permissive license. Skip it if you require a stable commercial support contract or if you cannot manage the JDK 25 requirement and the security advisory process.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 4 days ago.
- What is it written in?
- Mainly Java, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
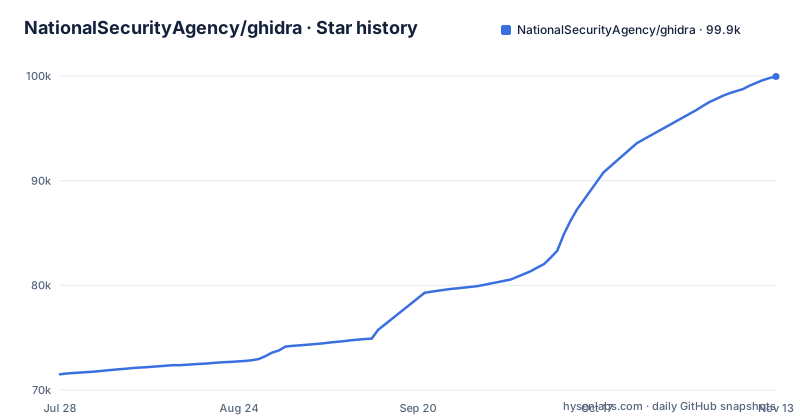
- NationalSecurityAgency/ghidra99,948 ★ · +28,445
| Repository | 2026-07-28 | 2026-11-13 |
|---|---|---|
| NationalSecurityAgency/ghidra | 71.5k | 99.9k |
28,445 Stars in the last 108 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What Ghidra actually is and who it serves
Ghidra is a software reverse engineering framework created and maintained by the National Security Agency's Research Directorate. The README describes it as a suite of full-featured, high-end analysis tools for compiled code on Windows, macOS, and Linux. It includes disassembly, assembly, decompilation, graphing, and scripting. The intended users are SRE analysts who need to understand malicious code or find vulnerabilities in networks and systems. The project was built to solve scaling and teaming problems on complex reverse engineering efforts. That origin matters. Ghidra is not a hobby tool. It is designed for organizations that need multiple analysts working on the same binaries and who want to automate parts of the analysis. If you are a solo reverse engineer, it still works, but the collaborative features are where the design effort went.
The mechanism: a Java framework with a decompiler and scripting
The README mentions capabilities like disassembly, decompilation, and graphing, but the key mechanism is the scriptable API. Users write scripts in Java or Python to extend or automate analysis. The framework runs in both user-interactive and automated modes. The automated mode is significant. It means you can run Ghidra headless, without the GUI, to process binaries in bulk. That is a different approach from a purely GUI-driven tool. The decompiler is also a differentiator. It turns assembly into a higher-level pseudo-code that analysts can read faster than raw opcodes. The architecture is modular enough that NSA has applied it to problems involving malicious code analysis, which suggests the framework can be adapted to different analysis pipelines.
Getting it running: install and build commands
The README gives clear install steps. You need a 64-bit JDK 25. Download the official release zip, which is named `ghidra_<version>_<release>_<date>.zip`, and extract it. The warning is explicit: do not extract on top of an existing installation. Launch with `./ghidraRun` on Linux/macOS or `ghidraRun.bat` on Windows. There is also a Python launcher: `./support/pyghidraRun`. For building from source, the requirements are JDK 25, Gradle 9.1.0+, Python 3.9 to 3.15 with bundled pip, GCC or Clang and make on Linux/macOS, and on Windows, Visual Studio 2017+ with MSVC, Windows SDK, and C++ ATL. The build process starts with `gradle -I gradle/support/fetchDependencies.gradle` to download additional dependencies, then `gradle buildGhidra`. The output lands in `build/dist/`. If you have an internet connection, you can use the Gradle wrapper `./gradlew` instead of a system Gradle. For development, the README recommends Eclipse, and you run `gradle prepdev eclipse buildNatives` to prepare the environment.
Scripting and extensions: Java and Python with a plugin system
Ghidra's extensibility is a central feature. Users write custom scripts and extensions using the GhidraDev plugin for Eclipse, which ships inside the release at `Extensions/Eclipse/GhidraDev/`. Alternatively, Visual Studio Code can edit scripts, and you can generate a fully-featured VSCode project from a CodeBrowser window via `Tools -> Create VSCode Module project`. The README notes that both integrations only work against a fully built Ghidra installation, not the source tree. That is a constraint. If you want to develop extensions, you must first download a release. PyGhidra is mentioned as a launcher, which suggests Python is a first-class citizen. For a team, this means you can have analysts who prefer Python and others who use Java, and they can share the same underlying framework. The trade-off is that writing a serious extension requires learning Ghidra's API; the README points to the Developer's Guide for more detail.
A real limitation: security advisories and version sensitivity
The README contains a blunt security warning: there are known security vulnerabilities within certain versions of Ghidra, and users must read the Security Advisories before proceeding. That is a genuine limitation. You cannot assume a downloaded release is safe. The project's own documentation tells you to check for advisories, which means you must track version-specific issues. This is unusual for a reverse engineering tool, where the tool itself is analyzing untrusted binaries. If you use Ghidra to open a malicious sample, a vulnerability in Ghidra could compromise your analysis machine. The README does not list specific advisories, so you have to visit the security page. This is a case where the wrong tool is one that you use without a patching process. For teams, this adds an operational burden: you need to monitor the advisories and upgrade when a fix is released. The release cadence is visible in the repository, with Ghidra 12.2 on 22 October 2026 following 12.1.4 on 21 September and 12.1.3 on 18 August, but the README does not say how often security patches appear. You should treat that as an unknown and verify before deployment.
Alternatives: how Ghidra differs from the other major SRE tool
The most direct alternative is IDA Pro, but the README does not mention it. The difference in approach is fundamental. IDA Pro is a commercial, closed-source product with a mature plugin ecosystem and a long history. Ghidra is open source under Apache-2.0, free to use, and maintained by a government agency. The licensing difference alone changes your cost model. IDA Pro requires a paid license, which can be expensive for a team. Ghidra has no license fee, but you pay in other ways. You must handle your own security patching, and the tool's development direction is driven by NSA's mission, not by a commercial roadmap. Another open alternative is radare2, which is a command-line-first tool with a different scripting model. Ghidra's decompiler and GUI are more accessible for analysts who prefer visual analysis. The choice depends on your team's skill set and budget. If you need commercial support, Ghidra does not offer it. If you need zero cost and are willing to manage the security advisories, Ghidra is a strong candidate.
Maintenance and upgrade cost
The README gives some signals about maintenance. The build process requires a specific JDK version (25) and Gradle version (9.1.0+), which means upgrading Ghidra from source requires keeping those toolchains current. For pre-built releases, the upgrade path is to download a new zip and extract it to a fresh directory. The README does not describe a migration tool for user settings. The license is Apache-2.0, which is permissive. You can modify the source and distribute your changes, but you must keep the license notice. That is a low legal burden, but not zero. The contributor's guide exists, but the README does not state how often releases are published. The repository shows a recent push and releases 12.1.3 in August, 12.1.4 in September and 12.2 in October 2026, so the project is active, but you should verify the release cadence yourself if that matters for your planning.
Editorial conclusion
Adopt Ghidra if you need a free, extensible SRE platform for team-based analysis of compiled code, especially if you value Java/Python scripting and a permissive license. Skip it if you require a stable commercial support contract or if you cannot manage the JDK 25 requirement and the security advisory process. Before adopting, verify your exact processor and executable format support against the release notes, and review the Security Advisories page for any known vulnerabilities in the version you plan to deploy.
Frequently asked questions
What is Ghidra used for?
It is a software reverse engineering framework created and maintained by the NSA Research Directorate for analyzing compiled code on Windows, macOS and Linux. Its listed capabilities are disassembly, assembly, decompilation, graphing and scripting, across a wide variety of processor instruction sets and executable formats, in user-interactive and automated modes.
Where can I get Ghidra?
From the project's Releases page on GitHub, under the Assets drop-down of the build you want. The file is named ghidra_<version>_<release>_<date>.zip, and the two Source Code entries GitHub offers are explicitly not the right download for an installation.
How do I install Ghidra on Windows?
Install a 64-bit JDK 25, download the Assets zip from a release, extract it somewhere that is not on top of an existing installation, then run ghidraRun.bat or support\pyghidraRun.bat. Launching the batch file starts the Java tool; the one under support starts PyGhidra.
Is Ghidra as good as Ida?
The repository makes no comparison with Ida or with any other disassembler, so it gives you no basis for one. What it does state is that Ghidra analyzes compiled code across Windows, macOS and Linux, supports a wide variety of processor instruction sets and executable formats, runs interactively or automated, and is licensed under Apache-2.0.
How do I use Ghidra to decompile?
The repository names decompilation as one of its capabilities and tells you to launch the tool with ./ghidraRun or the PyGhidra launcher ./support/pyghidraRun. It does not include a decompilation walkthrough, a list of supported instruction sets, or a debugger and emulator configuration, so those details are not documented here.
Official sources
Where developers are discussing it
Posts on Hacker News, dev.to and Lobsters that link to this repository, found by our scan of those communities. 2 in the last 30 days; newest first.
- Reverse Engineering Block Blastdev.to · Oct 31, 2026 · 6 points · 0 comments
- Reverse Engineer Anything: The Open-Source Tool That Turns Any Binary Into a Readable Spec (And Why Big Tech Won’t Love It)dev.to · Oct 21, 2026 · 13 points · 2 comments
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/nationalsecurityagency-ghidra)Star history chart for your README
[](https://hysenlabs.com/projects/nationalsecurityagency-ghidra)Was this useful?