GoClaw: A Multi-Tenant Go Agent Gateway That Packs a Lot, but Check the License
GoClaw - GoClaw is OpenClaw rebuilt in Go — with multi-tenant isolation, 5-layer security, and native concurrency. Deploy AI agent teams at scale without compromising on safety.
At a glance
- What is it?
- GoClaw rebuilds OpenClaw in Go, adding multi-tenant isolation, a layered security model, and native concurrency. It is a serious server-side agent orchestrator, but the non-commercial license and beta release cadence need scrutiny.
- Who is it for?
- Adopt GoClaw if you run a server-side multi-tenant agent service, need per-user isolation and encrypted API keys, and can accept a non-commercial license (CC BY-NC 4.0). Do not adopt it if you require a permissive license for commercial products, or if you need a stable, non-beta release.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
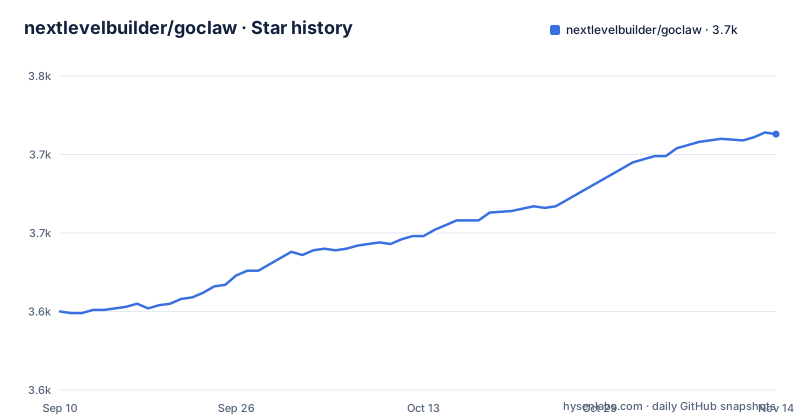
- nextlevelbuilder/goclaw3,713 ★ · +113
| Repository | 2026-09-10 | 2026-11-14 |
|---|---|---|
| nextlevelbuilder/goclaw | 3.6k | 3.7k |
113 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What GoClaw Solves and Who It Targets
GoClaw is a multi-tenant AI agent platform written in Go, positioned as a rebuild of OpenClaw with added isolation and concurrency. The problem it addresses is running many AI agents for different users or teams without letting one tenant's data or permissions bleed into another's. The README describes per-user workspaces, encrypted API keys, and RBAC, which are typical needs for a SaaS product that exposes agent capabilities to external customers. The target user is an engineer building a production agent service that must handle multiple clients, not a hobbyist running a single bot. The desktop edition, GoClaw Lite, targets a different audience: local, single-user use with no server infrastructure, but it caps agents at five and teams at one. That split means GoClaw tries to cover both a self-hosted server product and a local app, which is ambitious and may dilute focus.
The 8-Stage Pipeline and 4-Mode Prompt System
The core execution model is an 8-stage agent pipeline: context, history, prompt, think, act, observe, memory, summarize. The README says stages are pluggable and always on, meaning every agent run passes through these stages in order. This is a structured approach to agent loops, forcing a consistent cycle of reasoning and tool use. The prompt system has four modes: Full, Task, Minimal, and None, with section gating and cache boundary optimization. The idea is that different tasks need different amounts of context; a simple query should not send a huge prompt to an LLM. Per-session mode resolution suggests the system can decide which mode to use based on the session's needs. This is a concrete mechanism for controlling token costs and latency, which is useful for scale. However, the README does not explain how the mode is chosen or what heuristics drive the resolution. Without that detail, an operator cannot predict when a session will switch modes, which could lead to unexpected behavior or costs.
3-Tier Memory and Knowledge Vault Architecture
Memory is split into three tiers: working memory for conversation, episodic memory for session summaries, and semantic memory backed by a knowledge graph. The README mentions progressive loading L0/L1/L2, which suggests that not all memory is loaded into context at once. Instead, the system fetches more detailed memory only when needed, which is a practical way to manage context windows. The Knowledge Vault adds a document registry with [[wikilinks]] and hybrid search combining full-text search and pgvector. That means you can store documents and have agents retrieve them via vector similarity or keyword matching. In the Lite edition, memory degrades to FTS5 text search because SQLite does not have pgvector, so semantic search is a server-only feature. This is a real trade-off: the desktop version loses the knowledge graph and pgvector, making it less capable for long-term semantic recall. The architecture diagrams are referenced but not included in the text, so the exact data flow between tiers is not fully specified.
Getting It Running: Quick Start and Build Commands
The README gives a Quick Start section. What is visible is the desktop edition installation: on macOS you run a curl script from GitHub, and on Windows you use PowerShell with irm. For building from source, the prerequisites are Go 1.26+, pnpm, and the Wails CLI. Commands like make desktop-build and make desktop-dev are documented, and desktop releases use lite-v tags to trigger GitHub Actions builds. For the standard server edition, the badges indicate Docker and PostgreSQL 18 are involved, but no explicit docker run or config file example appears in the cleaned README. This is a gap: an operator cannot see how to set up the multi-tenant PostgreSQL schema or configure the 20+ LLM providers without visiting the external documentation site. The README does say it is a single binary, about 25 MB, with startup under 1 second, which implies a simple deployment, but the exact steps are left to docs.goclaw.sh.
Security Layers: What Is Claimed and What Is Missing
The README claims a 5-layer permission system, rate limiting, prompt injection detection, SSRF protection, and AES-256-GCM encryption for API keys. These are serious security features for a multi-tenant service. However, the README does not enumerate what the five layers are. Without a breakdown, you cannot assess whether the layers cover tenant isolation, user roles, tool access, or network egress. SSRF protection is important for agents that fetch URLs, because a malicious prompt could try to hit internal services. Prompt injection detection is also relevant, but no details are given on how it works or its false-positive rate. The encryption of API keys at rest is a good practice, but the key management process, such as where the master key is stored, is not described. For a production deployment, these missing details matter. You would need to read the documentation or source code to verify the security model actually matches the marketing.
Multi-Tenancy and Concurrency in Go
Go's native concurrency is a strong fit for an agent gateway that handles many simultaneous sessions. The README emphasizes native concurrency and multi-tenant isolation, which suggests that each tenant's sessions run in separate goroutines or contexts. The use of PostgreSQL as the central store for workspaces and sessions implies that horizontal scaling is possible by adding more instances behind a load balancer. But the README does not specify how session affinity or WebSocket connections are managed across instances. The 7 messaging channels (Telegram, Discord, Slack, Zalo, Feishu, WhatsApp) each require long-lived connections, which complicates scaling. If a channel connection is tied to a single instance, you need sticky sessions or a shared state layer. The README does not address this. Also, the default branch is dev, and the latest release is a beta (v3.15.0-beta.208), which indicates the project is in active development and not yet stable. The release cadence is high, with multiple beta tags per week, which means frequent changes and potential churn for adopters.
Licensing and Maintenance Cost
The license badge in the README says CC BY-NC 4.0, which is a Creative Commons Non-Commercial license. The repository metadata says NOASSERTION, meaning the license is not a standard open-source license. This is a major issue for commercial adoption. CC BY-NC allows use for non-commercial purposes only, so if you plan to sell a service built on GoClaw, you cannot legally use it without a separate commercial license from the maintainers. The README also has a badge for Go 1.26 and PostgreSQL 18, both of which are very recent or even future versions (as of the knowledge cutoff). This may require you to upgrade your infrastructure to match. Maintenance cost is high because the project is on a dev branch by default and releases betas frequently. You would need to track each beta to get bug fixes and security patches. The desktop edition auto-updates from GitHub Releases, which is convenient, but the server edition updates via Docker or binary, so you must manage that yourself. There is no mention of a migration path between versions, which is a risk for a fast-moving project.
Alternatives and Where GoClaw Fits
The README says GoClaw is OpenClaw rebuilt in Go. OpenClaw appears to be a similar agent platform, possibly in another language. The key difference is the language and the multi-tenant focus. If you are already using OpenClaw, moving to GoClaw would give you Go's concurrency and a smaller binary, but you would have to verify feature parity. Another alternative would be building your own agent orchestration on top of a generic LLM gateway like LiteLLM or a framework like LangGraph. Those tools do not provide multi-tenant isolation or memory tiers out of the box, so you would need to implement them yourself. That is a significant amount of work. GoClaw bundles these features, which is its appeal. However, the non-commercial license makes it a poor fit for a commercial SaaS unless you negotiate a license. For internal, non-commercial research or personal projects, GoClaw could save you months of work. For a commercial product, you might be better off with an open-source alternative that has a permissive license, even if you have to assemble more pieces yourself.
What to Verify Before Adoption
The README is marketing-heavy and leaves several implementation details unspecified. Before you adopt GoClaw, you should verify the following. First, check the actual license in the repository, because the badge says CC BY-NC but the metadata says NOASSERTION. Contact the maintainers if you need commercial use. Second, inspect the source code to confirm the 5-layer security model and see how prompt injection detection is implemented. Third, test the single-binary deployment on a small VPS, as the README claims under 1 second startup and a $5 VPS is enough. Fourth, review the documentation at docs.goclaw.sh for the Quick Start that is missing from the README. Fifth, check the default branch (dev) and recent release history to understand the stability. The project is in beta, so expect breaking changes. If you need a stable, long-term platform, wait for a non-beta release. If you are building a prototype or a non-commercial tool, GoClaw is worth trying, but do not bet your production infrastructure on a beta with a restrictive license.
Editorial conclusion
Adopt GoClaw if you run a server-side multi-tenant agent service, need per-user isolation and encrypted API keys, and can accept a non-commercial license (CC BY-NC 4.0). Do not adopt it if you require a permissive license for commercial products, or if you need a stable, non-beta release. Before committing, verify the current state of the default branch (dev), check whether the 5-layer security model matches your threat model, and test the single-binary deployment on a small VPS. GoClaw's value is real only if you can live with its licensing and early-stage versioning.
Frequently asked questions
Is GoClaw the same thing as OpenClaw?
No, it is a rewrite. The project describes itself as OpenClaw rebuilt in Go, adding multi-tenant isolation, a five-layer permission system and native concurrency, and shipping as a single static binary with its own PostgreSQL backend and a separate desktop edition.
Is GoClaw free and where do I get it?
This repository states no license for the project, though a LICENSE file exists at the root, so the terms have to be read there. The server edition builds from source with Go 1.26+ and PostgreSQL 18 with pgvector or runs as a container, and the desktop edition installs from GitHub Releases. OpenClaw's own terms are not covered here.
What does GoClaw need before it will start?
Go 1.26+, PostgreSQL 18 with pgvector, and Docker if you use Compose. The setup path is prepare-env.sh to generate secrets, one GOCLAW_*_API_KEY in .env, then make up, which migrates the database and serves the dashboard on port 18790.
Does GoClaw expose its dashboard to the network?
The compose service sets GOCLAW_HOST=0.0.0.0 and publishes port 18790, so the gateway token generated by prepare-env.sh is the control in front of it. The environment example also documents an empty-token mode for loopback-only development through GOCLAW_ALLOW_INSECURE_NO_AUTH=1.
What can GoClaw agents reach outside the container?
It depends on the compose profile you enable. The sandbox profile needs a Docker socket group id, 999 on Linux and 0 on macOS or Windows Docker Desktop, the cloudflared profile wants a tunnel token, and separate profiles add headless browser work through go-rod, Redis, Tailscale and OpenTelemetry.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/nextlevelbuilder-goclaw)Star history chart for your README
[](https://hysenlabs.com/projects/nextlevelbuilder-goclaw)Was this useful?