Node.js GitHub Bot: A Webhook-Driven Automation Layer for the Node.js Organization
@nodejs-github-bot's heart and soul. Node.js GitHub Bot The Node.js Foundation members use this bot to help manage the repositories of the GitHub organization.
At a glance
- What is it?
- The Node.js GitHub Bot is a single-instance webhook service that runs event-handling scripts across the Node.js organization's repositories. It is a pragmatic, MIT-licensed tool for org maintainers, but its architecture assumes a centralized deployment and a willingness to write custom JavaScript.
- Who is it for?
- Adopt the Node.js GitHub Bot if you manage a GitHub organization and want a lightweight, scriptable way to respond to webhook events without adopting a heavier automation platform. It is a good fit for Node.js maintainers who are comfortable writing JavaScript and deploying a single always-on service.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 5 days ago.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
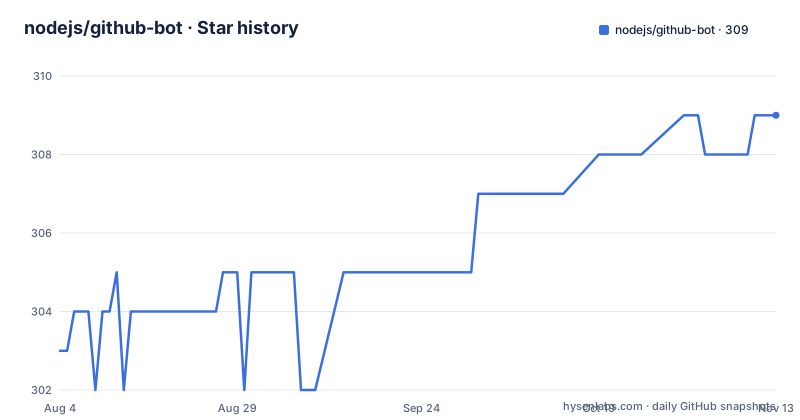
- nodejs/github-bot309 ★ · +6
| Repository | 2026-08-04 | 2026-11-13 |
|---|---|---|
| nodejs/github-bot | 303 | 309 |
6 Stars in the last 101 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
What the Bot Actually Does for the Node.js Organization
The Node.js GitHub Bot exists to automate repetitive repository management tasks across the dozens of repositories in the nodejs GitHub organization. The README describes it as the 'heart and soul' of the @nodejs-github-bot account, and the mechanism is simple: GitHub sends webhook events to a single URL, and the bot runs JavaScript scripts in response. Those scripts can do anything the GitHub API allows, such as labeling issues, closing stale PRs, or triggering CI builds. The intended audience is not the general public; it is the maintainers and collaborators of the Node.js Foundation who need a shared tool to enforce org-wide policies. The bot is not a product with a user interface. It is a codebase that you deploy and extend with your own event handlers.
The Single-Instance Webhook Architecture
The architecture is deliberately centralized. The README states that all repositories using the bot have the same webhook URL and secret, and that there is only one bot instance. This is a hard constraint, not a suggestion. GitHub does not allow org-wide webhooks, so the bot must be configured per repository, but each repository points to the same endpoint. The implication is that the bot becomes a single point of failure. If the service goes down, every repository in the org loses its automation until it comes back. The benefit is simplicity: you deploy one process, configure one secret, and all scripts run in the same context. The bot reads events and dispatches them to scripts, but the README does not detail the routing logic. You have to read the source to understand how a given script is matched to an event type. That is a gap in the documentation, but the script directory structure suggests that each script is responsible for a specific event handler.
Running the Bot: Environment Variables and Startup
Getting the bot running requires setting several environment variables. The only mandatory one is GITHUB_TOKEN, which must be a personal or bot account token with the right permissions for the actions your scripts perform. GITHUB_WEBHOOK_SECRET is also needed for production, with a default of 'hush-hush' if you do not set it. The README lists optional variables for Jenkins integration, such as JENKINS_WORKER_IPS and JENKINS_API_CREDENTIALS, which are only needed for scripts that talk to ci.nodejs.org. Logging is controlled by LOGS_DIR, KEEP_LOGS (default 10 days), and LOGIN_CREDENTIALS to protect the /logs endpoint. To start the bot, you run npm start, which presumably launches the main server. For local development, you can create a .env file at the project root, and the bot will load it. The README explicitly warns that the webhook content type must be application/json, because the default GitHub form-urlencoded will not work. That is a concrete configuration detail that will trip up anyone who skips the README.
Local Development Without a Public Webhook
Developing locally is awkward because GitHub webhooks need a publicly reachable endpoint. The README offers two workarounds. The first is an SSE relay: you set SSE_RELAY to a URL like https://hook-relay.example.com, and the bot receives GitHub events via Server-Sent Events instead of a direct webhook. The second is ngrok, which tunnels localhost to a public URL. The relay approach is interesting because it decouples the bot from the webhook delivery mechanism. The README also points to the TestOrgPleaseIgnore organization, which is set up to send events to a relay, so you can test your scripts without touching real repositories. This is a practical setup, but it means you need to run a separate relay server if you do not use the public one. The README does not say whether the relay is maintained or reliable, so you should assume you may need to host your own.
The Script System: Custom Code, Not Configuration
The bot's functionality is entirely defined by scripts in the scripts directory. The README shows that you can run a subset of scripts by passing a glob to the SCRIPTS environment variable, for example SCRIPTS=./scripts/my-new-event-handler.js npm start. This tells you that each script is a standalone file that registers itself to handle certain events. The documentation does not specify the script API, so you must read the existing scripts to learn the conventions. This is a high barrier for casual users, but it gives maintainers full control. There is no declarative configuration file; everything is code. That is a trade-off: flexibility at the cost of maintainability. If you are not a JavaScript developer, this bot is not for you. The scripts are likely simple event handlers, but the README gives no examples, so you cannot judge the complexity without browsing the repository.
Limitations and Failure Modes
The most obvious limitation is the single-instance model. If the bot crashes, no repository gets automated until it is restarted. There is no mention of high availability, load balancing, or failover in the README. Another failure mode is the webhook content type: if someone configures a new repository with the default GitHub webhook settings, the bot will silently fail because it expects application/json. The README warns about this, but it is easy to miss. The bot also depends on the GITHUB_TOKEN having the exact permissions required by each script. If a token is scoped too narrowly, scripts will fail with API errors, and there is no built-in error reporting described. The JENKINS_* variables are optional, but if you use the Jenkins trigger script, you must set them correctly for each repository, which is a lot of environment variable management. Finally, the bot is not a general-purpose automation platform; it is tied to GitHub webhooks and the Node.js org's specific workflows. Using it outside that context requires significant adaptation.
Alternatives: GitHub Actions and Probot
The natural alternative is GitHub Actions, which is built into GitHub and allows you to define workflows in YAML files within each repository. The key difference is that Actions runs on GitHub's infrastructure, so there is no server to maintain, and each repository can have its own workflows without a shared webhook secret. Actions also has a marketplace of pre-built actions, so you may not need to write custom JavaScript. However, Actions is not a single bot that can coordinate across repositories; you would need to duplicate workflows or use reusable workflows. Another alternative is Probot, a framework for building GitHub bots in Node.js. Probot handles the webhook receiving and authentication for you, and it supports multiple apps. The Node.js GitHub Bot predates or parallels Probot, but Probot gives you a more structured app model with a manifest and per-app installation. The difference is that Probot apps are installed per repository or org, whereas this bot is a single service with a shared secret. If you want a more maintainable, community-supported framework, Probot might be a better starting point. If you want a minimal, org-specific tool, this bot is fine.
Maintenance and License Considerations
The bot is MIT-licensed, so you can use, modify, and distribute it freely, with the only obligation being to preserve the license notice. There is no cost for the software itself. The maintenance cost is entirely in the custom scripts and the deployment. The README does not mention any versioning or release process, and the repository has no recent releases listed, so you are essentially running from the default branch. That means you need to track upstream changes manually if you fork it. The environment variables are numerous, and each new script may require new variables, so configuration management becomes a task. The bot also relies on external services like Jenkins and the SSE relay, which add operational dependencies. The KEEP_LOGS variable defaults to 10 days, but you must set LOGS_DIR to a writable location, and the /logs endpoint is protected by LOGIN_CREDENTIALS, so you need to manage those credentials. Overall, the maintenance burden is moderate if you are comfortable with Node.js and DevOps, but it is not a zero-ops solution.
Editorial conclusion
Adopt the Node.js GitHub Bot if you manage a GitHub organization and want a lightweight, scriptable way to respond to webhook events without adopting a heavier automation platform. It is a good fit for Node.js maintainers who are comfortable writing JavaScript and deploying a single always-on service. Do not adopt it if you need a GUI, a managed service, or if your organization cannot run a single instance with a shared webhook secret. Before adopting, verify that your GitHub account token has the required permissions for every script you plan to run, and confirm that your webhook content type is set to application/json, since the default form-urlencoded will not work. The bot is MIT-licensed, so there is no license cost, but you will own the maintenance of the scripts and the service itself.
Frequently asked questions
What does the Node.js GitHub bot do?
It runs scripts in response to GitHub webhook events for the repositories of the Node.js organisation. There is a single bot instance, so every participating repository is configured with the same webhook URL and secret, and organisation-wide webhooks are explicitly not allowed.
How do I run github-bot locally?
Create an environment file at the repository root with an API token and a relay address, then start the bot with the package start script. Events from a published test organisation are delivered to the relay instead of straight to your machine, and the secret variable is not required on that path because there is no inbound request to sign.
What is the GITHUB_WEBHOOK_SECRET for, and what is its default?
It is the value GitHub signs posted payloads with, and the readme states a two-word phrase as the default, which is also the value you are told to reuse when configuring a webhook on a test organisation. If you use your own repository you must set the secret to match the variable rather than relying on the published default.
How does github-bot talk to Jenkins?
Through four variables. One is a comma-separated allowlist of worker addresses permitted to push pull request status updates. Another is an API credential for the CI server. The last two are namespaced per repository: a job URL saying which job to trigger when a collaborator comments, and a build token for that specific job so a remote script can start a build.
Are github-bot's logs protected?
Yes, with a credentials variable holding a username and password pair in that format, and the logs are served under a logs path. A directory variable says where they are written and a retention variable, defaulting to ten days, says how many days of rotated files are kept.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/nodejs-github-bot)Star history chart for your README
[](https://hysenlabs.com/projects/nodejs-github-bot)Was this useful?