Obfuscar ships a security notice telling you not to run it on assemblies you do not trust
Open source obfuscation tool for .NET assemblies
At a glance
- What is it?
- An MIT licensed .NET assembly obfuscator whose own readme calls its coverage basic, whose version is derived from git history and is still in beta, whose build is nine Windows scripts and one shell script, and whose readme is a signpost to a documentation site rather than a manual. The three notices at the top are about trust, about deprecations and about the project being maintained by a company that sells support.
- Who is it for?
- Obfuscar suits a developer shipping a .NET assembly who wants names and strings to be harder to read, treats obfuscation as one layer rather than as protection, and builds on a platform where the assemblies arrive from their own pipeline. It does not suit anyone processing third-party binaries, because the tool says so itself.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 58 days ago.
- What is it written in?
- Mainly C#, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
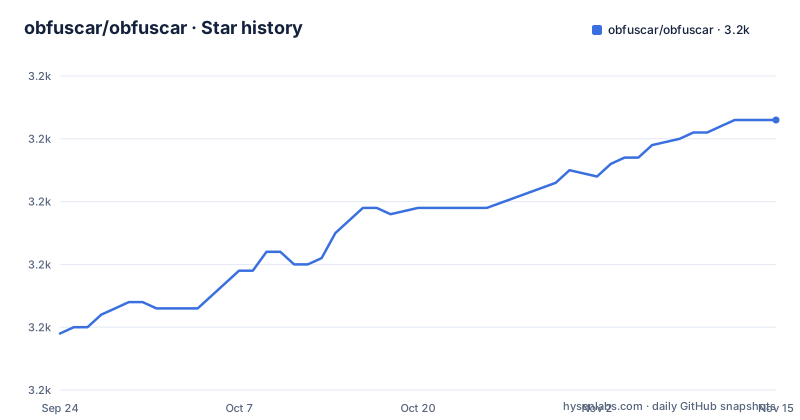
- obfuscar/obfuscar3,223 ★ · +34
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| obfuscar/obfuscar | 3.2k | 3.2k |
34 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The project calls its own coverage basic
The description is one sentence and it contains the most important word in it.
It says the tool provides basic obfuscation features that help secure secrets in a .NET assembly. The header calls it a minimalistic obfuscation tool. The repository description says the same thing again, more compactly.
Three separate places, one adjective, and it is not marketing. It is a limitation stated by the project about its own product, and for an obfuscator that is an unusual thing to lead with.
The alternative reading is that basic is meant reassuringly rather than diminutively: this is not a packer, not a virtualiser, not a commercial protector with a feature grid. It does renaming and encoding work and stops there.
Either way, the positioning matters for evaluation. If you are choosing a tool because you need to stop someone reading your strings, this may be enough. If you are choosing one because you need to stop someone reversing your logic, the readme is telling you not to expect that, and it is better to learn that from the readme than from an afternoon.
The licence is MIT, which is worth noting separately: this is the permissively licensed option in a category where commercial tools are common.
The security notice says do not feed it untrusted assemblies
Three notices sit at the top of this readme, and the first is the one to read twice.
It says the tool depends on low-level metadata and executable-reading interfaces, naming two specific ones, and that those are not designed to handle untrusted input. It says malformed or malicious assemblies or metadata can cause unexpected behaviour including crashes or hangs. And then it says: only run it on assemblies and inputs you trust.
That is a limitation statement in the shape of a security advisory, and it is attached to a tool whose entire purpose is to be pointed at a binary.
The practical reading is that the trust boundary is upstream of the tool. You obfuscate what your own build produced. You do not take a download, run an obfuscator over it to inspect it, or wire an obfuscator into a service that accepts uploaded assemblies, because the parsing layer underneath is not hardened for that and will fail in ways that are crashes and hangs rather than errors.
The notice links to a discussion in the platform's own API documentation, which suggests it was raised upstream rather than discovered here. That is a good sign about where the boundary comes from, and it does not change what you may feed the tool.
Both configuration conveniences are being removed
The other two notices are about the configuration file, and they are deprecations rather than warnings.
The first says environment-variable expansion inside configuration files is deprecated and will be removed in a future release, and asks you to avoid that syntax, pointing at the documentation for migration guidance. The second says relative paths in configuration files are deprecated and that future releases will require absolute paths.
So two things that made a configuration file portable are being taken away. A file that could name an endpoint by environment variable could live in source control unchanged across environments. A file that used relative paths could move with the build output.
For a build tool whose configuration is the only interface it has, that is a significant narrowing, and it lands on existing users first: the environment variable syntax has to be replaced with something per-machine, and relative paths have to be rewritten to absolute ones, which means the configuration stops being shareable between machines and starts being generated.
Neither deprecation says when. The readme gives a version-shaped promise and no timeline, so the practical approach is to migrate before you upgrade rather than after.
The version comes from git history, and it is still beta
The release list tells you the project is pre-1.0 on its current major, and busy.
The three most recent releases are consecutive beta builds of the same 3.0.0 version, published in late August and twice in September 2026, the newest on the same day as the last push.
So this is an active project shipping frequently, and it has not yet cut a stable 3.0.0. Two weeks of beta builds and no stable tag means anyone installing by version is installing something that expects to change.
Where the number comes from is also in the repository. A configuration file for a git-based versioning tool sits at the root, which means the version is computed from tags and commit history rather than written into a file. That is a good default for a tool that wants releases to match history, and it also means a local build produces a version string describing your checkout rather than a release.
Combined with a configuration file that pins the software development kit version, this repository pins two things a contributor needs: which toolkit they are building with, and what the build thinks it is.
The build is nine Windows scripts and one shell script
The root listing is mostly build tooling, and the shape of it is informative.
There is a solution file, in the newer XML-based format rather than the classic one. There is a package specification file. There is a global configuration file pinning the software development kit. And then there are ten scripts.
Nine of those ten are Windows: a script that builds everything, a script that packs everything, a script that publishes to the public package feed, a script that installs the package tool, a script that runs the tests, and a pre-build, release, and signing script in PowerShell.
One is a shell script, and it does the same job as the Windows distribution script beside it.
So the project is built and released primarily on Windows, with a shell equivalent provided for the distribution step alone. Nothing in the readme says so, and there is no build documentation here either: the readme points at a documentation site for the history and the detail.
There is also a directory of third-party code wired in as submodules, which is how a tool that reads a binary format keeps its format readers current without vendoring copies.
An MIT tool with a company selling support behind it
The licensing and the support arrangement are the same three lines of the readme, and they are worth reading together.
The tool is MIT licensed. It is maintained by a named company. Support services are available from that company. Pull requests are welcome provided you sign a contributor licence agreement. Donations go through a sponsorship link.
That is a coherent and common arrangement for infrastructure tooling: the code stays open, and the company that maintains it sells help with it. It also tells you who the security response path is, because the maintainer is an organisation rather than a hobbyist.
The logo credit is the other detail in that block. The project logo came from a named icon set by a named artist, linked. For a security tool that is a small thing and a good one, because it establishes that the trademark is not being passed off as the project's own artwork.
The readme also credits the platform and the maintainer consistently across sections, which in a repository with this few files is a sign of care rather than of volume.
The readme is a signpost, and the documentation site holds the history
This readme is about a page long, and almost all of it is notices and contact details.
There is no installation section, no configuration example, no usage walkthrough and no option reference. What it does say about documentation is that a separate site contains most of the information you need, and also a detailed history of the project through the years.
That is a deliberate division of labour, and for a tool with a configuration file full of options it is a defensible one. It does mean the readme cannot answer the two questions a new user actually has, which are how to run it and what the options do.
The notices therefore carry an unusual share of the document. Three of the six substantive paragraphs are about trust, about deprecations and about who to contact, which is the correct priority for a tool that reads binaries, and also a sign that the real documentation is being maintained somewhere the readme cannot track.
Two badges at the top point at a package feed and a global tool entry, and one at a workflow file for Windows builds, so the three ways to obtain the thing are discoverable from the first line.
Editorial conclusion
Obfuscar suits a developer shipping a .NET assembly who wants names and strings to be harder to read, treats obfuscation as one layer rather than as protection, and builds on a platform where the assemblies arrive from their own pipeline. It does not suit anyone processing third-party binaries, because the tool says so itself. Before you build it into a release pipeline, check three things: whether the assemblies you feed it are all yours, since the readme says malformed or malicious metadata can cause crashes or hangs; whether your configuration uses relative paths or environment-variable expansion, because both are deprecated and the first will become an error; and whether you are comfortable with a version scheme derived from git history that is still shipping beta builds.
Frequently asked questions
how to use obfuscar
The readme does not give steps. It points at a documentation site for the detail, and links two package feed entries, one for a global tool and one for the library. What it does state is the scope, basic obfuscation features that help secure secrets in a .NET assembly, and the constraint that matters most: run it only on assemblies and inputs you trust, because the low-level metadata interfaces underneath can crash or hang on malformed input.
how to use obfuscar in visual studio
The repository does not describe any editor integration. What the tree shows instead is a command line build: a solution file in the newer XML format, a package specification, a pinned software development kit version, and a set of batch and PowerShell scripts for building, packing, testing, releasing and signing, plus a publishing script that targets the public package feed. Anything about editor integration would be documented on the project's documentation site.
What does an obfuscator do?
In this project's terms, it provides basic obfuscation features that help secure secrets in a .NET assembly, and the project describes itself as a minimalistic tool. That is deliberately modest positioning rather than a claim of coverage, and it is worth weighing against your threat model before assuming renaming and encoding is the protection you need.
What are the drawbacks of obfuscating?
This project does not answer that. What its readme does disclose is operational: environment-variable expansion inside configuration files is deprecated and will be removed, relative paths in configuration files are deprecated and will become required to be absolute, the current version line is still shipping beta builds of a single major version, and the tool should only be run on assemblies and inputs you trust.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/obfuscar-obfuscar)Star history chart for your README
[](https://hysenlabs.com/projects/obfuscar-obfuscar)Was this useful?