Suricata: a network IDS and IPS whose README is aimed at patch authors
Suricata is a network Intrusion Detection System, Intrusion Prevention System and Network Security Monitoring engine developed by the OISF and the Suricata community.
At a glance
- What is it?
- Suricata is a network IDS, IPS and NSM engine from OISF, and its repository spends almost all of its README on the private QA process rather than on installation. What the repository does document is the risk model, the exact test battery behind every merge, and the zero warnings policy that governs them.
- Who is it for?
- Take Suricata when your requirement is a network IDS, IPS and NSM engine whose detection logic and logging you can read, patch and rebuild yourself, and when your team can absorb a C codebase tested against multi-gigabit traffic and multi-terabyte pcap collections.
- Can I use it commercially?
- Yes, with conditions. GPL-2.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly C, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
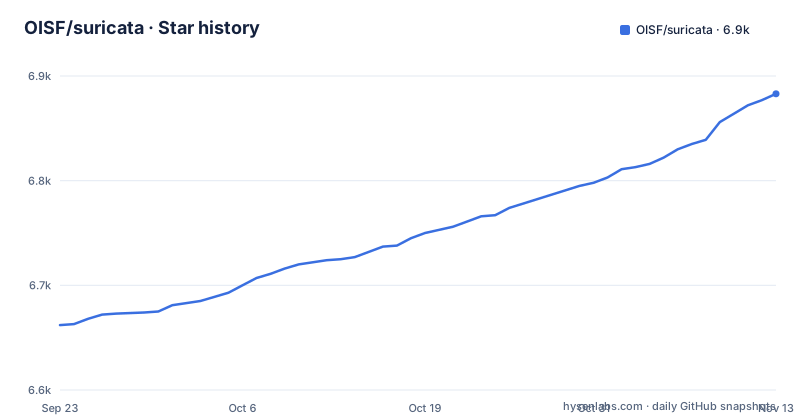
- OISF/suricata6,883 ★ · +221
| Repository | 2026-09-23 | 2026-11-13 |
|---|---|---|
| OISF/suricata | 6.7k | 6.9k |
221 Stars in the last 51 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Two lines of introduction, then a contributor handbook
The introduction to this repository takes two sentences: Suricata is a network IDS, IPS and NSM engine developed by OISF and the Suricata community. After that, the README never explains how to install it or how to configure it. What it does instead is a resources list and then several hundred words about the contribution process.
That resources list is short and it is where the operator information lives. The home page is suricata.io, the user guide is docs.suricata.io, the installation guide is at docs.suricata.io/en/latest/install.html, the developer guide sits under the same docs site, bugs go to redmine.openinfosecfoundation.org, and the support forum is forum.suricata.io. Two badges point at continuous integration: the OSS-Fuzz issue list for proj:suricata and the codecov project page.
So the first judgement about this repository is about its audience. It is written for people patching the engine and for integrators packaging it. If you are looking for the configuration reference or the default rule set, this README is the wrong file, and the documentation site it points to is the one to read.
The risk sentence that justifies the whole process
One paragraph explains why the contribution process is slow, and it is the most useful paragraph in the file. Suricata is described as a complex piece of software dealing with mostly untrusted input, and mishandling that input has serious consequences in three distinct ways.
In IPS mode a crash may knock a network offline. In passive mode a compromise of the IDS may lead to loss of critical and confidential data. And a missed detection may lead to undetected compromise of the network. The project adds that in many common cases the IDS or IPS is directly reachable by an attacker.
Read as an engineer, those three lines are a specification of failure modes rather than marketing. The first says the blocking path is the dangerous one, which is why traffic replay based IDS and IPS tests are part of the standard run rather than an optional extra. The second says the sensor holds data worth stealing. The third says a false negative is the failure that matters most, and it is the one no amount of test coverage can prove absent.
This is also why the project tells contributors that contributing can be a somewhat lengthy process. That is a direct consequence of treating untrusted input as the normal case.
What the private QA run covers overnight
Team members can submit builds to a private QA setup. It runs a series of build tests and a regression suite to confirm that no existing feature breaks. The final run takes a few hours minimally and generally runs overnight, and the setup is private because of the nature of the test traffic.
These are among the top-level entries in the repository tree:
src/
rust/
ebpf/
lua/
plugins/
python/
rules/
qa/
suricata-update/
suricata.yaml.in
threshold.config
The scripted pass covers extensive build tests on different operating systems, compilers, optimization levels and configure features. Static code analysis runs with cppcheck and scan-build. Runtime code analysis runs with valgrind, AddressSanitizer and LeakSanitizer. Then come regression tests for past bugs, output validation of logging, unix socket testing, pcap based fuzz testing under ASAN and LSAN, and traffic replay based IDS and IPS tests. Almost all of these are acceptance tests: if something fails, addressing it is up to the patch author.
The manual tier measured in terabytes and weeks
Beyond the scripted pass, some changes trigger manual tests chosen according to what was touched. The list is where the project's real scale shows: traffic replay testing at multi-gigabit rates, processing large pcap collections in the multi-terabytes, fuzz testing that might take multiple days or even weeks, pcap based performance testing, and live performance testing.
Those entries are not decoration. Which of them run depends on the type of code change.
One QA step runs after the merge rather than before it. Builds are submitted to the Coverity Scan program, and because of the limits of that free service the submission happens at most once a day. The project is explicit that the community can still find problems after a merge, and asks for help addressing them when they appear. That is an honest admission about what pre-merge testing cannot promise.
Zero warnings is a policy with an escape hatch
One FAQ entry covers the situation every contributor hits eventually: the compiler, the code analyser or the tool is wrong, what now. The answer is that warnings and errors are not accepted to stay, and that in some cases a suppression is added when the tool supports one, naming valgrind and DrMemory as examples. Some warnings can be disabled. And in exceptional cases the only solution is to refactor the code so the static checker no longer trips over a false positive.
The stated reasoning is worth quoting in spirit because it is a maintenance argument rather than a style rule: warnings tend to get ignored and then increase the risk of hiding other warnings. A build that always prints a wall of them trains people to scroll past, and the next real one goes unread.
The refactor option is the expensive part. Rewriting code to satisfy a checker that has a false positive costs the author time on every future version of that tool, and the project still prefers it to a suppressed warning. For an adopter this matters in a specific way: the codebase stays warning free against a moving toolchain, which means upgrading the analysers is part of the maintenance budget rather than an event that lands as a wall of new output.
A closed PR usually means the QA failed
The FAQ explains the pull request lifecycle in a way that tells you how much weight to put on a green CI badge. The documented workflow expects a new pull request for every change. When feedback arrives, the expectation is that the original is replaced by an improved pull request rather than amended through more commits, and the comment thread on the closed request stays open for disagreement.
Then the useful diagnostic: a request closed without comments is the one to suspect QA, and a failure in the GitHub-CI checks means the fix is immediate, with no discussion unless the reporter believes the failure itself is wrong. There is a companion entry on believing a QA test is wrong. The invitation to discuss is there, but the expectation is the opposite of it: more often it is the code that turns out to be wrong.
Timing is deliberately vague. Acceptance depends on code quality, whether the team or community considers the feature useful, how much it affects other code, and the risk of a performance regression. A major feature or a high risk change goes into the next major version. Read as an adopter, that is a maintenance signal: anything substantial lands in a major version boundary, so upgrades are planned events.
GPL-2.0 and a contributor agreement that keeps one owner
The repository is GPL-2.0, with COPYING and LICENSE at the root. On top of that the project requires a signed contributor license agreement, and gives its reason without hedging: to keep the ownership of Suricata in one hand, the Open Information Security Foundation. The two pages behind that decision are suricata.io/about/open-source/ and suricata.io/about/contribution-agreement/.
For a security appliance vendor that is the clause to read twice, because it decides whether outside patches can be relicensed later and whether a downstream distributor has any say. It is a governance fact, not a defect, and it is the reason the ownership question has a single answer.
Release cadence points the same way. The recent tags are suricata-8.0.8 from 2026-10-29, 8.0.7 from 2026-09-15 and 8.0.6 from 2026-07-07. The last push to the repository landed on 2026-11-02.
What this repository refuses to tell you
There are four gaps worth naming before anyone evaluates the engine from this repository alone. First, no install command appears in the README. The configuration template suricata.yaml.in is present at the root, along with threshold.config and the suricata-update tooling, but the file that would explain what belongs in them lives at docs.suricata.io.
Second, no supported platform list is given. The QA pass builds on different operating systems, compilers and optimization levels, which tells you coverage exists without telling you which combination is a supported target.
Third, no throughput or memory figure appears, even though live performance testing and multi-gigabit replay are part of the process. The test regime is described in detail and the results are not, so sizing a sensor has to be done on your own traffic.
Fourth, the rules themselves are a separate concern from the engine. The repository carries a rules/ directory and a suricata-update/ project, but nothing here documents which rule sources are supported or how often they update. Judging detection quality from this README is not possible, and the honest summary is that this file is a contribution document that happens to identify the engine.
Editorial conclusion
Take Suricata when your requirement is a network IDS, IPS and NSM engine whose detection logic and logging you can read, patch and rebuild yourself, and when your team can absorb a C codebase tested against multi-gigabit traffic and multi-terabyte pcap collections. Do not take it expecting a turnkey product: the README gives no install command, no configuration reference and no throughput numbers, so every operational decision has to come from docs.suricata.io and from measurements on your own traffic. Before committing, check three things: whether the current 8.0.8 release matches the rule formats and log outputs your tooling already parses, how GPL-2.0 together with a contributor license agreement that keeps ownership in one hand fits your distribution model, and whether your on-call can wait out the regression suite when a detection bug shows up, because the project's own process assumes exactly that wait.
Frequently asked questions
What is Suricata used for?
It is a network IDS, IPS and NSM engine, meaning intrusion detection, intrusion prevention and network security monitoring, developed by OISF and the Suricata community. This repository describes that project from the contributor side; the operator documentation is at docs.suricata.io.
Is Suricata an IDS or IPS?
Both, plus network security monitoring. The project describes the risk differently in each mode: in IPS mode a crash may knock a network offline, while in passive mode a compromise of the IDS may lead to loss of critical and confidential data.
how to install suricata
The repository README carries no install command of its own. It points to the Installation Guide at docs.suricata.io/en/latest/install.html, and the build inputs are visible in the tree at the root: autogen.sh, configure.ac, Makefile.am and acsite.m4.
how does suricata work
This repository does not describe the detection pipeline. What it documents is the safety net around the engine: build tests across operating systems and compilers, static analysis with cppcheck and scan-build, runtime analysis with valgrind, AddressSanitizer and LeakSanitizer, regression tests for past bugs, log output validation, unix socket testing and traffic replay based IDS and IPS tests.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/oisf-suricata)Star history chart for your README
[](https://hysenlabs.com/projects/oisf-suricata)Was this useful?