onWatch and the changeme pair it hands you with the dashboard
Track AI API quotas across Synthetic, Z.ai, Anthropic (Claude Code), Codex, GitHub Copilot & Antigravity in real time. Lightweight background daemon (<50MB RAM), SQLite storage, Material Design 3 dashboard. Zero telemetry.
At a glance
- What is it?
- A Go daemon that polls eleven AI provider APIs, stores quota history in SQLite and serves a Material Design 3 dashboard on port 9211. Its own configuration example ships a default admin login, and the compose file needs a chown before the daemon can write.
- Who is it for?
- Judge this one on its configuration surface rather than its feature list, because that is where the decisions are. The dashboard login is the pair of values in the readme's own example, the compose file mounts a directory the daemon cannot write until you change its owner, and the memory ceiling in that same file sits above the figure the project advertises.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 5 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
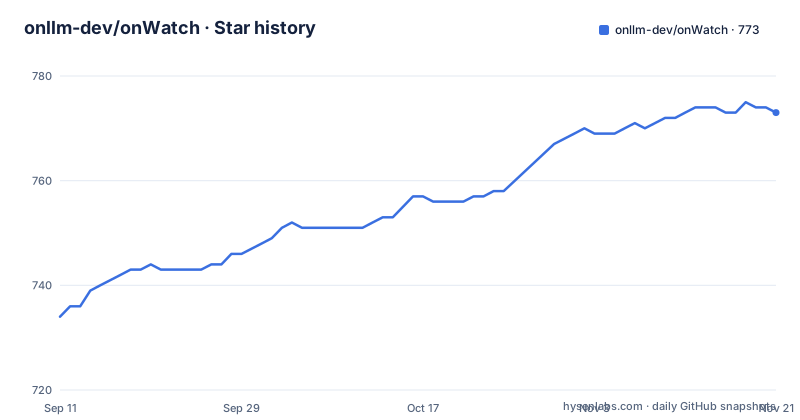
- onllm-dev/onWatch773 ★ · +39
| Repository | 2026-09-11 | 2026-11-21 |
|---|---|---|
| onllm-dev/onWatch | 734 | 773 |
39 Stars in the last 71 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The dashboard you log into with admin and changeme
The configure section hands out a working login in the same block as the provider keys.
SYNTHETIC_API_KEY=syn_your_key_here       # https://synthetic.new/settings/api
ZAI_API_KEY=your_zai_key_here             # https://www.z.ai/api-keys
ANTHROPIC_TOKEN=your_token_here           # Auto-detected from Claude Code credentials
CODEX_TOKEN=your_token_here               # Recommended for Codex-only setups
COPILOT_TOKEN=ghp_your_token_here         # GitHub PAT with copilot scope (Beta)
ONWATCH_ADMIN_USER=admin
ONWATCH_ADMIN_PASS=changeme
The run section then says to open `http://localhost:9211` and log in with your `.env` credentials, so those two lines are the account, and the password is the literal word `changeme`. The port is a default rather than a constant: the compose file maps `${ONWATCH_PORT:-9211}:9211`, so the host side is yours to move and the container side is fixed at 9211. That same compose file hands the whole `.env` to the container through `env_file`, so the credential pair travels in with every provider key.
Compose caps the daemon at 64M and keeps 30 megabytes of logs
The project advertises a lightweight background agent under 50 MB of RAM with all providers polling in parallel, and ships a single binary. The compose file sets its own ceiling above that figure, with a memory limit of 64M and a reservation of 32M under `deploy.resources`.
Two numbers for the same process, one in prose and one in a file that actually applies. Neither is wrong on its own; the reserve is less than the limit, which is how a limit is normally written. The consequence is that the documented footprint fits and a provider that starts polling more often would reach the limit rather than slow down, and a container memory kill is an event in the runtime rather than a line in the application's own log.
Disk is bounded too. The logging driver is `json-file` with a maximum file size of 10m and three files kept, so roughly thirty megabytes of log history survive a restart. The restart policy is `unless-stopped`, so the container comes back after a daemon reboot without anyone asking.
The bind mount needs a chown before the daemon can write to it
The compose file mounts `./onwatch-data:/data` and carries its own instruction in a comment: pre-create with `mkdir -p ./onwatch-data && chown -R 65532:65532 ./onwatch-data`. That UID is not an arbitrary number, it is the non-root user the image creates, and the Dockerfile does the same thing inside the image with a comment about fixing permission errors for both bind mounts and named volumes.
The fix inside the image does not survive the bind mount. `mkdir -p /data && chown 65532:65532 /data` sets the ownership of the container's own directory, and the moment a host directory is mounted over `/data` the host directory's ownership wins while the daemon is still running as 65532. That is why the compose file has to tell you to chown on the host, and why the step is easy to miss on a first run: the container starts, and the database write is what fails.
One variable in that same block is not in the readme's configure list at all. The compose file sets `ONWATCH_DB_PATH=/data/onwatch.db` under `environment`, overriding anything from the `.env`.
A build left at dev turns off update checks, so the VERSION file is the fallback
The Dockerfile is careful about one value and the reason is worth reading. `main.version` is stamped purely through ldflags, so the build step declares `ARG VERSION=dev` and then, if the value is empty or the literal string `dev`, reads the repository's root `VERSION` file instead. The comment on those lines gives the stakes directly: leaving it as `dev` would silently disable update checks.
Compose drives that path by default. The build arguments in the compose file are `VERSION: ${VERSION:-dev}` and `BUILD_TIME: ${BUILD_TIME:-}`, so a plain `docker compose up --build` with no VERSION in the shell takes the fallback branch and gets a real version number out of the file. `BUILD_TIME` has no fallback and defaults to an empty string, and it is stamped into `main.buildTime` by the same ldflags string as the version.
The build then checks itself. After compiling with `CGO_ENABLED=0`, trimmed paths and stripped symbols, the last build line runs `./onwatch --version` and falls through to an echo when the binary was cross-compiled and cannot execute.
Three providers read their credentials from outside the .env file
The `.env` is not the only place a token can come from, and for three of the eleven providers it is the second choice.
`ANTHROPIC_TOKEN` can be left empty. Anthropic tokens are auto-detected from Claude Code credentials, and the readme names the three places it looks: the macOS Keychain, the Linux keyring, or `~/.claude/.credentials.json`. Codex is similar but stronger, since during runtime onWatch re-reads Codex auth state from `~/.codex/auth.json` or `CODEX_HOME/auth.json` and picks up token changes without a restart. The `.env` example explains why you would still set `CODEX_TOKEN` anyway: onWatch can re-read fresh tokens while running, but setting it in `.env` ensures Codex-only startup works reliably.
Copilot is the third. `COPILOT_TOKEN` takes a GitHub Personal Access Token of the classic kind with the `copilot` scope, and it is the one key in that block marked Beta.
The env example documents a provider the readme's list never names
The headline list runs from Synthetic and Z.ai through Anthropic, Codex, GitHub Copilot, MiniMax, Gemini CLI marked legacy, Cursor, Grok, Kimi Code and Antigravity, with a setup guide in `docs/` for most of them. The `.env` example goes past that list.
Three variables there are for a provider the readme never puts in its own lineup: `OPENCODE_ENABLED`, `OPENCODE_GO_API_KEY`, described as a console service-account key with usage read access in the `oc_sk_` form, and `OPENCODE_GO_WORKSPACE_ID`, a `wrk_` value sent as the `x-org-id` header. The comments set out the fallback: when the API key is empty, a browser session is used instead and both values are required. What gets tracked is described as the plan's own five-hour, weekly and monthly meters, read from the console API, with the walkthrough in `docs/OPENCODE_SETUP.md`.
`ZAI_BASE_URL` is also there, defaulted to `https://api.z.ai/api` and described as an override for a custom Z.ai endpoint. So the file you copy into `.env` carries at least one provider the headline list and the setup guides section leave out.
Five install routes and at least that many places to put a .env
Six routes are documented and they do not agree on where things live. The one-line installer pipes `install.sh` into bash, downloads the binary to `~/.onwatch/`, creates a `.env`, registers a systemd service on Linux or offers a launchd agent on macOS, and puts `onwatch` on your PATH. Homebrew is a tap install followed by `onwatch setup`, an interactive wizard. Windows has a PowerShell one-liner over `install.ps1` that writes to `%USERPROFILE%\.onwatch\`, and an `install.bat` you can double-click.
Manual means a binary from the Releases page, with builds for macOS on ARM64 and AMD64, Linux on AMD64 and ARM64, and Windows on AMD64 and ARM64. Building from source needs Go 1.25 or higher and goes through `./app.sh --build` or `make build`. Docker starts from a different example file, `.env.docker.example`, then `docker-compose up -d`, or `./app.sh --docker --run`.
Both example files ship in the root alongside a `.envrc` for direnv. The container is distroless at roughly ten to twelve megabytes and runs as non-root, with an Alpine variant carrying a shell, and data persists at `/data`.
One binary carries a menubar item, a system tray and an editor extension
The installer is said to fetch the standard binary, which includes the menubar companion on macOS and the system tray on Linux desktops. The dependency list agrees: `fyne.io/systray` for the tray, `github.com/aymanbagabas/go-pty` for terminals, `github.com/mattn/go-isatty` and `github.com/pkg/browser` for console and browser launching, `github.com/joho/godotenv` for the `.env`, `modernc.org/sqlite` for storage, and `github.com/prometheus/client_golang` for metrics.
That SQLite choice is what makes the container build possible. A pure Go driver is why `CGO_ENABLED=0` and a distroless base can go together, and `golang.org/x/crypto` and `github.com/steipete/sweetcookie` sit alongside for credential and cookie handling. The module path is versioned as `/v2` and the required Go version is 1.25.7.
The editor side is separate from all of it. The VS Code extension installs with `code --install-extension onllm-dev.onwatch` and is described as a thin client that needs the daemon already running and finds it automatically, offering a status bar item, hover tables and a sidebar quick view. The repository also carries `extensions/` and `gnome-extension/` directories. That extension paragraph is where this version of the readme stops, mid-sentence.
Editorial conclusion
Judge this one on its configuration surface rather than its feature list, because that is where the decisions are. The dashboard login is the pair of values in the readme's own example, the compose file mounts a directory the daemon cannot write until you change its owner, and the memory ceiling in that same file sits above the figure the project advertises. None of that is disqualifying, but all three have to be handled on day one. Before you point it at a machine, change the admin password, pre-create and chown the data directory to UID 65532, decide whether you want the .env values or the credentials already stored by Claude Code and Codex, and remember the project labels itself beta with two releases published on the same day.
Frequently asked questions
What does onWatch actually track?
Usage and quota across Synthetic, Z.ai, Anthropic, Codex, GitHub Copilot, MiniMax, Gemini CLI, Cursor, Grok, Kimi Code and Antigravity, with history kept in SQLite and shown on a Material Design 3 dashboard at http://localhost:9211. It works with any tool using those keys, named examples being Cline, Roo Code, Kilo Code, Claude Code, Codex CLI and Cursor.
How do you install onWatch?
Six routes are given: piping install.sh to bash, `brew install onllm-dev/tap/onwatch`, piping install.ps1 to iex in PowerShell on Windows, a manual binary from the Releases page for macOS, Linux and Windows on both architectures, building from source with Go 1.25 or higher, and docker-compose up -d from .env.docker.example. The installer writes the binary to ~/.onwatch, creates a .env, and registers a systemd service on Linux or a launchd agent on macOS.
What does onWatch need before it will start?
At least one provider key in a .env file, plus ONWATCH_ADMIN_USER and ONWATCH_ADMIN_PASS, which are the credentials for the dashboard. Anthropic tokens can be left out and auto-detected from Claude Code credentials, Codex auth state is re-read from ~/.codex/auth.json while running, and GitHub Copilot needs a classic personal access token with the copilot scope.
Is onWatch considered stable?
It does not claim to be. The readme labels it beta and says it is in active development with features and APIs that may change as the product is refined. The release line moves quickly on 2.14: v2.14.6 on 2026-09-28, then v2.14.7 and v2.14.8 both on 2026-10-02.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/onllm-dev-onwatch)Star history chart for your README
[](https://hysenlabs.com/projects/onllm-dev-onwatch)Was this useful?